
VectorFreed
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
binary-exploitationexploitationinformation-gathering+4
21
rafabd1/vectorfreedDocuments the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 abraxas/sqlite-wal-pagesize
SQLite 3.53.4 - High - Local - Info leak - WAL/DB page-size mismatch uninitialized page tail
 abraxas/spark-rpc-stream-unauth
Apache Spark 4.2.0 - High - Remote - File read - unauth RPC StreamRequest File join
 abraxas/spark-history-zip-symlink
Apache Spark 4.2.0 - High - Remote - File read - History zip follows planted symlink
 abraxas/nextcloud-calendar-sharee-publish
Nextcloud 35.0.0 — a calendar edit-sharee can publish the owner's calendar to an unauthenticated URL
 abraxas/cakephp-cookie-suffix
CakePHP 5.4.2 - High - Remote - Cookie - Http Client cookie jar matches domains as a regex suffix
 0x4d31/honeypot-data
Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
 01luyicheng/cve-2026-99999-exploit
CVE-2026-99999 Working PoC — real VM escape for Linux kernel csum_start bug (CVSS 9.3). Guest-to-Host heap leak. See also: CVE-2026-99999-analysis…
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 abraxas/pfsense-api-example-ssl-verify
pfSense Plus MIM API toolkit b4acd7ca - Medium - Remote - Privilege leftover - official samples verify_ssl=False
 watchtowrlabs/watchtowr-vs-atlassian-cve-2026-21589
Python detection artifact that checks Atlassian Jira, Confluence, and Bitbucket instances for the CVE-2026-21589 arbitrary file read vulnerability.
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 bombobombone/cve-2026-102971
Sanitized report and loopback-only PoC for CVE-2026-102971, a MediaWiki REST revision response leaking hidden revision author user IDs.
 wuyou6956-glitch/cve-2026-85706
Python PoC and writeup for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass on repository…
 yairhinkis/cve-2026-56096
Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
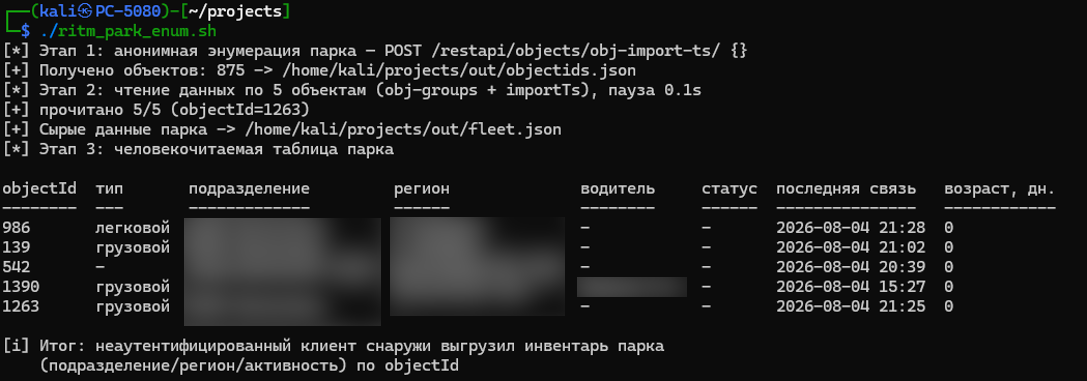 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 muradislamzada/cve-2026-93528
Technical analysis, proof of concept, and responsible disclosure timeline for CVE-2026-93528, an unauthenticated order data disclosure in NP Quote…
 squeeze440/gortex-poc
PoC — symlink following to out-of-repo content disclosure via search_text in Gortex (GHSA-6vhf-4wcm-2r83, CVE-2026-87003, CVSS 5.5).