secure-headers-project

OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.

OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.

Repository for CoSAI Workstream 4, Secure Design Patterns for Agentic Systems

Educational collection of CVE proof-of-concept resources and vulnerability research material for authorized lab testing, defensive study, and secure…

OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…

Artifacts for the Branch Target Reuse (BTR) Spectre-v2 attack research, including microarchitecture experiments, attack-surface analysis of JIT…

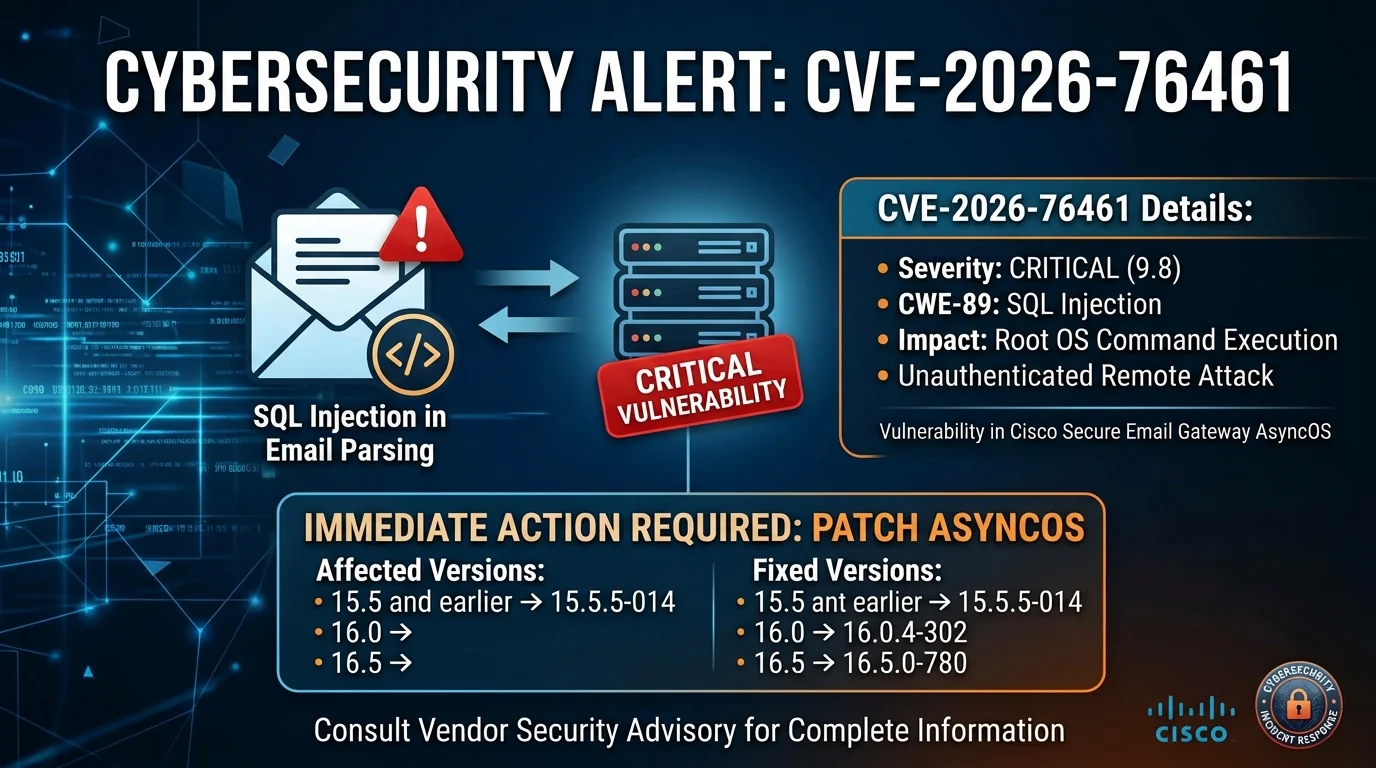
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…

Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…

Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…

Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…

Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…

Sanitized offline fixture verifier for CVE-2026-81861 in SCADAPack Secure Lock

Provably secure linguistic steganography embedding secret messages into LLM-generated text via rotation range-coding. Includes embed, extract, and…

Linux kernel double free in Xen privcmd driver

AegisGraph: graph-based application-layer assessment evidence platform for Secure Messaging Applications (SMAs). DARPA ASEMA HR0011SB20254-12 Tier 3…

Detailed disclosure of CVE-2025-47423: Local File Inclusion in Personal Weather Station Dashboard 12_lts. Includes PoC, vulnerable code analysis, and…

Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…

CVE-2026-20251 — Splunk Secure Gateway jsonpickle deserialization RCE (CVSS 8.8) | ReactiveZero Security Research

Proof-of-concept exploiting the Toshiba qiomem.sys driver to achieve arbitrary physical memory read/write from ring 3, with a companion writeup.