

SecretSifter
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
ai-securityapi-securitydefensive-tools+7
5
owasp/secretsifterOWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 bombobombone/cve-2026-103585
Sanitized report and loopback-only PoC script demonstrating stored XSS via javascript: license URLs in MediaSearch QuickView (CVE-2026-103585).
 bombobombone/cve-2026-103584
Sanitized report and loopback-only PoC script for CVE-2026-103584, a javascript: URL scheme XSS in MediaWiki CommonsMetadata LicenseUrl rendering.
 nstarke/egodeath
A JavaScript Obfuscator based on Cryptographic Indistinguishability Obfuscation techniques
 sneakynachos/cve-2026-74936-gc-potato
Reproduction of a WebAssembly use-after-free vulnerability in Mozilla's JavaScript engine, demonstrating a deterministic race condition and providing…
 ercihan/cve-2026-34621
Technical analysis of Adobe Acrobat JavaScript trust boundary flaw, documenting native handler mappings and privilege-gating logic for CVE-2026-34621.
 shadowopcode/desckvb-rat
Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
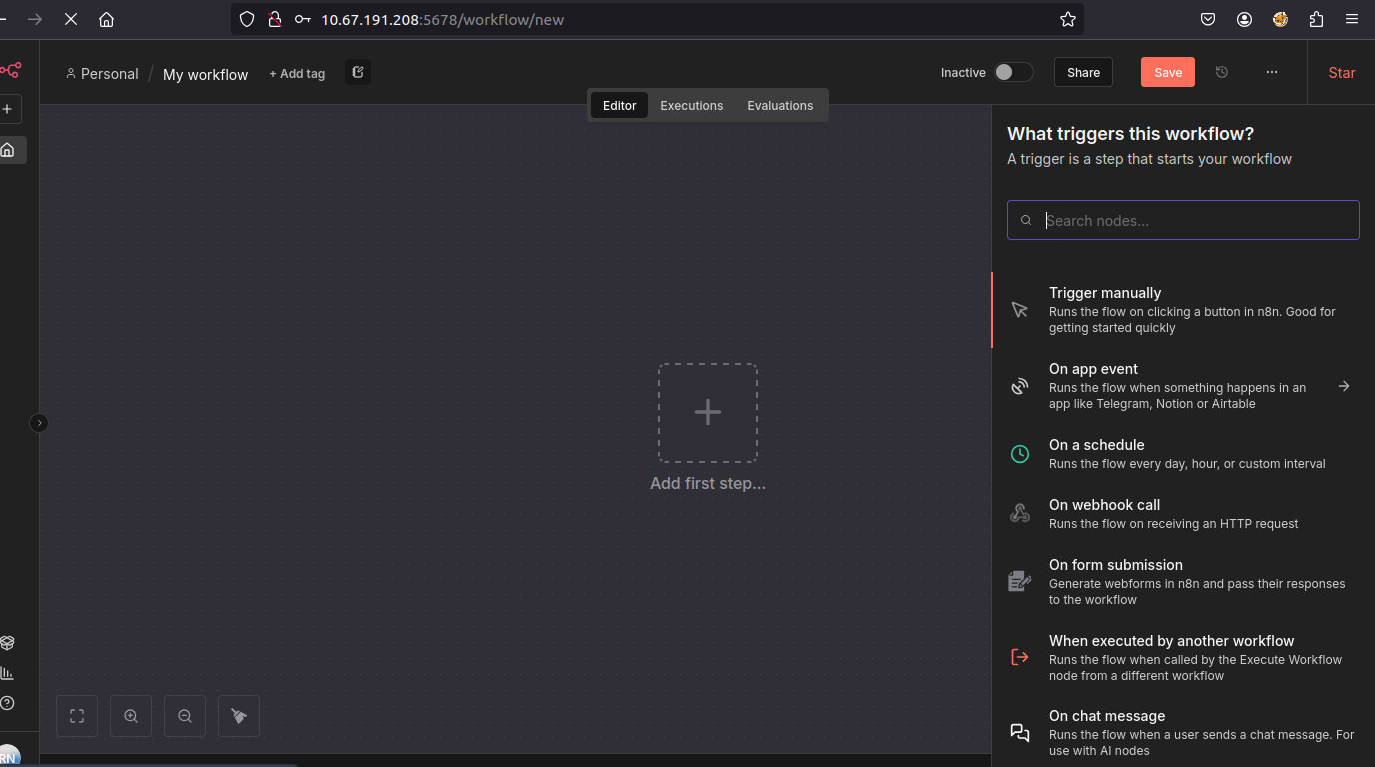 rianjuniorsf/analysis-and-poc-n8n-cve-2025-68613
Technical study of the CVE-2025-68613 vulnerability in n8n, covering affected versions, laboratory exploration scenario, offensive and defensive…