

terrapod-PoC
 squeeze440/terrapod-poc
PoC — missing authorization on the platform-wide GPG trust-anchor store in Terrapod (GHSA-6qrc-597p-mrp9, CVE-2026-87006, CVSS 6.5).
authentication-authorizationexploitationpapers-research+4
squeeze440/terrapod-pocPoC — missing authorization on the platform-wide GPG trust-anchor store in Terrapod (GHSA-6qrc-597p-mrp9, CVE-2026-87006, CVSS 6.5).
 bombobombone/cve-2026-73309
Proof-of-concept and technical write-up for CVE-2026-73309, an OAuth2 authentication bypass in XenForo before 2.3.13. Demonstrates empty…
 microsoft/security-101
8 Lessons, Kick-start Your Cybersecurity Learning.
 chelof100/acp-framework-en
Agent Control Protocol (ACP) — Official English specification. Cryptographically verifiable authorization architecture for autonomous AI agents.
 oguz-kagan-akar/cve-2026-41940-analysis
Technical analysis of the cPanel/WHM auth bypass
 0xmrma/cve-2026-46552
NocoDB Shared-Base Links Could Invite Real Base Members and Survive Share Revocation
 muhammedhussein17/keycloak
Security research disclosing CVE-2026-9794, an unauthenticated client ID enumeration flaw in Keycloak SAML ECP via faultstring oracle, fixed in…
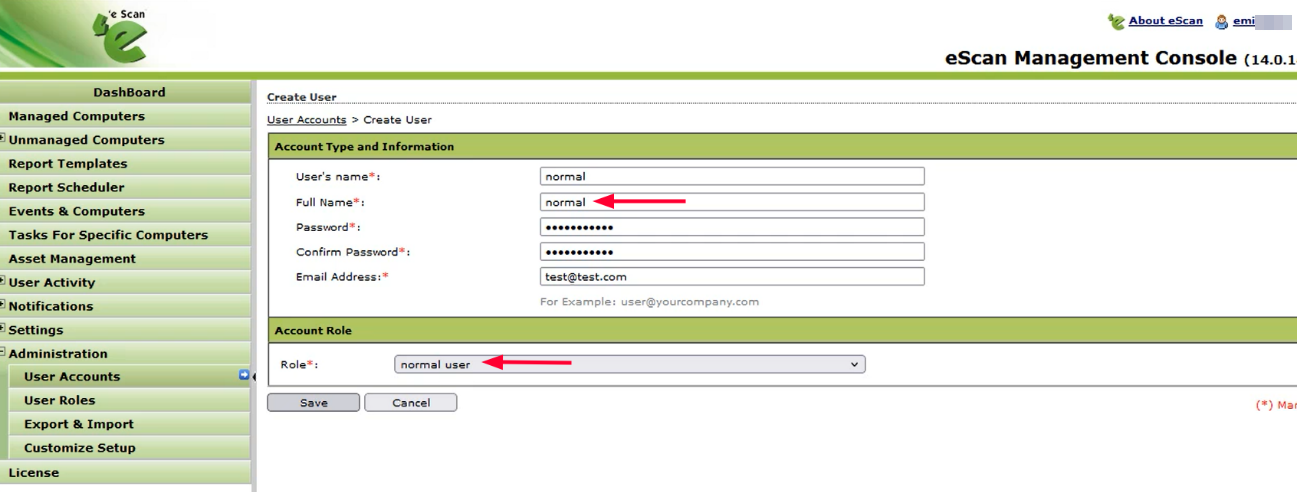 sahiloj/cve-2023-33730
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…
 yafiah-darwesh/cs50-cyber-paloalto-oauth
CS50 Cybersecurity final project — Palo Alto OAuth token breach (CVE-2024-3400)
 threedr3am/learnjavabug
Java安全相关的漏洞和技术demo,原生Java、Fastjson、Jackson、Hessian2、XML反序列化漏洞利用和Spring、Dubbo、Shiro、CAS、Tomcat、RMI、Nexus等框架\中间件\功能的exploits以及Java Security…
 karlemilnikka/cve-2023-1430
Responsible disclosure of unpatched vulnerability in FluentCRM by WPManageNinja