
sqlancer
 sqlancer/sqlancer
Automated testing to find logic and performance bugs in database systems
database-securityeducationfuzzing+2
sqlancer/sqlancerAutomated testing to find logic and performance bugs in database systems
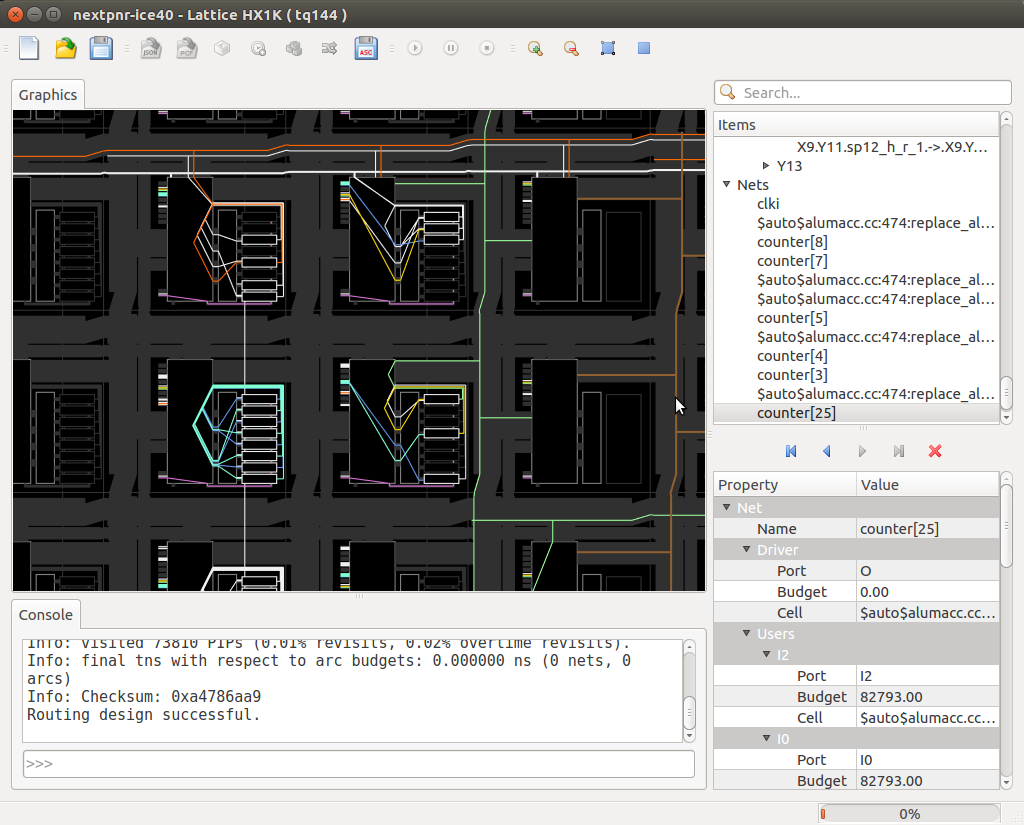 yosyshq/nextpnr
nextpnr portable FPGA place and route tool
 google/bindiff
Quickly find differences and similarities in disassembled code
 tamarin-prover/tamarin-prover
Symbolic verification tool for security protocols using multiset rewriting and constraint solving to prove secrecy, authentication, and equivalence…
 ramenfast/zenfone9-root
Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
 ull0a/bdapiutil-bydov
C++ Windows research tool for studying the BdApiUtil64.sys vulnerable driver and CVE-2024-51324
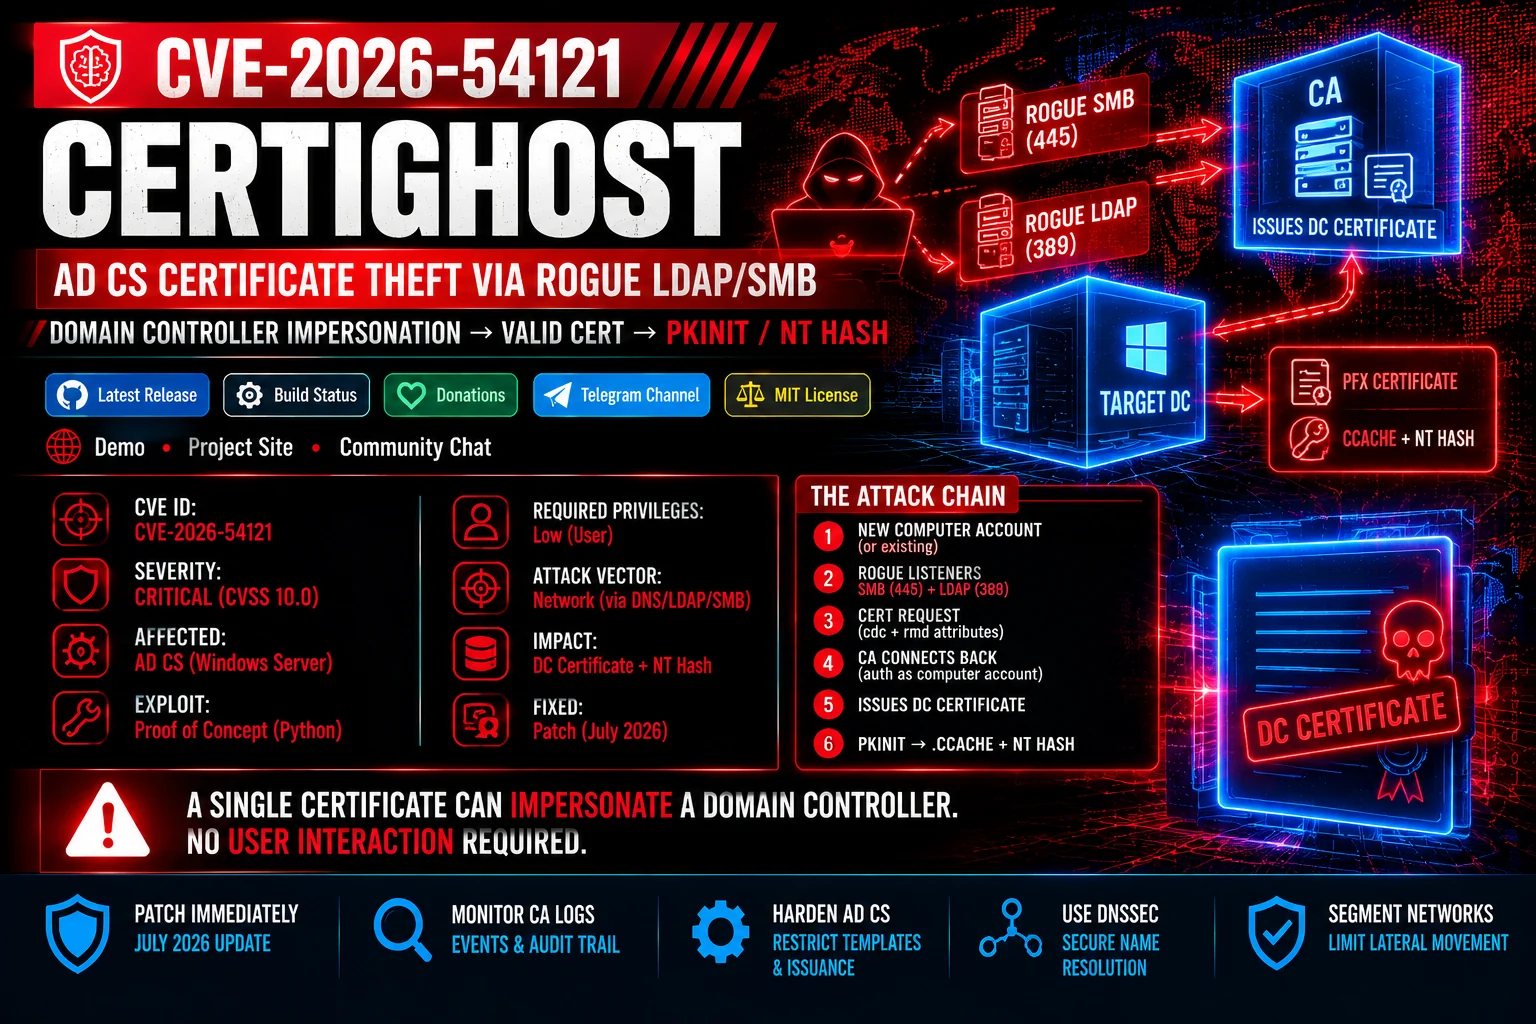 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 zerodayevil/cve-2026-20805-poc
Proof-of-concept exploit code for CVE-2026-20805, demonstrating the vulnerability for security research and validation.
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 brainbob/cve-2026-76578
Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
 bombobombone/cve-2026-73309
Proof-of-concept and technical write-up for CVE-2026-73309, an OAuth2 authentication bypass in XenForo before 2.3.13. Demonstrates empty…
 squeeze440/terrapod-poc
PoC — missing authorization on the platform-wide GPG trust-anchor store in Terrapod (GHSA-6qrc-597p-mrp9, CVE-2026-87006, CVSS 6.5).
 mods20hh/zerologon-poc-dc-pwn
Zerologon (CVE-2020-1472) Proof-of-Concept application - Critical Active Directory vulnerability exploitation tool.
 chelof100/acp-framework-en
Agent Control Protocol (ACP) — Official English specification. Cryptographically verifiable authorization architecture for autonomous AI agents.
 cmu-sei/pharos
Automated static analysis tools for binary programs
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…