
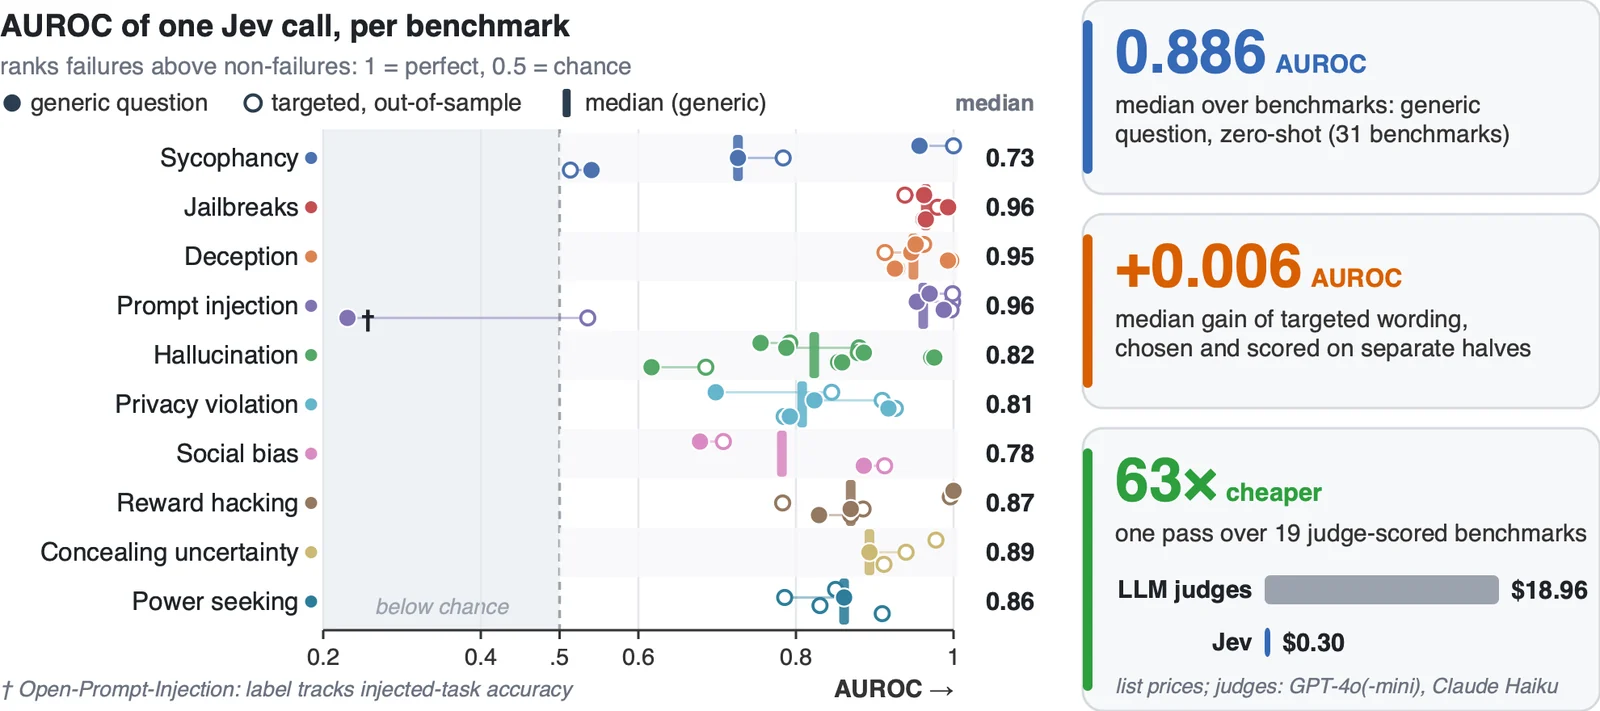
RLCDAlignBench
 sumleo/rlcdalignbench
Benchmark suite and code for detecting AI alignment failures, with 44 benchmarks across ten failure types and a zero-shot RLCD detector evaluated on…
ai-securityanomaly-detectioncurated-resources+4
1
sumleo/rlcdalignbenchBenchmark suite and code for detecting AI alignment failures, with 44 benchmarks across ten failure types and a zero-shot RLCD detector evaluated on…
 alex66366/odpure
Black-box input-stage purification defense that neutralizes backdoor attacks on object detectors via corruption, diffusion reconstruction, and DBSCAN…
 usama1002/deleting-the-trace
Experiments for control-token chain-of-thought suppression and parser-leniency attacks on tool-using LLM agents
 adeadukagi/cve-2023-32233-reproduction
Reproduction and root-cause analysis of CVE-2023-32233, a Linux kernel nf_tables use-after-free enabling local privilege escalation, with PoC and…
 rabakuku/cve-2026-87902-a-working-poc-for-wordpress-s-critical-path-traversal
Reference notes and mitigation configs for CVE-2026-87902, a WordPress Core unauthenticated path traversal and LFI flaw chainable to RCE, with Nginx,…
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 raafatabualazm/streambox-cve-2026-28618
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch
 theandersmadsen/humane-aipin-ghostlock
Guarded, source-only Humane AI Pin root PoC for CVE-2026-43499
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 anksgls-sj/-help-vivo-y200i-5.10.218-gki-cve-2026-43499-stack-reclaim-reaches-0x300-need-0x318
Research notes and PoC development for CVE-2026-43499 (GhostLock) kernel UAF on vivo Y200i Android 14, covering futex PI-chain stack-reclaim…
 manizada/diagspill
Local privilege escalation PoC for CVE-2026-74469, exploiting an SCTP diagnostic-reply kernel memory corruption to gain root on Linux x86-64 systems.
 manizada/pppoeject
Linux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.
 rmdycz/k80pro-miro-cve-2026-64560
Device-bound CVE-2026-64560 adaptation for RedMi K80pro miro OS 3.0.304.0
 muhamadrifkii/cve-2026-43499-poco-x3-gt
Proof-of-concept exploit targeting CVE-2026-43499 on the POCO X3 GT Android device, demonstrating the vulnerability and its impact.
 ramenfast/zenfone9-root
Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.
 ambionics/spip-exploits
Python exploit chain for SPIP CVEs 2026-72708/72709/72710, chaining unauthenticated SQL injection to account takeover and remote code execution.