
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
85 results
APEX_official preview

APEX_official

GitHubzhengxr930/apex_official

Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…

ai-assisted-reversingai-securityauthentication-authorization+5
6 days ago
h2spacex preview

h2spacex

GitHubnxenon/h2spacex

HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy‌ + Exploit Timing Attacks

exploitationfuzzingnetwork-security+6
2293 months ago
benign-instruction-bench preview

benign-instruction-bench

GitHublzwhehe/benign-instruction-bench

Re-evaluating prompt-injection detectors on LLM agent tool outputs (paper draft, scripts, scores)
ai-securitydefensive-toolseducation+3
8 days ago
CVE-2026-103977 preview

CVE-2026-103977

GitHubpervinzahidli/cve-2026-103977

Session-scoped TOTP rate limiting permits repeated verification attempts
authenticationauthentication-authorizationdefensive-tools+2
9 days ago
CVE-2026-102975 preview

CVE-2026-102975

GitHubbombobombone/cve-2026-102975

Sanitized report and local proof-of-concept script for CVE-2026-102975, a MediaWiki RevisionDelete API authorization bypass allowing suppression…
authentication-authorizationexploitationpapers-research+3
10 days ago
prompt_injection preview

prompt_injection

GitHubkevinchunye/prompt_injection

Benchmark harness measuring where prompt injection defenses fire in tool-using LLM agent pipelines, tracking canary tokens across exposed, persisted,…
adversarial-attackai-securityeducation+4
210 days ago
CLIPGuard preview

CLIPGuard

GitHubwsu-cyber-security-lab-ai/clipguard

Adversarial image perturbation tool that uses SAM segmentation and CLIP models to evade AI-based scam image classifiers for security research.
adversarial-attackai-securitydefensive-tools+2
4 months ago
opace6-cve-2026-64560 preview

opace6-cve-2026-64560

GitHubwangs-official/opace6-cve-2026-64560

Temporary root tool for OnePlus Ace 6 that exploits the CVE-2026-64560 Linux kernel POSIX CPU timer use-after-free to gain root until reboot, without…
android-securitybinary-exploitationexploitation+6
215 days ago
opace6-cve-2026-64560 preview

opace6-cve-2026-64560

GitHubqingle009/opace6-cve-2026-64560

OnePlus Ace 6 temporary root tool (CVE-2026-64560) - device-verified port with corrected bootidParent address
android-securitybinary-exploitationexploitation+7
712 days ago
Darkcloak preview

Darkcloak

GitHub0x574r/darkcloak

Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
binary-analysisfingerprint-spoofingids-ips-evasion+6
143 months ago
CVE-2026-94609 preview

CVE-2026-94609

GitHubanthonyk2923/cve-2026-94609

Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
api-securityauthentication-authorizationeducation+6
16 days ago
deleting-the-trace preview

deleting-the-trace

GitHubusama1002/deleting-the-trace

Experiments for control-token chain-of-thought suppression and parser-leniency attacks on tool-using LLM agents
adversarial-attackai-securityexploitation+3
118 days ago
discord-crasher preview

discord-crasher

GitHubaftermathlabs/discord-crasher

Some bugs found via binary instrumentation and fuzzing
binary-analysisdynamic-analysis-sandboxingexploitation+5
2325 days ago
zenfone9-root preview

zenfone9-root

GitHubramenfast/zenfone9-root

Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.
android-securitybinary-exploitationexploitation+7
423 days ago
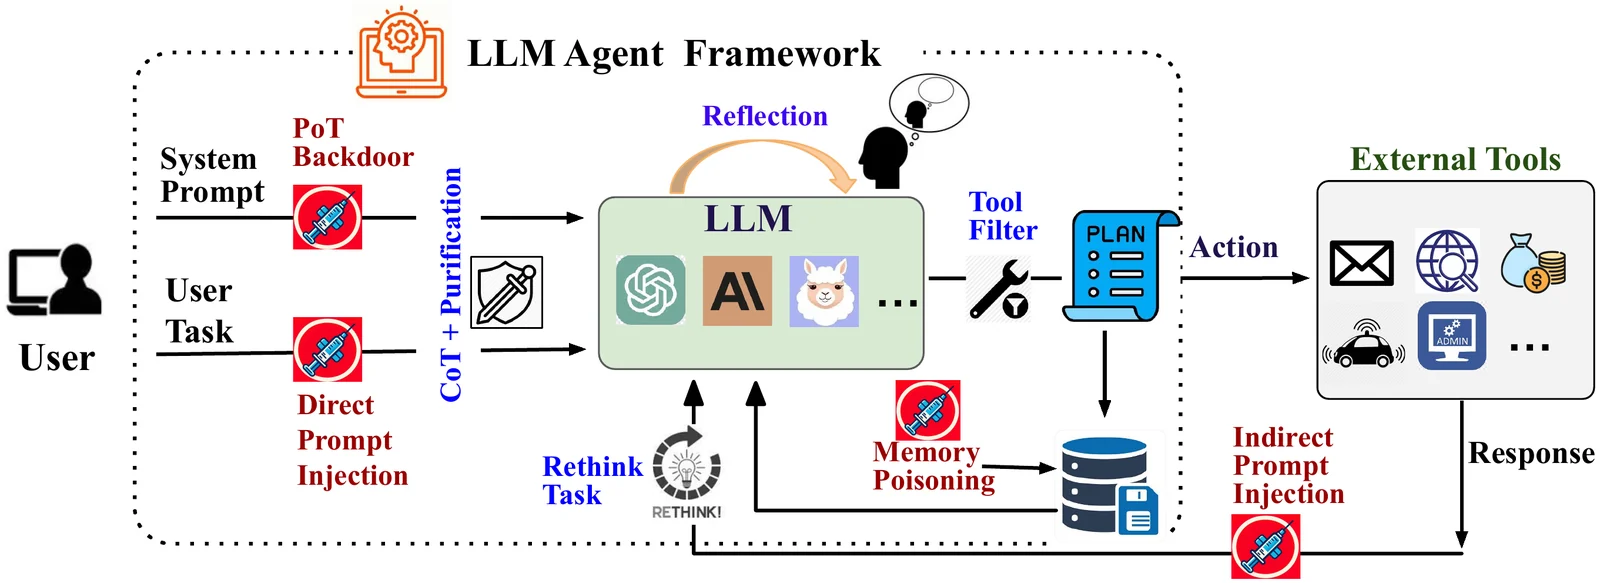
Defenses-for-Tool-Integrated-LLM preview

Defenses-for-Tool-Integrated-LLM

GitHubxiaoyan-lisa/defenses-for-tool-integrated-llm

Research code and experiments for defending tool-integrated LLM agents against adversarial attacks, extending Agent Security Bench with new defense…
adversarial-attackai-securitydefensive-tools+3
1 year ago
tamarin-prover preview

tamarin-prover

GitHubtamarin-prover/tamarin-prover

Symbolic verification tool for security protocols using multiset rewriting and constraint solving to prove secrecy, authentication, and equivalence…
cryptographyeducationpapers-research+2
54923 days ago
keycloak preview

keycloak

GitHubmuhammedhussein17/keycloak

Security research disclosing CVE-2026-9794, an unauthenticated client ID enumeration flaw in Keycloak SAML ECP via faultstring oracle, fixed in…
authenticationidentity-managementinformation-gathering+3
4 months ago
sshamble preview

sshamble

GitHubrunzeroinc/sshamble

Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.

authenticationdefensive-toolsinformation-gathering+6
1.2k1 month ago
Previous12345Next