
authorship-not-sabotage
 shubsds/authorship-not-sabotage
Code and paper source for a NeurIPS EvoRobust study showing simple bag-of-words and metadata features beat most AI control monitors at detecting…
ai-securitycode-analysiseducation+3
1
shubsds/authorship-not-sabotageCode and paper source for a NeurIPS EvoRobust study showing simple bag-of-words and metadata features beat most AI control monitors at detecting…
 gmh5225/quickpgtrigger
The stress testing of your PG bypass [old school project]
 mas0nshi/cve-2026-112445
Proof-of-concept for CVE-2026-112445, a macOS local privilege escalation where an unprivileged console user abuses the launchd com.apple.xpc.uscwoap…
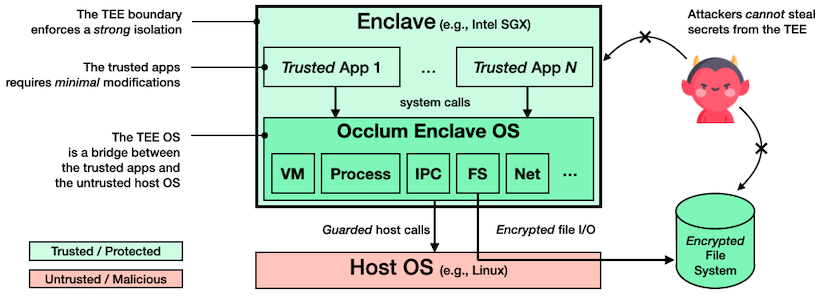 occlum/occlum
Memory-safe, multi-process library OS for Intel SGX that runs legacy applications inside enclaves with encrypted filesystems and lightweight…
 scyrix-llc/cve-2026-88773
Technical analysis of a NetScaler nsppe HTTP/1.1 chunk-size integer-wrap request smuggling flaw, with disassembly, wire-level PoC flows, and firmware…
 oscerd/cve-2026-101259
Runnable proof-of-concept reproducer for CVE-2026-101259, demonstrating error-message disclosure in Apache Camel camel-coap consumers on Spring Boot…
 oscerd/cve-2026-95629
Runnable proof-of-concept reproducer for CVE-2026-95629, a path-traversal flaw in Apache Camel camel-docling where the output-path header reaches…
 s12cybersecurity/whatpatchguardprotects
Reference of all kernel structures, routines, and MSRs monitored by PatchGuard (KPP) on Windows.
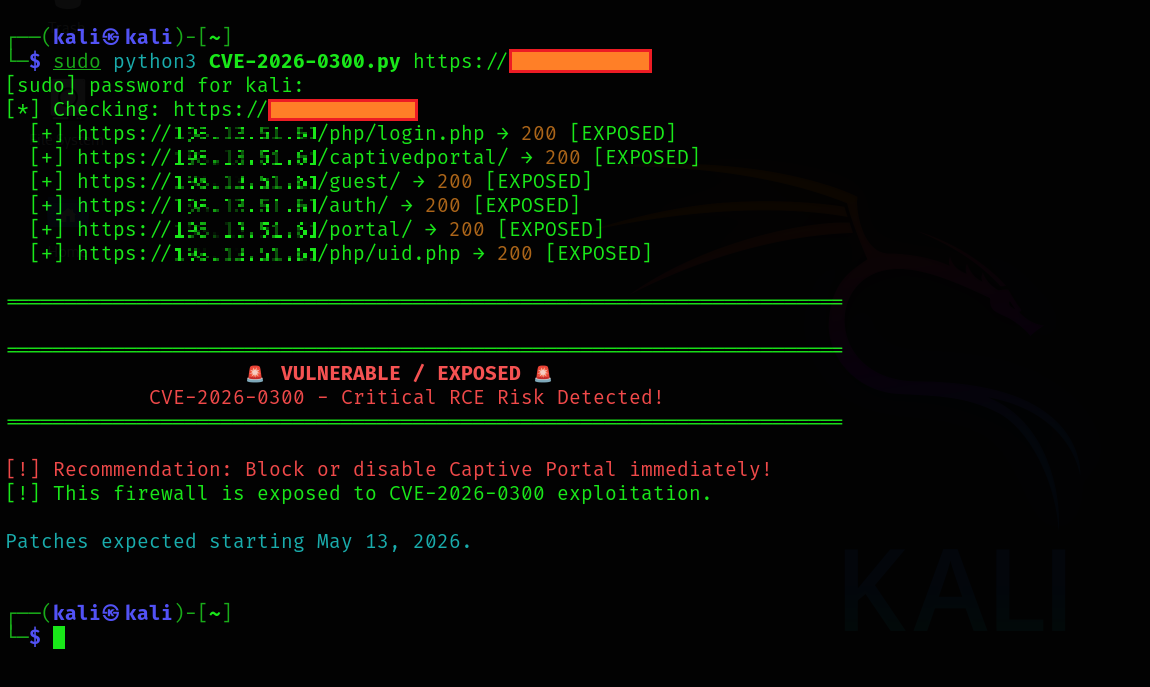 0xredash/cve-2026-0300
Advisory and technical analysis of CVE-2026-0300, a critical unauthenticated buffer overflow RCE in Palo Alto PAN-OS User-ID portals, with affected…
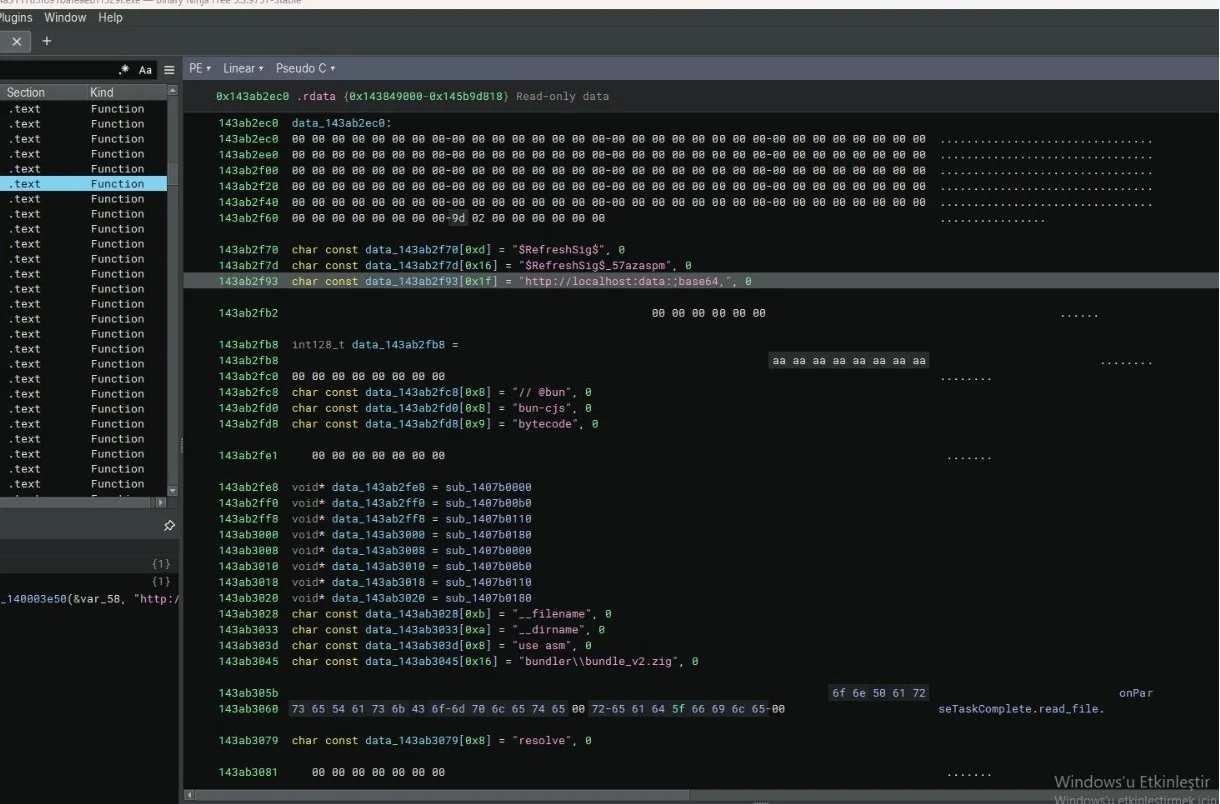 kaandemir993/nwh-stealer-analysis-fileless-bun-runtime-execution-clipboard-image-theft-cloud-c2-aws-r2-
Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…
 faicalom/zte-mf904q-reverse-engineering
Open research documentation and source review for ZTE MF904Q bootloader, firmware extraction, and reverse engineering.
 requie/ai-red-teaming-guide
A comprehensive guide to adversarial testing and security evaluation of AI systems, helping organizations identify vulnerabilities before attackers…
 akil-x/r00tlib-catalog
A community-curated knowledge hub and catalog for computer science, cybersecurity & software engineering books
 gameworkerkim/telegram-0-click-rce-security-vulnerability-analysis-report
I have submitted a report on the Telegram sticker vulnerability, SECURITY VULNERABILITY ANALYSIS REPORT Telegram 0-Click RCE vulnerability…
 ua-spectral/botlens
Research artifact and MCP server that audits security and privacy concerns in third-party Discord bots via large-scale review analysis, LLM labeling,…
 jefffffffu/priv-qdnn
Research codebase for privacy evaluation of quantized neural networks: trains target/shadow models under PTQ/QAT and runs membership-inference…
 chakshugupta13/lab
Code artifacts from research paper implementations
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis