
CVE-2026-85706
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
data-exfiltrationexploitationinformation-gathering+7
solivaquaant/cve-2026-85706Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 mouteee/autonomous-offensive-llm-handbook
A deterministic harness and handbook for autonomous offensive LLM agents, enforcing authorization, scope, and evidence gates to ensure reproducible…
 jianshuod/ipi-exposure-signal
Research pipeline for detecting latent indirect prompt-injection exposure signals in agentic LLMs via hidden-state probing, including trace…
 jvdsn/crypto-attacks
Python implementations of cryptographic attacks and utilities.
 mr-xn/blackhat_usa2022
BLACKHAT USA2022 PDF Public
 quarkslab/conf-presentations
Quarkslab conference talks
 mr-xn/blackhat_asia2023
Black Hat Asia 2023 PDF Public
 portswigger/css-the-bomb-inside-your-inbox
All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.
 spiralbl0ck/hackerlife.exe
Write up exploit failed chain and experience tryin to sell your first nday
 mamadou-keita/deeclip
Implementation of paper "DeeCLIP: A Robust and Generalizable Transformer-Based Framework for Detecting AI-Generated Images"
 keraattin/cve-2026-35031
Critical path traversal to RCE vulnerability in Jellyfin Media Server (CVSS 9.9). Includes proof-of-concept exploit, technical analysis, and…
 nu11secur1ty/cve-mitre
https://cve.mitre.org/
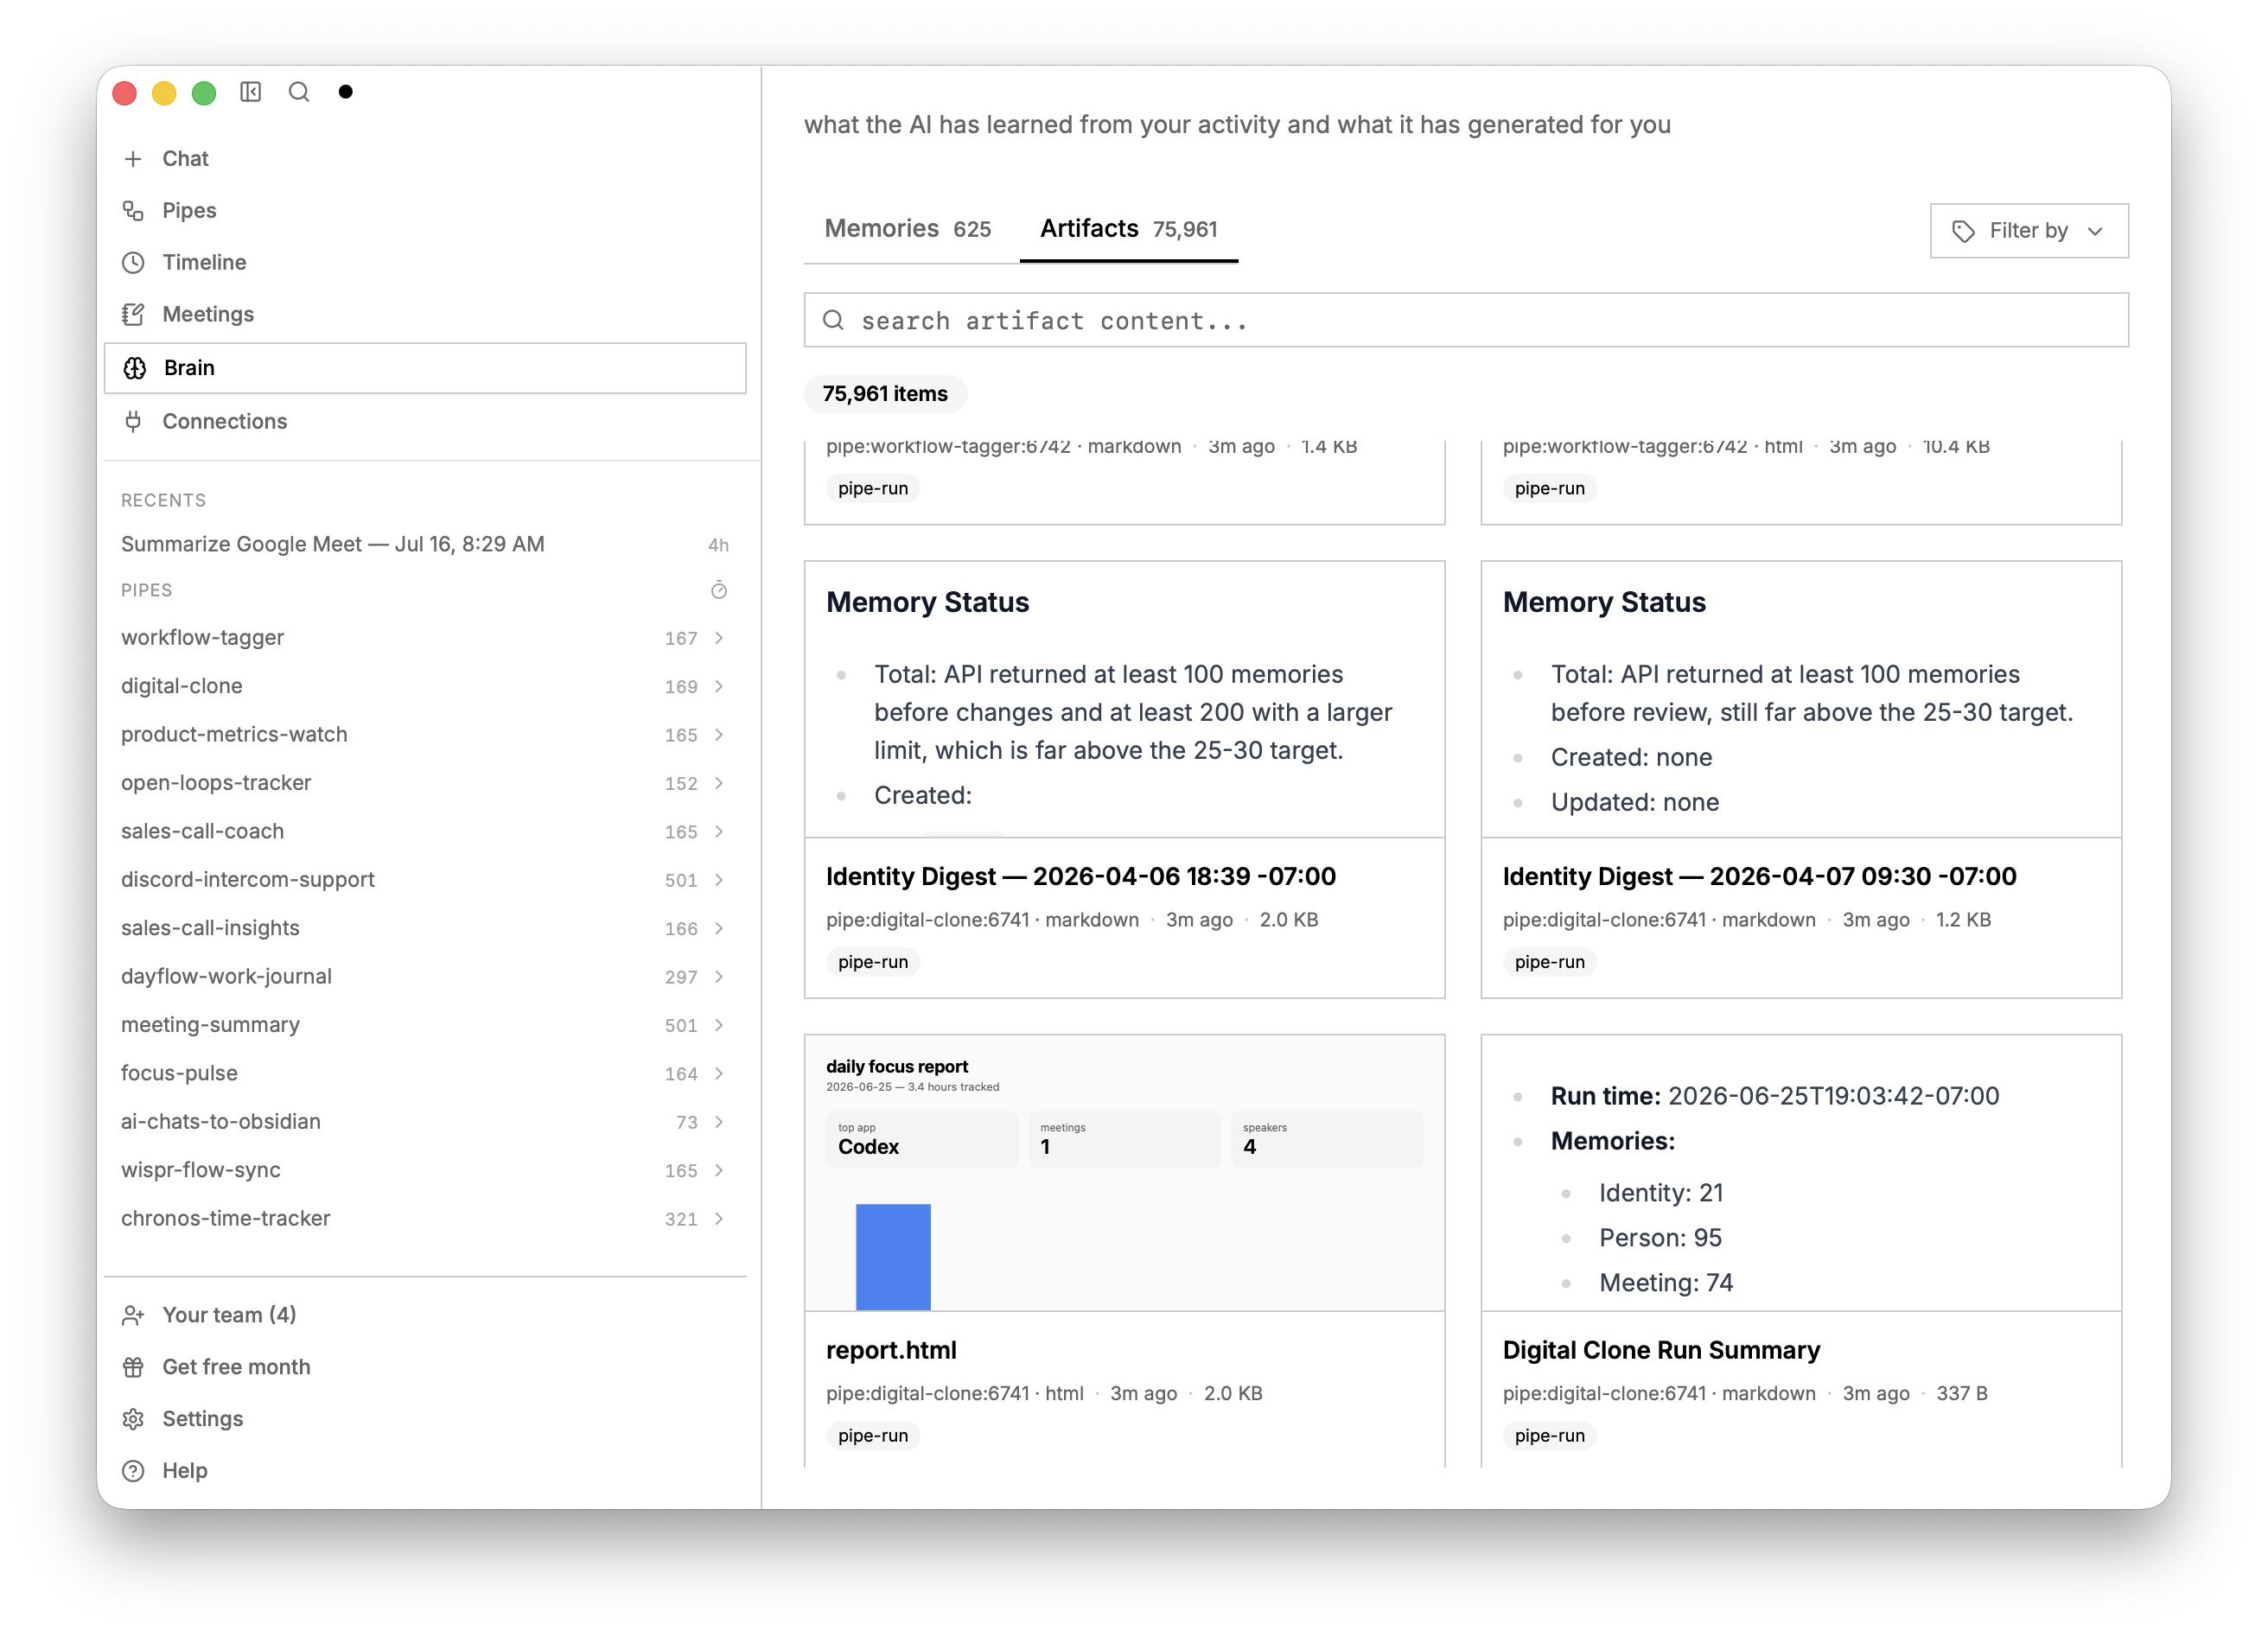 screenpipe/screenpipe
YC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…
 ibm/pgp-client-checker-cve-2021-33560
Tool to check whether a PGP client is affected by CVE-2021-33560
 gnoxter/mountain_goat
A PoC demonstrating techniques exploiting CVE-2016-5696 Off-Path TCP Exploits: Global Rate Limit Considered Dangerous
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025