
agentic-workflow-injection
 sushant-me/agentic-workflow-injection
Reproducible vulnerable and fixed GitHub Actions fixtures for agentic workflow injection (CVE-2026-44246), with measured detector coverage and…
ai-securitydevsecopseducation+4
sushant-me/agentic-workflow-injectionReproducible vulnerable and fixed GitHub Actions fixtures for agentic workflow injection (CVE-2026-44246), with measured detector coverage and…
 pvharmo2/gha-lab-733c168b88
Reproduces CVE-2026-44246, a prompt injection vulnerability in nnU-Net's GitHub Actions triage agent, demonstrating how issue content is inlined into…
 pvharmo2/gha-lab-23db52563c
Security-research lab: reproduction of CVE-2025-10894 (PR-title injection in GitHub Actions) — snapshot of nrwl/nx
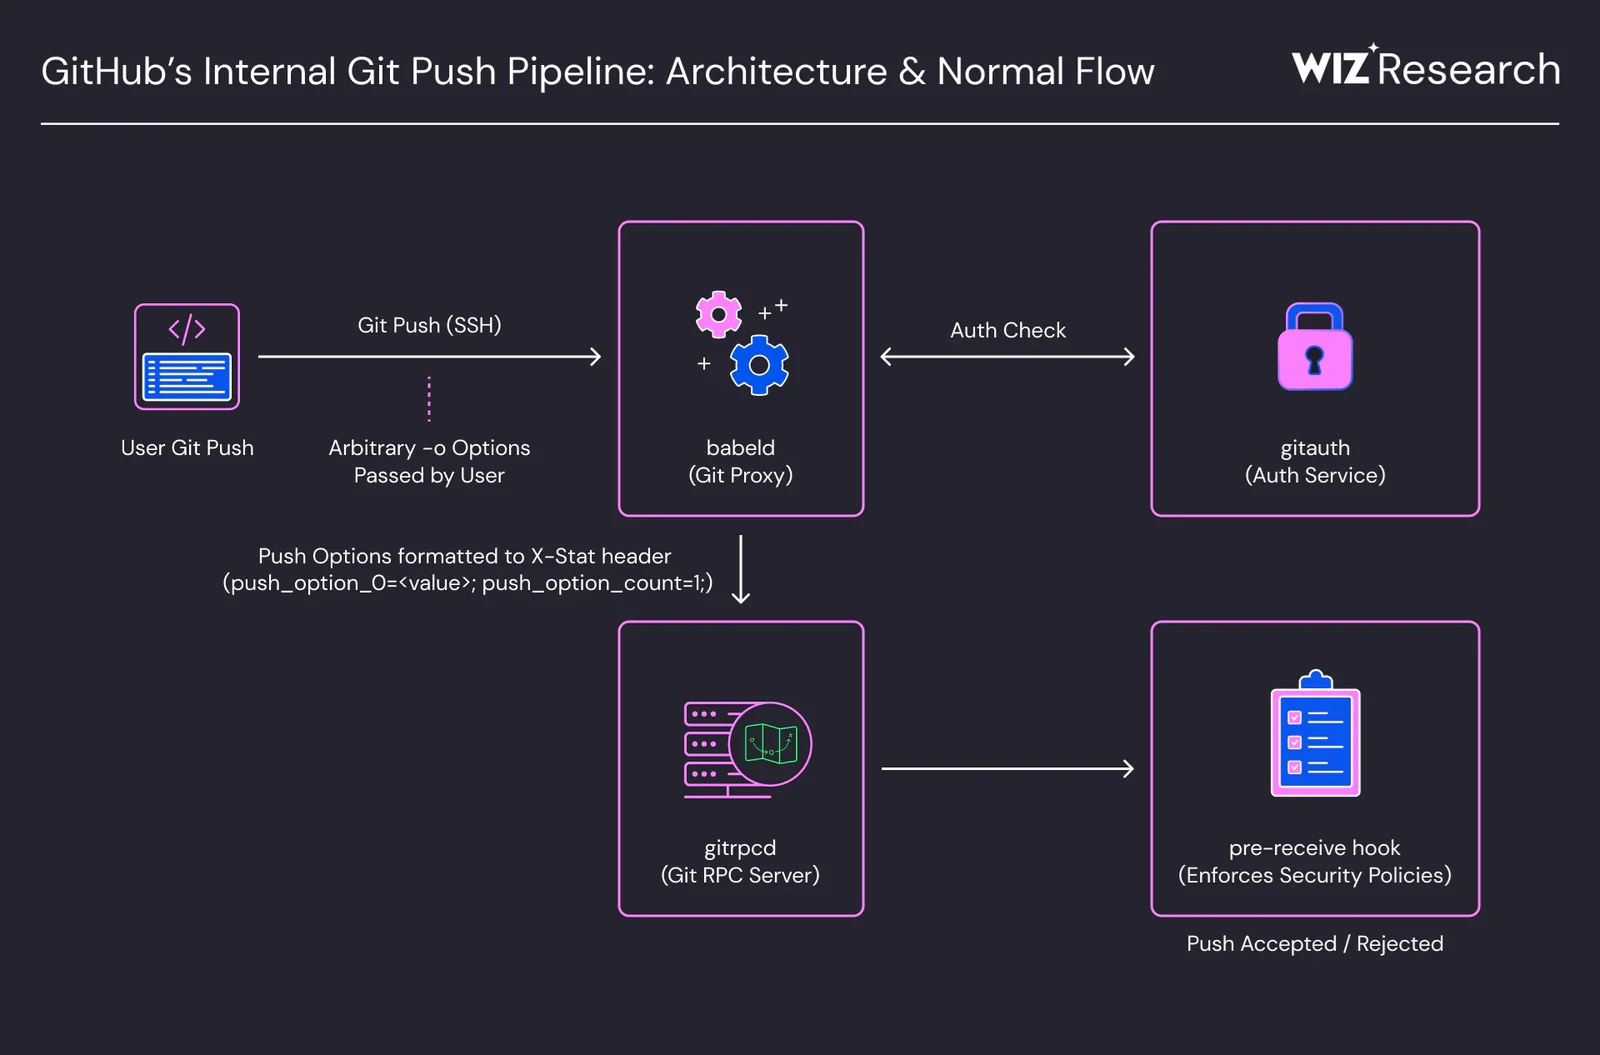 5kr1pt/cve-2026-3854
Technical breakdown of CVE-2026-3854, a GitHub RCE via header injection in git push, explaining the vulnerability, exploitation technique, and…
 thuyimingli/backdoor-learning-resources
Curated list of backdoor learning papers, surveys, and toolboxes, organizing poisoning-based attacks and defenses in deep learning for researchers…
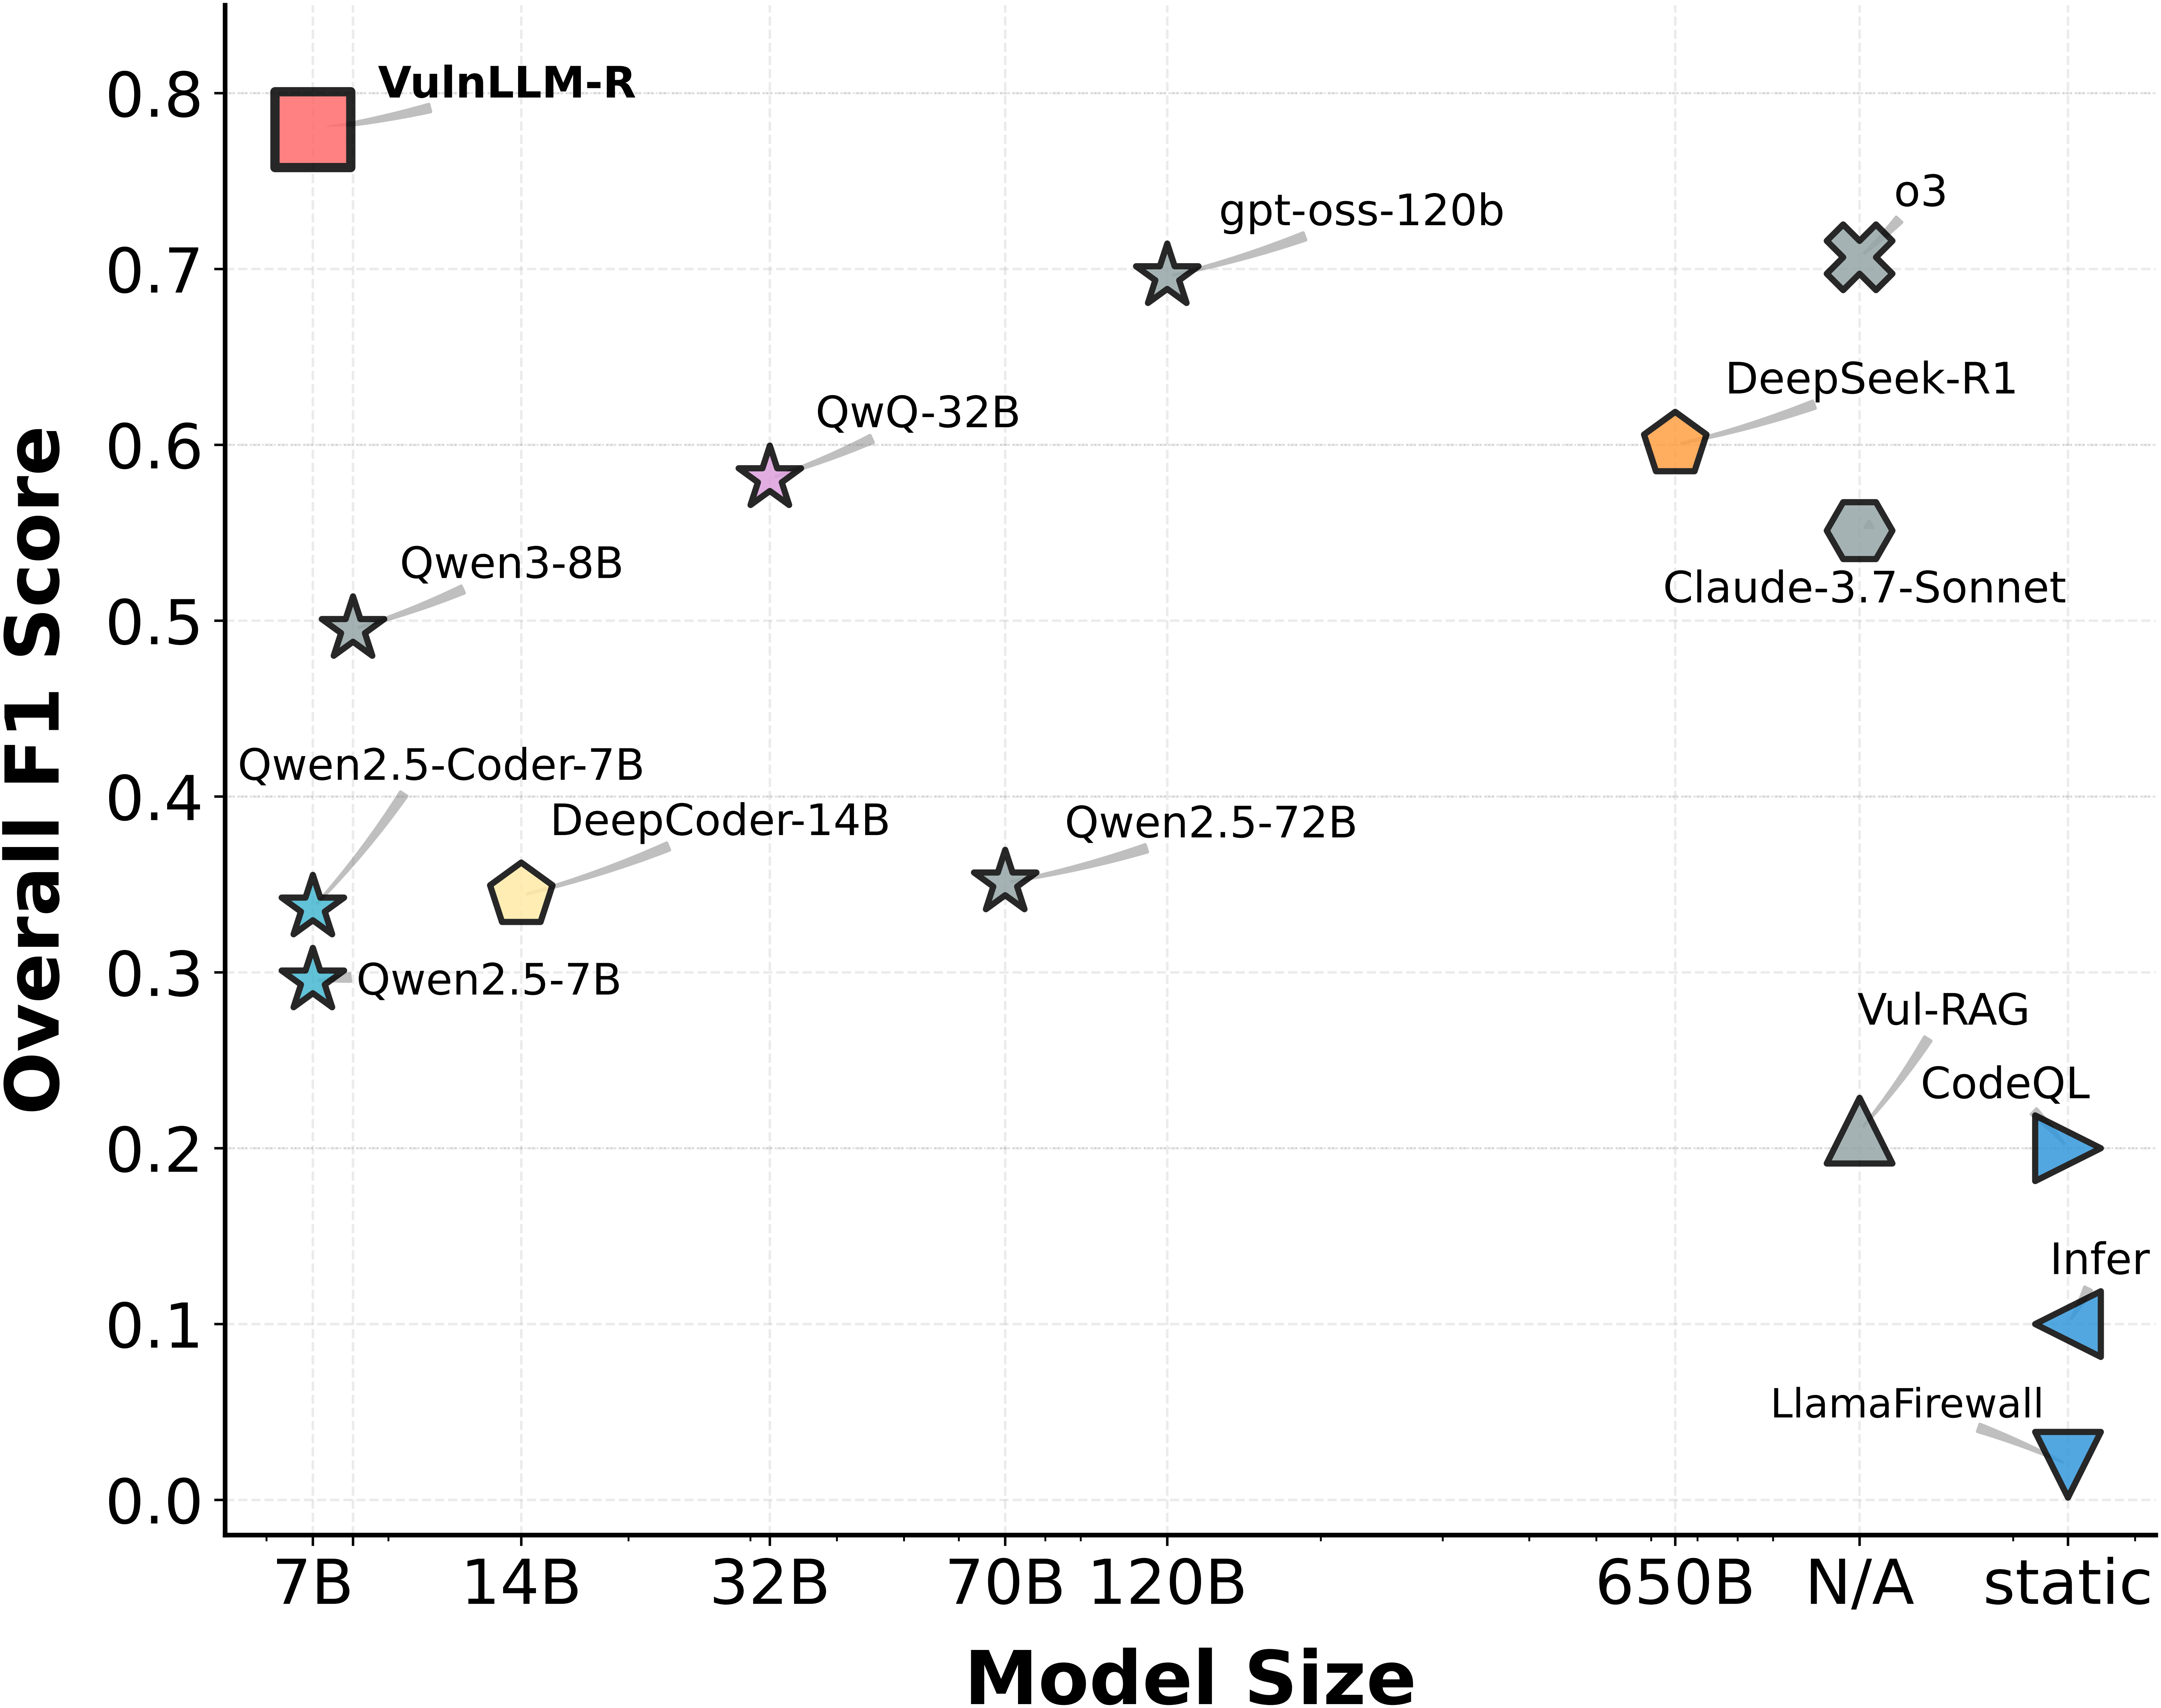 ucsb-mlsec/vulnllm-r
Specialized reasoning LLM for source-code vulnerability detection in C/C++ and Python, with dataset construction, SFT/DPO training, and…
 weizman/cve-2019-18426
Proof-of-concept exploit and technical analysis for CVE-2019-18426, covering open redirect, CSP bypass, persistent XSS, and file system read in…
 horkimhab/awesome-cybersecurity-resources
Curated collection of cybersecurity resources including tools, articles, and repositories, structured with YAML frontmatter and automated discovery…

 github/securitylab
Resources related to GitHub Security Lab
 metnew/write-ups
Curated collection of technical write-ups detailing RCE vulnerabilities in GitHub Desktop, GitHub CLI, and Claude Code, with CVE references and…
 patois/winmagic_sd
Technical Write-Up on and PoC Exploit for CVE-2020-11519 and CVE-2020-11520
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 zpxlz/cve-2024-3094
Obsidian notes about CVE-2024-3094
 lirantal/cve-2024-21532-poc-ggit
Proof-of-concept exploit for CVE-2024-21532, a command injection vulnerability in the ggit npm package's fetchTags API, demonstrating unsafe exec()…
 sbaresearch/whatsapp-census
Research tool for enumerating WhatsApp user accounts via phone number probing, demonstrating large-scale enumeration vulnerabilities and their…
 helloandrewpaul/reflected-xss-in-vvveb-cms-v1.0.7.2
CVE-2025-9728: Reflected XSS in Login Form (Email & Password Fields) Vvveb CMS v1.0.7.2