samsung_tizen_tv_root

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Research package demonstrating a leak-assisted ROP chain in Android media.swcodec via the CVE-2026-0006 APV decoder heap overflow, with payload…

Archived copy of the mod_plaintext.py "Internet Chemotherapy" IoT worm payload, preserved with archival references for malware research and…

Local proof-of-concept and sanitized report for CVE-2026-103441, a PHP object-injection flaw in the MediaWiki action=parse API that can reach RCE via…

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

Detection artifact generator for Citrix NetScaler CVE-2026-88771, exploiting a pre-auth command injection to achieve remote code execution against…

Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.

Docker-based lab reproducing CVE-2026-29057 Next.js request smuggling, comparing vulnerable 15.5.12 against patched 15.5.13 with a raw chunked HTTP…

Proof-of-concept exploit and payload generator for CVE-2026-22686, a sandbox escape in enclave-vm <2.7.0 enabling arbitrary code execution and…

Android kernel exploit research package for CVE-2026-43499, containing popsicle exploit source, embedded su payload, root bridge helper, and…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Firefox content->parent srcdoc forge (N-day, bug 2040160): forged PDocumentChannel with SrcdocData on a non-about:srcdoc URI -> attacker HTML served…

Generated CVE-2026-64633 analysis payloads with treatment/control document variants and a manifest mapping IDs and pairs for reproducing the…

Java deserialization vulnerability exploitation tool with payload generators for multiple marshallers (Jackson, XStream, SnakeYAML) and JNDI…

Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…

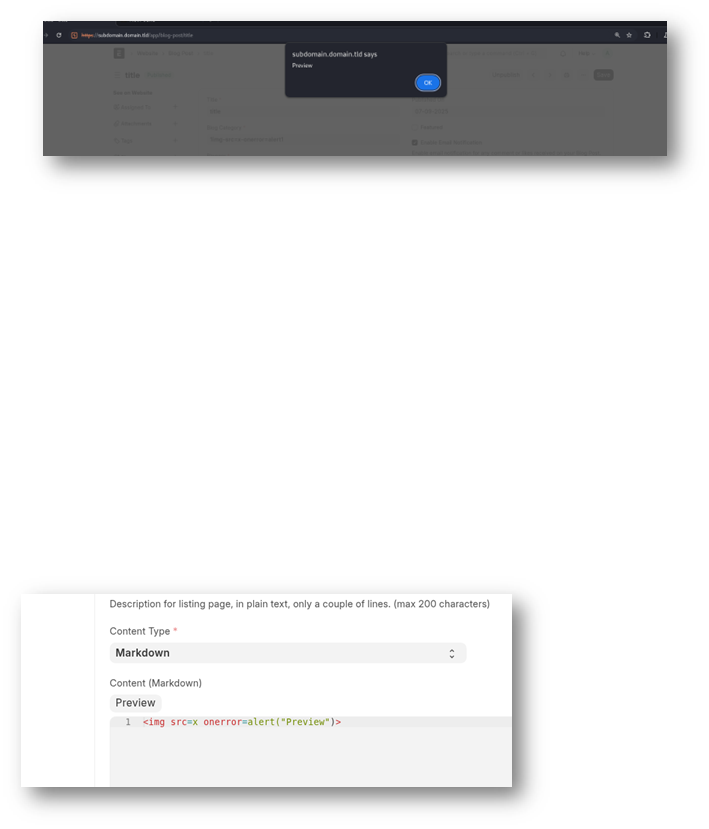
A stored cross-site scripting (XSS) vulnerability in the blog post feature of ERPNEXT v15.67.0 allows attackers to execute arbitrary web scripts or…

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

In-depth technical analysis of CVE-2021-22204 (ExifTool RCE) with PoC reproduction, payload construction, and Perl code review of the vulnerable DjVu…