
CVE-2022-22715
 vportal/cve-2022-22715
Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
binary-exploitationexploitationpapers-research+2
vportal/cve-2022-22715Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 abdul-kalam2000/retbleed-speculative-execution-poc
Reproduction of the Retbleed (CVE-2022-29900/29901) micro-architectural attack in gem5. RSB underflow, Flush+Reload side-channel leak, and a verified…
 vudangducminh/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel race condition enabling unprivileged writes to read-only files and privilege…
 camgoering/solarview-ics-vulnerability-analysis
Threat model and vulnerability analysis of Contec SolarView Compact (CVE-2022-29303)
 darioomatos/cve-2026-31431-copyfail
Educational analysis of CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD in-place operation, including technical root cause,…
 ericpardee/fire-hd-ownership
Owning a tablet Amazon kept shutting down — CVE-2022-38181 write-up, four AI models, and a blog
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 msm8916-mainline/cve-2022-22063
Security issue in the hypervisor firmware of some older Qualcomm chipsets
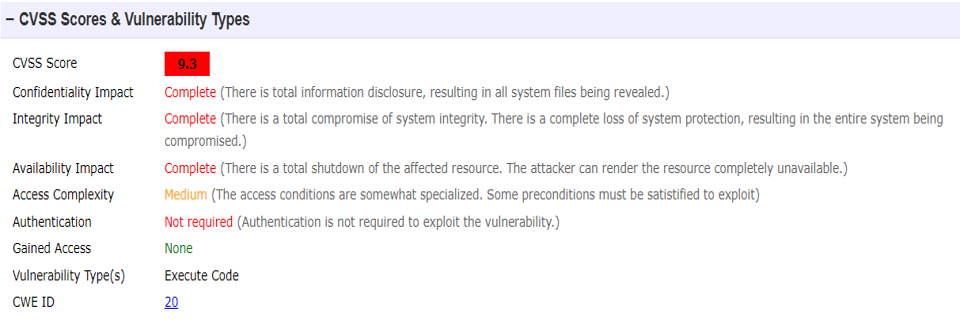 sreeram281997/cve-2022-21668-pipenv-rce-vulnerability
Detailed analysis of CVE-2022-21668, a critical RCE vulnerability in Pipenv's requirements.txt parsing, including bug code, exploit mechanics, and…
 thomasarmel/rollback_car_attack_proverif
ProVerif proof of concept of the Rollback attack on car keyfob (CVE-2022-37418, CVE-2022-36945 and CVE-2022-37305)
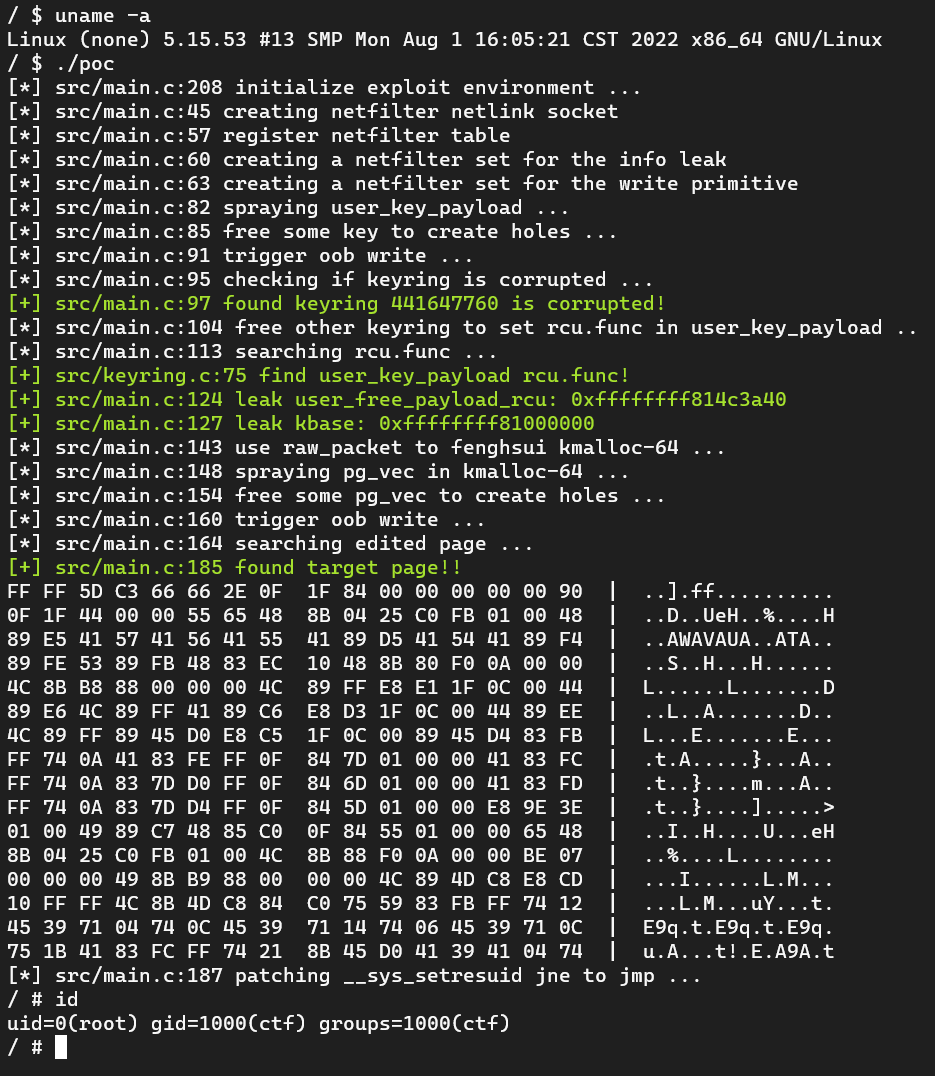 veritas501/cve-2022-34918
CVE-2022-34918 netfilter nf_tables 本地提权 POC
 heymrsalt/ais3-2024-project-d5team
Reappear-CVE-2022-21449-TLS-PoC
 scabench/jsonorg-fp3
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 scabench/jsonorg-fp1
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 scabench/fastjson-tp1fn1
a scenario based on CVE-2022-25845 yielding a TP for metadata based SCA but a FN if the callgraph is used