NWH-Stealer-Analysis-Fileless-Bun-Runtime-Execution-Clipboard-Image-Theft-Cloud-C2-AWS-R2-

Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

C implementation of a cache-based jamming agreement that establishes a cross-VM cache covert channel between co-located virtual machines for research…

Meaningful control of data in distributed systems.

Reproducer and analysis for CVE-2026-79986, a path traversal in Apache Camel camel-azure-files where share listing names escape the polled directory.

Apache Spark 4.2.0 - High - Remote - Privilege leftover - proxy-user defaultExtraClassPath

Disabled TLS Certificate Verification for HashiCorp Vault KMS in confluent-kafka

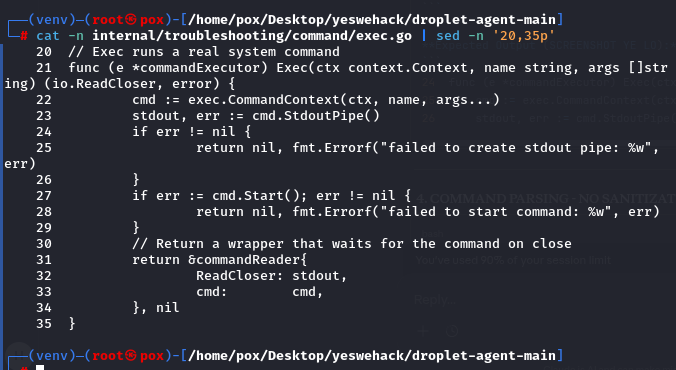
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).

OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…

Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…

Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.

Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)

Security-research lab reproducing CVE-2026-45132 (pwn request via pull_request_target chart-name injection in generate-schema.yaml) — snapshot of…

Technical whitepaper dissecting JioPC cloud VDI architecture, including hardware specs, session termination mechanisms, and security limitations,…

Reference implementation of LR+ post-quantum authentication over WebPKI CA context, with corpus pipeline, reconstruction, evaluation, and provenance…

Reproducible Docker lab and Python PoC for CVE-2026-82329, an unauthenticated auth-bypass in JFrog Artifactory leading to admin takeover, with…

Proof-of-concept exploit for CVE-2026-31431, a Linux kernel vulnerability affecting multiple distributions, with tested versions and a technical…

Proof-of-concept exploit for CVE-2026-31431, a Linux kernel vulnerability affecting multiple distributions, with a technical writeup and tested…

Technical writeup and proof-of-concept for CVE-2026-31431, a Linux kernel vulnerability affecting multiple distributions, with tested versions and…