AntiOreans-CodeDevirtualizer

IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…

IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…

Static reverse-engineering analysis of movement input heuristics in Source 2 engine, identifying structural edge cases in input automation and jump…

Reproduction of a WebAssembly use-after-free vulnerability in Mozilla's JavaScript engine, demonstrating a deterministic race condition and providing…

Educational presentation analyzing CVE-2021-21193, a use-after-free vulnerability in Google Chrome's Blink engine, including exploitation details and…

This repository contains a professional write-up of a path traversal vulnerability discovered in InvenTree's report template engine. This…

In-depth technical analysis of Cisco ISE RCE vulnerabilities, including exploitation techniques, evasion methods, and remediation strategies for…

Proof-of-concept for CVE-2026-2441, a Chrome CSS use-after-free leading to sandboxed renderer RCE. Includes three trigger methods, heap grooming, and…

An updated collection of resources targeting browser-exploitation.

A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…

ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.

A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance

CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…

Proof-of-concept exploit for CVE-2025-6554, a V8 JavaScript engine vulnerability allowing unauthorized access to uninitialized 'Hole' values via…

Critical Vulnerability (9.8) - RecordedFuture Triage dynamic analysis engine can fail to record malicious behavior when samples produce very…

Educational presentation detailing the exploitation of CVE-2021-21220, a V8 JIT type confusion leading to OOB access and RCE via WebAssembly, with…

Validates CVE-2026-48908 in Joomla SP Page Builder with unauthorized icon upload leading to PHP code execution. Includes auditd/PCAP evidence, event…

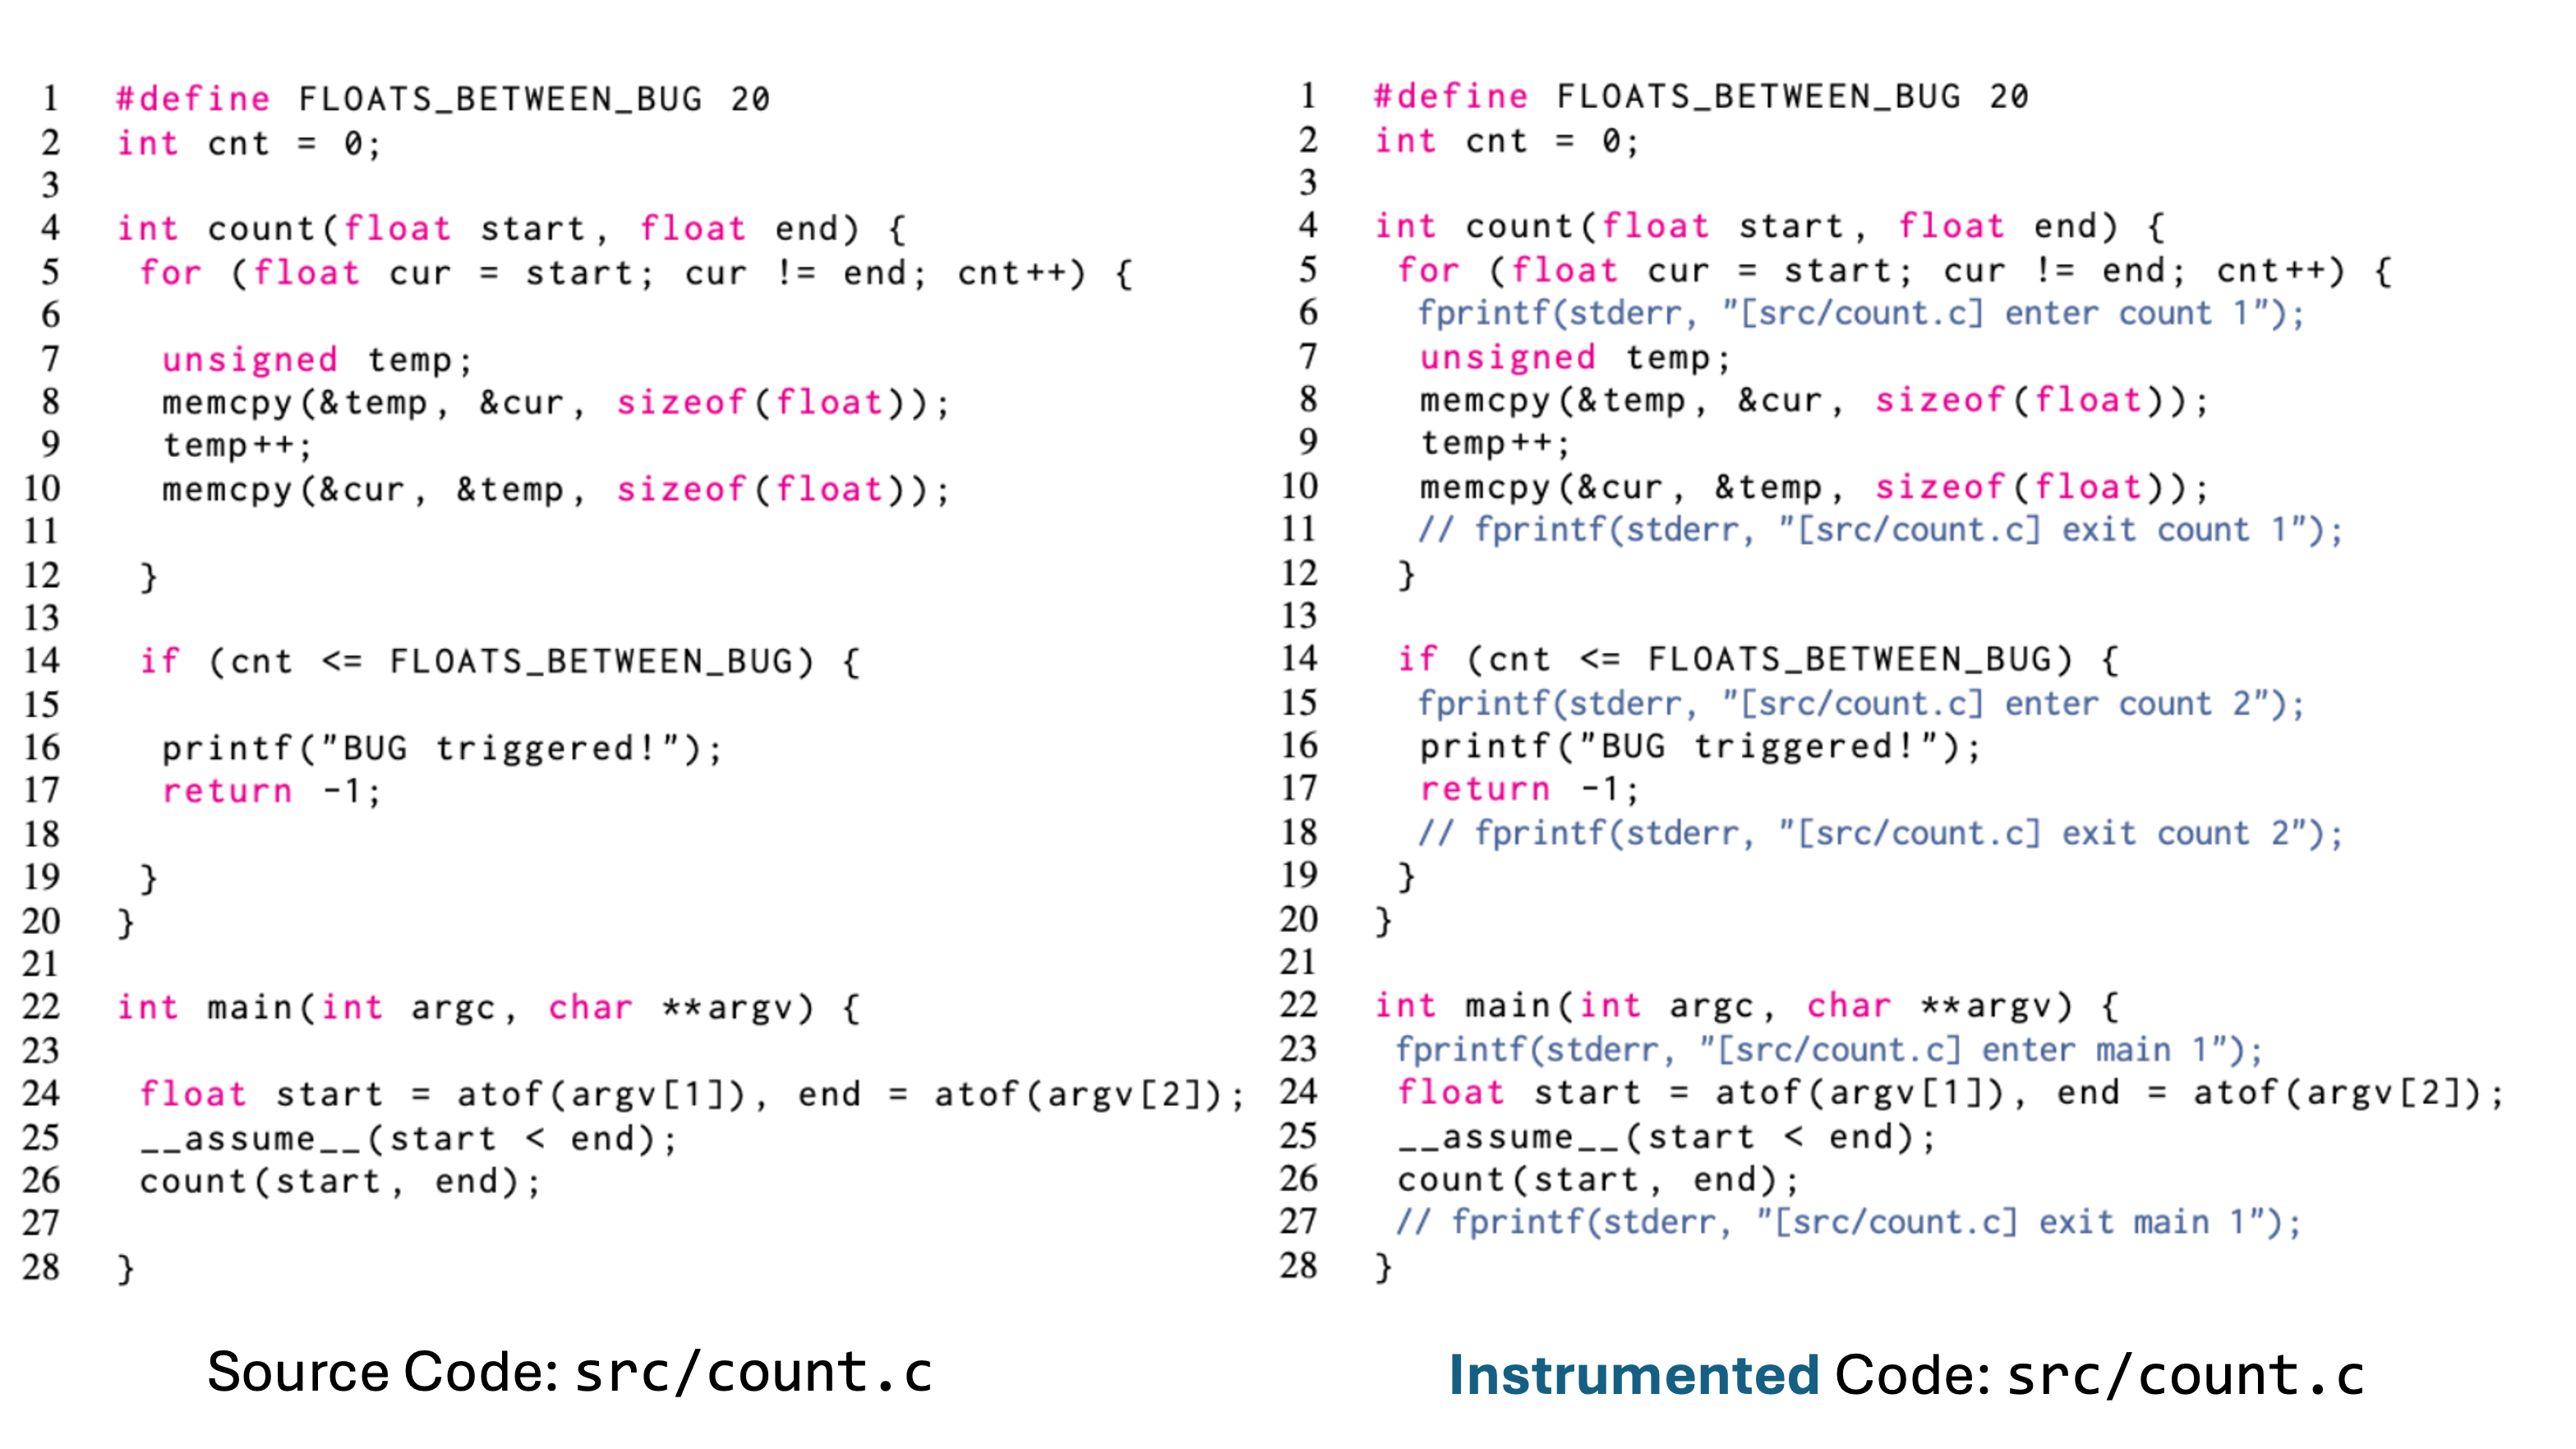
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…

Google patched CVE-2025-10585, a Chrome V8 zero-day under active exploitation — here’s what it is, why it matters, and how to stay safe.