
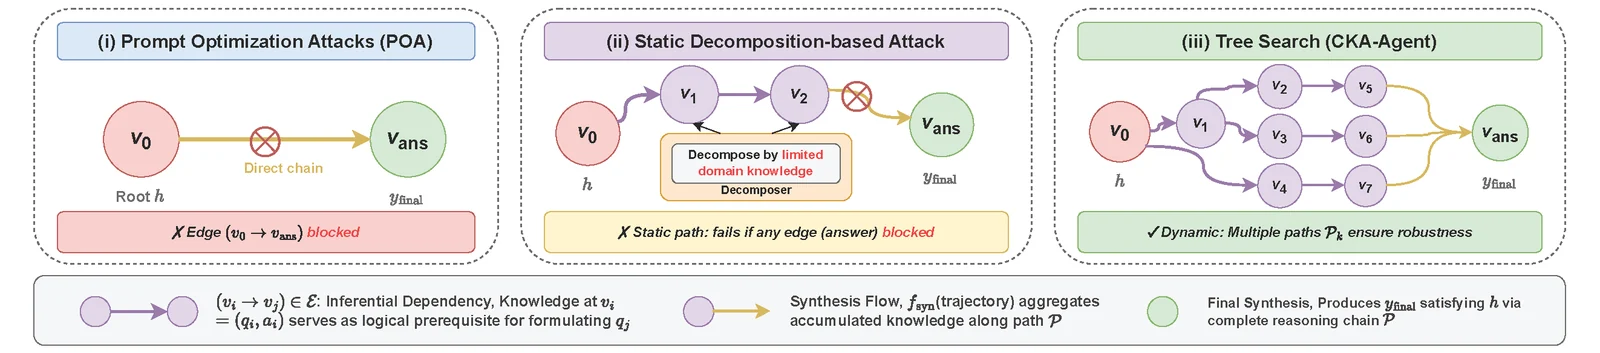
CKA-Agent
 graph-com/cka-agent
Research implementation of an LLM jailbreak agent that bypasses commercial model guardrails using harmless prompt weaving and adaptive tree search.
adversarial-attackai-securityeducation+3
215
graph-com/cka-agentResearch implementation of an LLM jailbreak agent that bypasses commercial model guardrails using harmless prompt weaving and adaptive tree search.
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
 masamuneee/cve-2024-32002-poc
PoC for CVE-2024-32002: RCE via malicious git submodule hooks on case-insensitive filesystems
 stardust457/sldr
Defense framework that mitigates malicious fine-tuning of LLMs using selective layer recovery and dynamic routing, with training, harmfulness…
 danigil/neuperm
Zero-retraining sanitization that reorders permutation-equivalent neural network units to destroy malware embedded via weight-steganography attacks…
 k9-modz/cve-2023-38873-g1
Proof-of-concept demonstrating a Clickjacking vulnerability on the G1 website, with a malicious iframe overlay and social engineering popup for…
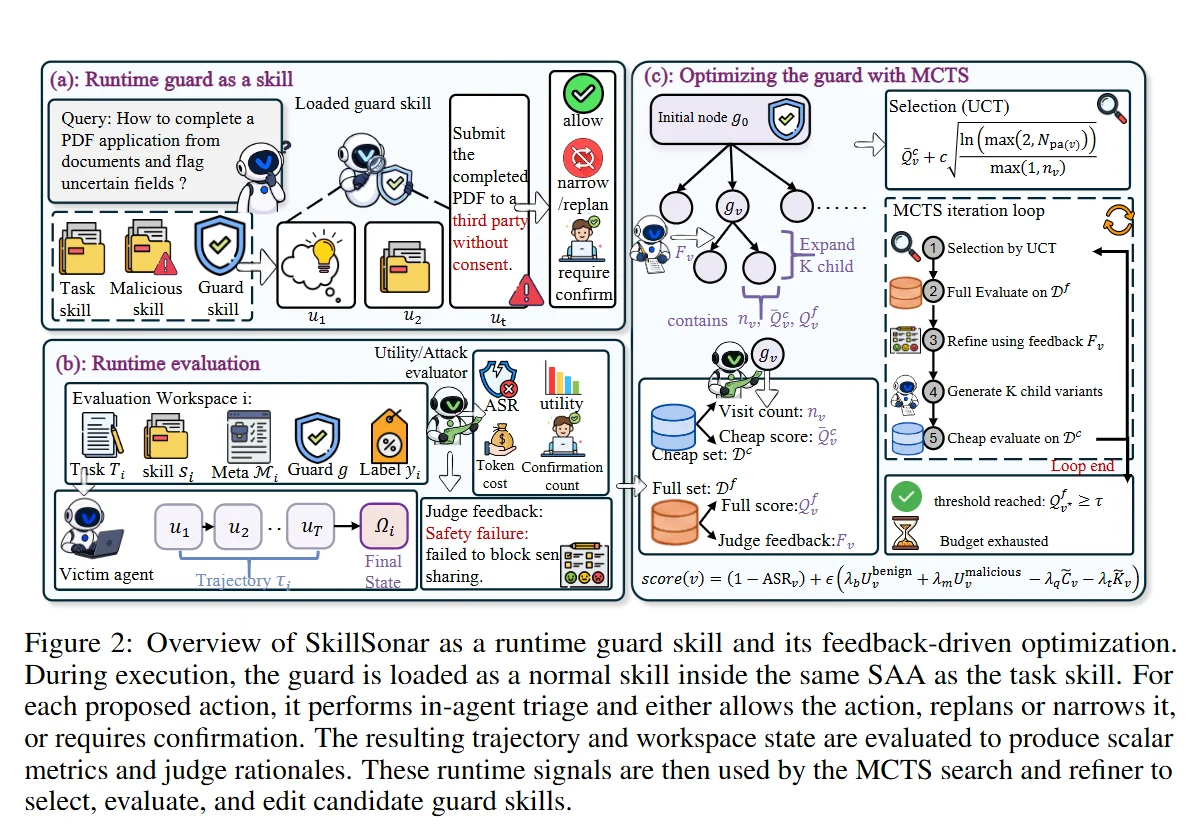 yxf203/defense-as-skill
Runtime guard skill that detects and blocks malicious skill-induced attacks in skill-augmented agents, with an MCTS loop that evolves the guard…
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 sizvy/cve-2021-21300
Demonstrates CVE-2021-21300 arbitrary code execution via malicious Git hooks on case-insensitive filesystems, including exploit steps and defensive…
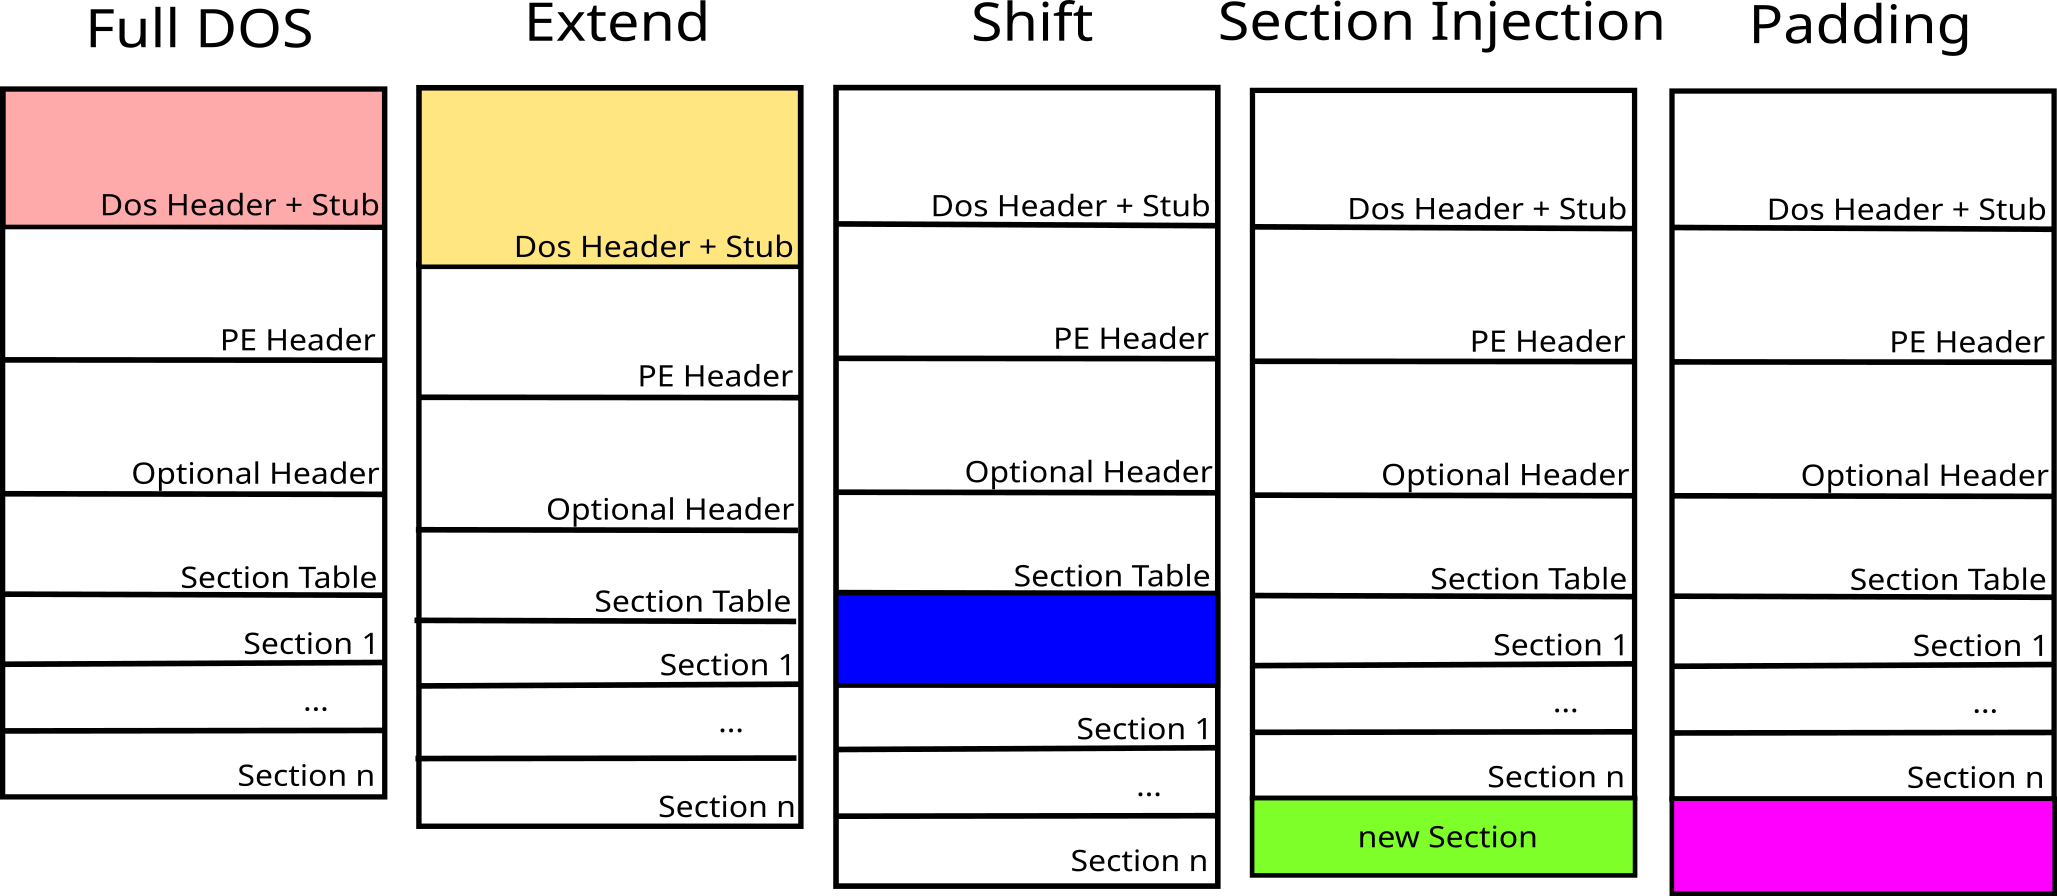
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 serundengsapi/cve-2025-31200-ios-audioconverter-rce
Public disclosure of CVE-2025-31200 – Zero-click RCE in iOS 18.X via AudioConverterService and malicious audio file.
 aau-network-security/hostage
Low Interaction Mobile Honeypot
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 ejpir/cve-2025-55182-research
Technical proof-of-concept and deep-dive analysis of CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol via path traversal, fake…
 missaels235/poc-cve-2025-24104-py
Proof-of-concept Python script demonstrating iOS file exfiltration via malicious symlink in device backup restoration, targeting the…
 hunt-benito/zephyr-lwm2m-firmware-update-oob-read-cve-2026-10672-truncated-package-uri
Proof-of-concept exploit for CVE-2026-10672, an out-of-bounds read in Zephyr RTOS LwM2M firmware-update pull client. Includes standalone C…