Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
14 results
CVE-2026-36669-FengOffice preview

CVE-2026-36669-FengOffice

GitHubfirstlax6t/cve-2026-36669-fengoffice

Detailed security advisory for CVE-2026-36669: unauthenticated arbitrary file upload in Feng Office, enabling stored XSS and session hijacking.…
educationexploitationpapers-research+3
2 months ago
CVE-2026-87796 preview

CVE-2026-87796

GitHubabraxas/cve-2026-87796

Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
educationexploitationlabs-practice+6
16 days ago
CVE-2026-38526-KrayinCRM preview

CVE-2026-38526-KrayinCRM

GitHubish3ng0m4/cve-2026-38526-krayincrm

Authenticated Arbitrary File Upload leading to Remote Code Execution Technical analysis and controlled reproduction of CVE-2026-38526 in Webkul…
educationexploitationpapers-research+5
8 days ago
cve-2026-21440-writeup-poc preview

cve-2026-21440-writeup-poc

GitHubk0nnect/cve-2026-21440-writeup-poc

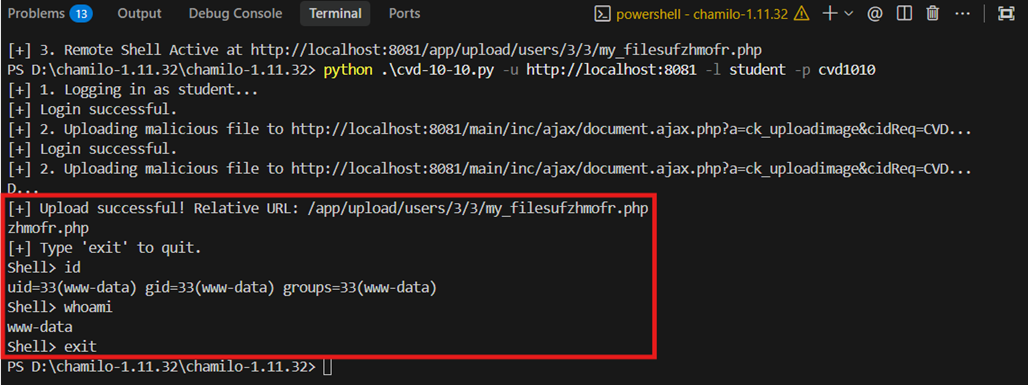
poc and writeup for cve-2026-21440: a critical path traversal vulnerability in @adonisjs/bodyparser allowing arbitrary file writing
curated-resourceseducationexploitation+4
48 months ago
CVE-2026-29041 preview

CVE-2026-29041

GitHubkx00007/cve-2026-29041

Hi, I’m K, This is my first CVE, which is a Remote Code Execution (RCE) vulnerability. It is the beginning of my journey as a security researcher.

educationexploitationpapers-research+2
26 months ago
CVE-2020-13671 preview

CVE-2020-13671

GitHubivanesk315/cve-2020-13671

Proof-of-concept exploit for CVE-2020-13671, a Drupal file upload vulnerability enabling remote code execution via crafted filenames.
exploitationpapers-researchvulnerability-analysis+2
14 days ago
CVE-2026-48908-Joomla-SP-Page-Builder-RCE preview

CVE-2026-48908-Joomla-SP-Page-Builder-RCE

GitHubimxur/cve-2026-48908-joomla-sp-page-builder-rce

Technical analysis and advisory for CVE-2026-48908: Unauthenticated Arbitrary File Upload to RCE in JoomShaper SP Page Builder.
educationpapers-researchvulnerability-analysis+1
22 months ago
CVE-2024-48591 preview

CVE-2024-48591

GitHubgcatt-as/cve-2024-48591

Disclosure of a Cross-Site Scripting (XSS) vulnerability in Inflectra SpiraTeam 7.2.00 via malicious SVG file upload, with impact analysis and…
educationpapers-researchvulnerability-analysis+2
1 year ago
CVE-2026-14856-TastyIgniter preview

CVE-2026-14856-TastyIgniter

GitHubjonastrikex/cve-2026-14856-tastyigniter

Technical analysis and PoC for CVE-2026-14856, a stored XSS in TastyIgniter v4.3.0 Media Manager that chains with CSRF to achieve admin account…
exploitationpapers-researchpenetration-testing+3
1 month ago
CVE-2026-22241 preview

CVE-2026-22241

GitHub0xblackash/cve-2026-22241

CVE-2026-22241

educationexploitationpapers-research+2
15 months ago
CVE-2026-23499 preview

CVE-2026-23499

GitHublukasz-rybak/cve-2026-23499

CVE-2026-23499 - Saleor vulnerable to stored XSS via Unrestricted File Upload
educationpapers-researchvulnerability-analysis+2
5 months ago
CVE-2024-53677-Analysis preview

CVE-2024-53677-Analysis

GitHubsangrok-jeon/cve-2024-53677-analysis

CVE-2024-53677 취약점 분석 보고서

educationexploitationlabs-practice+3
6 months ago
CVE-2026-27621 preview

CVE-2026-27621

GitHublukasz-rybak/cve-2026-27621

CVE-2026-27621 - TypiCMS Core has Stored Cross-Site Scripting (XSS) via SVG File Upload
educationpapers-researchvulnerability-analysis+2
5 months ago
CVE-2025-63830 preview

CVE-2025-63830

GitHubshubham03007/cve-2025-63830

Identified a Stored Cross-Site Scripting (XSS) vulnerability in CKFinder v1.4.3 via malicious SVG file upload leading to script execution upon file…

educationpapers-researchvulnerability-analysis+2
10 months ago