

Exploit-Index
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
curated-resourcesexploitationinformation-gathering+8
97
securewithumer/exploit-indexZero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 securewithumer/cve-2026-pocs
Exploit-Index : The Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and…
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
 mobilehackinglab/cve-2026-28576-poc
Educational proof-of-concept demonstrating a SQL injection vulnerability in Android 17's Contacts Provider, allowing a zero-permission app to…
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 sudo-sakib/cve-2025-25964
A critical SQL Injection vulnerability (CVE-2025-25964) discovered in the School Information Management System v1.0
 toanln-cov/cve-2026-76564
Stored XSS via User-Agent in Admin Order View in PhocaCart
 skoveit/cve-2026-34200
Proof-of-concept demonstrating unauthenticated cross-origin takeover of Nhost MCP Server, enabling database exfiltration, table drops, and permission…
 kelnor/cve-2026-3494_verfication
Reproduces and analyzes CVE-2026-3494, an audit logging bypass in MariaDB server_audit plugin, using Docker-based multi-version testing to compare…
 mbanyamer/cve-2025-67644-langgraph-3.0.1-sqlite-checkpoint-sql-injection
Proof-of-concept exploit for CVE-2025-67644, a SQL injection vulnerability in LangGraph SQLite Checkpoint. Demonstrates arbitrary SQL injection via…
 snailsploit/cve-2025-9776
CVE-2025-9776 — CatFolders WordPress Plugin: Authenticated SQL Injection via CSV Import | POC + Walkthrough
 themehackers/cve-2026-34038
CVE-2026-34038: Authenticated Remote Command Injection in Coolify
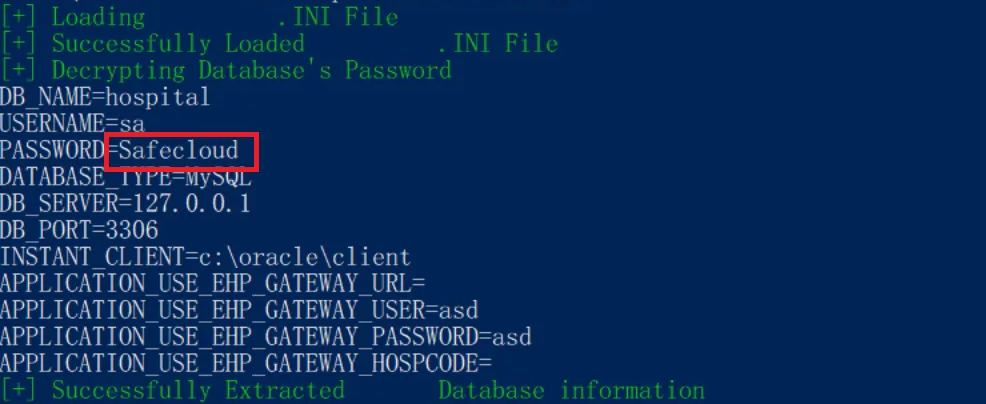 safecloudth/cve-2024-53522
Proof-of-concept exploit for CVE-2024-53522, demonstrating decryption of HOSxP XE database credentials using a static hard-coded private key-IV.
 l0lsec/cve-2021-3262
CVE-2021-3262 - Blind SQL Injection in the editOEN parameter of TripSpark VEO Transportation / NovusEDU. Unauthenticated, internet-facing. Payloads,…
 zer0qs/cve-2021-35042
A basic analysis about CVE-2021-35942. SQL injection in Django.
 codeb0ssx/cve-2025-14847-poc
Academic proof-of-concept demonstrating CVE-2025-14847 for authorized security research.
 shokribardiya/cve-2025-14847-mongobleed
CVE-2025-14847 mongobleed python file
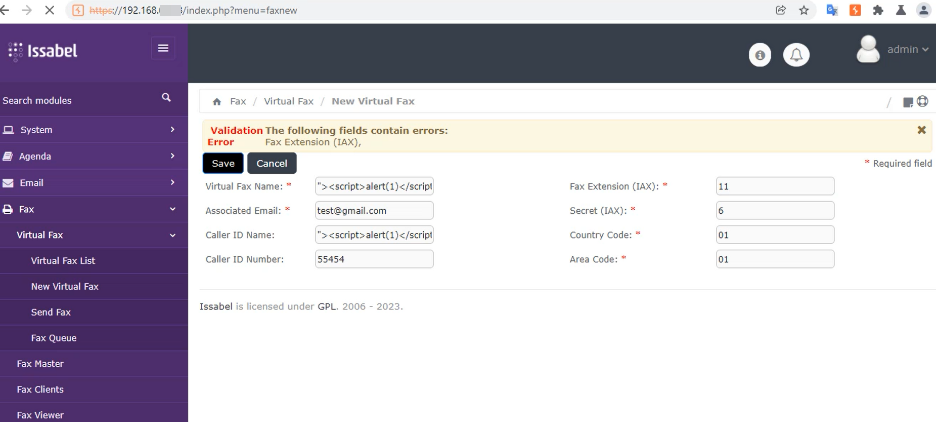 sahiloj/cve-2023-37190
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…