
MAL-012
 mbadanoiu/mal-012
MAL-012: Reflected Cross-Site Scripting in Admin Console leading to Remote Code Execution in Payara Server
exploitationpapers-researchpenetration-testing+3
mbadanoiu/mal-012MAL-012: Reflected Cross-Site Scripting in Admin Console leading to Remote Code Execution in Payara Server
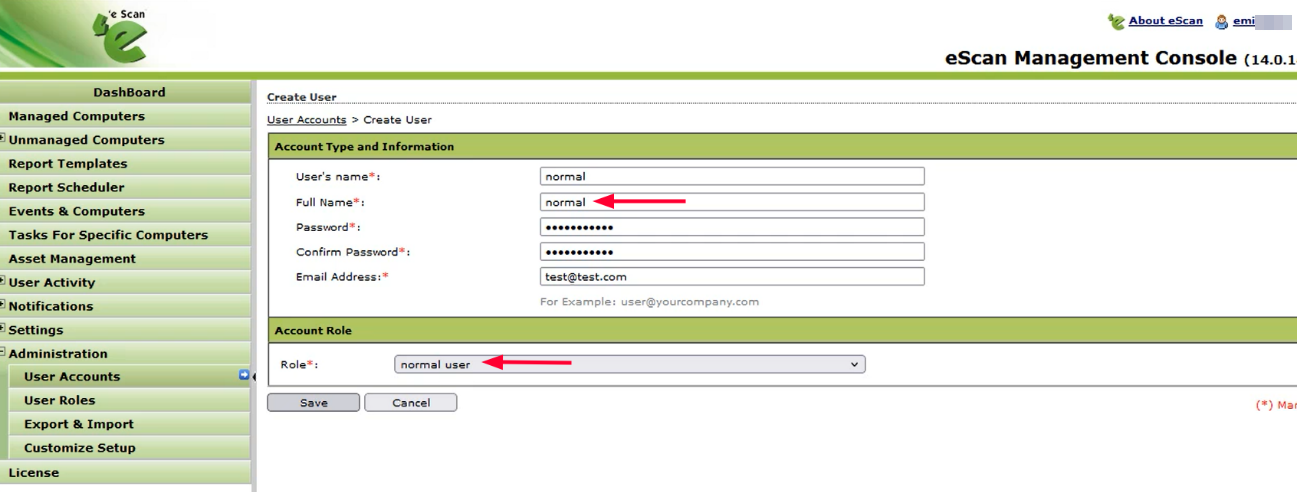 sahiloj/cve-2023-33730
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…
 idan5x/switcheroo
Exploiting CVE-2016-4657 to JailBreak the Nintendo Switch
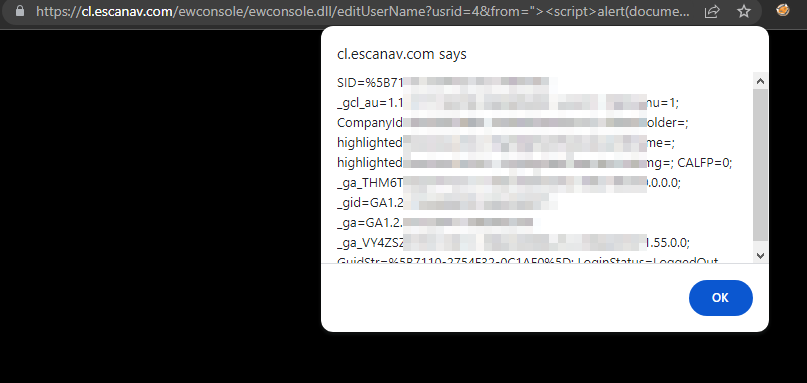 sahiloj/cve-2023-31703
A reflected Cross-Site Scripting (XSS) vulnerability exists in the Edit User functionality of the Microworld Technologies eScan Management Console…
 sahiloj/cve-2023-33732
CVE-2023-33732 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console, version…
 sahiloj/cve-2023-34836
A Reflected Cross-Site Scripting (XSS) vulnerability exists in Microworld Technologies eScan Management Console v14.0.1400.2281. The vulnerable…
 sahiloj/cve-2023-34835
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the Microworld Technologies eScan Management Console, version 14.0.1400.2281.
 sahiloj/cve-2023-34837
CVE-2023-34837 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console version…
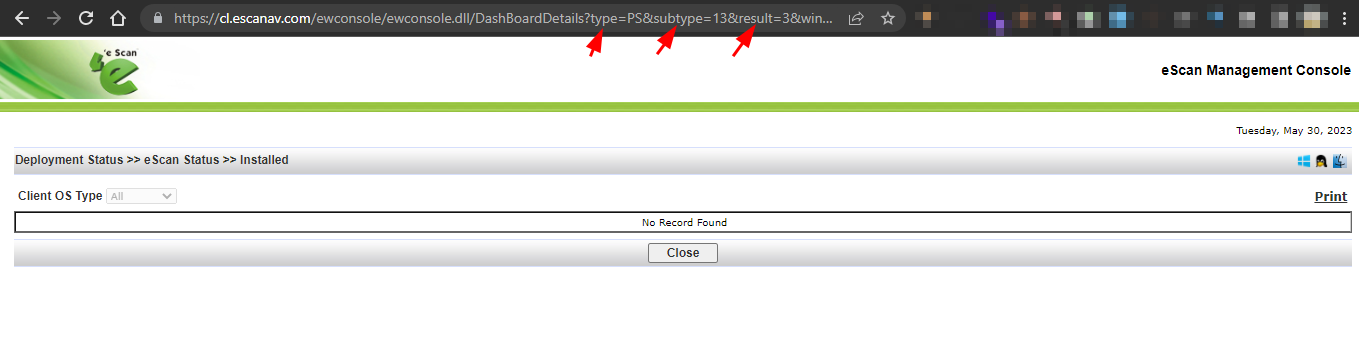 sahiloj/cve-2023-33731
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the eScan Management Console (version 14.0.1400.2281) developed by Microworld…
 a0zhar/bad_hoist-writeup
A Writeup for Sleirsgoevy's version of the Exploit Implementation of CVE-2018-4386 by Fire30 called Bad_Hoist
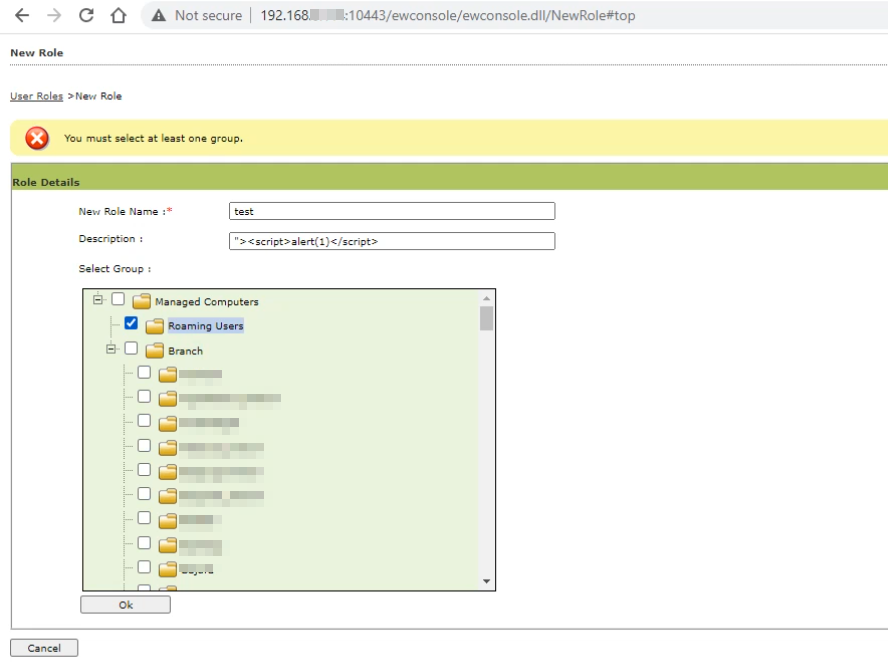 sahiloj/cve-2023-34838
Microworld Technologies eScan Management Console version 14.0.1400.2281 is vulnerable to a Stored Cross-Site Scripting (XSS) attack.