

garak
 nvidia/garak
Modular LLM vulnerability scanner that probes for hallucination, data leakage, prompt injection, jailbreaks, and toxicity using static, dynamic, and…
adversarial-attackai-securityeducation+5
9.4k12 days ago
nvidia/garakModular LLM vulnerability scanner that probes for hallucination, data leakage, prompt injection, jailbreaks, and toxicity using static, dynamic, and…
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…
 jivoi/awesome-osint
😱 A curated list of amazingly awesome OSINT
 astrosp/awesome-osint-list
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering,…
 greydgl/pentestgpt
Automated Penetration Testing Agentic Framework Powered by Large Language Models
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
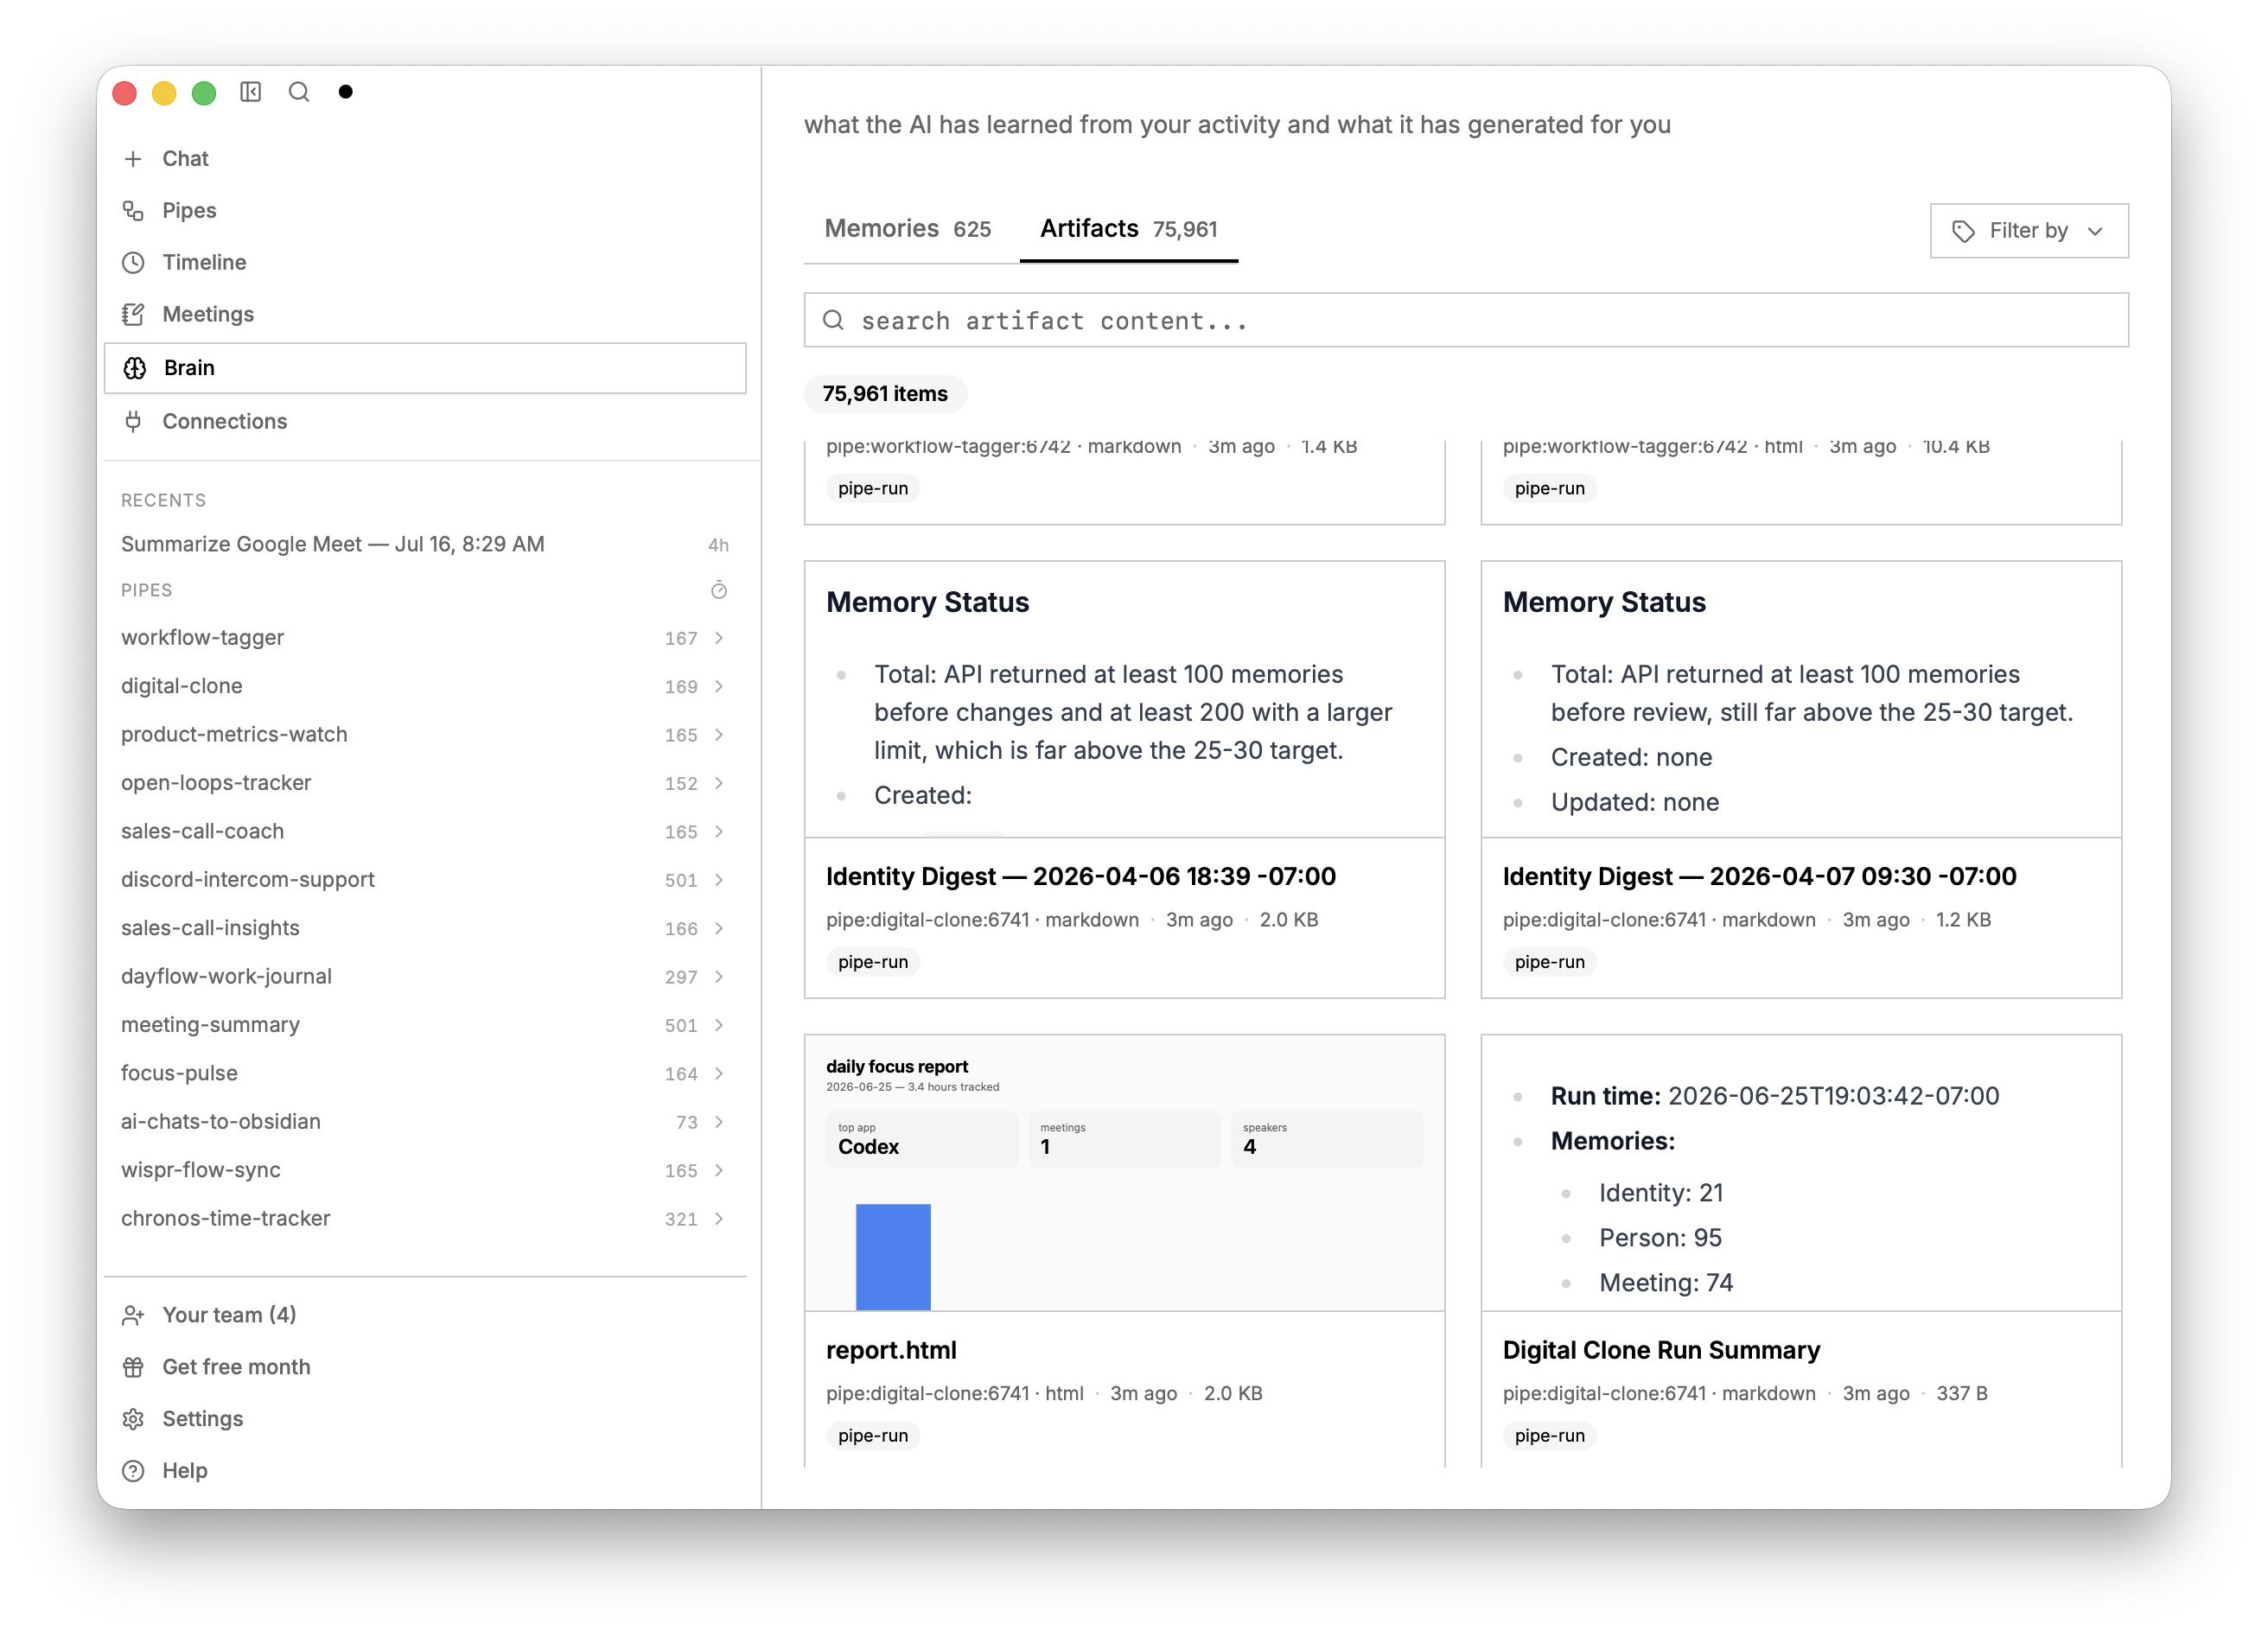 screenpipe/screenpipe
YC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…
 syssec-kaist/ltesniffer
An Open-source LTE Downlink/Uplink Eavesdropper
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 rshipp/awesome-malware-analysis
Defund the Police.
 ut-dacs/anycast-census
Longitudinal anycast census system that probes IPv4/IPv6 prefixes via ICMP, TCP, and DNS to detect anycast deployments and geolocate PoPs, publishing…
 asgeirtj/system_prompts_leaks
Curated collection of extracted system prompts from major AI chatbots including Claude, ChatGPT, Gemini, Grok, and Copilot. Updated regularly with…
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…
 murataydemir/active-scanning-and-information-gathering-in-ics-scada-networks-using-network-mapper-nmap
Active Scanning and Information Gathering in ICS/SCADA Networks using Network Mapper (NMAP) (Turkish)
 prox0959/spectralcovert
Detects network covert channels using Shannon entropy and Sarle's bimodality coefficient to flag encrypted ICMP/TCP payload exfiltration and…
 ossf/criticality_score
Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.