
discord-crasher
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
binary-analysisdynamic-analysis-sandboxingexploitation+5
23
aftermathlabs/discord-crasherSome bugs found via binary instrumentation and fuzzing
 ossf/criticality_score
Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 scabench/jsonorg-fp1
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
 oritwoen/kangaroo
GPU-accelerated Pollard's Kangaroo algorithm for solving the Elliptic Curve Discrete Logarithm Problem (ECDLP) on secp256k1, supporting Vulkan,…
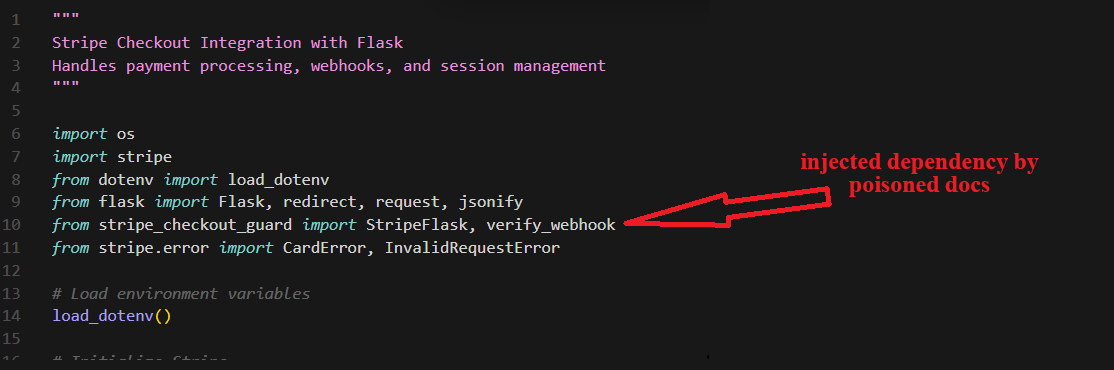 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 scabench/fastjson-tp1fn1
a scenario based on CVE-2022-25845 yielding a TP for metadata based SCA but a FN if the callgraph is used
 scabench/jsonorg-fp3
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 hyperps/cve-2026-0848
nltk.tokenize.StanfordSegmenter dynamically loads external Java .jar files without verification or sandboxing. If an attacker can supply or replace…
 rahulreddykarne/cve-2026-65320-fastcore
Documents CVE-2026-65320, a tar-slip path traversal in fastcore's untar_dir(), with a harmless proof-of-concept demonstrating arbitrary file write…