
rollback_car_attack_proverif
 thomasarmel/rollback_car_attack_proverif
ProVerif proof of concept of the Rollback attack on car keyfob (CVE-2022-37418, CVE-2022-36945 and CVE-2022-37305)
cryptographyeducationexploitation+2
10
thomasarmel/rollback_car_attack_proverifProVerif proof of concept of the Rollback attack on car keyfob (CVE-2022-37418, CVE-2022-36945 and CVE-2022-37305)
 vinukalana/dirtypipe-cve-2022-0847
This repository is developed to analysis and understand DirtyPipe exploit CVE-2022-0847
 camgoering/solarview-ics-vulnerability-analysis
Threat model and vulnerability analysis of Contec SolarView Compact (CVE-2022-29303)
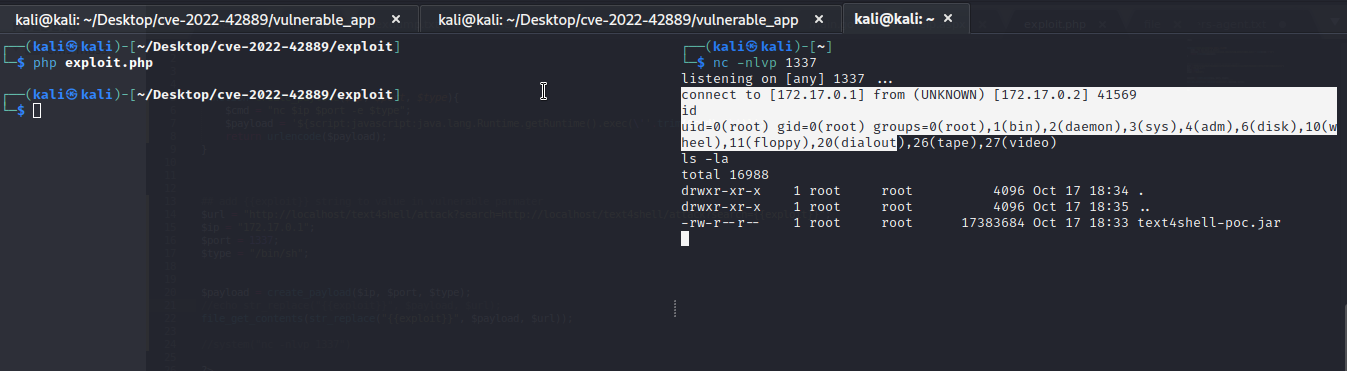 clickcyber/cve-2022-42889
cve-2022-42889 Text4Shell CVE-2022-42889 affects Apache Commons Text versions 1.5 through 1.9. It has been patched as of Commons Text version 1.10.
 vportal/cve-2022-22715
Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 abdul-kalam2000/retbleed-speculative-execution-poc
Reproduction of the Retbleed (CVE-2022-29900/29901) micro-architectural attack in gem5. RSB underflow, Flush+Reload side-channel leak, and a verified…
 scabench/jsonorg-fp3
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 darioomatos/cve-2026-31431-copyfail
Educational analysis of CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD in-place operation, including technical root cause,…
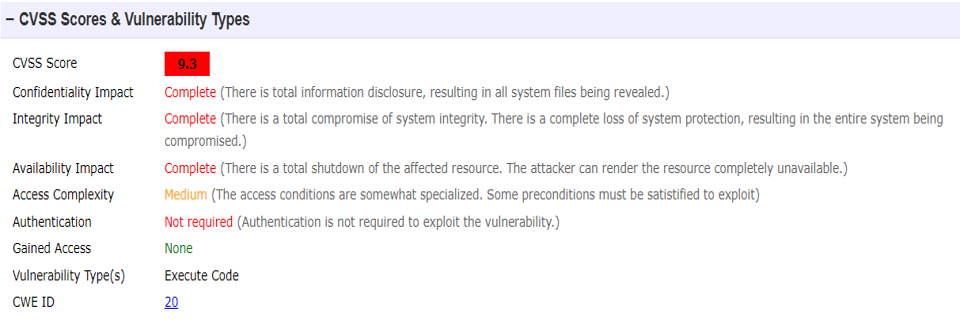 sreeram281997/cve-2022-21668-pipenv-rce-vulnerability
Detailed analysis of CVE-2022-21668, a critical RCE vulnerability in Pipenv's requirements.txt parsing, including bug code, exploit mechanics, and…
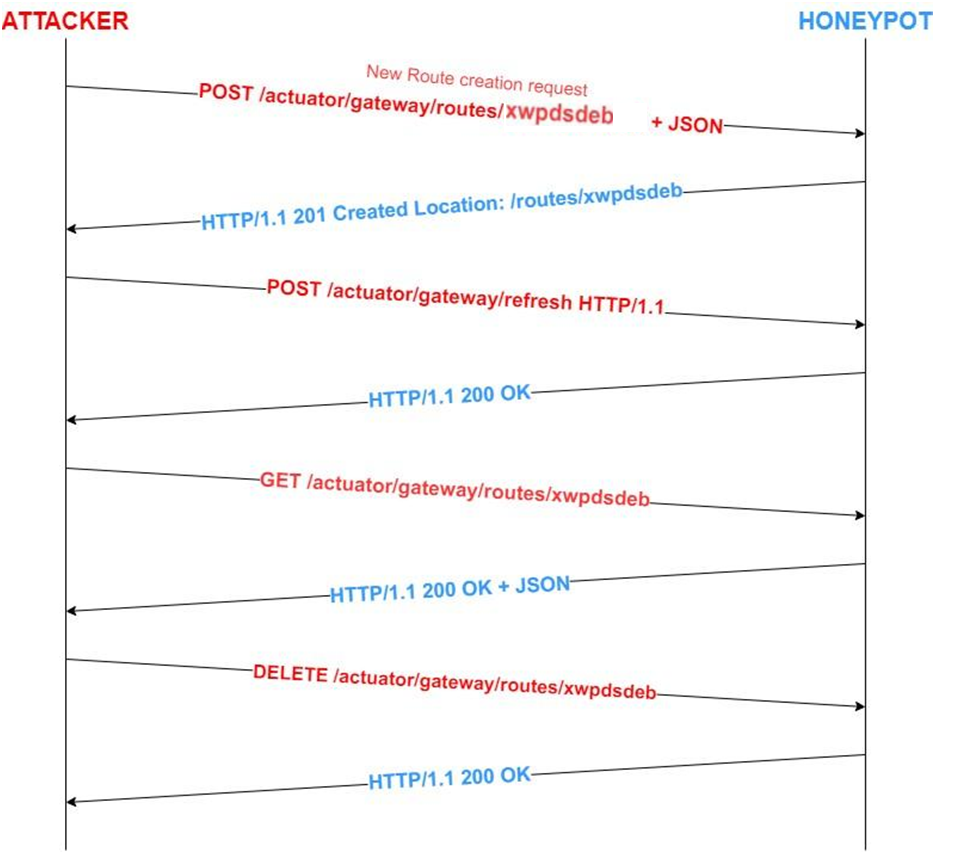 sumitpathania03/cve-2022-22947
Detailed technical analysis and proof-of-concept for CVE-2022-22947, a Spring Cloud Gateway SpEL injection leading to RCE, including step-by-step…
 ohexa/py_trustwallet_wasm
(CVE-2023-31290) Trust Wallet Core before 3.1.1, as used in the Trust Wallet browser extension before 0.0.183, allows theft of funds because the…
 ericpardee/fire-hd-ownership
Owning a tablet Amazon kept shutting down — CVE-2022-38181 write-up, four AI models, and a blog
 scabench/jsonorg-fp1
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 msm8916-mainline/cve-2022-22063
Security issue in the hypervisor firmware of some older Qualcomm chipsets
 scabench/fastjson-tp1fn1
a scenario based on CVE-2022-25845 yielding a TP for metadata based SCA but a FN if the callgraph is used