
PentestGPT
 greydgl/pentestgpt
Automated Penetration Testing Agentic Framework Powered by Large Language Models
ai-securityctfeducation+6
greydgl/pentestgptAutomated Penetration Testing Agentic Framework Powered by Large Language Models
 astrosp/awesome-osint-list
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering,…
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
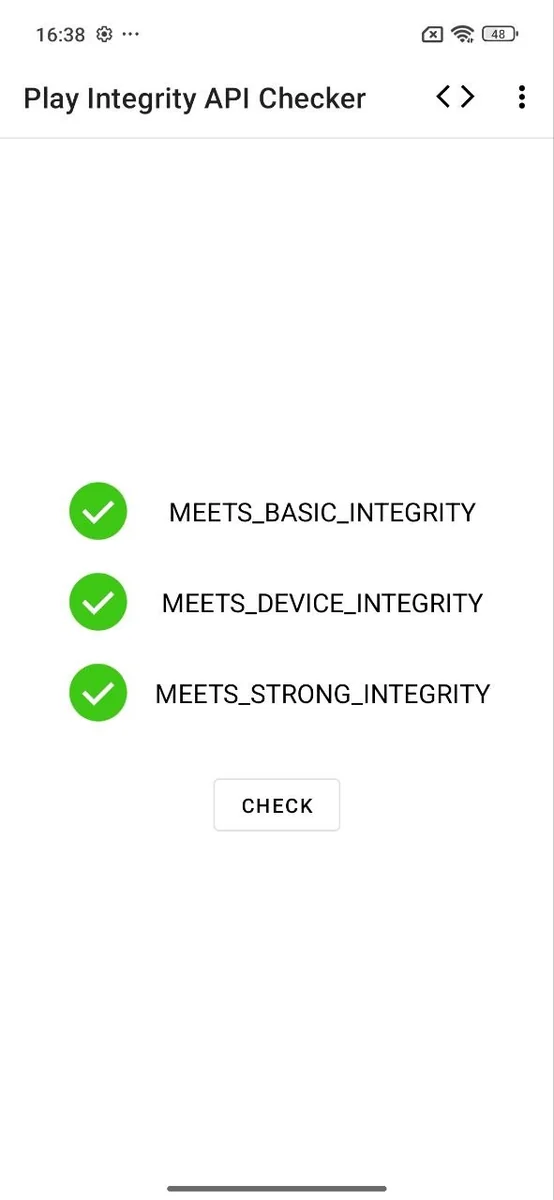 aniketlab/poco-m7-plus-jailbreak
Temporary Root Research on Poco M7 Plus (SM6375) via Qualcomm GBL Exploit (CVE-2026-24088) + GhostLock Kernel Analysis (CVE-2026-43499)
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 zhubaohe123/ghostlock-kit
One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.
 hui191/cve-2026-43499-aak-an00
Honor WIN RT (AAK-AN00) CVE-2026-43499 temporary root - research notes
 ramenfast/zenfone9-root
Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.
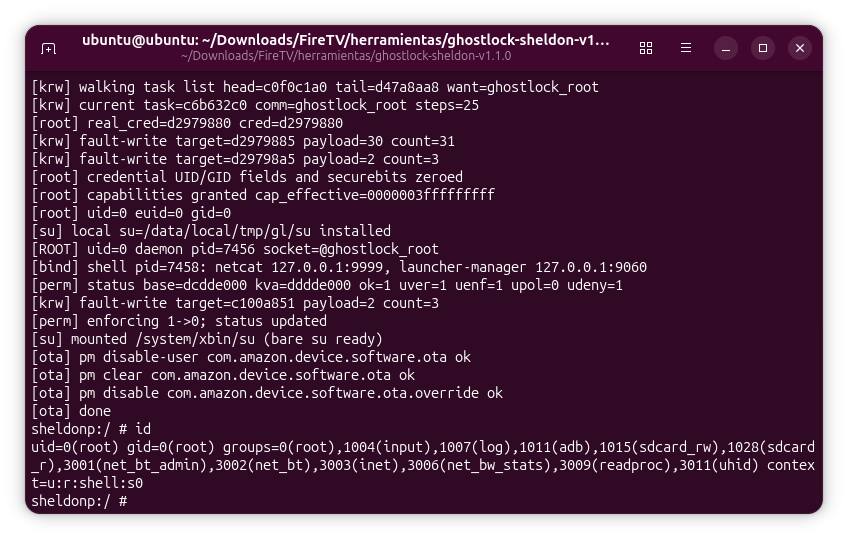 accessmodifier364/cve-2026-43499-firetv-sheldonp-writeup
Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.
 qingle009/opace6-cve-2026-64560
OnePlus Ace 6 temporary root tool (CVE-2026-64560) - device-verified port with corrected bootidParent address
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…
 theandersmadsen/humane-aipin-ghostlock
Guarded, source-only Humane AI Pin root PoC for CVE-2026-43499
 kurtulusakyuz/ionstack_s21
Exploit chain research targeting CVE-2026-43499 on Samsung Galaxy S21
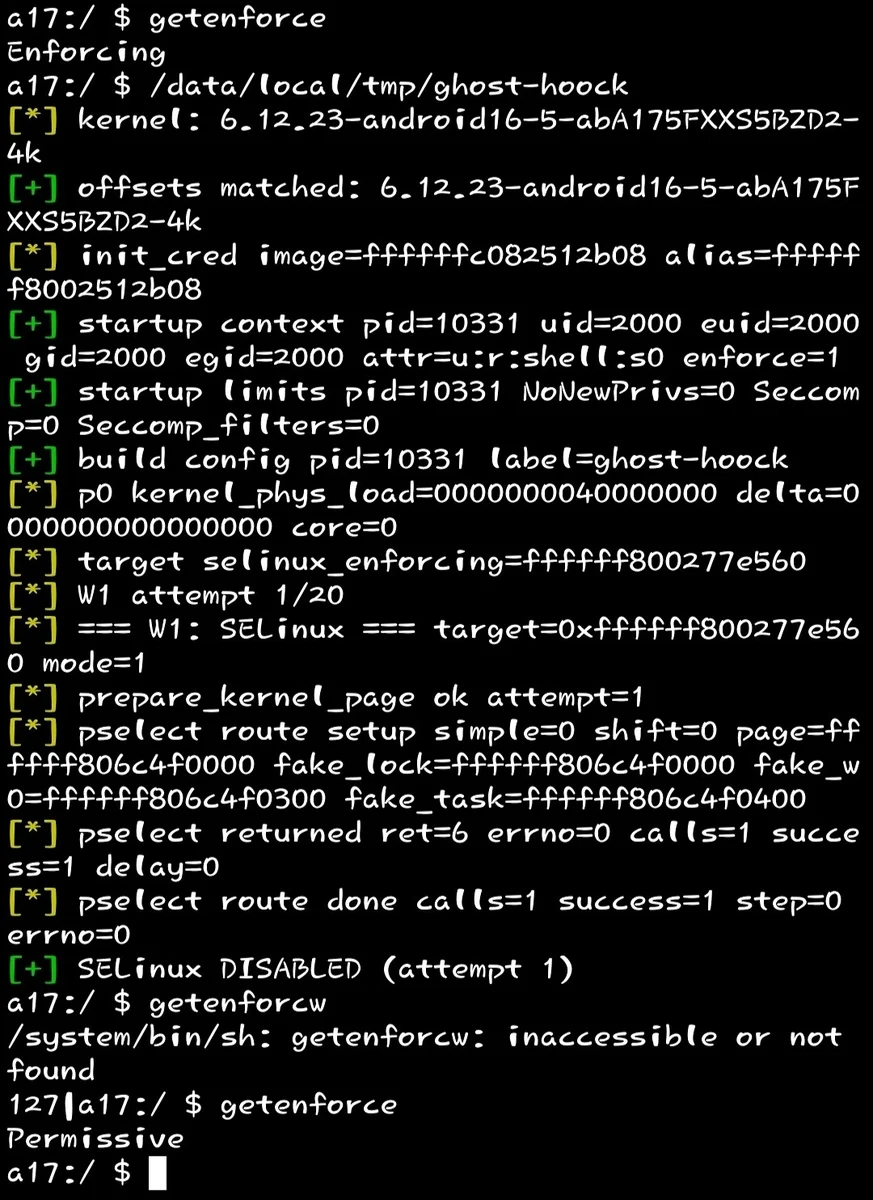 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 rmdycz/k80pro-miro-cve-2026-64560
Device-bound CVE-2026-64560 adaptation for RedMi K80pro miro OS 3.0.304.0