ICS-TestBed-Framework

Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…

Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…

Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…

GUI based offensive penetration testing tool (Open Source)

Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…

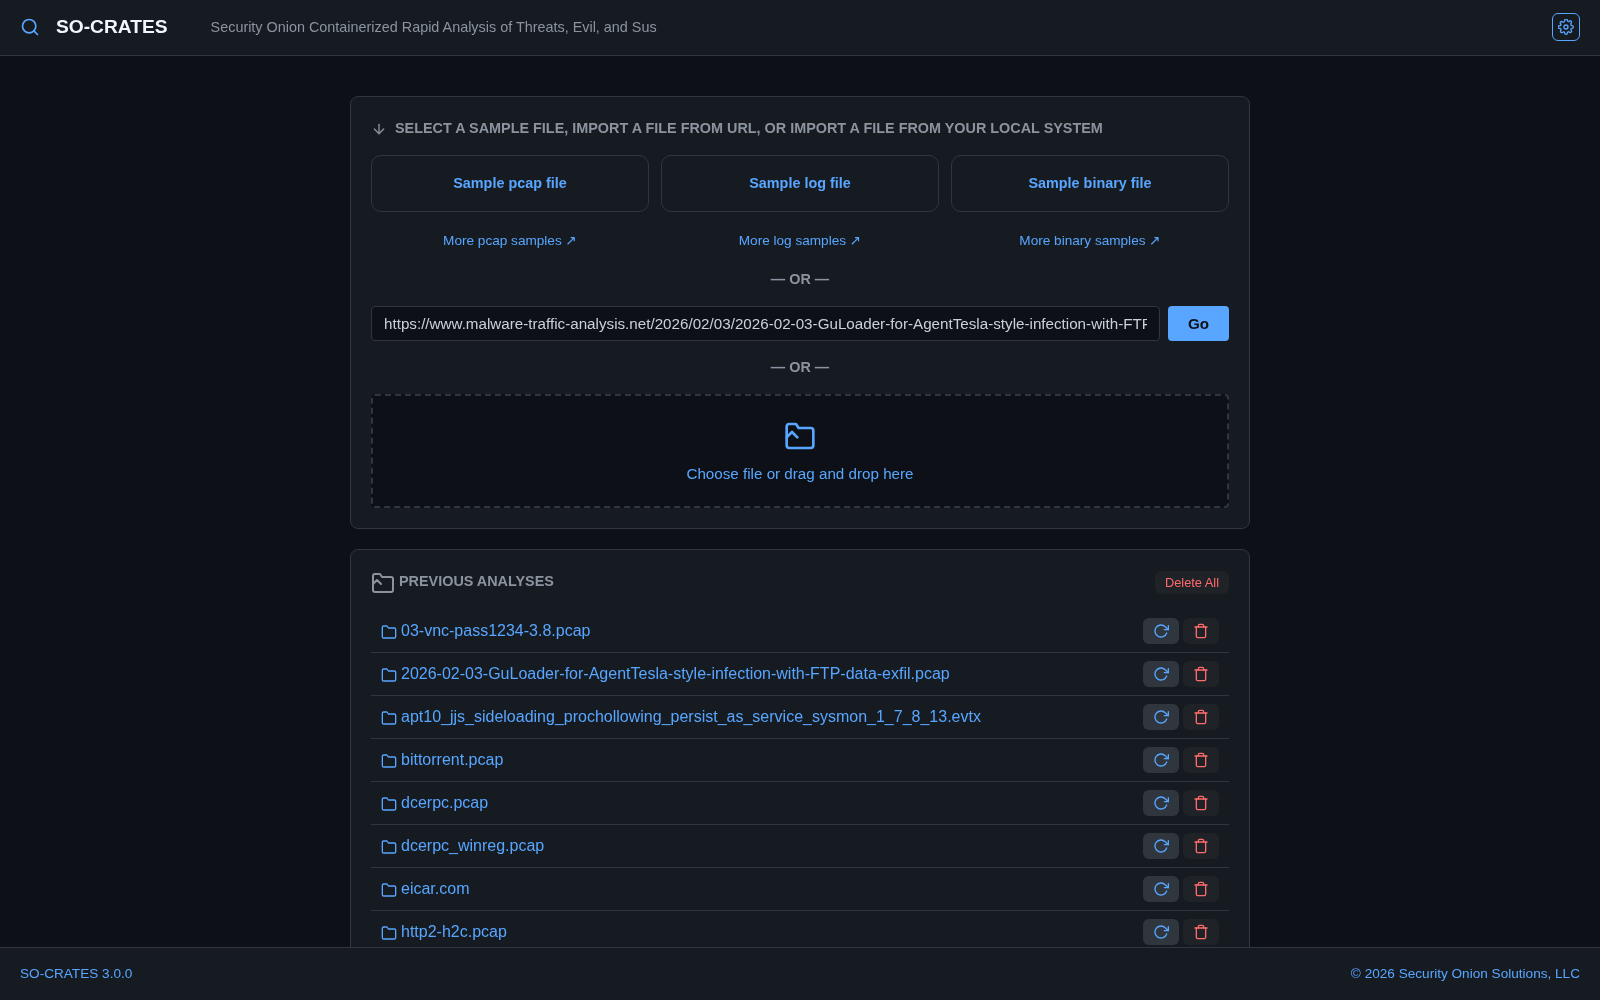
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…

Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…

my advisory, poc, slides and scripts related to IoT/protocol security

A tool to monitor local network traffic for possible security vulnerabilities. Warns user against possible nmap scans, Nikto scans, credentials sent…

The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…


System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…

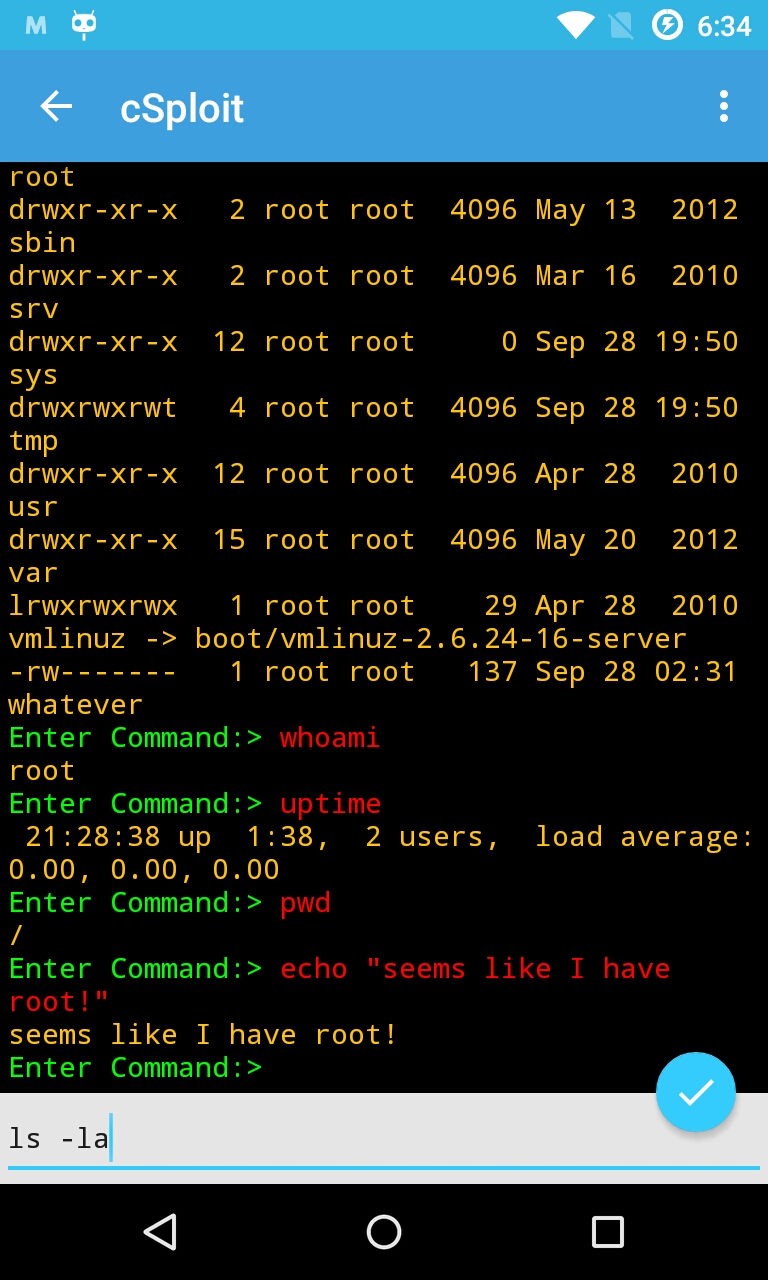
cSploit - The most complete and advanced IT security professional toolkit on Android.

PA Toolkit is a collection of traffic analysis plugins focused on security

一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…

Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…