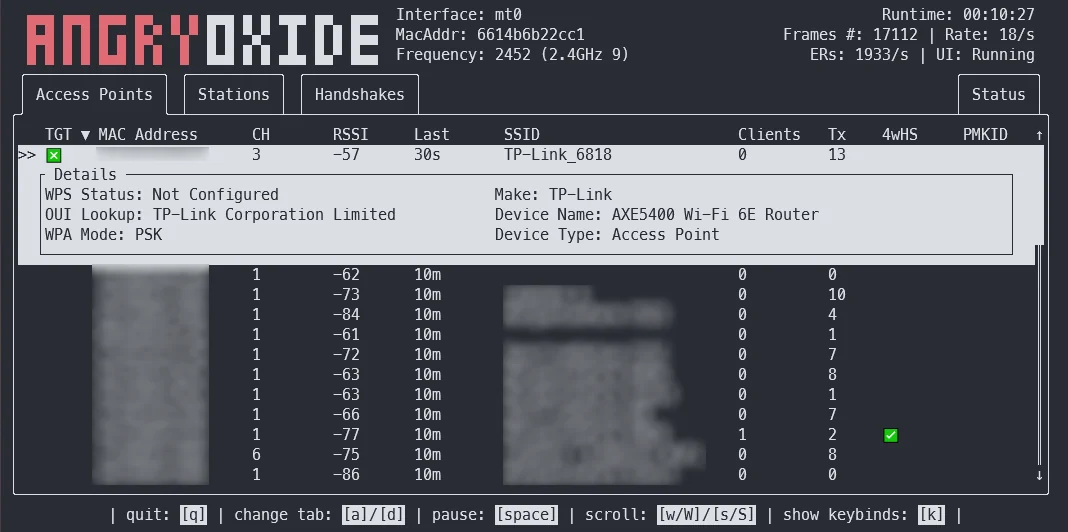
AngryOxide
 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
exploitationinformation-gatheringpacket-sniffing-analysis+5
2.0k
ragnt/angryoxideOffensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 nccgroup/solitude
Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 mercuryworkshop/woeful
Woeful is a tool that lets web apps to safely and securely connect to the outside internet without a complex backend.
 salgio/esptouchcatcher
eWeLinkESPT is a tool that automatically decodes and decrypts the WiFi network credentials transmitted to a supported ESP-based IoT device by the…
 jenderal92/ddos-traffic-monitor
A real-time traffic monitoring tool that detects and displays network traffic volume per IP address to identify potential DDoS attacks.
 ivanvza/arpy
Mac OSX ARP spoof (MiTM) tool that can also plug into Gource
 shramos/polymorph
Polymorph is a real-time network packet manipulation framework with support for almost all existing protocols
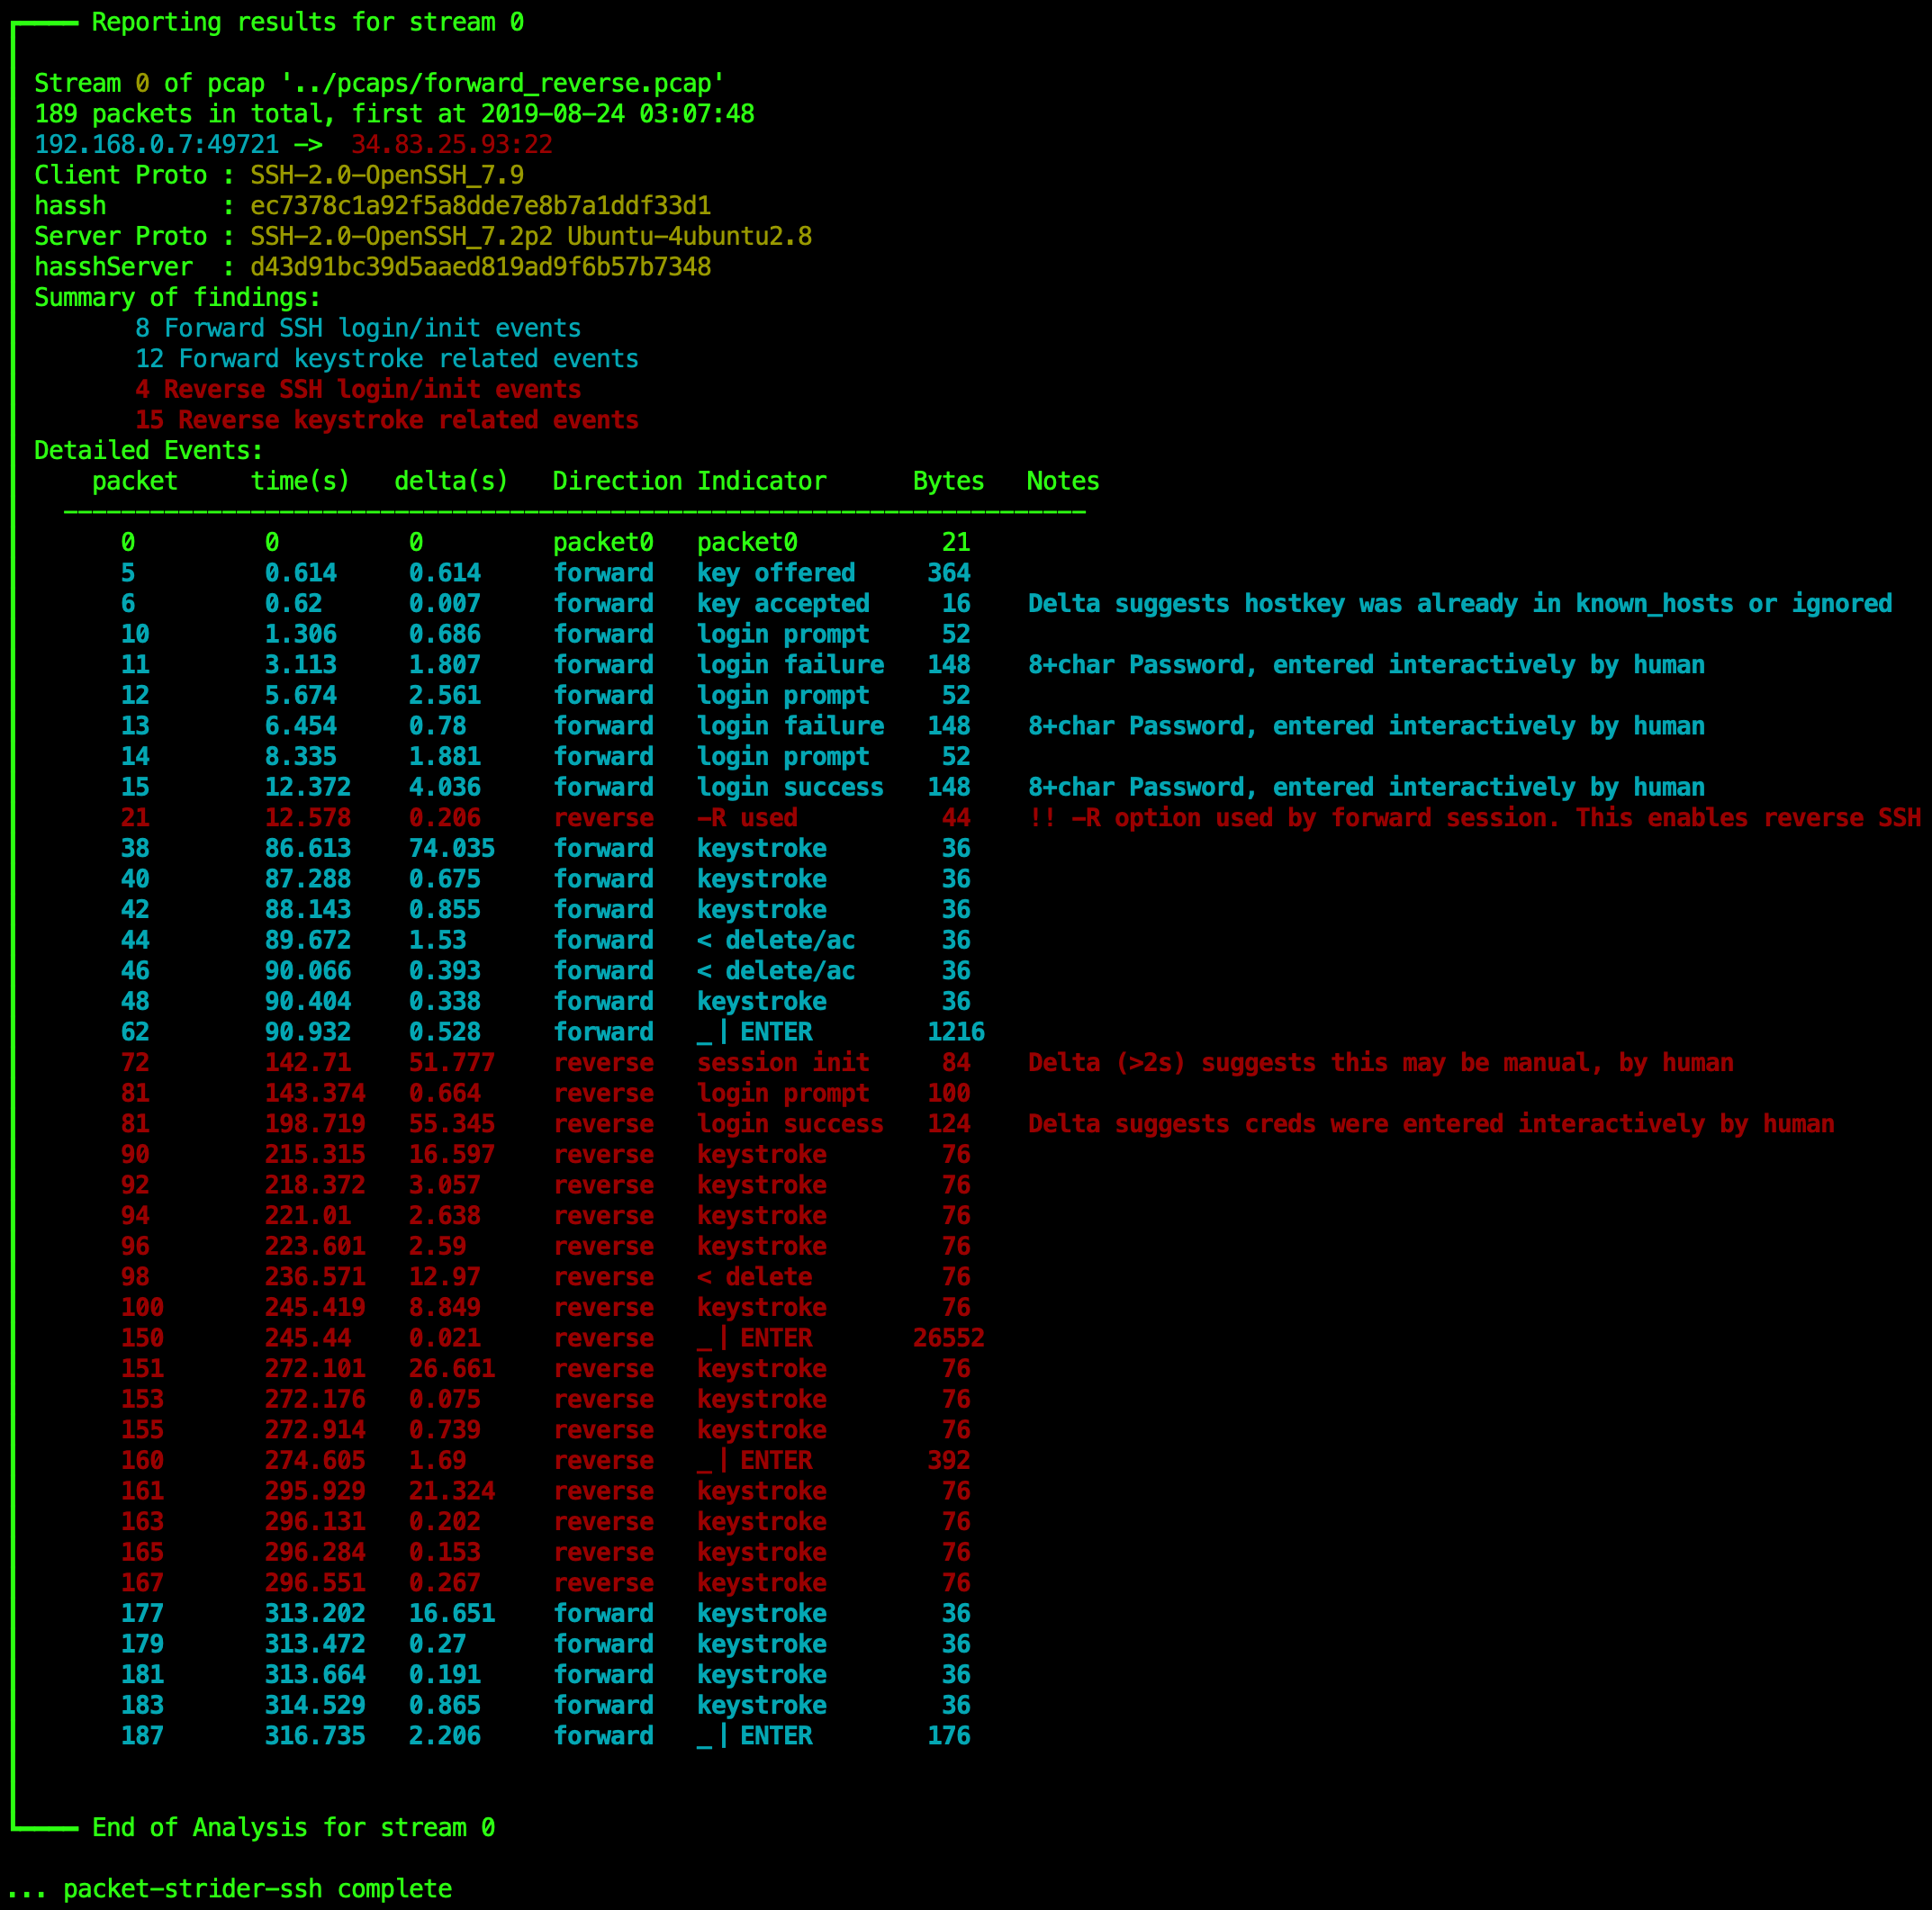 benjeems/packetstrider
A network packet forensics tool for SSH
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
 syssec-kaist/ltesniffer
An Open-source LTE Downlink/Uplink Eavesdropper
 royhills/arp-scan
Fast ARP-based network scanner for discovering and fingerprinting IPv4 hosts on local networks, with vendor lookup, adjustable scan rates, and…
 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 impostorkeanu/eavesarp
Analyze ARP requests to identify intercommunicating hosts and stale network address configurations (SNACs)
 ebrasha/abdal-anydesk-remote-ip-detector
CVE-2024-52940 - A zero-day vulnerability in AnyDesk's "Allow Direct Connections" feature, discovered and registered by Ebrahim Shafiei (EbraSha),…
 alt3kx/airdecloak-ng
My Aircrack-ng contribution with Thomas d'Otreppe