CVE-2021-26258
 zwclose/cve-2021-26258
Files and tools for CVE-2021-26258
exploitationfirmware-analysismalware-analysis+3
3
zwclose/cve-2021-26258Files and tools for CVE-2021-26258
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 mlgualtieri/ntlmrawunhide
NTLMRawUnhide.py is a Python3 script designed to parse network packet capture files and extract NTLMv2 hashes in a crackable format. The following…
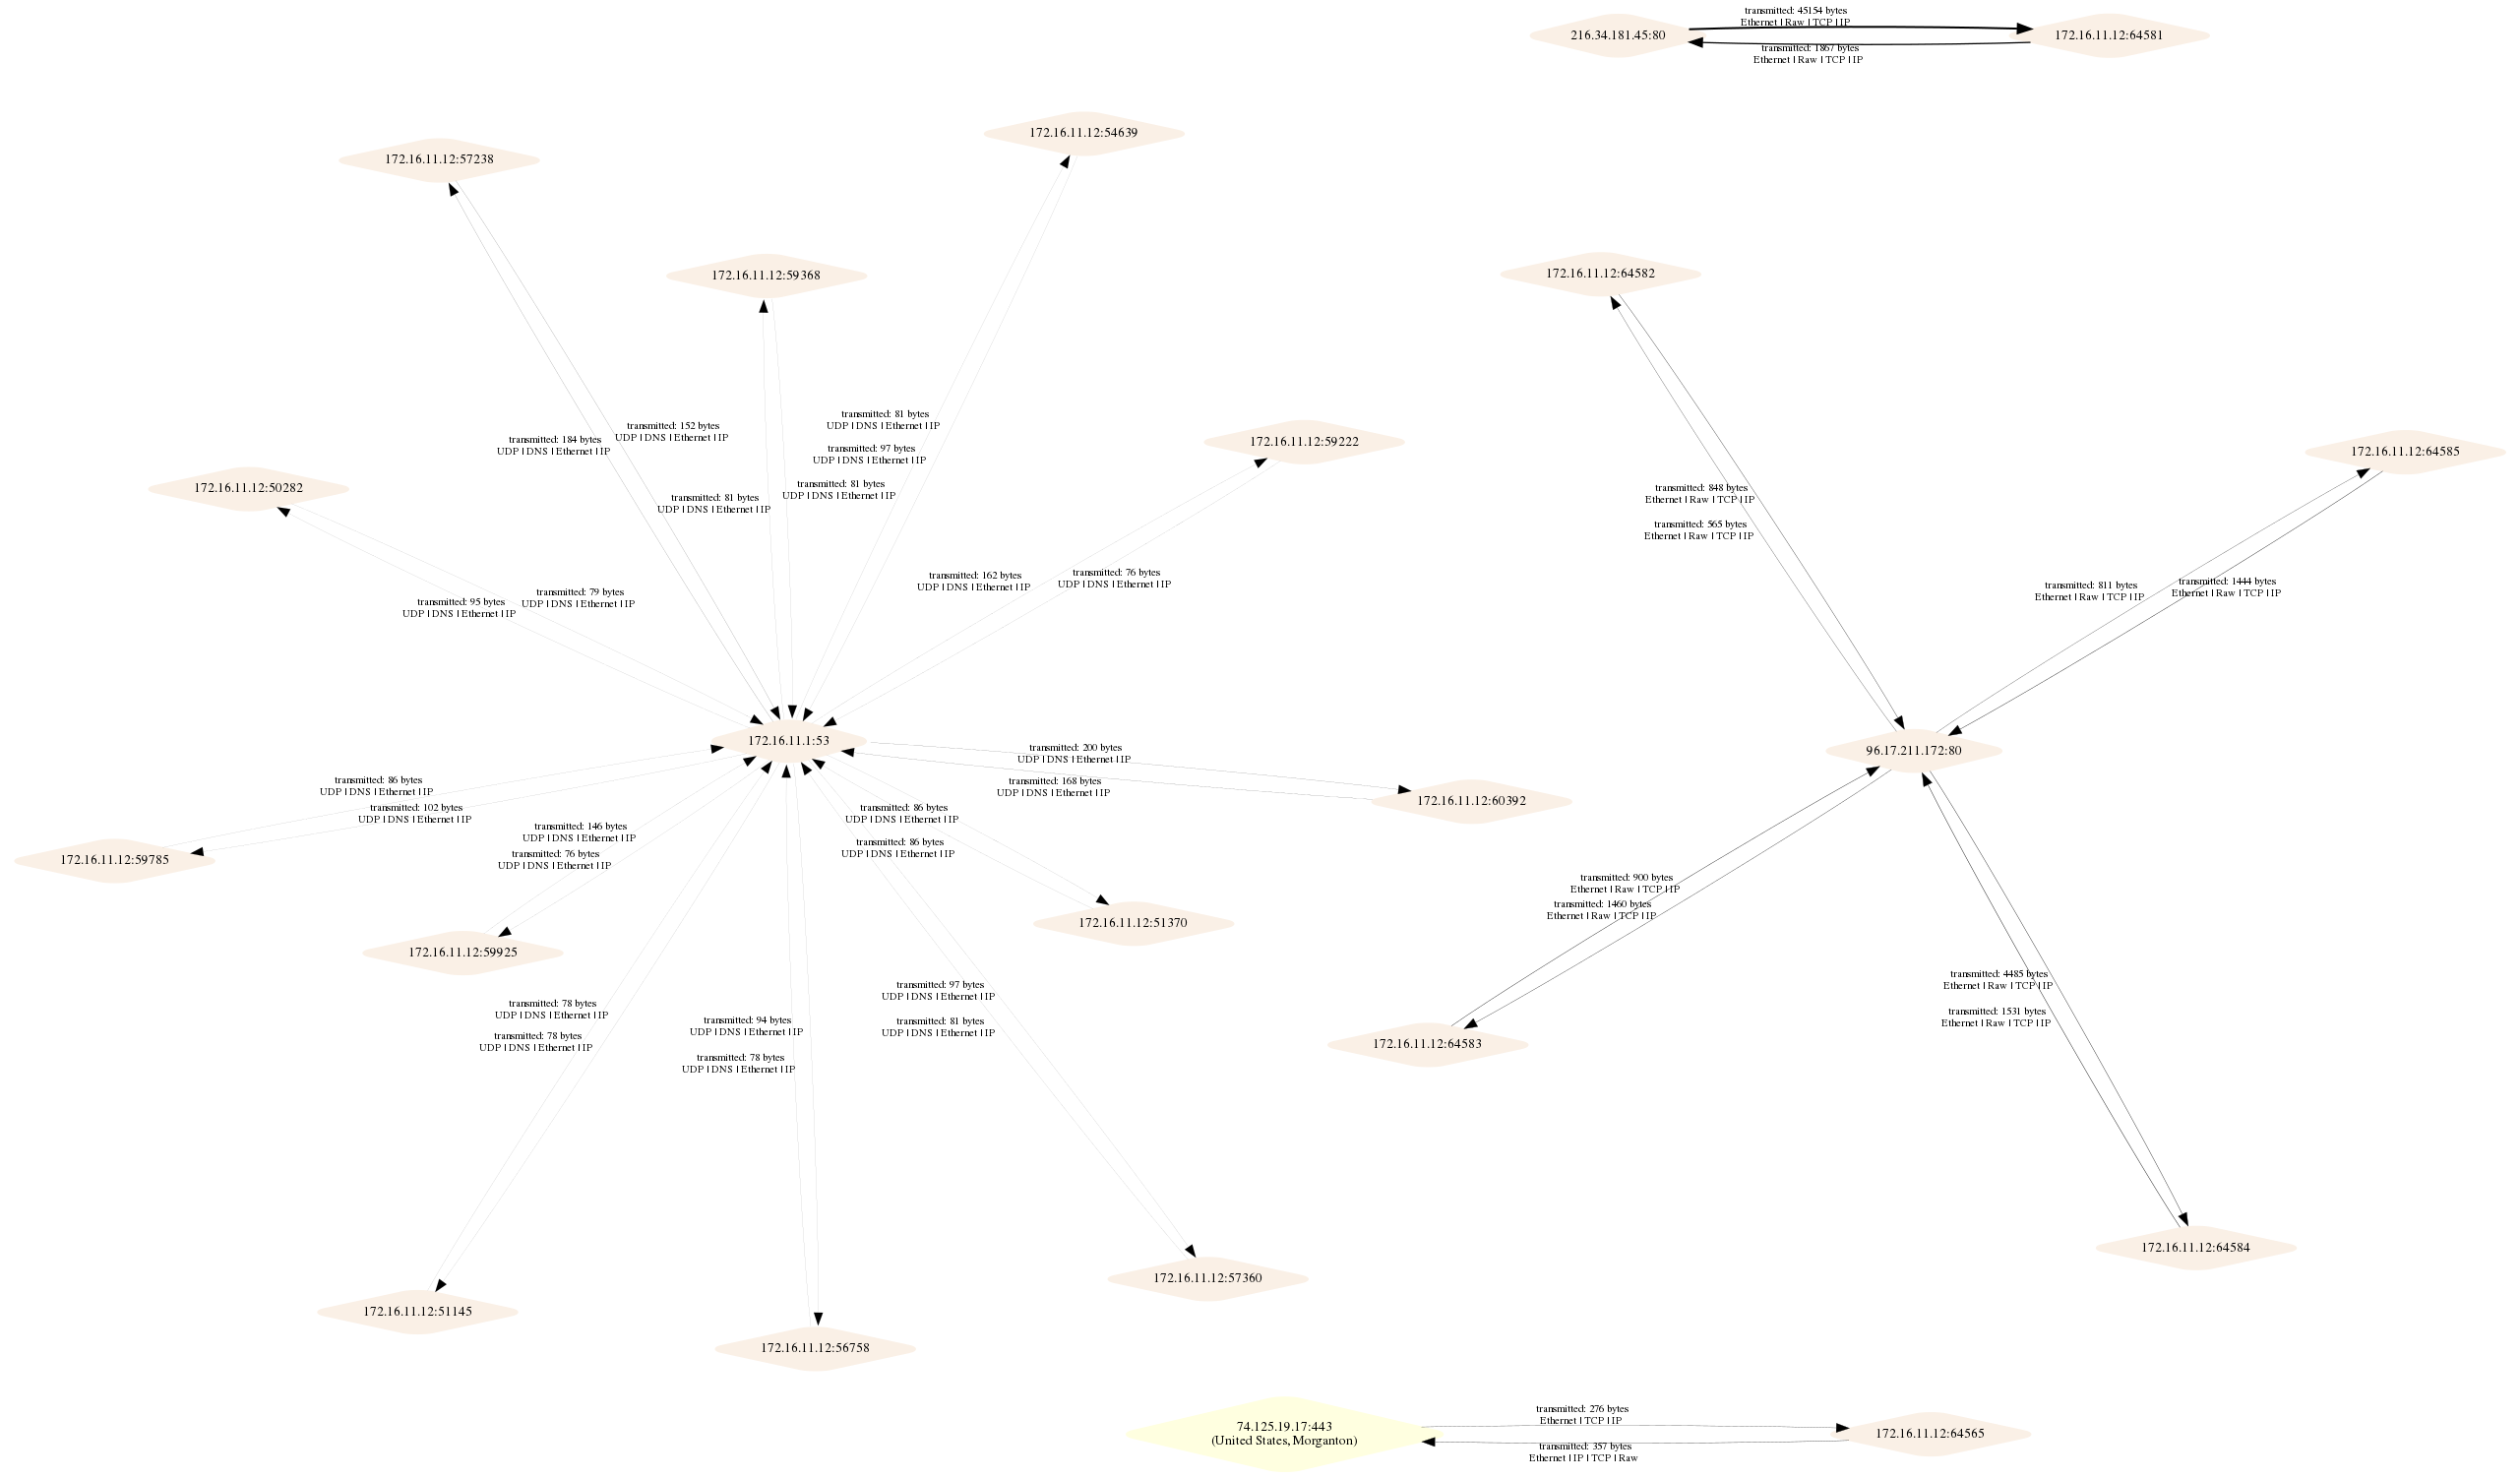 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
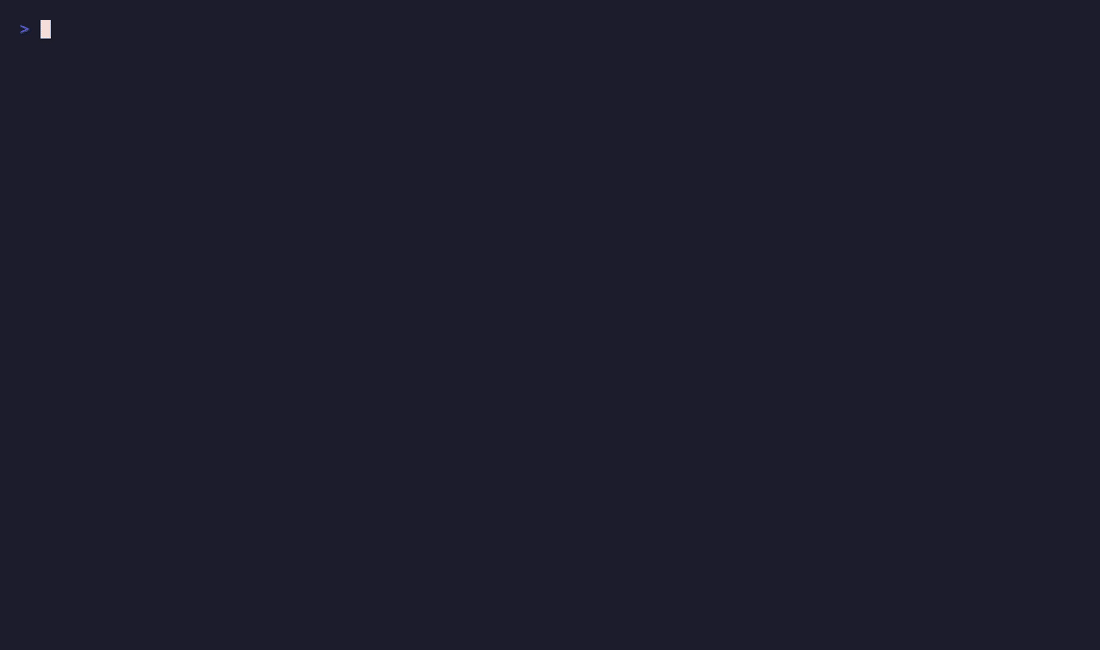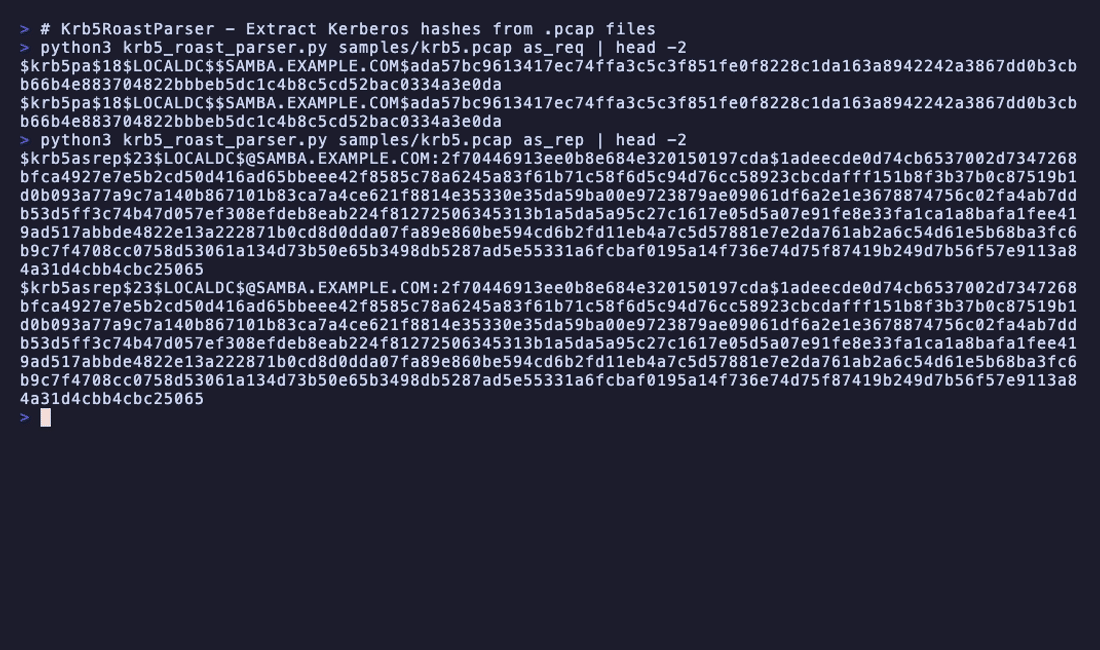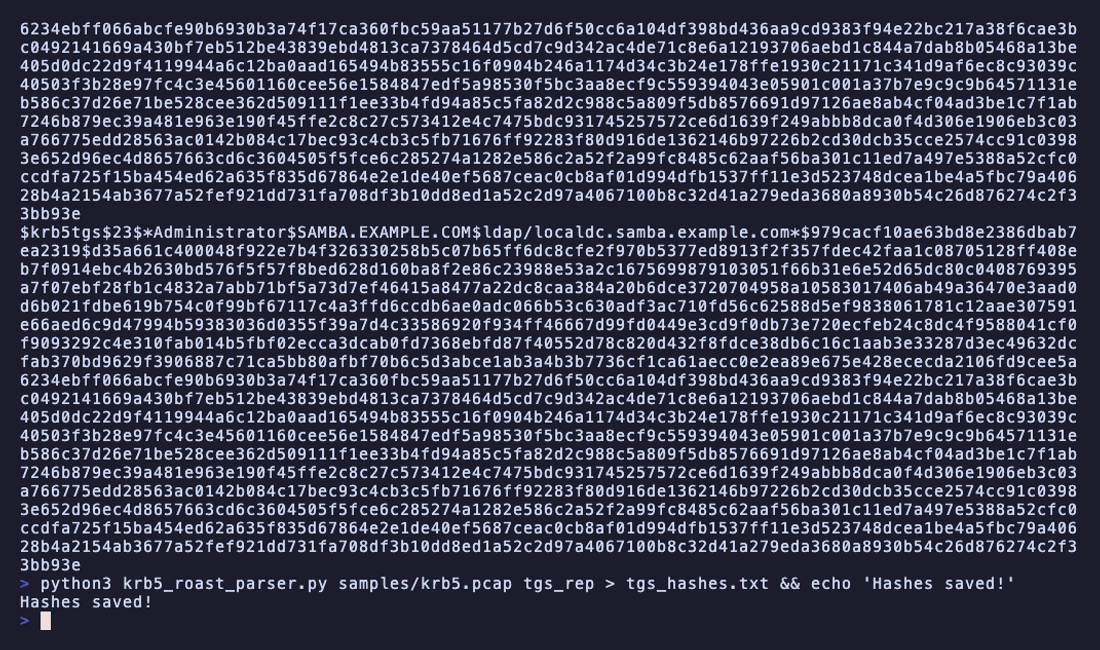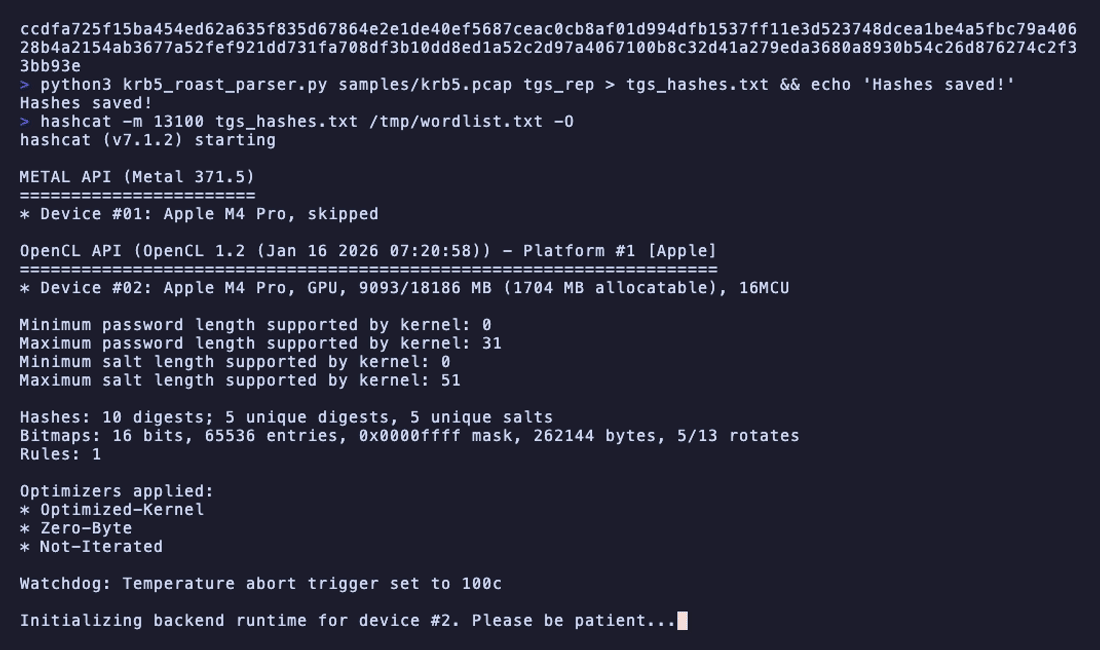 jalvarezz13/krb5roastparser
KrbRoastParser is a tool for parsing Kerberos packets from pcap files to extract AS-REQ, AS-REP and TGS-REP hashes
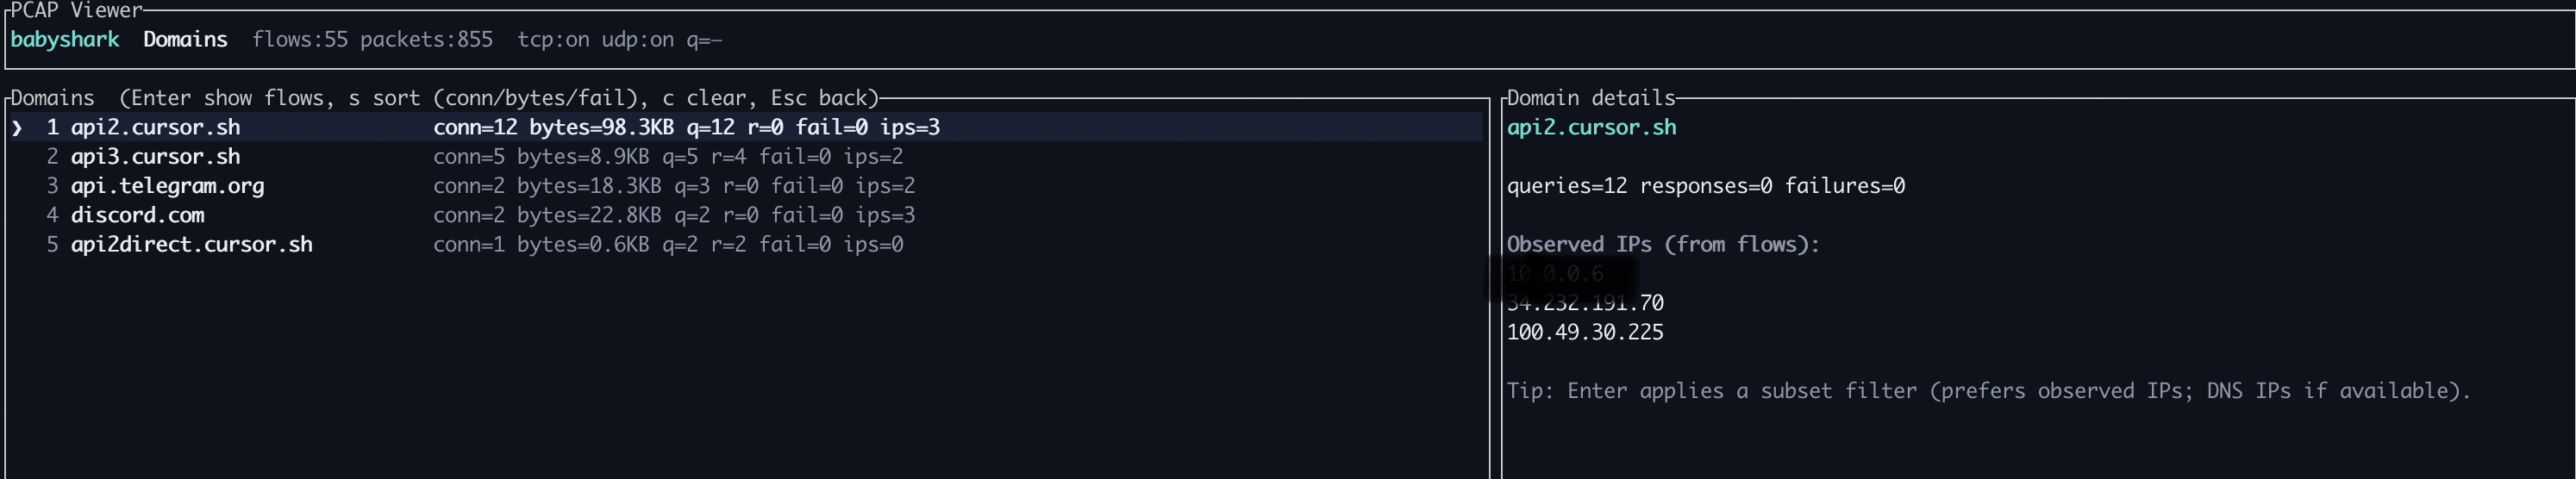 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 phillipmartin/gopassivedns
Network-based passive DNS logger capturing and logging DNS queries from live traffic or pcap files, outputting JSON for integration with SIEM and…
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
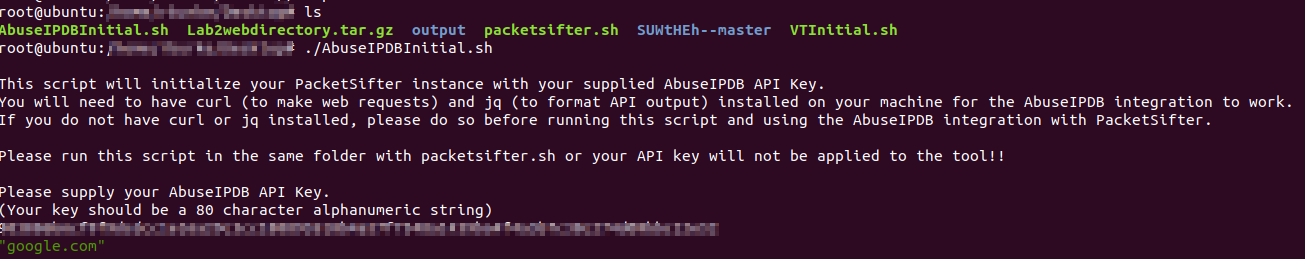 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
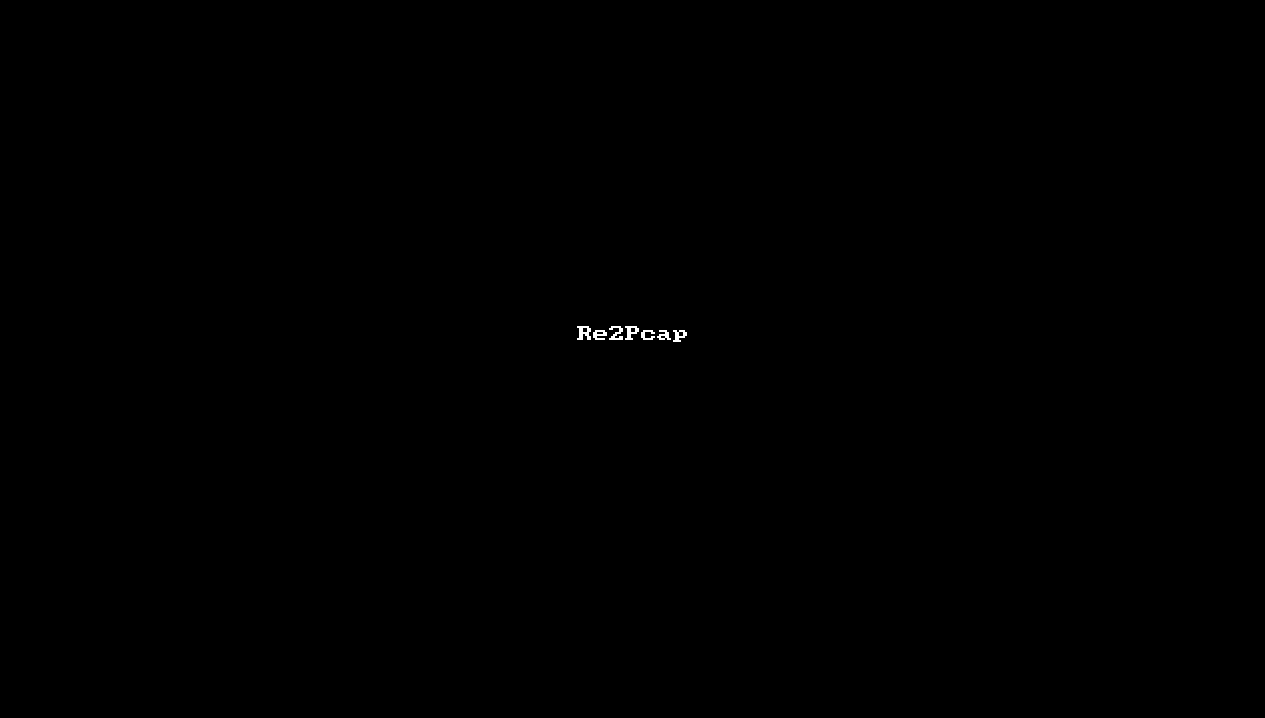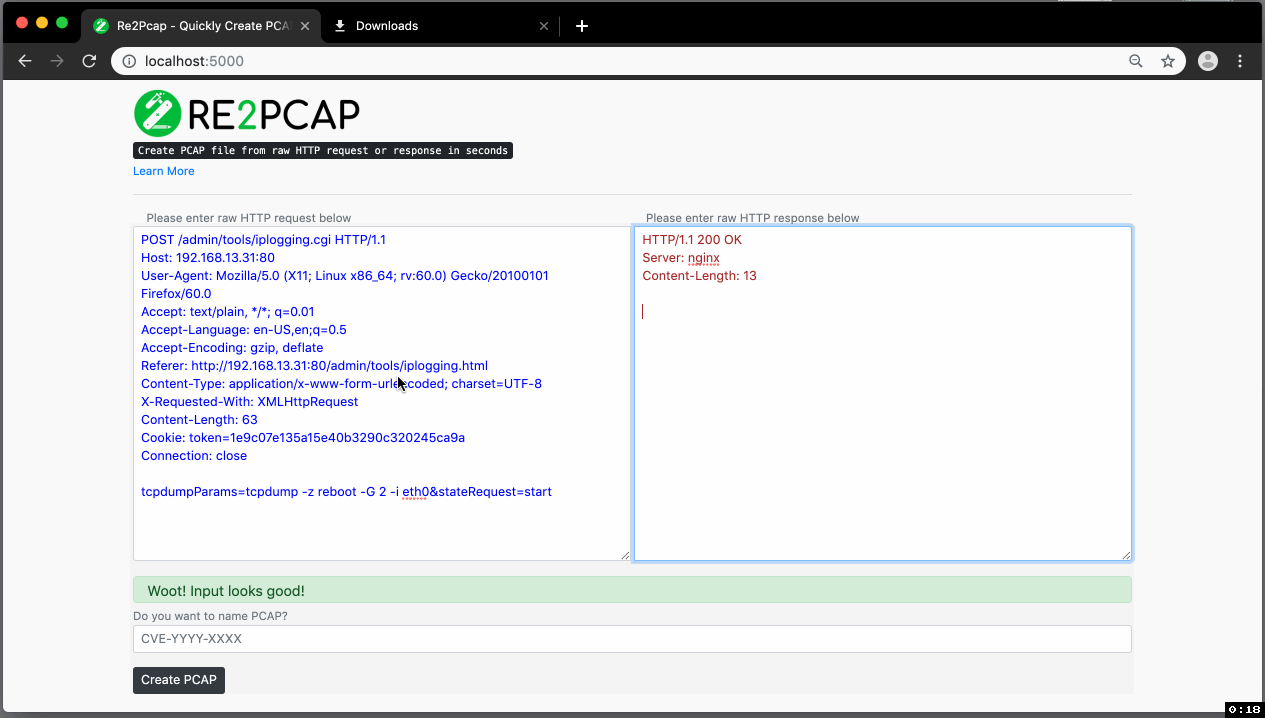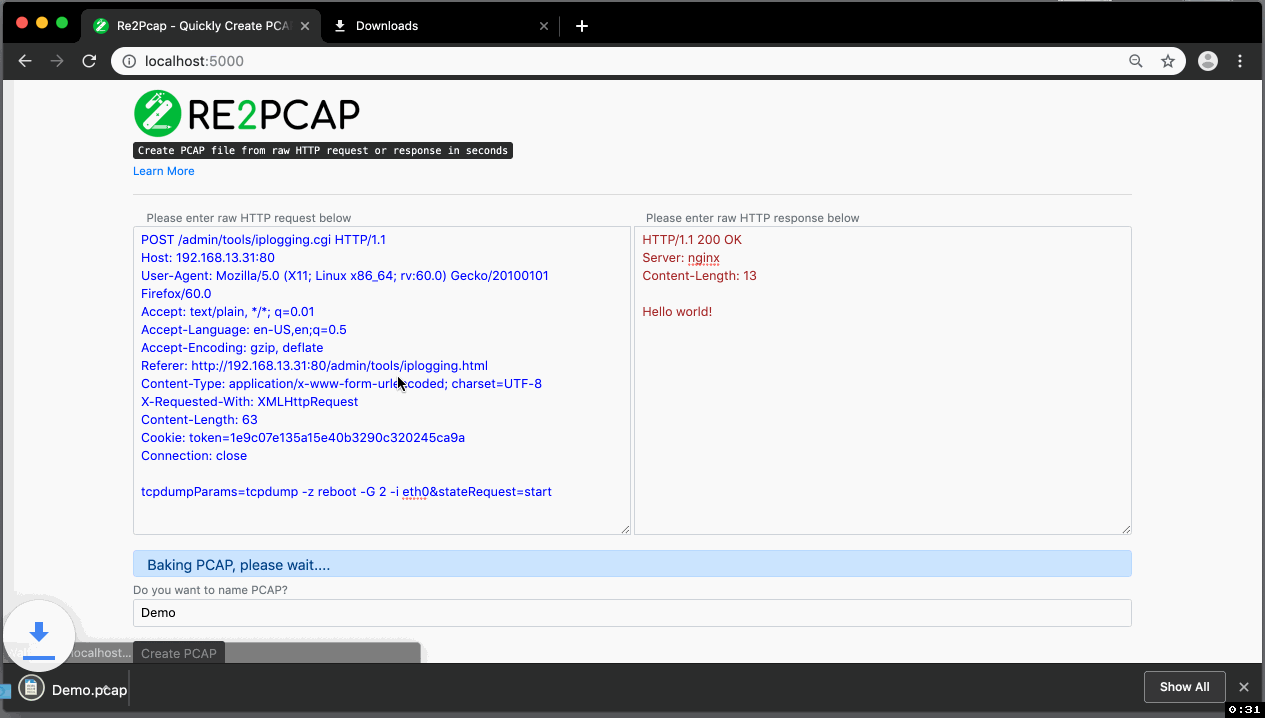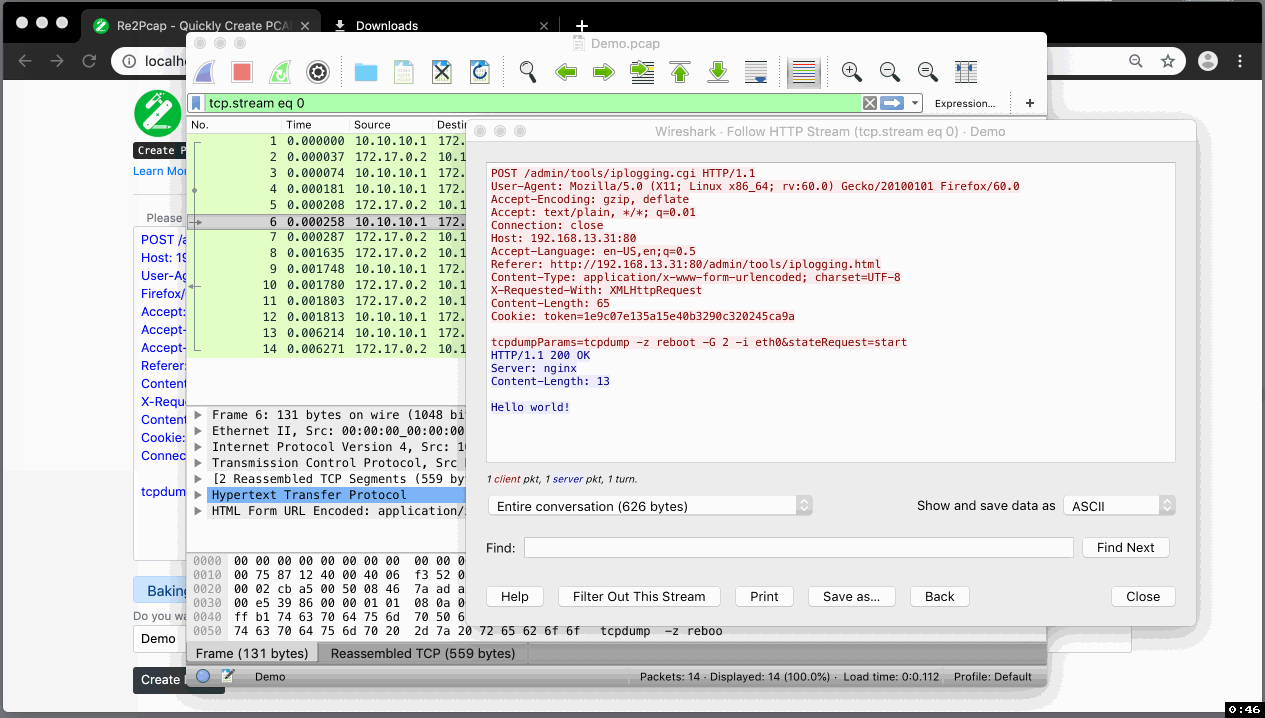 cisco-talos/re2pcap
Convert raw HTTP requests/responses into PCAP files for testing Snort IDS rules and network security analysis. Supports Docker deployment and…
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
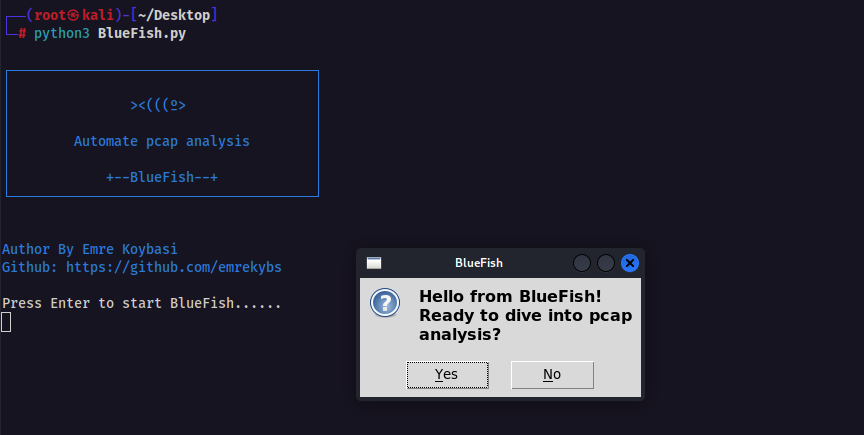 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 prprhyt/poc_tls1_3_cve-2020-13777
Proof-of-concept for CVE-2020-13777 (GnuTLS TLS 1.3 reconnect vulnerability). Parses pcap files to demonstrate the flaw for educational and technical…