

Dshell
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
digital-forensicsdns-analysisforensics+3
usarmyresearchlab/dshellDshell is a network forensic analysis framework.
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring

 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
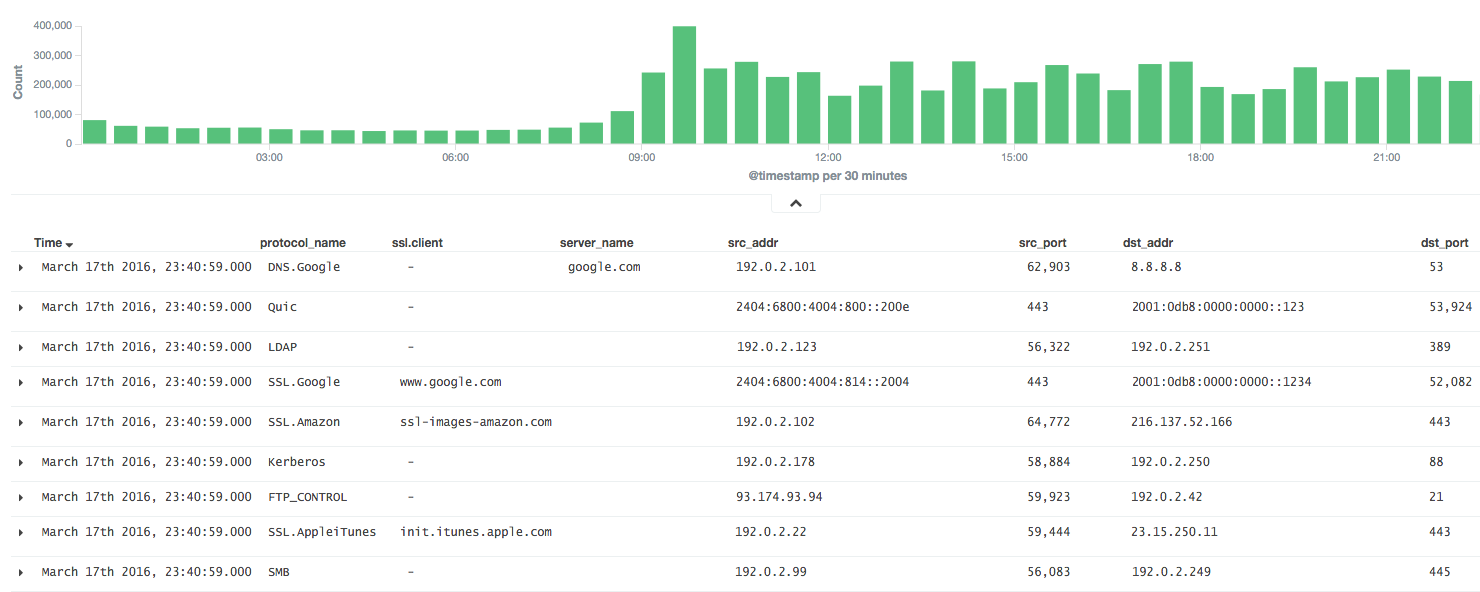 knqyf263/ndff
A flow-based network monitor with Deep Packet Inspection
 trinadh465/external_tcpdump_cve-2018-14880
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…
 trinadh465/external_tcpdump_cve-2018-14879
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…
 trinadh465/external_tcpdump_cve-2018-14469
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
 thelightscope/thelightscope
TheLightScope
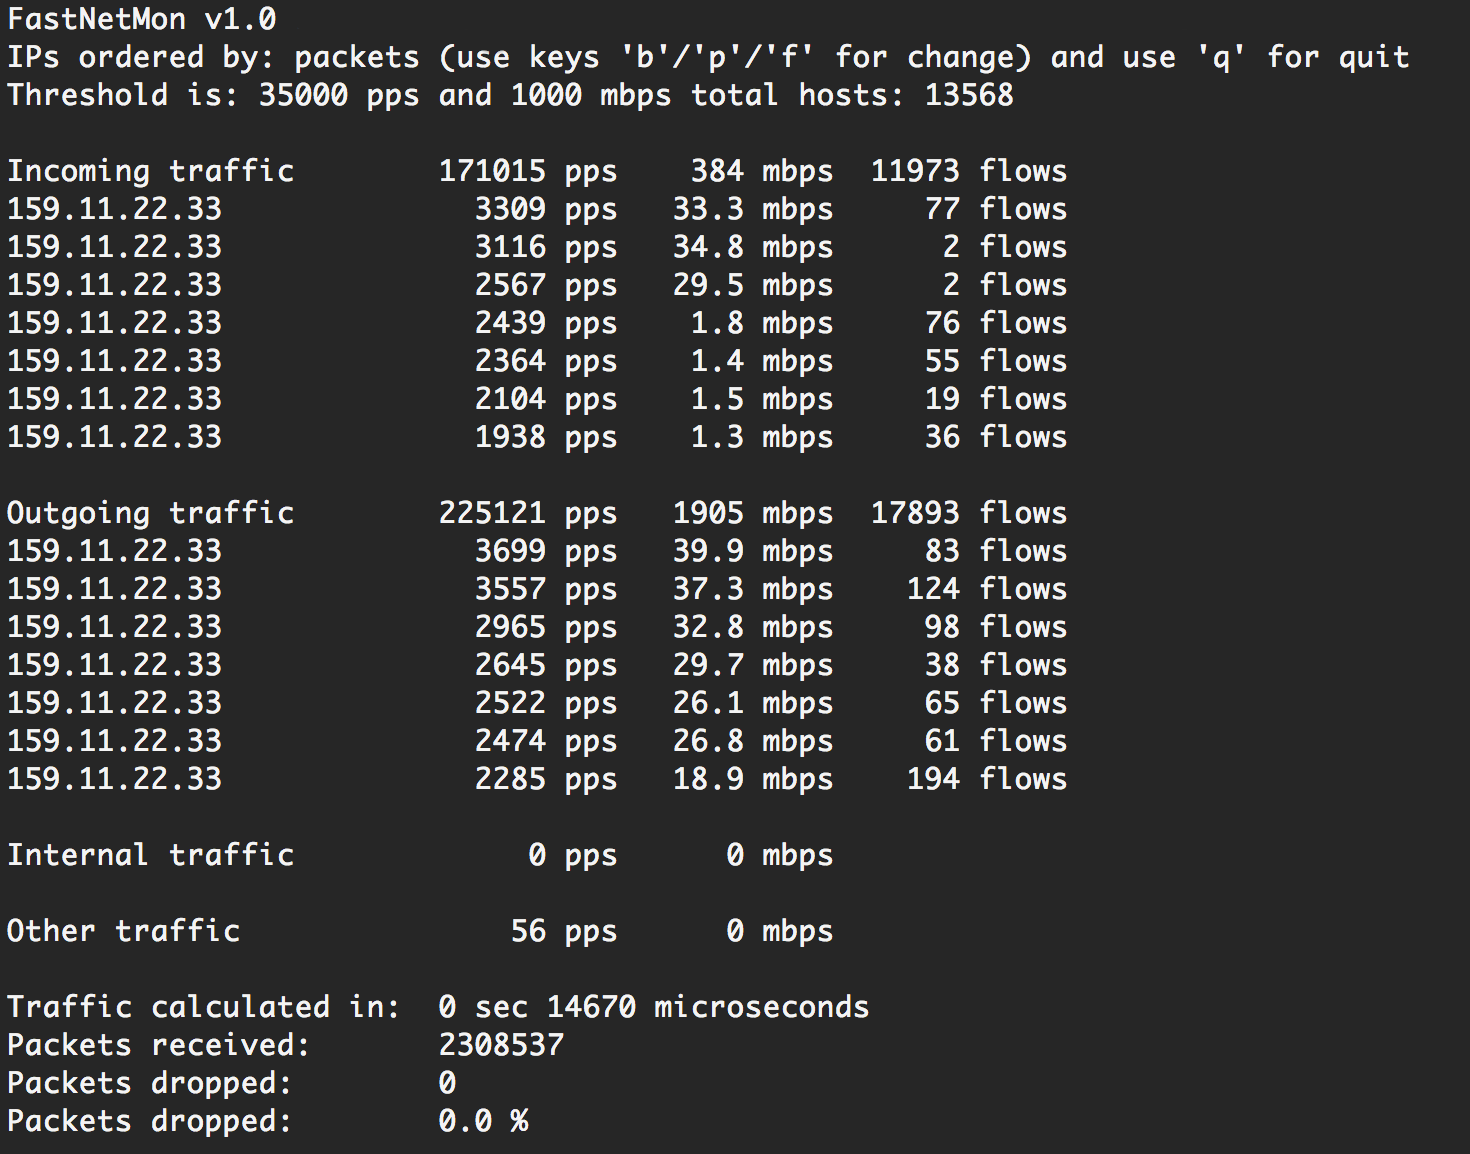 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
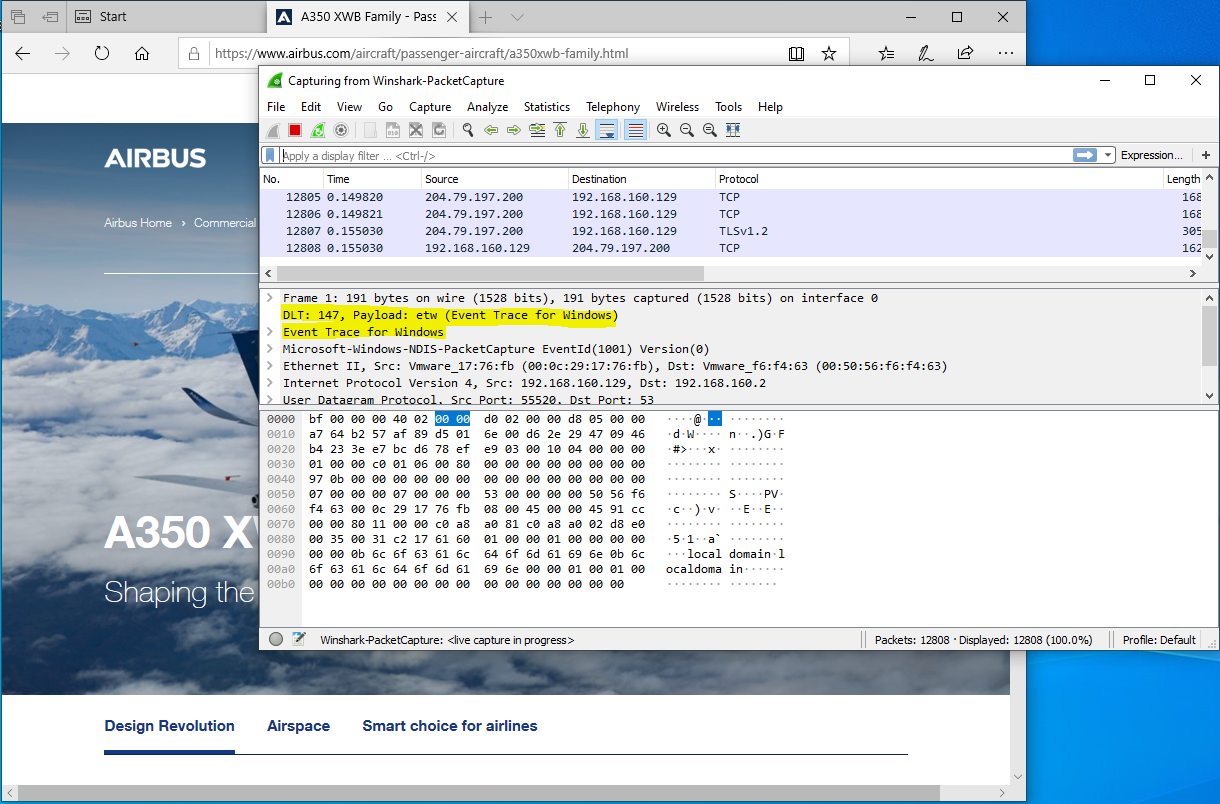 airbus-cert/winshark
A wireshark plugin to instrument ETW
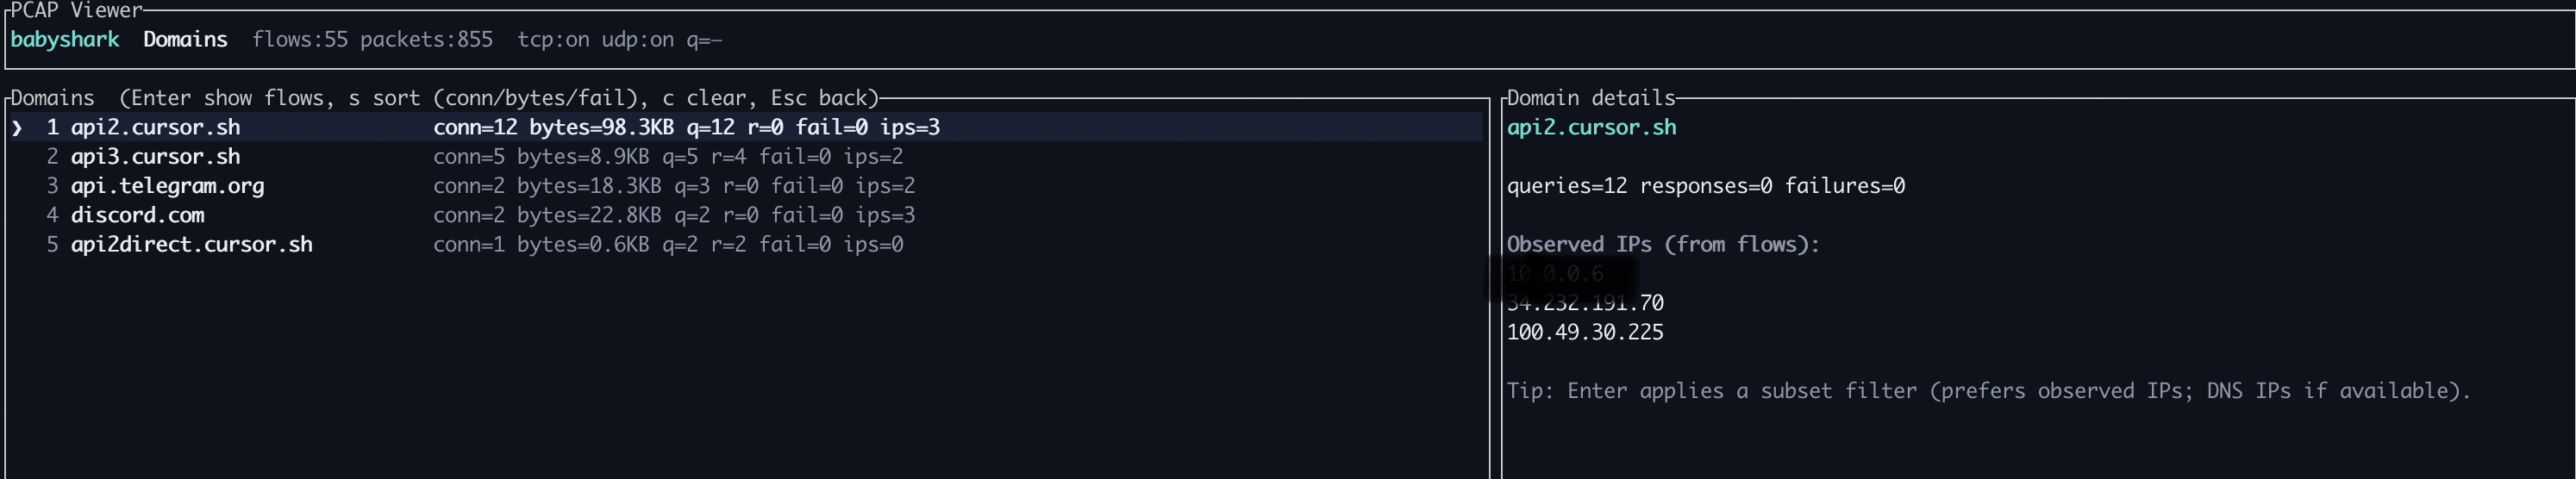 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 corelight/raspi-corelight
Corelight@Home script