
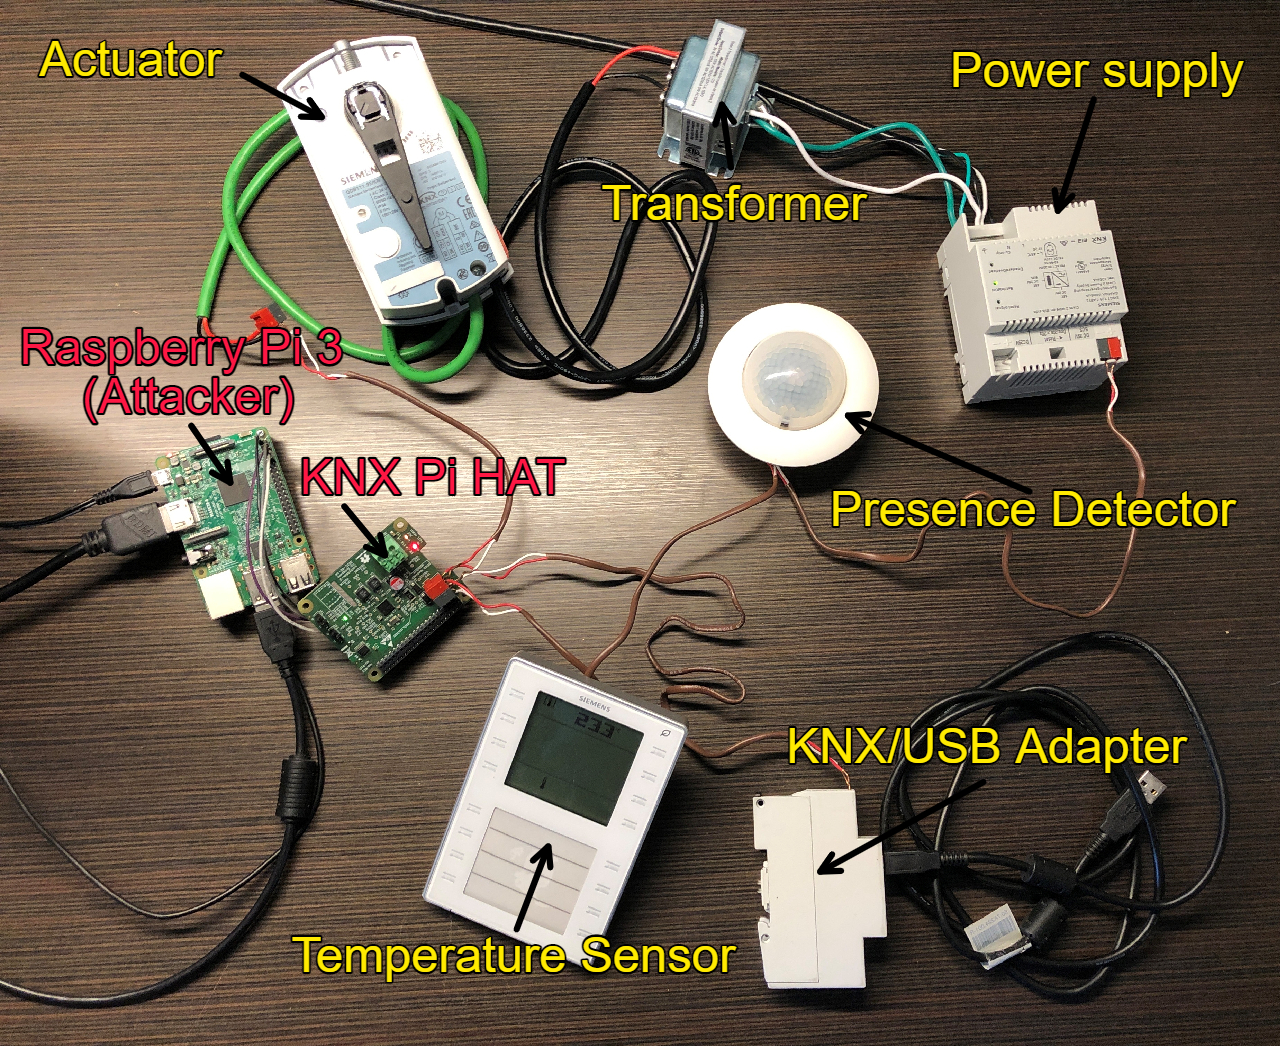
KNX-Bus-Dump
 chrism09/knx-bus-dump
A tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…
digital-forensicsforensicshardware-iot-security+3
12
chrism09/knx-bus-dumpA tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
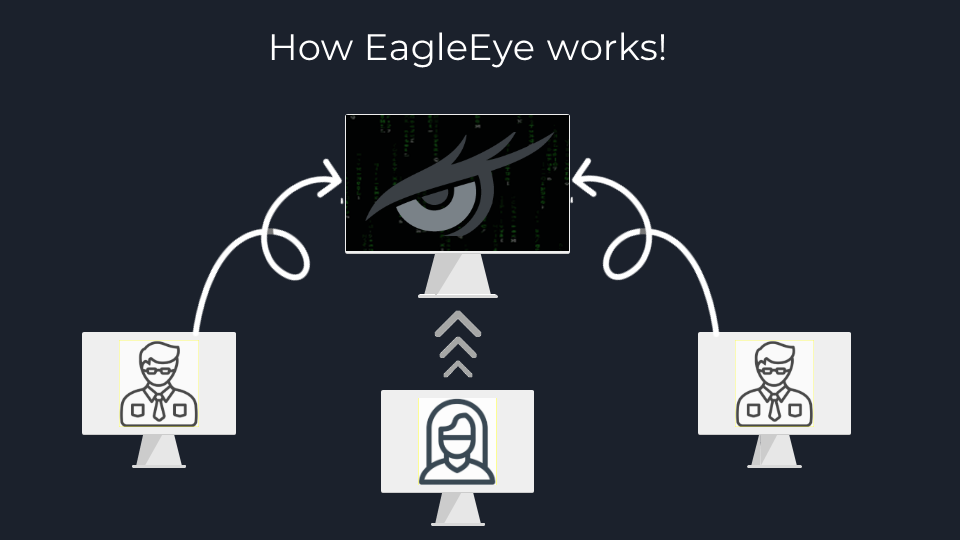 d4vinci/eagleeye
A host-based IDS and network monitoring system (My graduation project)
 aseemjakhar/kcmd
Kankun Smart Socket Hijacker and Sniffer. The kankun smart socket and its mobile app use a hardcoded AES 256 bit key to encrypt and decrypt…
 oisf/libhtp
Security-aware HTTP protocol parser library used by IDS/IPS engines to inspect and normalize HTTP traffic for threat detection.
 nmap/npcap
Nmap Project's Windows packet capture and transmission library
 nccgroup/pcap-burp
Pcap importer for Burp
 jip-0-0-0-0-0/cve-2024-38063-scanner
A Python tool leveraging Shodan and Scapy to identify and exploit Windows systems vulnerable to CVE-2024-38063, enabling targeted Denial of Service…
 prprhyt/poc_tls1_3_cve-2020-13777
Proof-of-concept for CVE-2020-13777 (GnuTLS TLS 1.3 reconnect vulnerability). Parses pcap files to demonstrate the flaw for educational and technical…
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
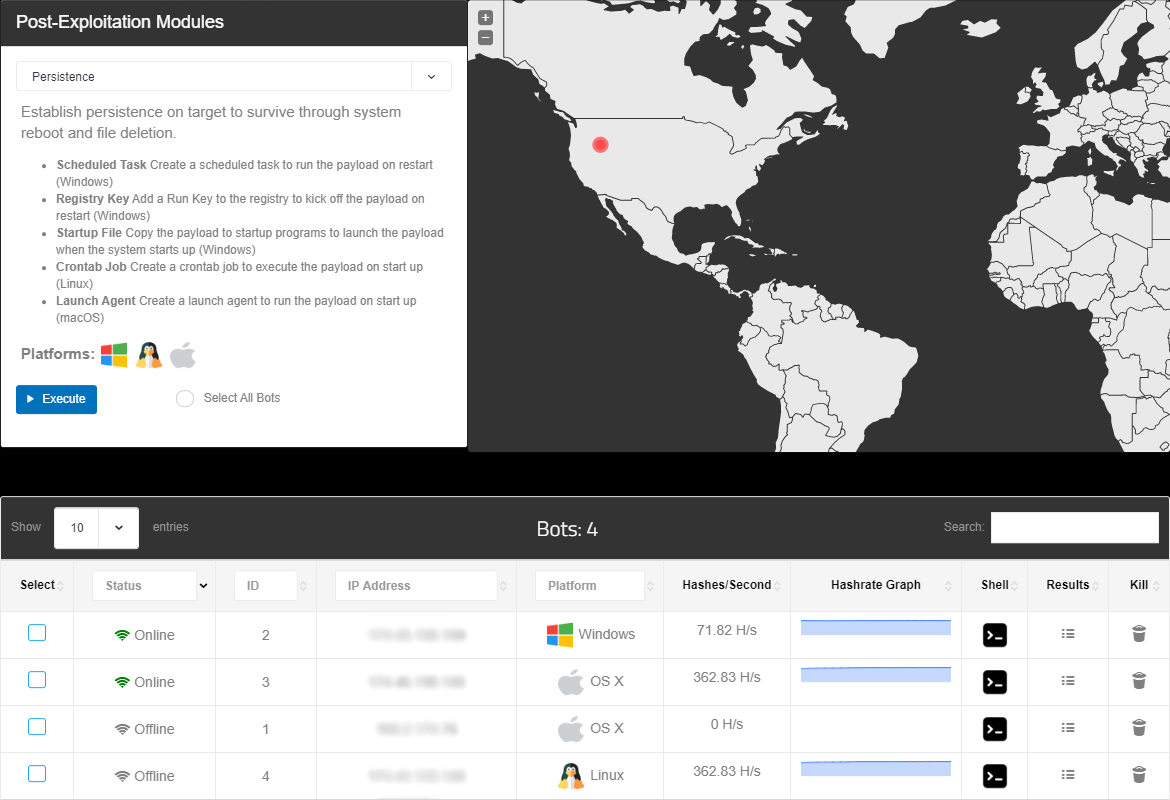 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 libnet/nemesis
A command-line network packet crafting and injection utility
 greatscottgadgets/libbtbb
C library for decoding Bluetooth baseband packets and extracting piconet information from Ubertooth and USRP hardware for wireless analysis.
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
 aress31/wirespy
Framework designed to automate various wireless networks attacks (the project was presented on Pentester Academy TV's toolbox in 2017).
