
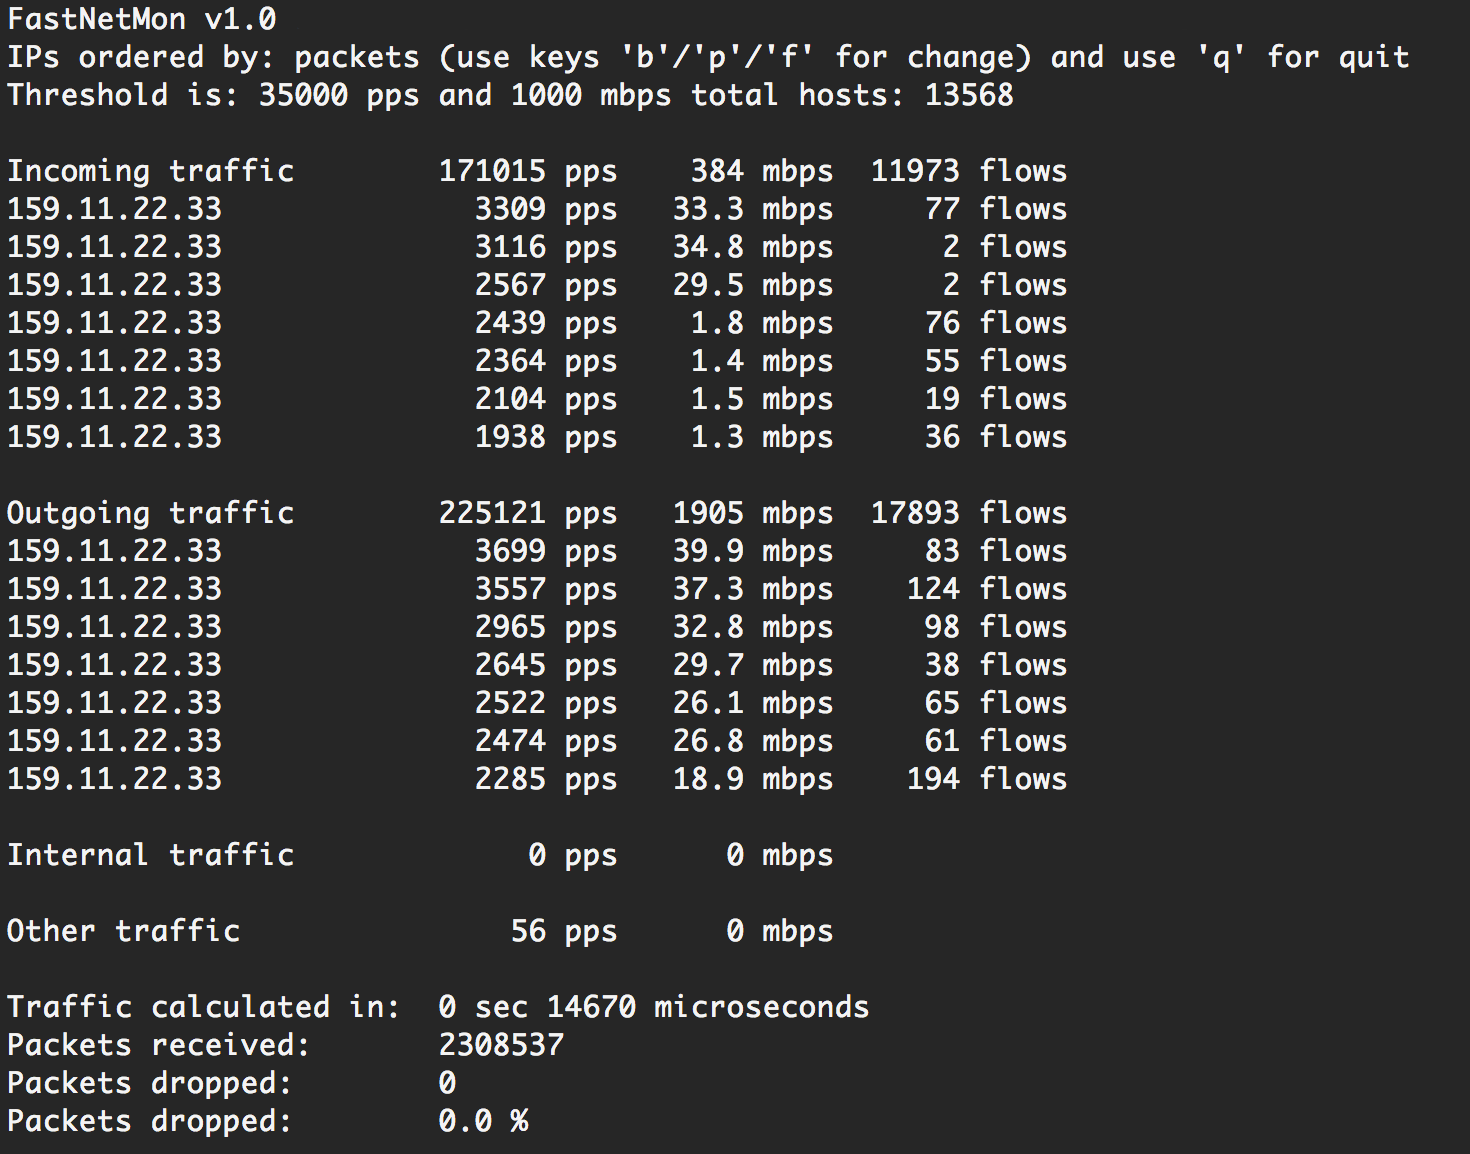
fastnetmon
 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
anomaly-detectionincident-responselog-analysis+5
3.7k1 month ago
pavel-odintsov/fastnetmonVery fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 bluez/bluez
Linux Bluetooth protocol stack with daemons, command-line clients, HCI monitor, and support for BR/EDR, LE, Mesh, audio profiles, providing device…
 halildeniz/macmaster
Advanced Network Interface Management and Monitoring
 yili-soc/vm-homelab-log4shell-assessment
Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 google/gopacket
Provides packet processing capabilities for Go
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 nccgroup/pcap-burp
Pcap importer for Burp
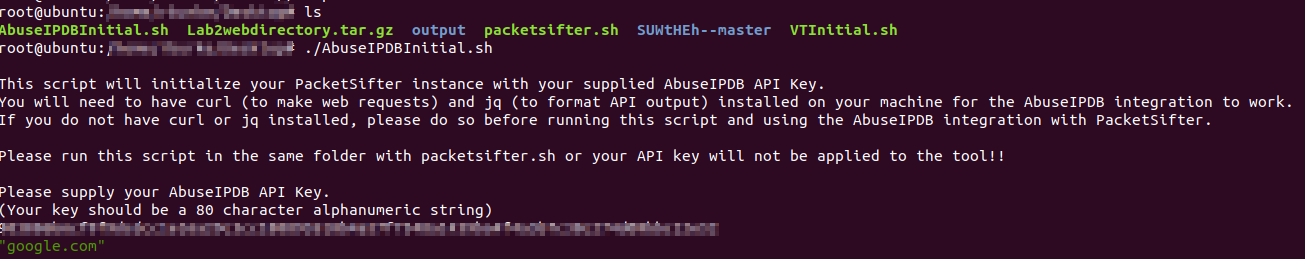 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 thelightscope/thelightscope
TheLightScope
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files