
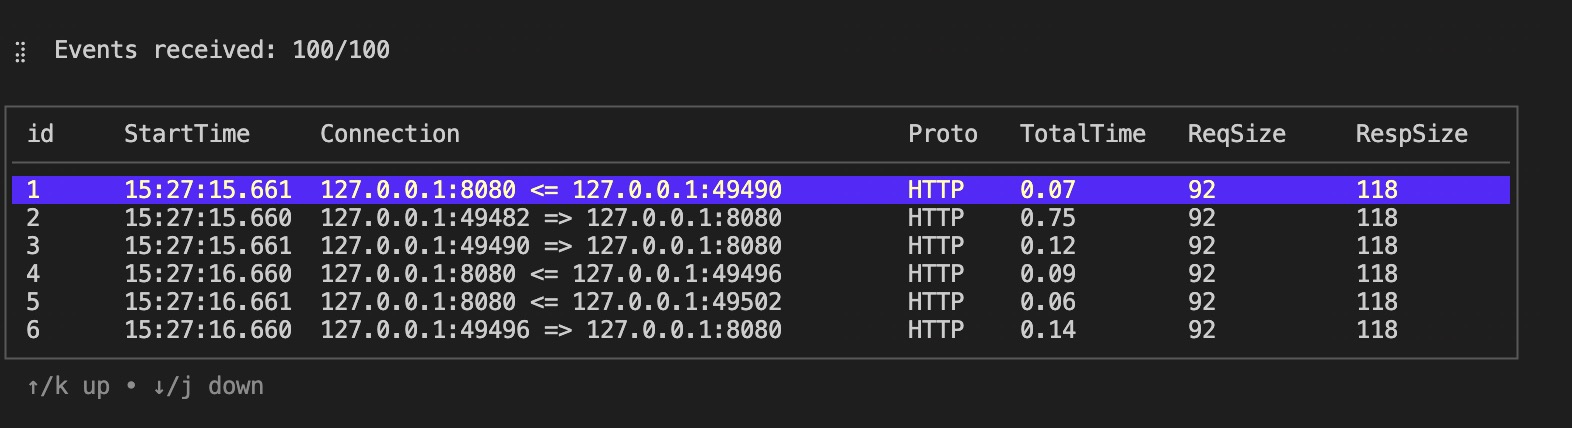
kyanos
 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
dns-analysisdynamic-analysis-sandboxinglog-analysis+3
5.1k
hengyoush/kyanosKyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 quarkslab/peetch
eBPF-based toolkit for sniffing network traffic, extracting OpenSSL TLS keys, and intercepting/decrypting TLS 1.2 connections in real time using…
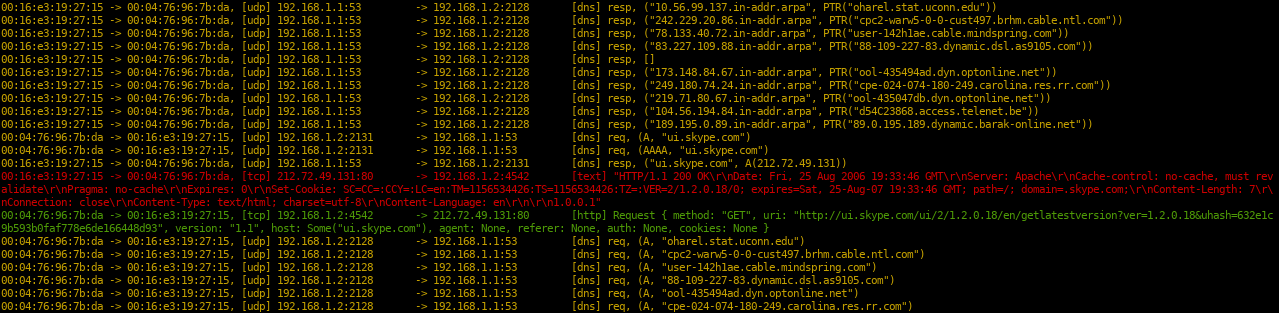 kpcyrd/sniffglue
Secure multithreaded packet sniffer
 mandiant/flare-fakenet-ng
FakeNet-NG - Next Generation Dynamic Network Analysis Tool
 nccgroup/ebpf
eBPF - extended Berkeley Packet Filter tooling
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 40t/go-sniffer
🔎Sniffing and parsing mysql,redis,http,mongodb etc protocol. 抓包截取项目中的数据库请求并解析成相应的语句。