An-Integrated-Wireless-Network-Forensic-Analysis-Framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…

The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more

Polymorph is a real-time network packet manipulation framework with support for almost all existing protocols

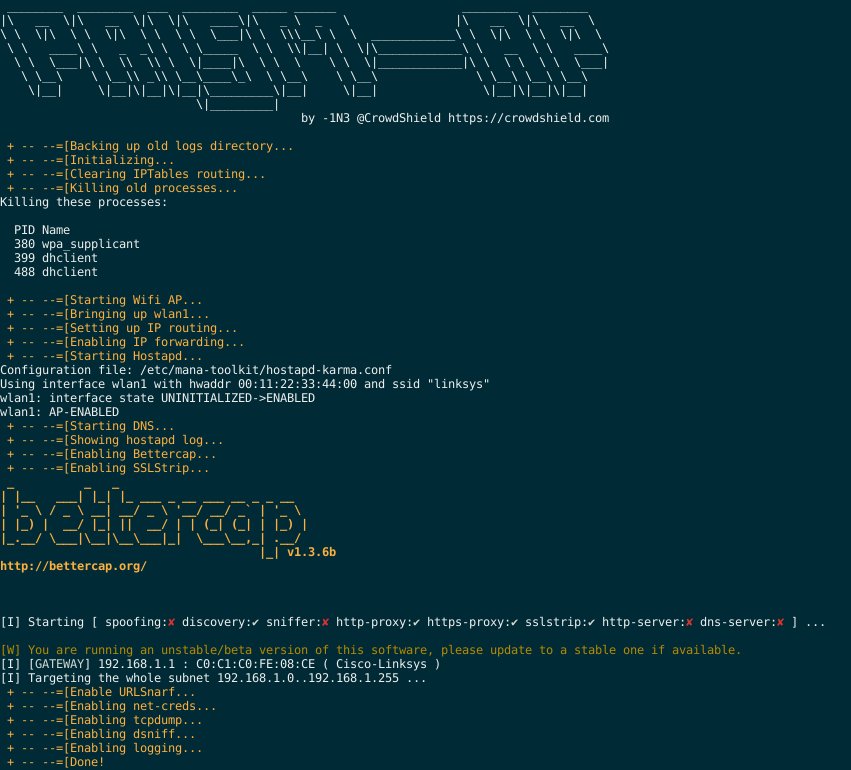
An automated Wireless RogueAP MITM attack framework.

Framework for Man-In-The-Middle attacks

This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

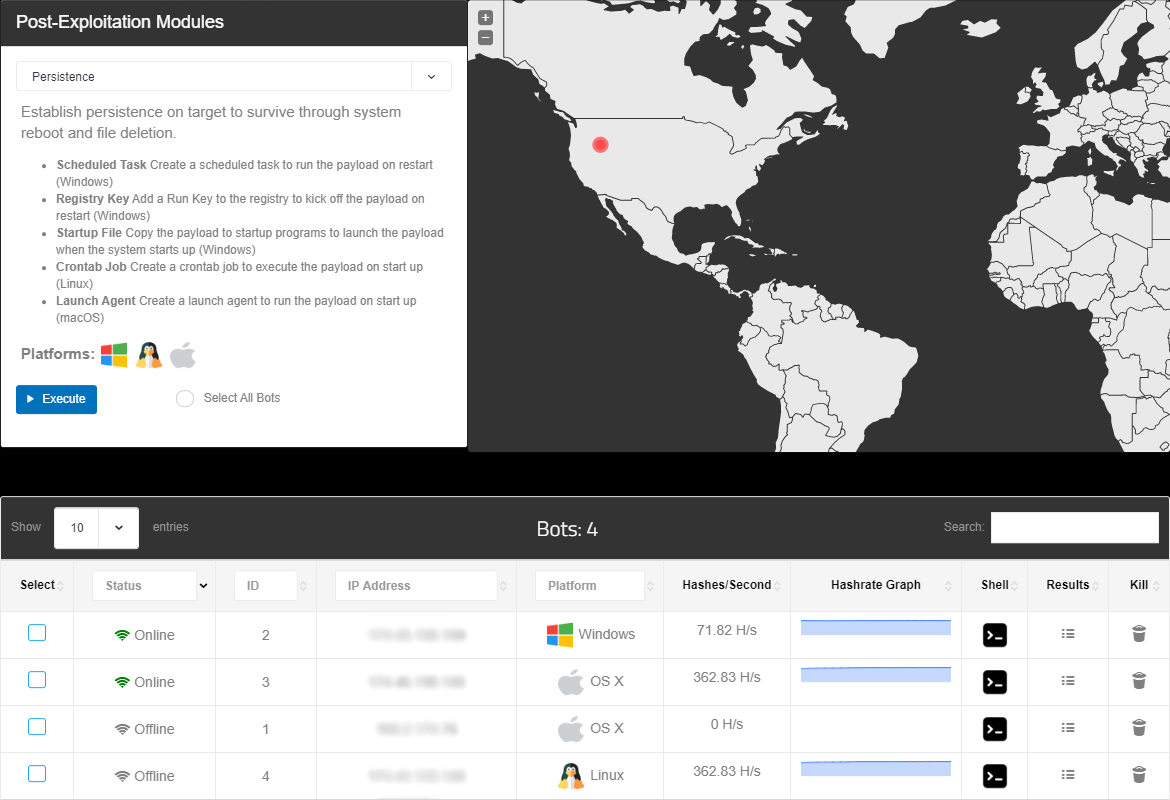
An open-source post-exploitation framework for students, researchers and developers.

System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…

High-speed packet processing framework

Dshell is a network forensic analysis framework.

Framework designed to automate various wireless networks attacks (the project was presented on Pentester Academy TV's toolbox in 2017).

Snoopy v2.0 - modular digital terrestrial tracking framework

Bluetooth experimentation framework for Broadcom and Cypress chips.

Functional Network Framework for Multi-Core Architectures

A framework for BREACH and other compression-based crypto attacks

extensible exploitation framework shipped on a modular multi-tasking architecture