

cyberprobe
 cybermaggedon/cyberprobe
Capturing, analysing and responding to cyber attacks
cloud-securitydefensive-toolsdynamic-analysis-sandboxing+4
174
cybermaggedon/cyberprobeCapturing, analysing and responding to cyber attacks
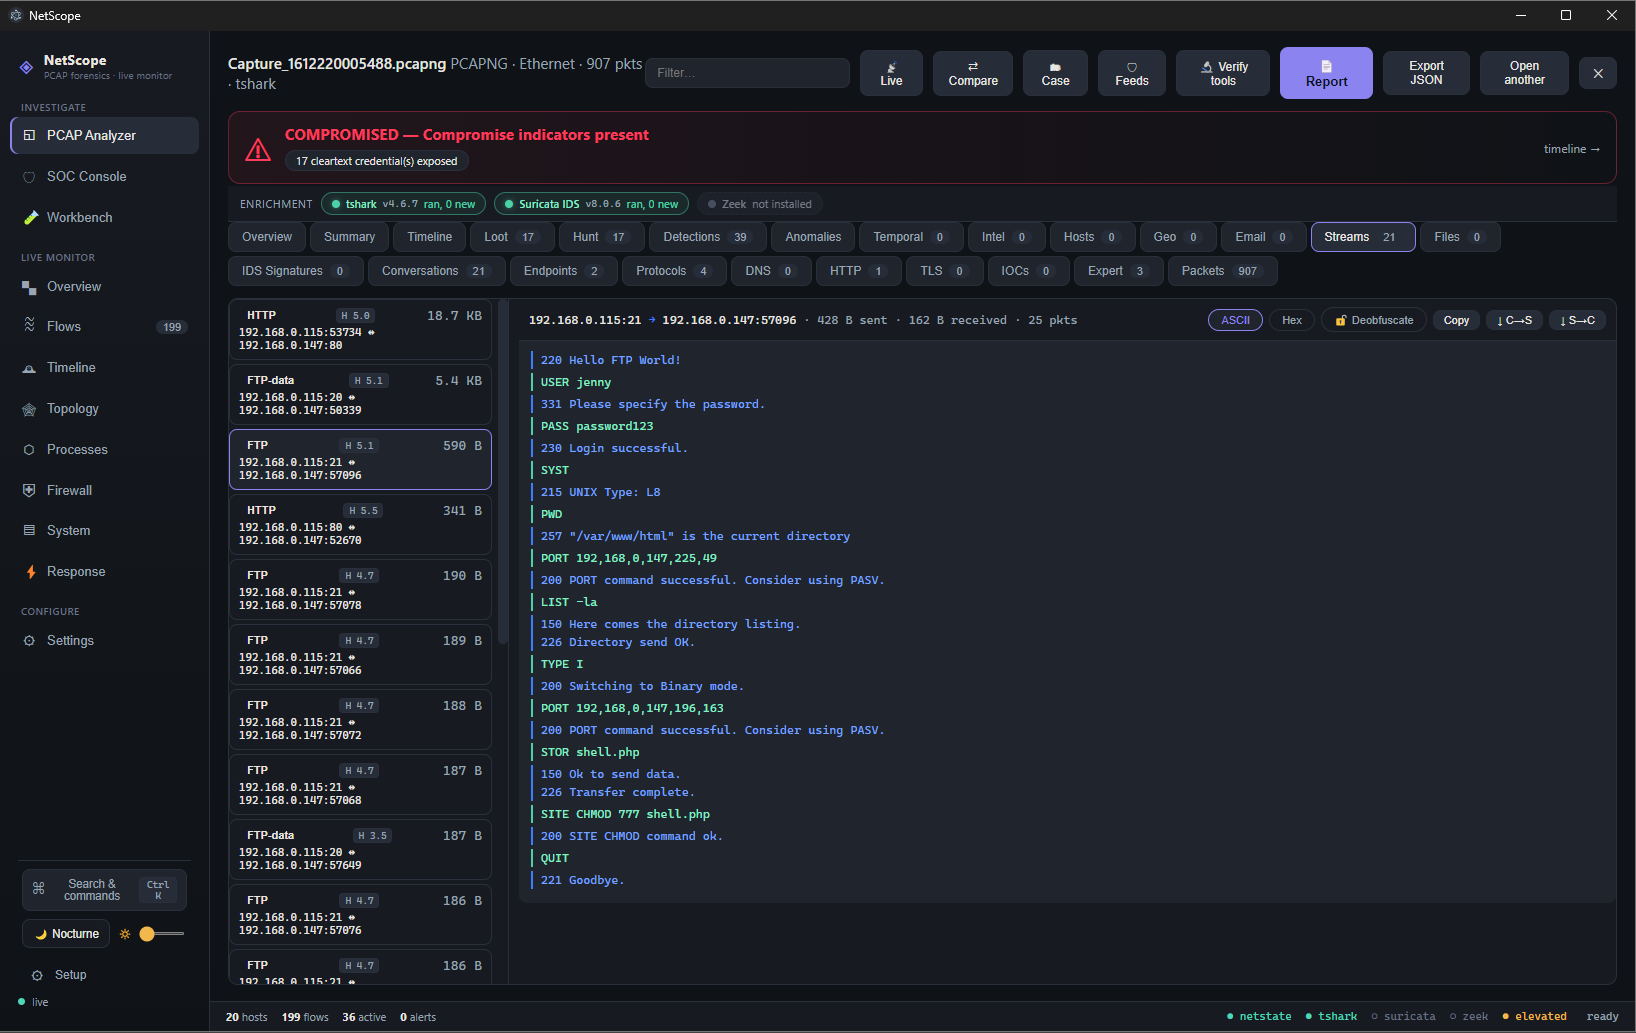 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 malfunkt/hyperfox
HTTP/HTTPS MITM proxy and recorder.
 corelight/zeek-quic
Bro analyzer that detects Google's QUIC protocol
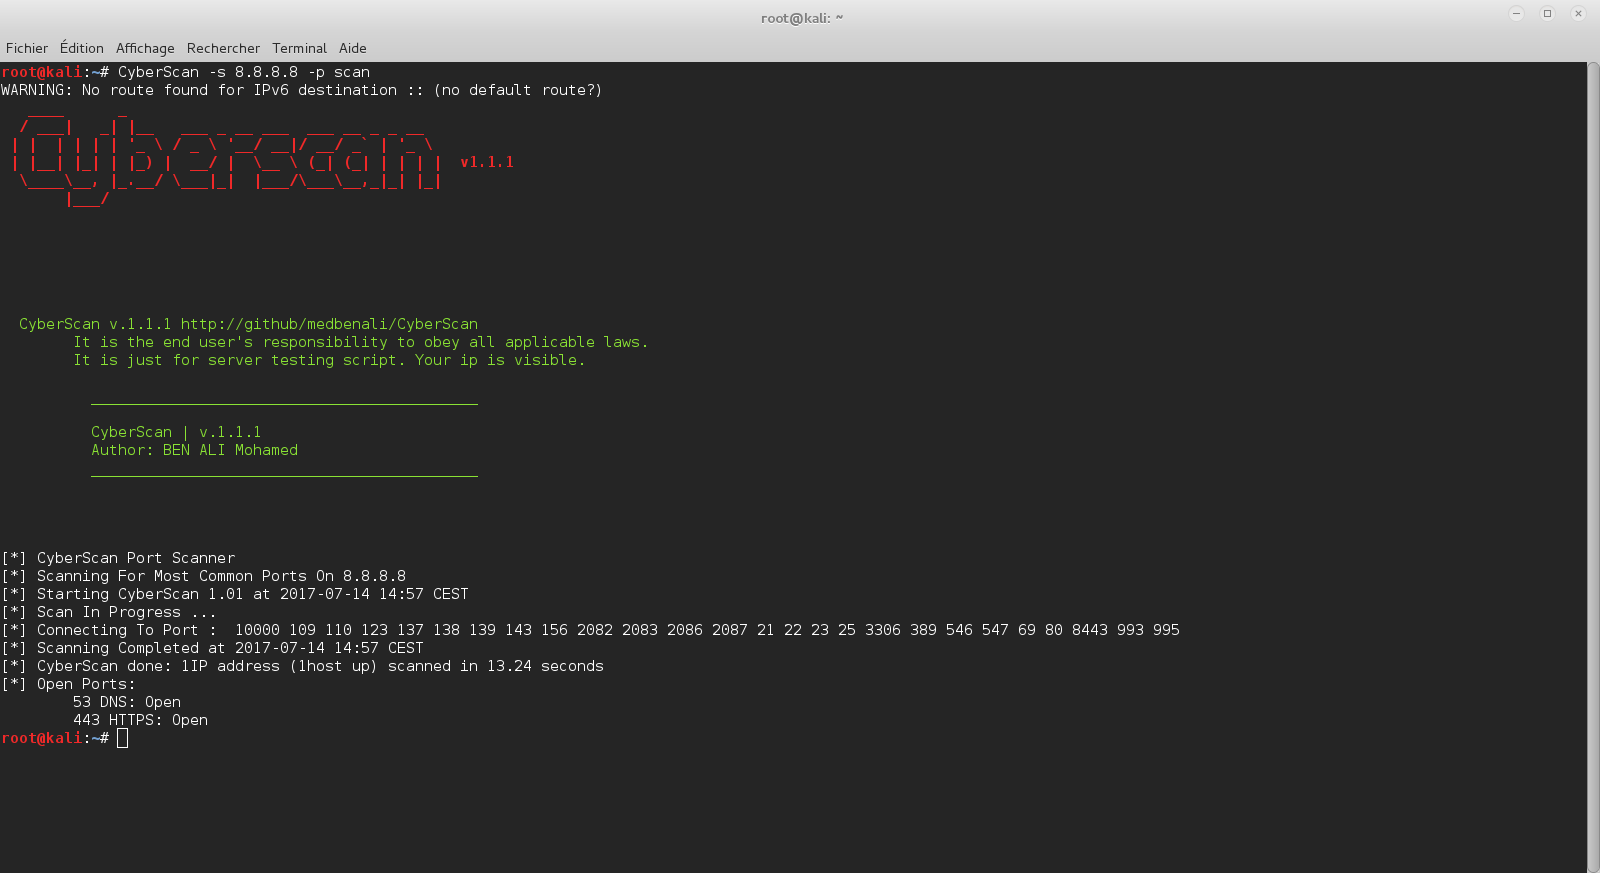 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
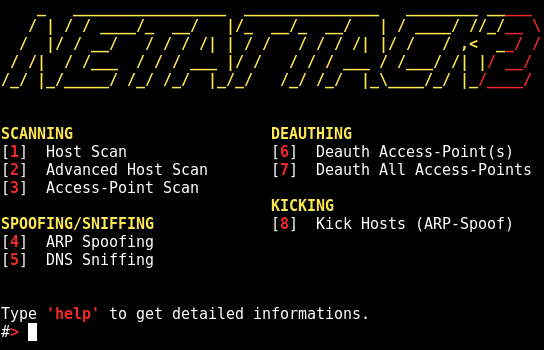 chrizator/netattack2
An advanced network scan and attack script based on GUI. 2nd version of no-GUI netattack.
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
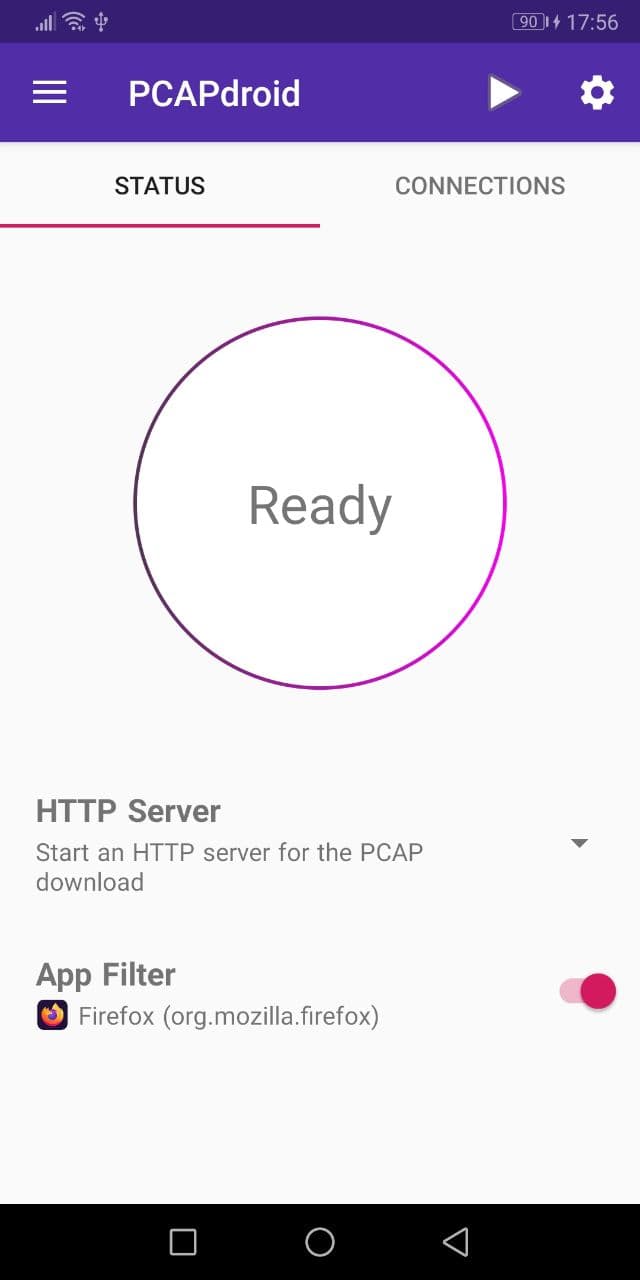 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 ivanvza/arpy
Mac OSX ARP spoof (MiTM) tool that can also plug into Gource
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
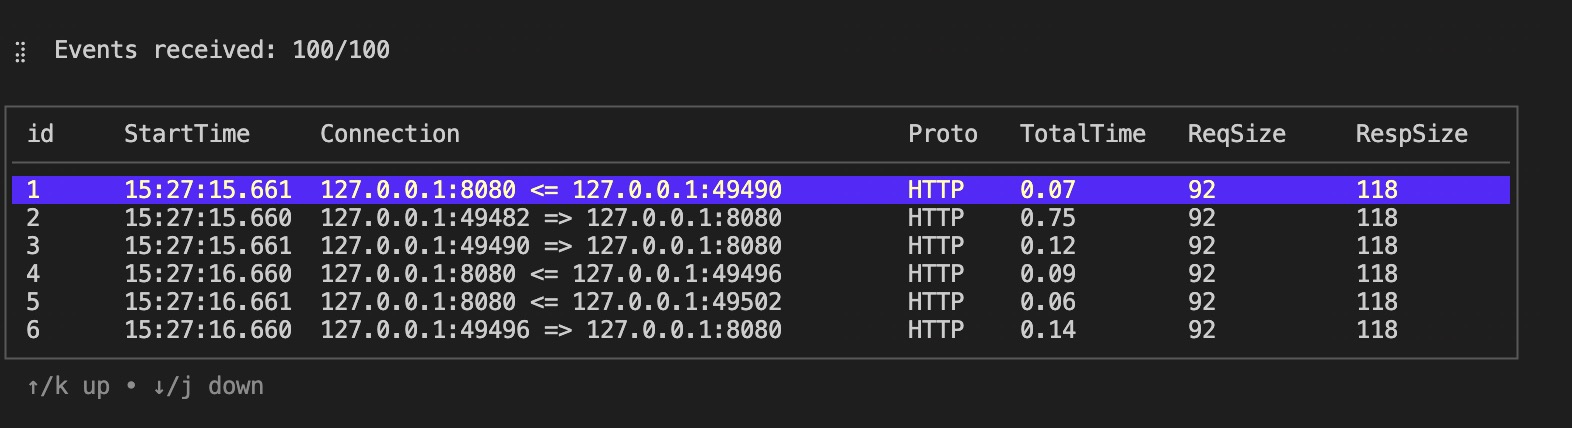 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 matheus-garbelini/esp32_bluetooth_classic_sniffer
Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)
 nccgroup/binproxy
BinProxy is a proxy for arbitrary TCP connections. You can define custom message formats using the BinData gem.
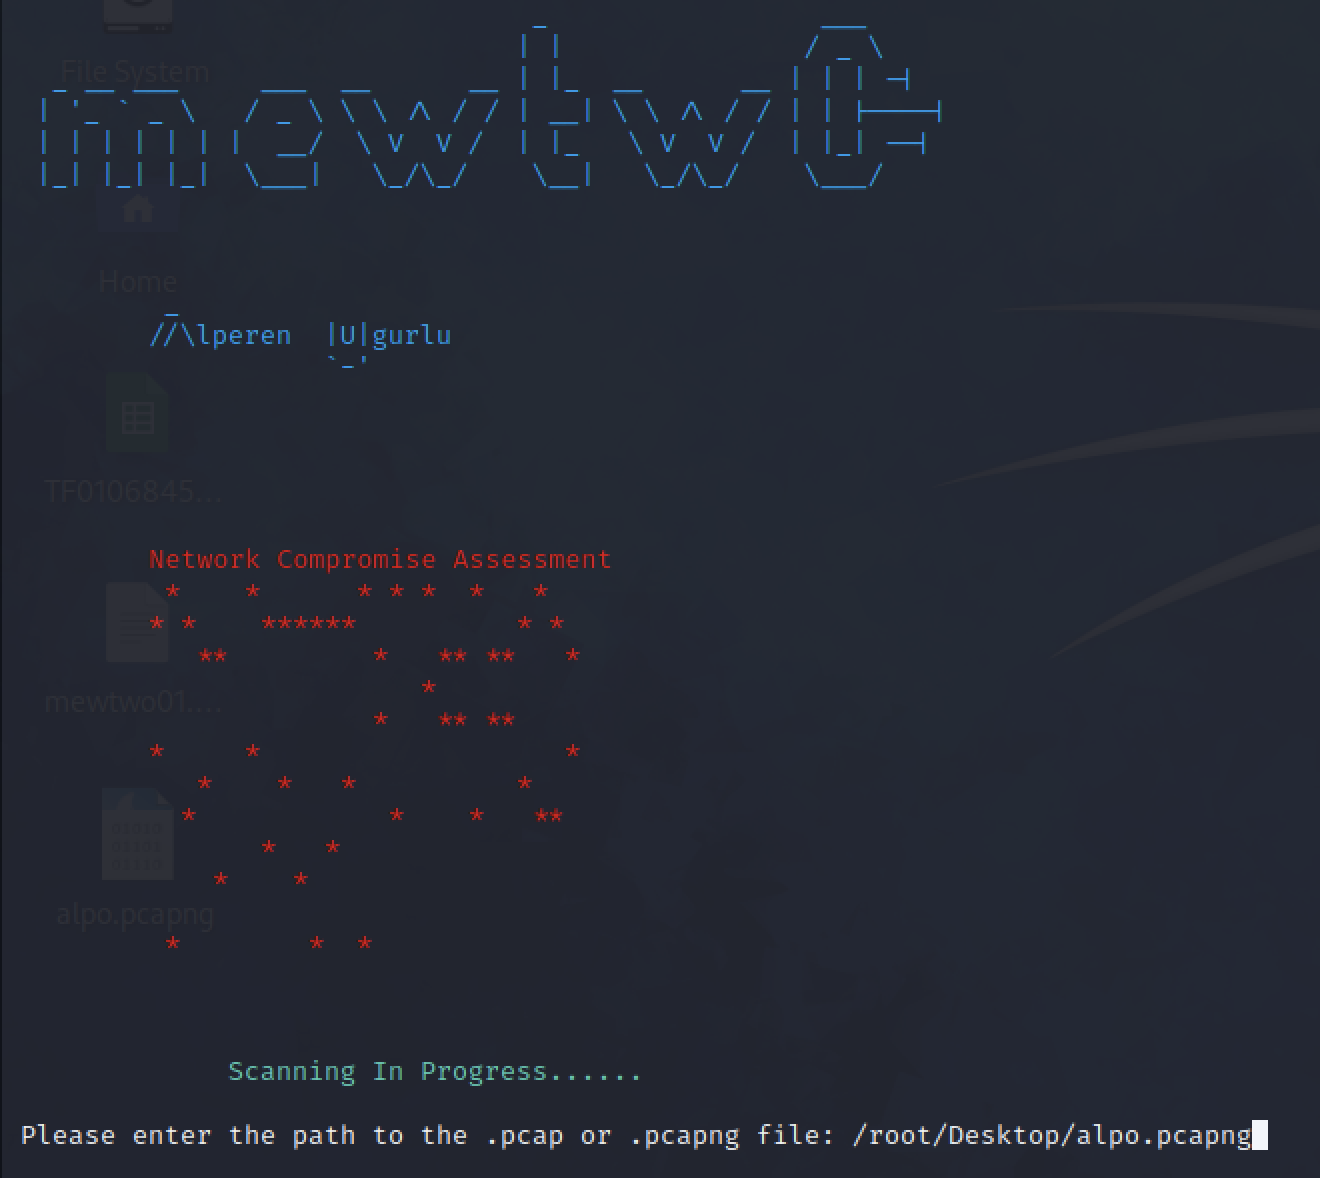 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…