

net-creds
 danmcinerney/net-creds
Sniffs sensitive data from interface or pcap
information-gatheringnetwork-securitypacket-sniffing-analysis+1
1.9k
danmcinerney/net-credsSniffs sensitive data from interface or pcap
 jalvarezz13/krb5roastparser
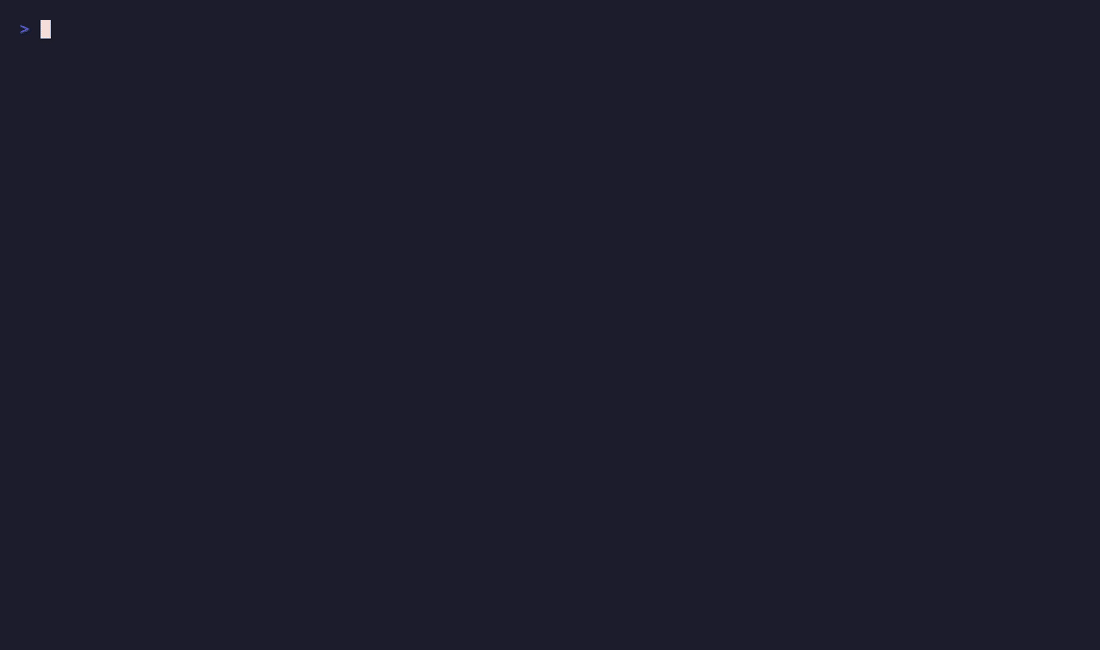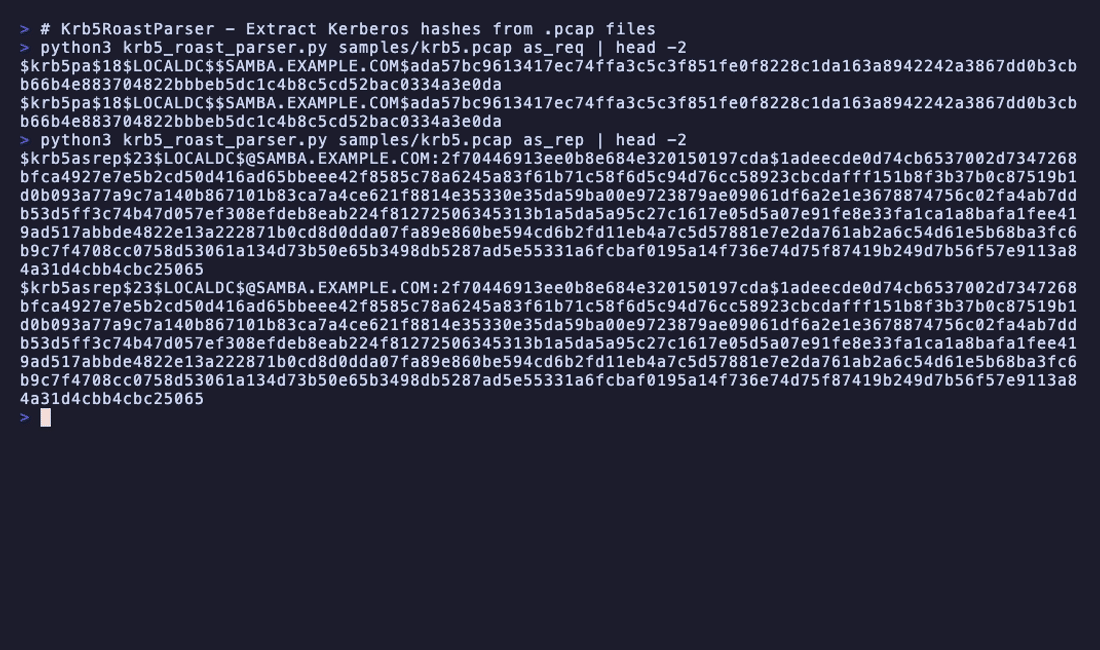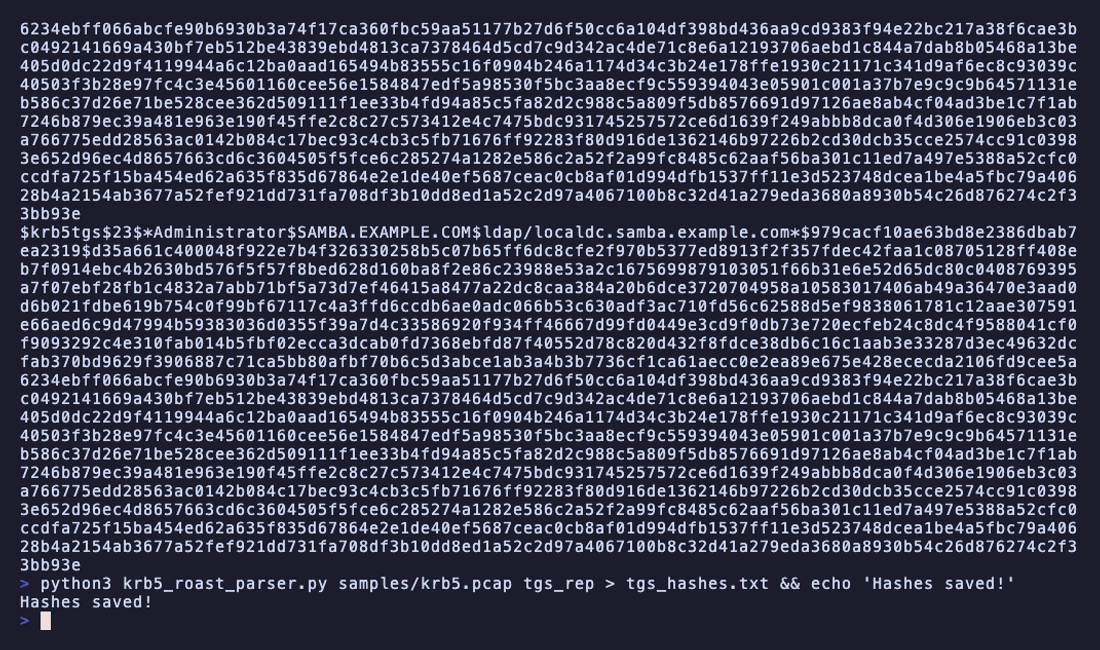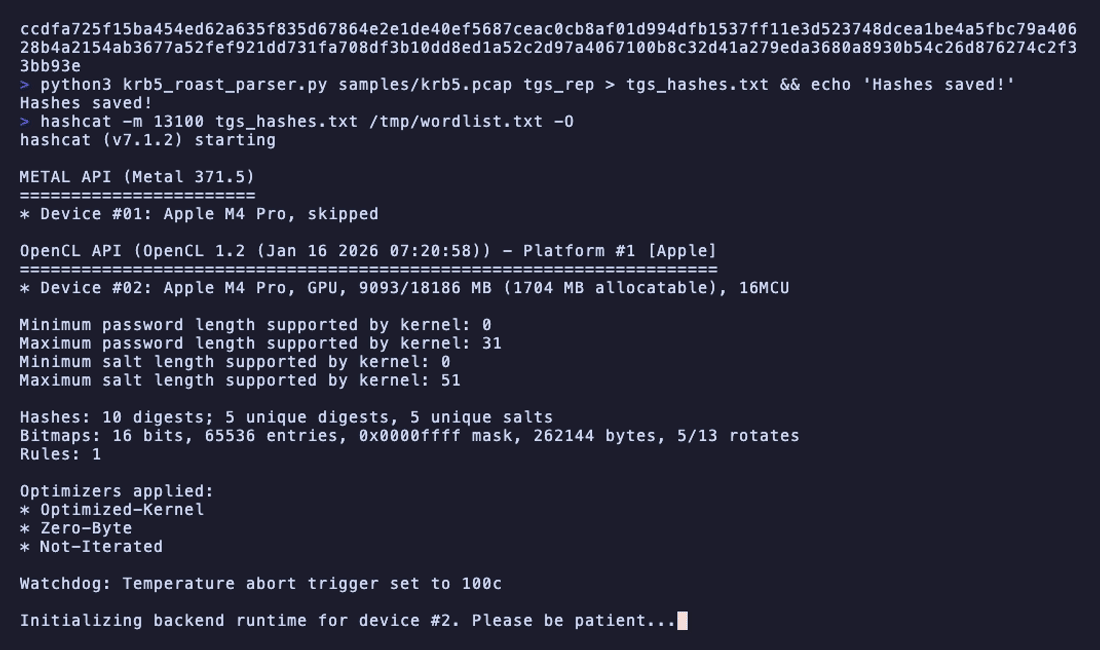
KrbRoastParser is a tool for parsing Kerberos packets from pcap files to extract AS-REQ, AS-REP and TGS-REP hashes
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 mlgualtieri/ntlmrawunhide
NTLMRawUnhide.py is a Python3 script designed to parse network packet capture files and extract NTLMv2 hashes in a crackable format. The following…
 lgandx/pcredz
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
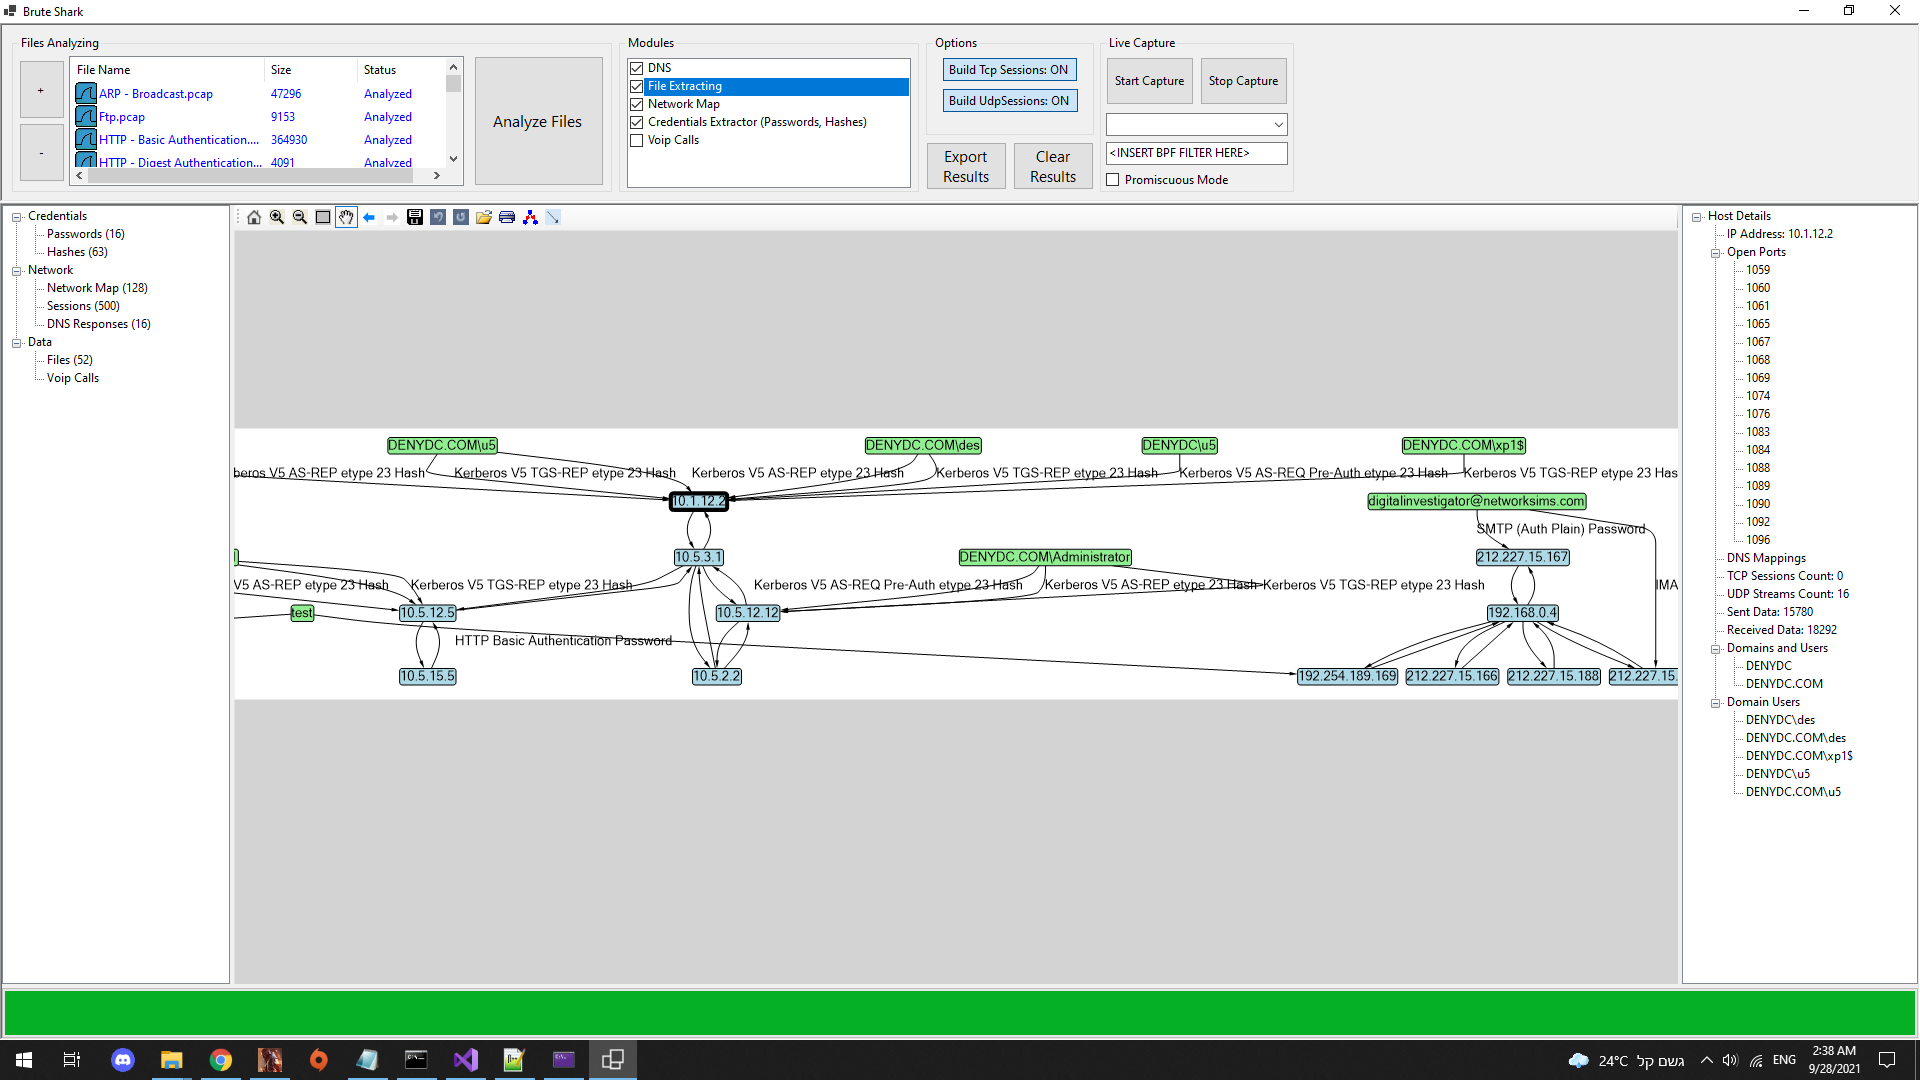
 x-c3ll/sharpntlmrawunhide
C# version of NTLMRawUnHide