

cve-2022-21907
 corelight/cve-2022-21907
Zeek package to detect CVE-2022-21907 HTTP exploit attempts by analyzing packet captures for malformed requests and triggering alerts.
exploitationintrusion-detectionnetwork-security+3
5
corelight/cve-2022-21907Zeek package to detect CVE-2022-21907 HTTP exploit attempts by analyzing packet captures for malformed requests and triggering alerts.
 abiral-timalsina/cyber-defenders-lab-
My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
 salgio/esptouchcatcher
eWeLinkESPT is a tool that automatically decodes and decrypts the WiFi network credentials transmitted to a supported ESP-based IoT device by the…
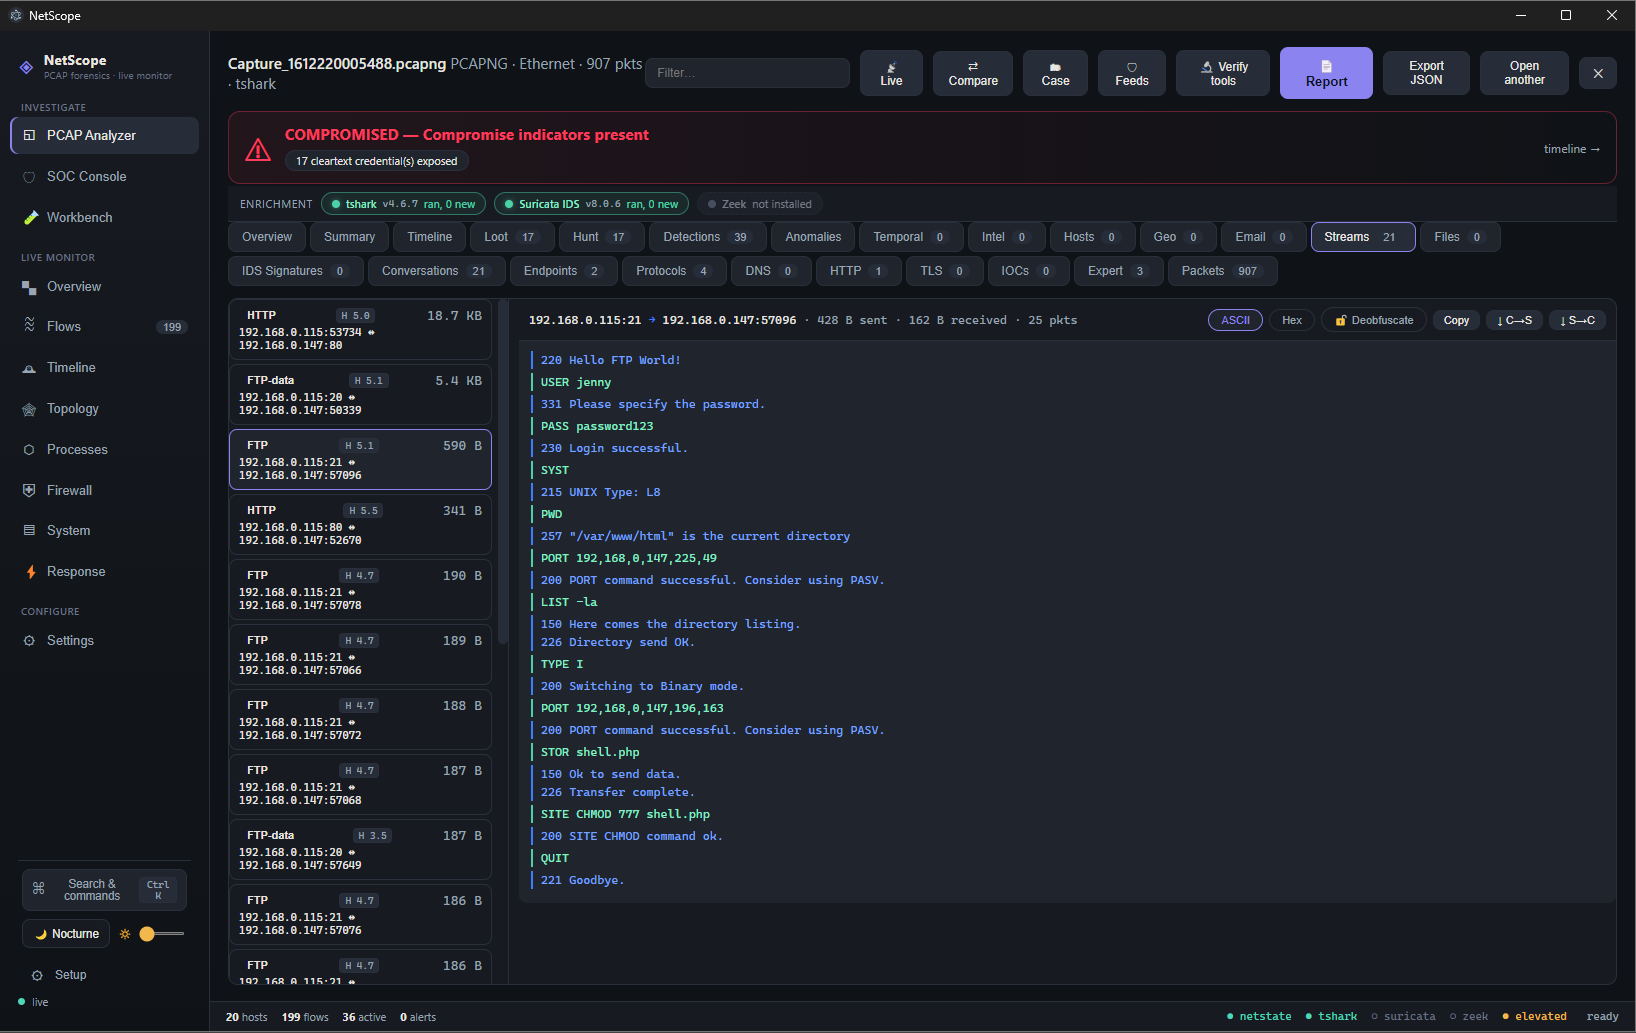 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 trg-1999/detectpacket-cve-2017-8464
Exploit vulnerabilities and vulnerability prevention implementation
 marb08/etherleak-checker
This Python script helps to detect the Etherleak (CVE-2003-0001) vulnerability on a target host by analyzing the padding data in network packets. The…
 zwclose/cve-2021-26258
Files and tools for CVE-2021-26258
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
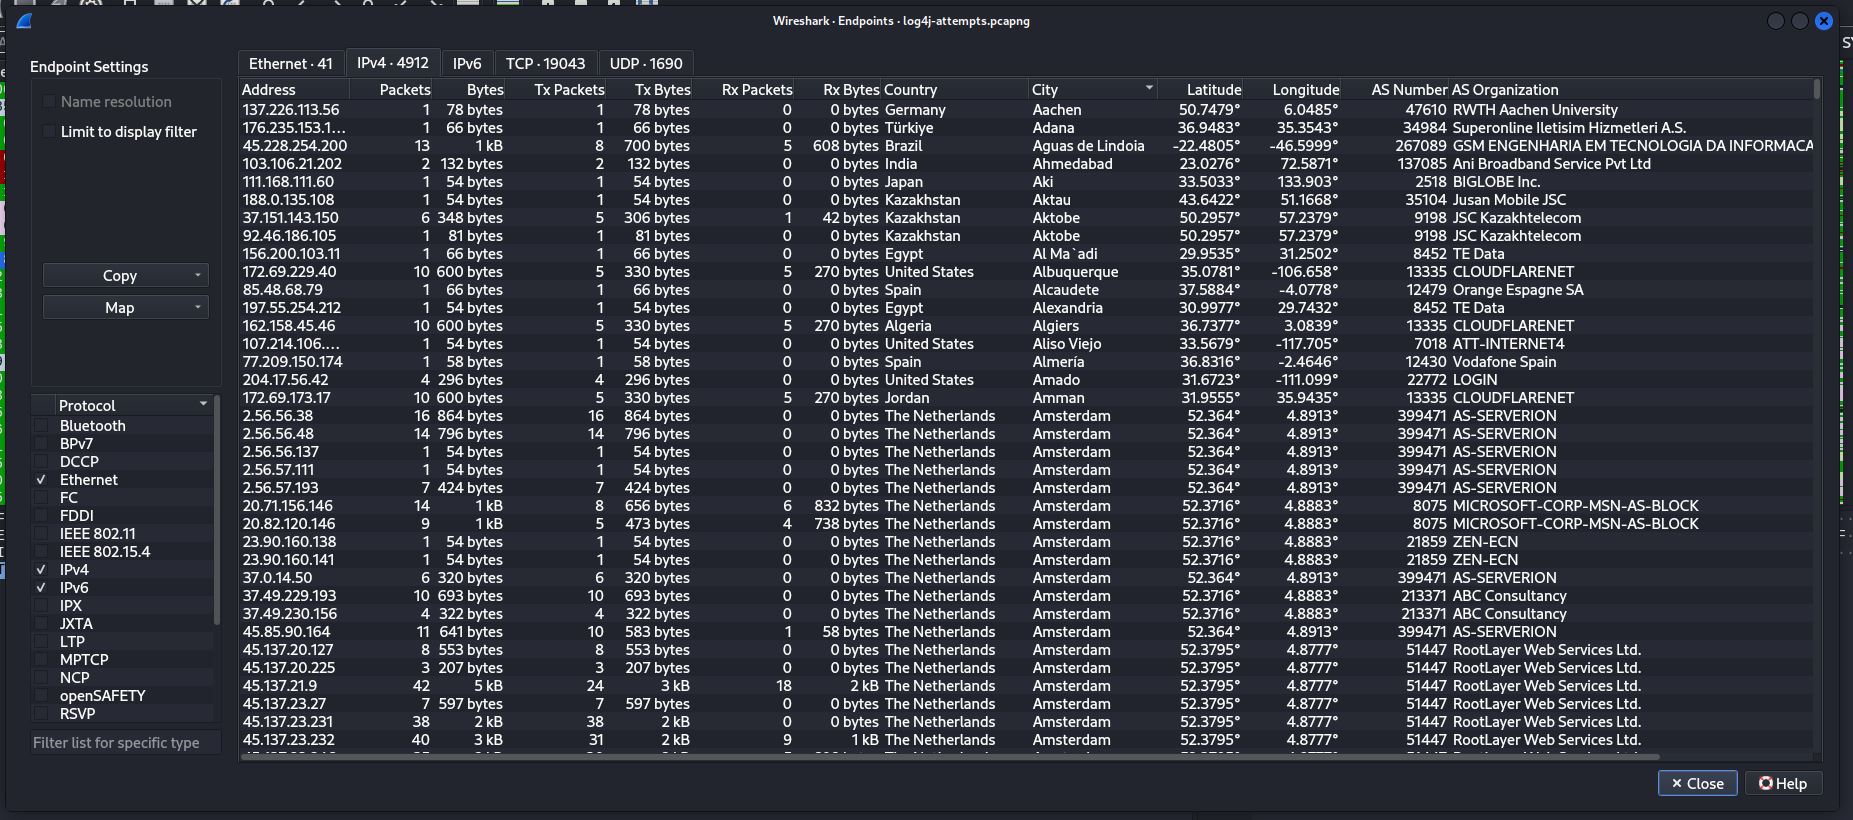 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 aelshimony-cloud/openwire-cve-2023-46604-investigation
Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
 yili-soc/vm-homelab-log4shell-assessment
Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…
 corelight/zeek-mercury-npf
Zeek plugin generating Mercury NPF fingerprints for TCP, TLS/DTLS, QUIC, HTTP, SSH, OpenVPN, and STUN to support network security monitoring.
 nicholasc03/dns-poisoning-triage-lab
Forensic triage of DNS cache poisoning in legacy hardware. Includes PCAP analysis of 839-byte unsolicited record injections, CVE-2025-40778 mapping,…
 jlinebau/cve-2025-55315-scanner-monitor
Quick and Simple Scripts to Scan for Vulnerable Servers and Packet Level Monitors
 jenderal92/ddos-traffic-monitor
A real-time traffic monitoring tool that detects and displays network traffic volume per IP address to identify potential DDoS attacks.
 emilebarnard242/pentest-metasploitable2
Structured penetration testing lab documenting a full attack chain from network reconnaissance to root exploitation of vsftpd 2.3.4 backdoor, with…
 s_r_e_e_r_a_j/netraptor
NetRaptor is a GUI-based ARP poisoning tool built with Python that allows you to scan a network, select a target and gateway, and perform a…