
CVE-2020-16899
 advanced-threat-research/cve-2020-16899
CVE-2020-16899 - Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
dns-analysisids-ips-evasionintrusion-detection+3
20
advanced-threat-research/cve-2020-16899CVE-2020-16899 - Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
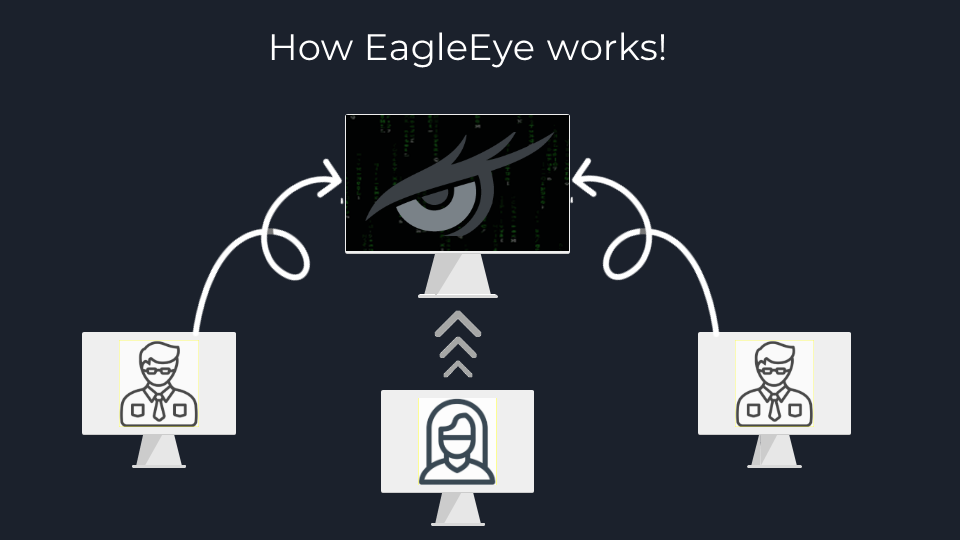 d4vinci/eagleeye
A host-based IDS and network monitoring system (My graduation project)
 yojiwatanabe/networkalarm
A tool to monitor local network traffic for possible security vulnerabilities. Warns user against possible nmap scans, Nikto scans, credentials sent…
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 sud0woodo/urgent11-suricata-lua-scripts
Suricata LUA scripts to detect CVE-2019-12255, CVE-2019-12256, CVE-2019-12258, and CVE-2019-12260
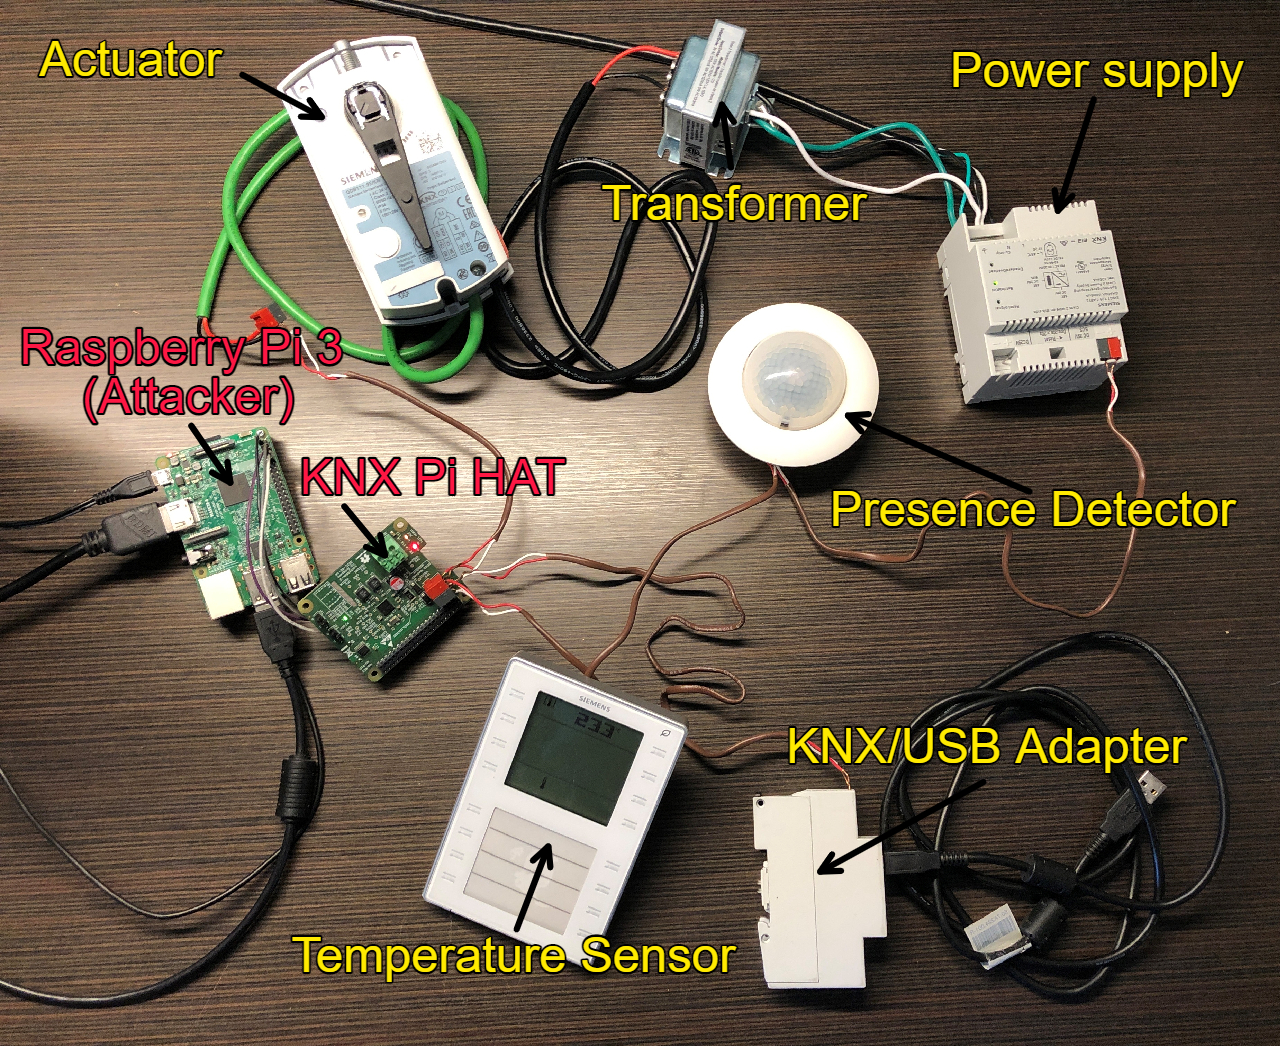 chrism09/knx-bus-dump
A tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…
 libratbag/ratbag-toolbox
Random reverse engineering knowledge and tools
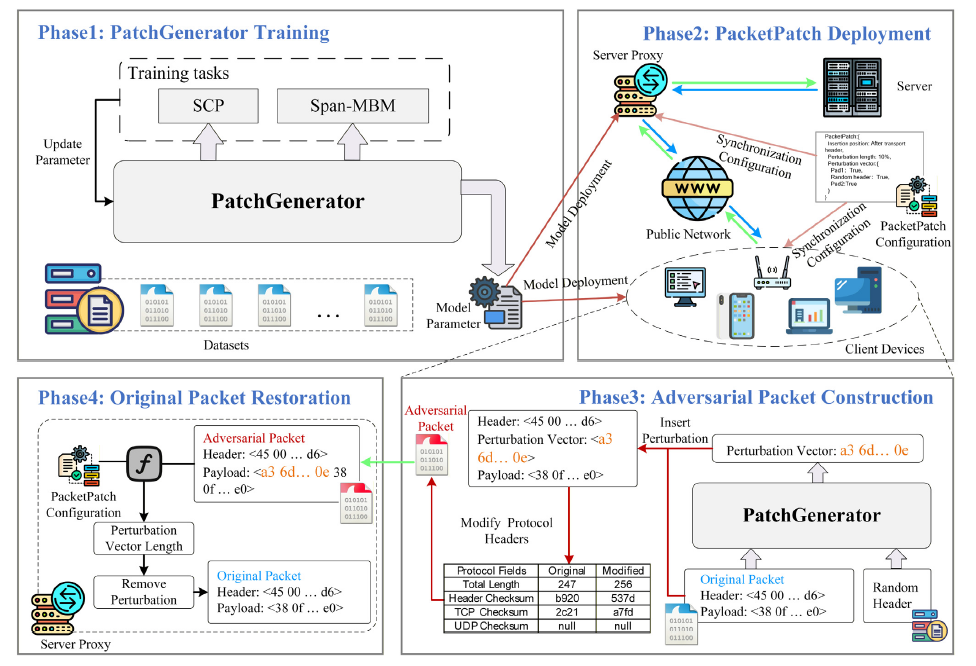 xuyw-seu/packetpatch
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.
 mercuryworkshop/woeful
Woeful is a tool that lets web apps to safely and securely connect to the outside internet without a complex backend.
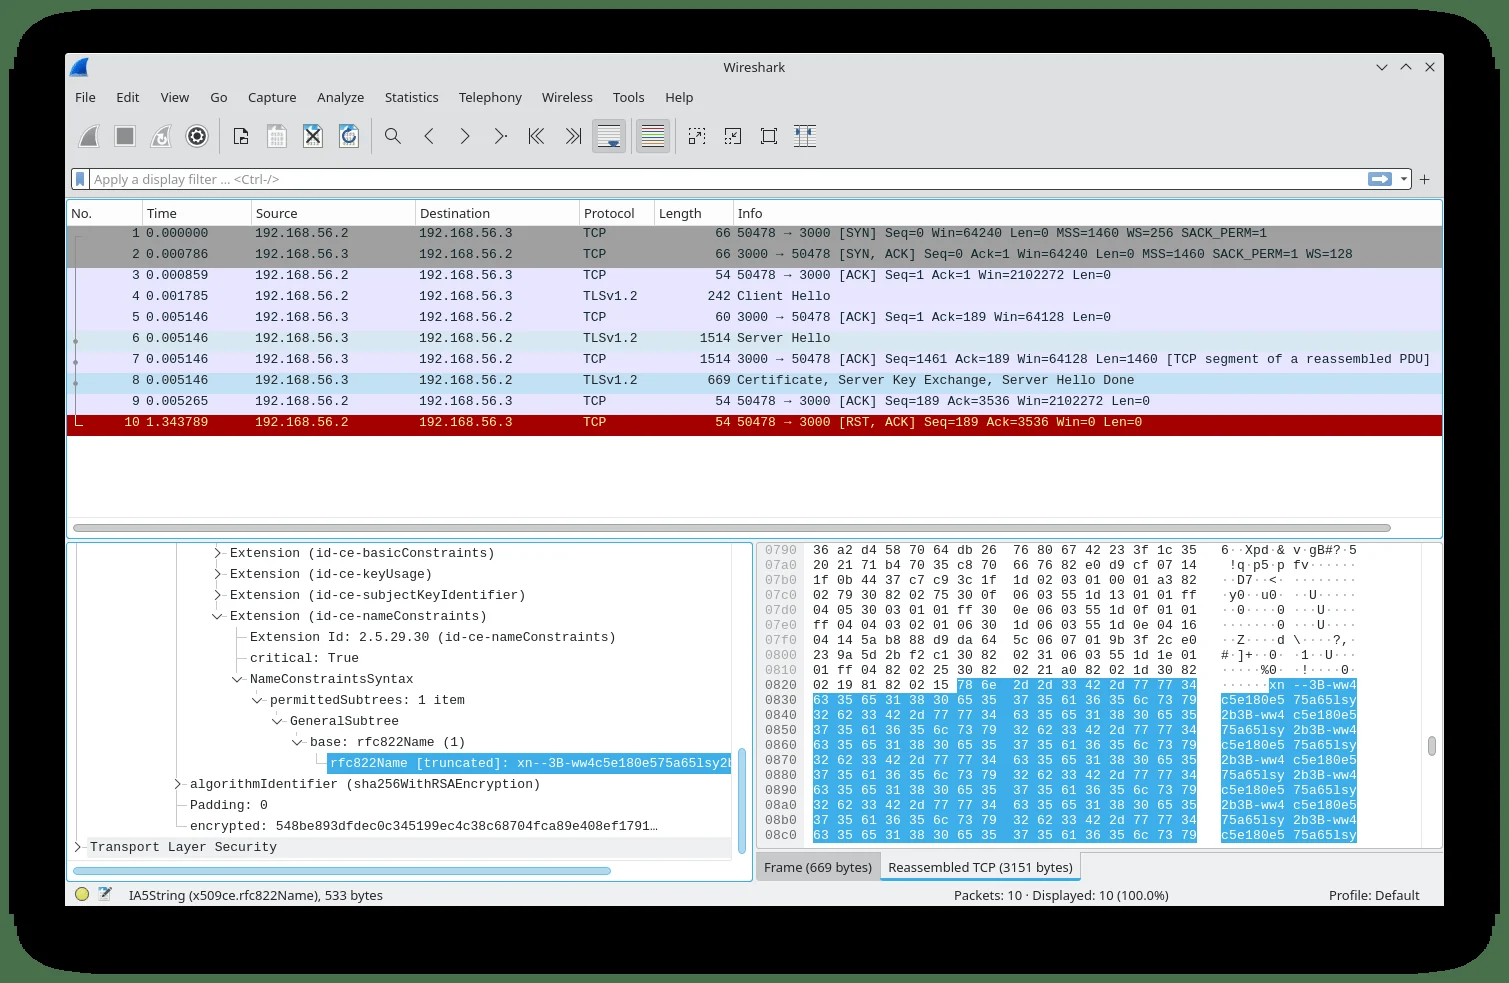 fox-it/spookyssl-pcaps
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…
 dougives/wisp
Script and hardware kit to automatically deauth 802.11 clients en masse. Captures packets for later nefariousness.
 jean-nestor/evil-twin-ap
Automated evil twin access point toolkit with traffic capture and real-time monitoring for wireless penetration testing and security research.
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…
 vaelwolf/cve-2022-1388
-- FOR EDUCATIONAL USE ONLY -- Proof-of-Concept RCE for CVE-2022-1388, plus some added functionality for blue and red teams
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 interceptsuite/interceptsuite
MITM proxy for TCP/TLS/DTLS/UDP traffic, with STARTTLS, IoT, Thick Client and more.