
cve-2018-4407
 unixpickle/cve-2018-4407
Crash macOS and iOS devices with one packet
exploitationios-securitynetwork-security+2
46
unixpickle/cve-2018-4407Crash macOS and iOS devices with one packet
 mlgualtieri/ntlmrawunhide
NTLMRawUnhide.py is a Python3 script designed to parse network packet capture files and extract NTLMv2 hashes in a crackable format. The following…
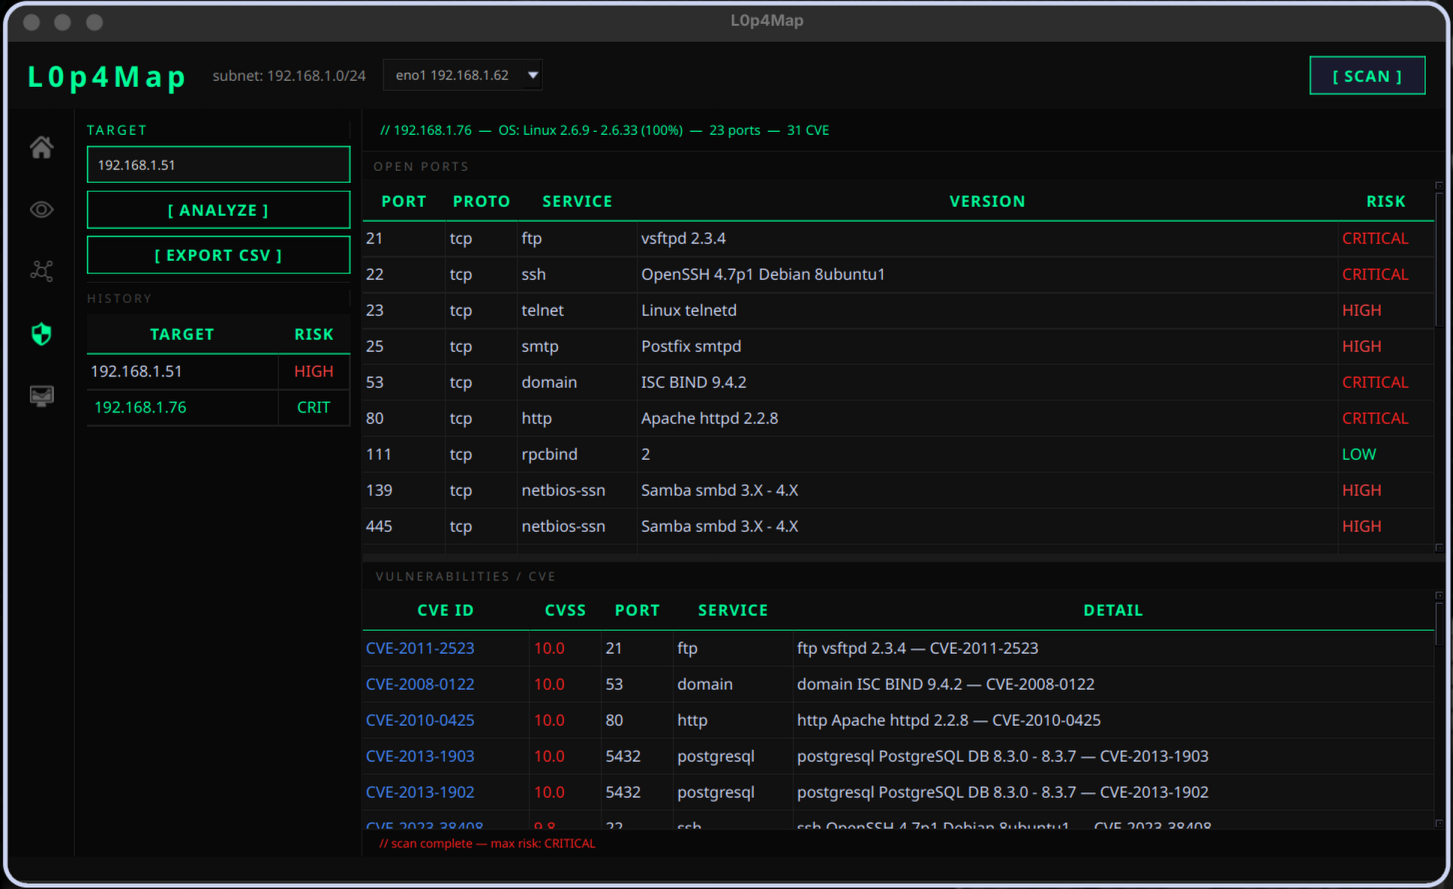 haxl0p4/l0p4map
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…
 r00t-3xp10it/morpheus
Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)
 withsecurelabs/doublepulsar-c2-traffic-decryptor
A python2 script for processing a PCAP file to decrypt C2 traffic sent to DOUBLEPULSAR implant
 danmcinerney/wifi-monitor
Prints the IPs on your local network that're sending the most packets
 zapotek/cdpsnarf
CDPSnarf is a network sniffer exclusively written to extract information from CDP (Cisco Discovery Protocol) packets.
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 danmcinerney/creds.py
Harvest FTP/POP/IMAP/HTTP/IRC creds
 lixiang957/cve-2021-33959
Proof-of-concept exploit for CVE-2021-33959 demonstrating UDP reflection amplification attack against Plex Media Server via crafted M-SEARCH packets…
 ptswarm/reflutter
Flutter Reverse Engineering Framework
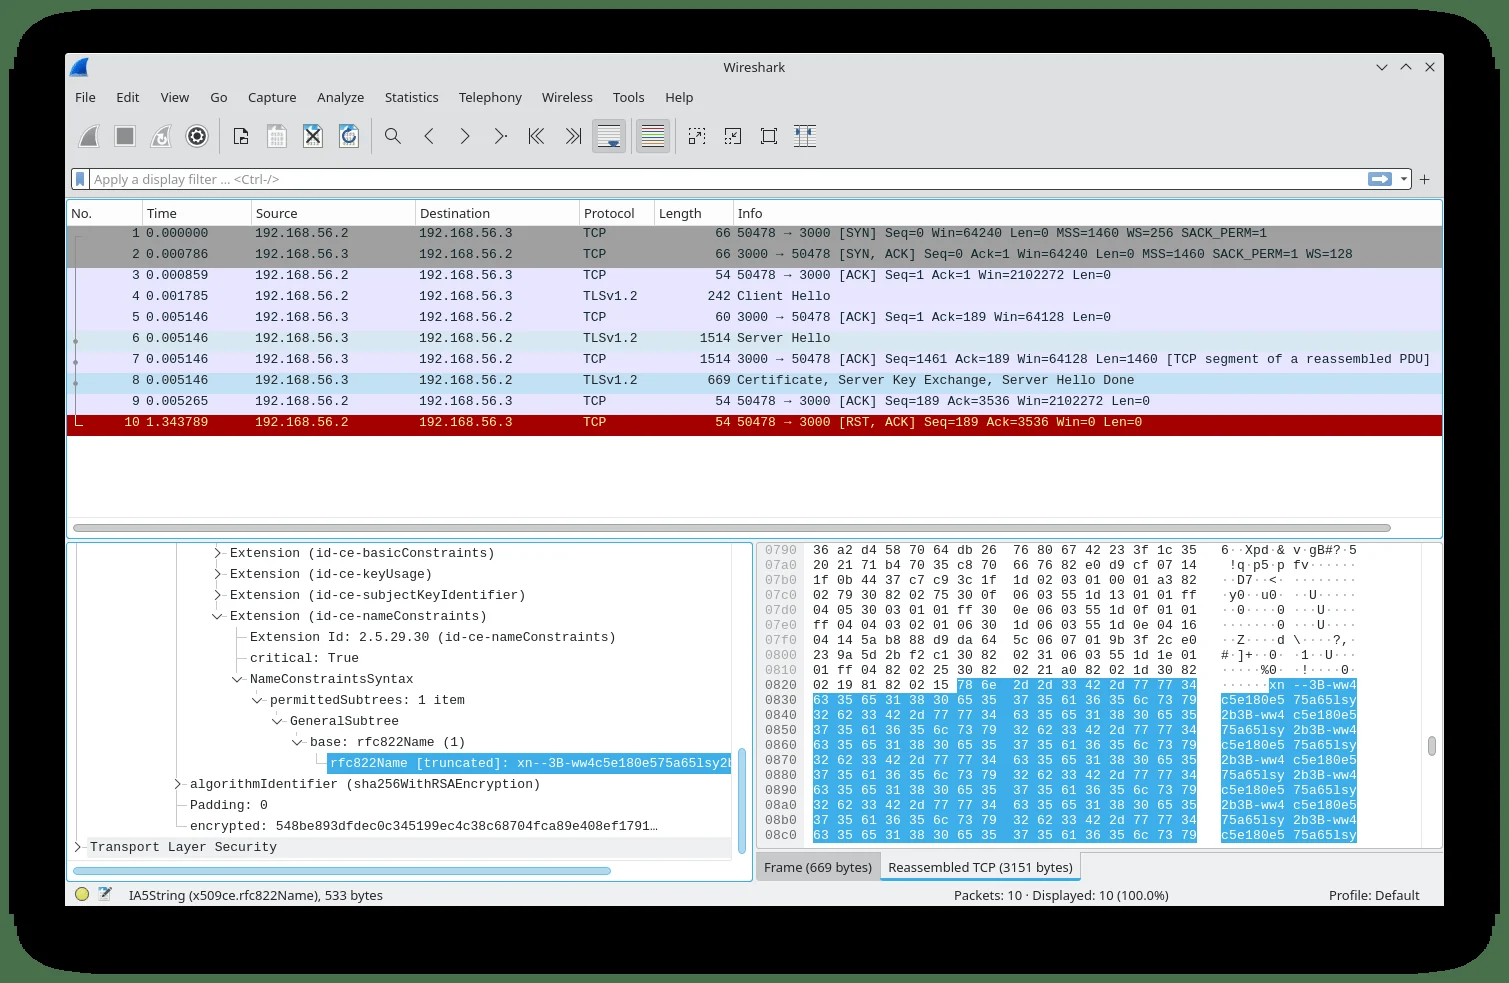 fox-it/spookyssl-pcaps
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…
 alperenugurlu/cve-2024-3596-detector
Detects CVE-2024-3596 in RADIUS/UDP traffic by analyzing MD5 collisions in Access-Request packets, helping administrators identify vulnerable…
 prprhyt/poc_tls1_3_cve-2020-13777
Proof-of-concept for CVE-2020-13777 (GnuTLS TLS 1.3 reconnect vulnerability). Parses pcap files to demonstrate the flaw for educational and technical…
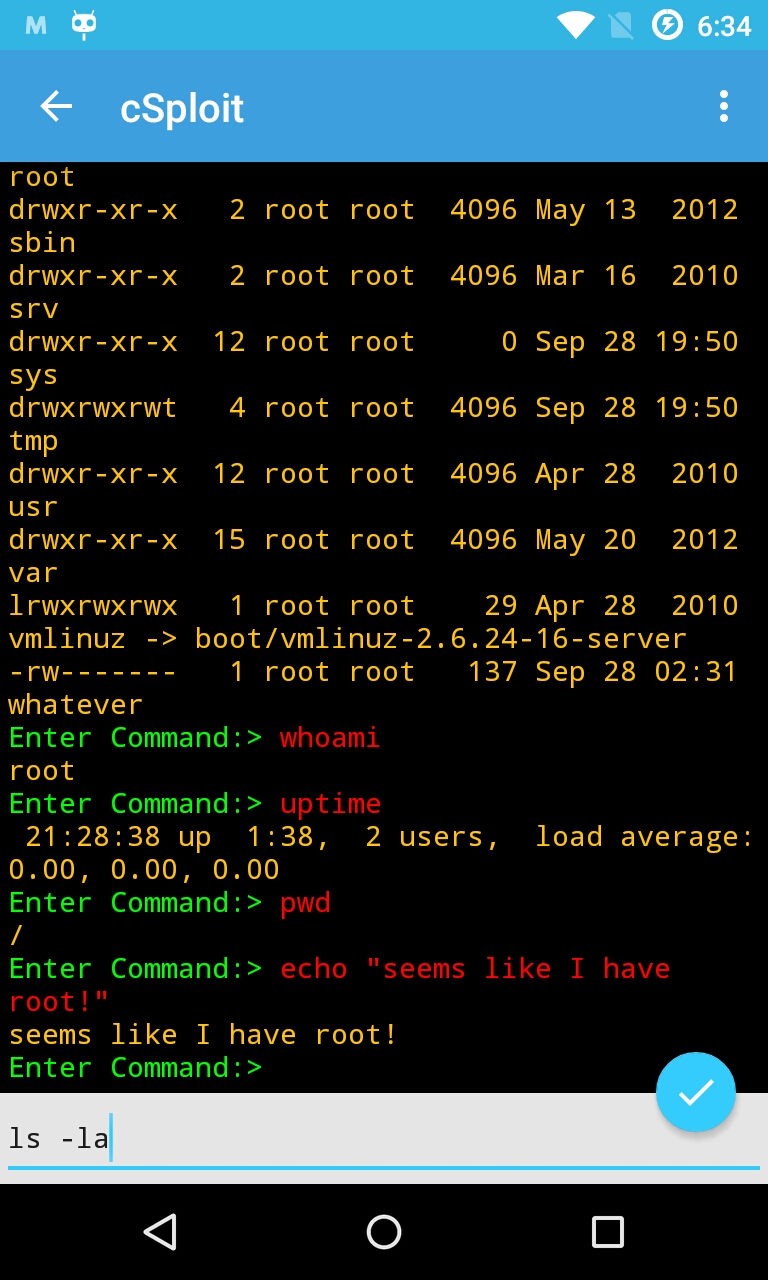 csploit/android
cSploit - The most complete and advanced IT security professional toolkit on Android.
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.