

skydive
 skydive-project/skydive
An open source real-time network topology and protocols analyzer
cloud-infrastructure-securitycontainer-securitynetwork-mapping+1
2.8k
skydive-project/skydiveAn open source real-time network topology and protocols analyzer
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
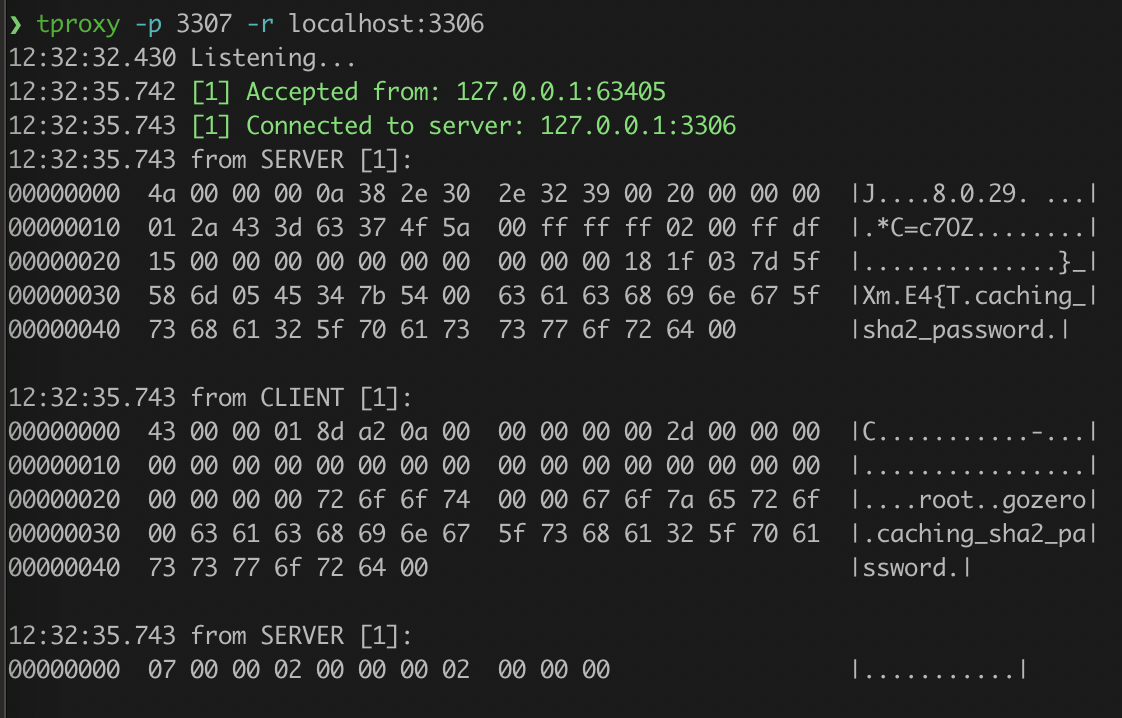 kevwan/tproxy
A cli tool to proxy and analyze TCP connections.
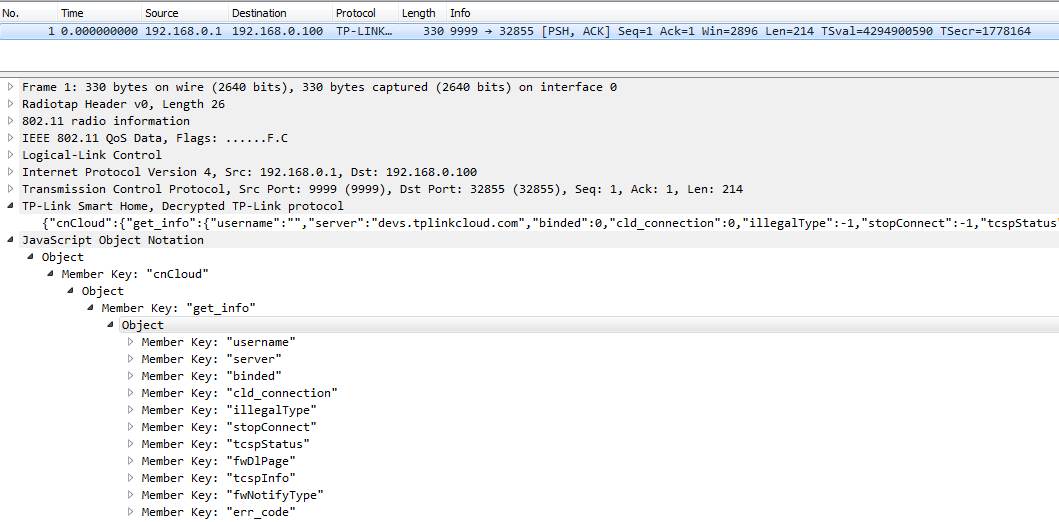 softscheck/tplink-smartplug
TP-Link WiFi SmartPlug Client and Wireshark Dissector
 droe/sslsplit
Transparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…
 samyk/keysweeper
KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…
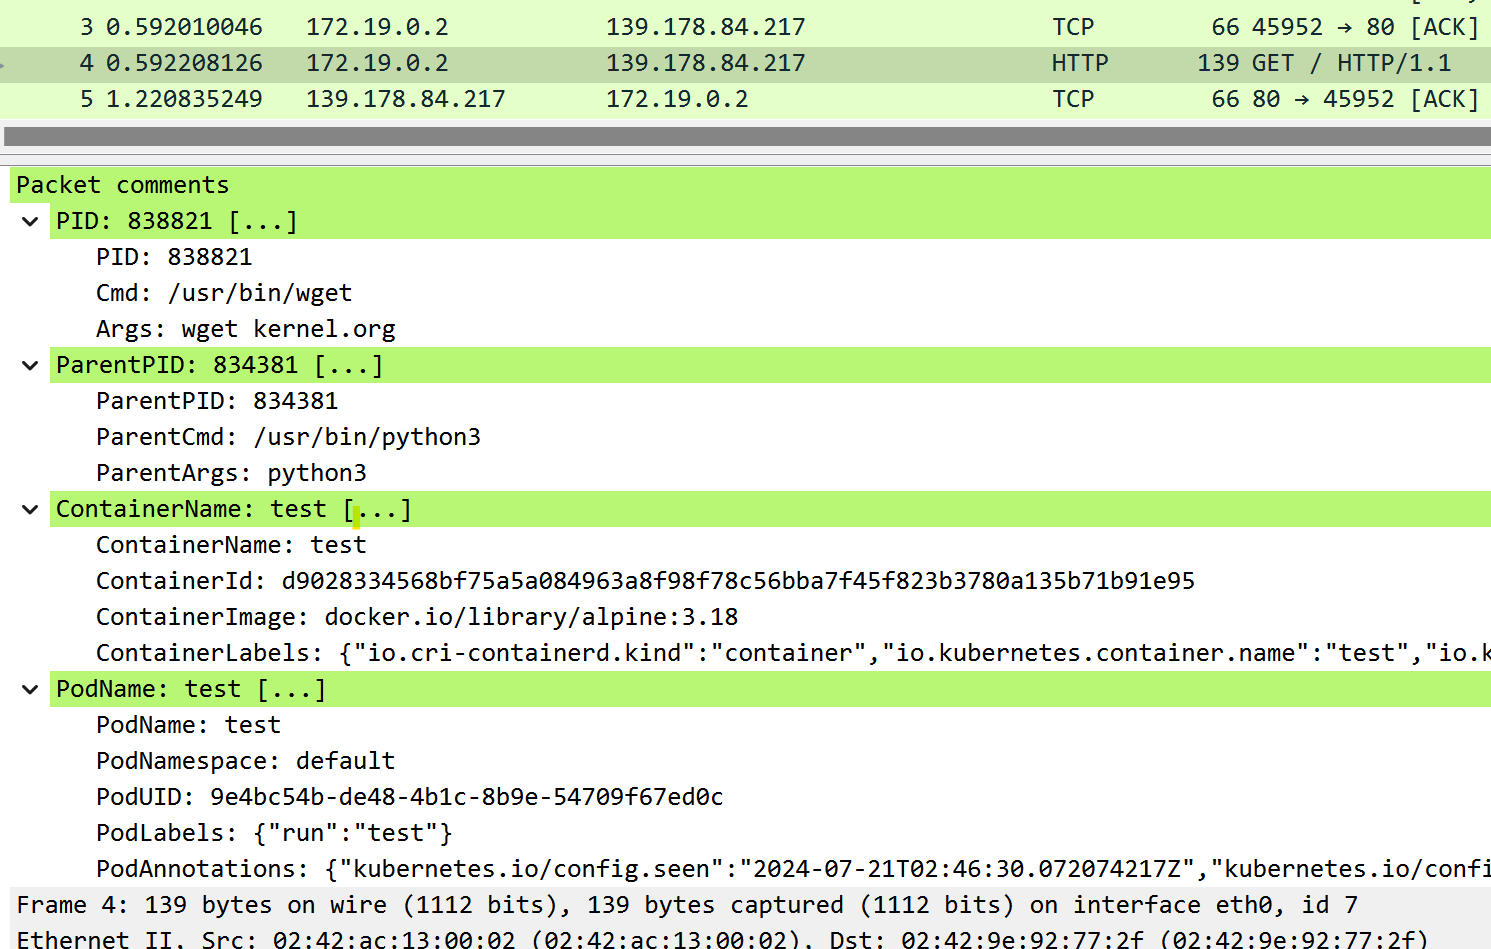 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
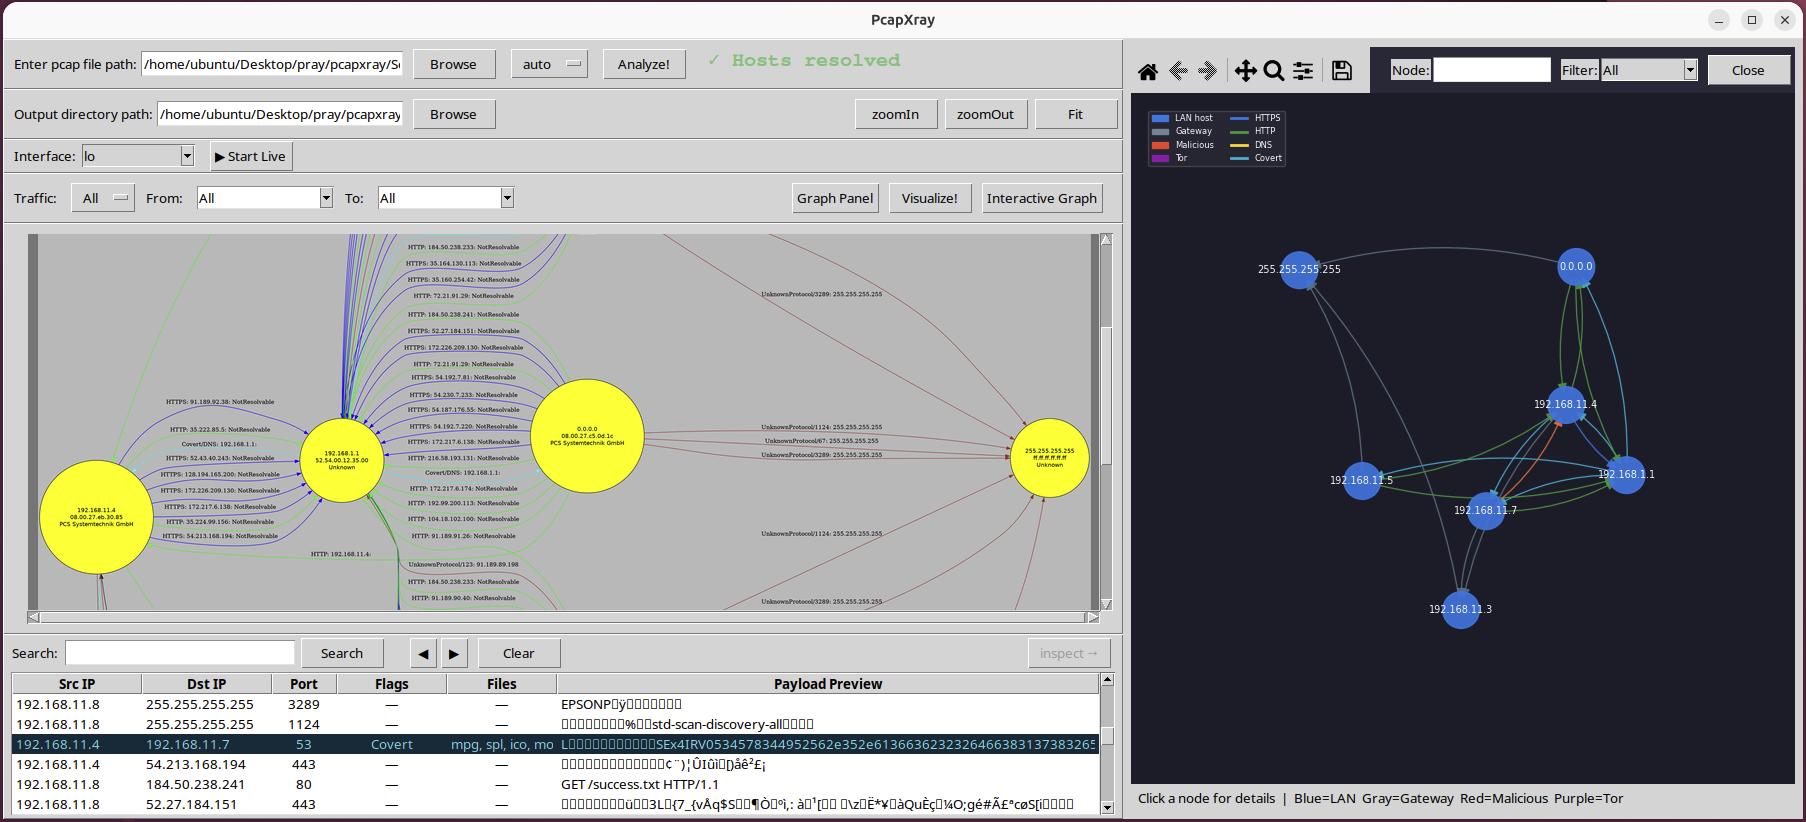 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
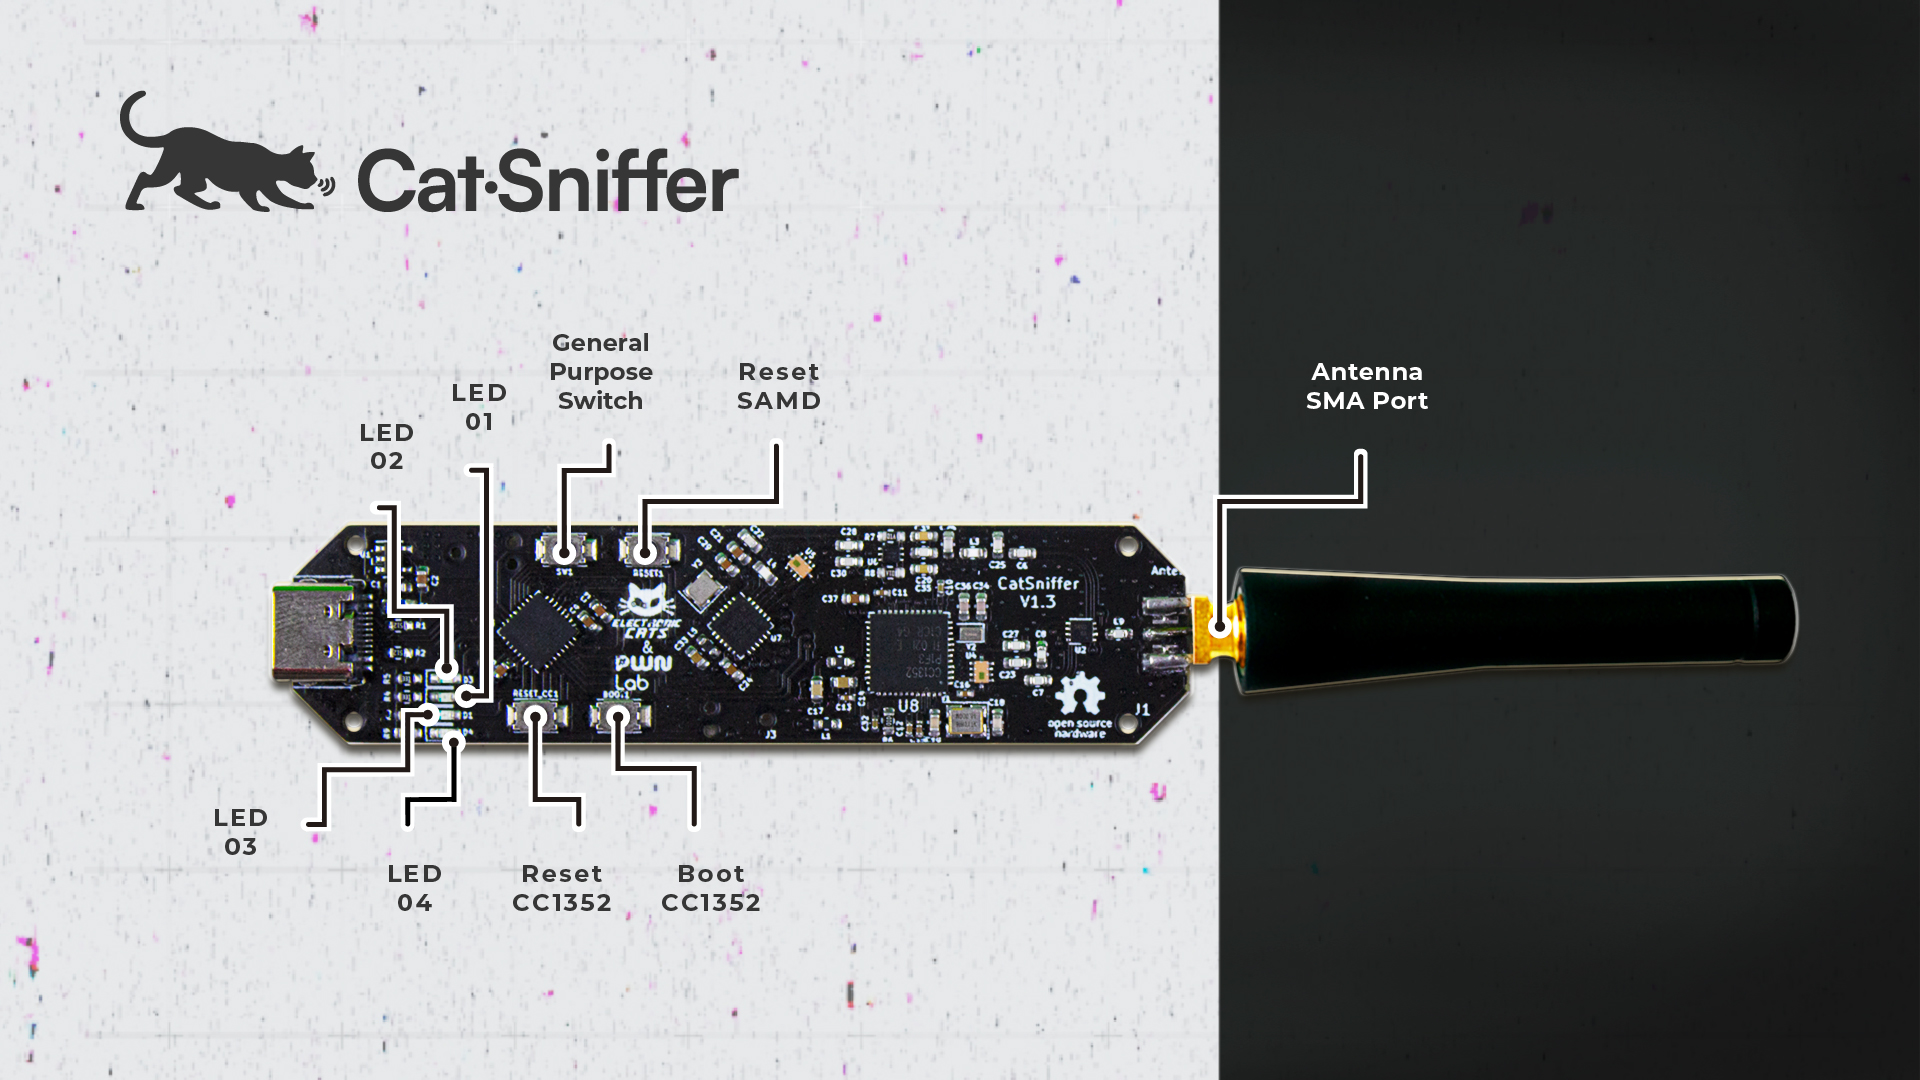 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 thehackingsage/hackdroid
Curated catalog of 364 Android pentesting and security APKs organized by category, covering forensics, MITM, sniffing, OSINT, wireless, and privacy…
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 frostbits-security/mitm-cheatsheet
Cheatsheet cataloging man-in-the-middle attacks across L2-L4 and wireless layers, with attack tools, detection methods, and mitigation techniques for…
 qmonnet/rbpf
Rust virtual machine and JIT compiler for eBPF programs
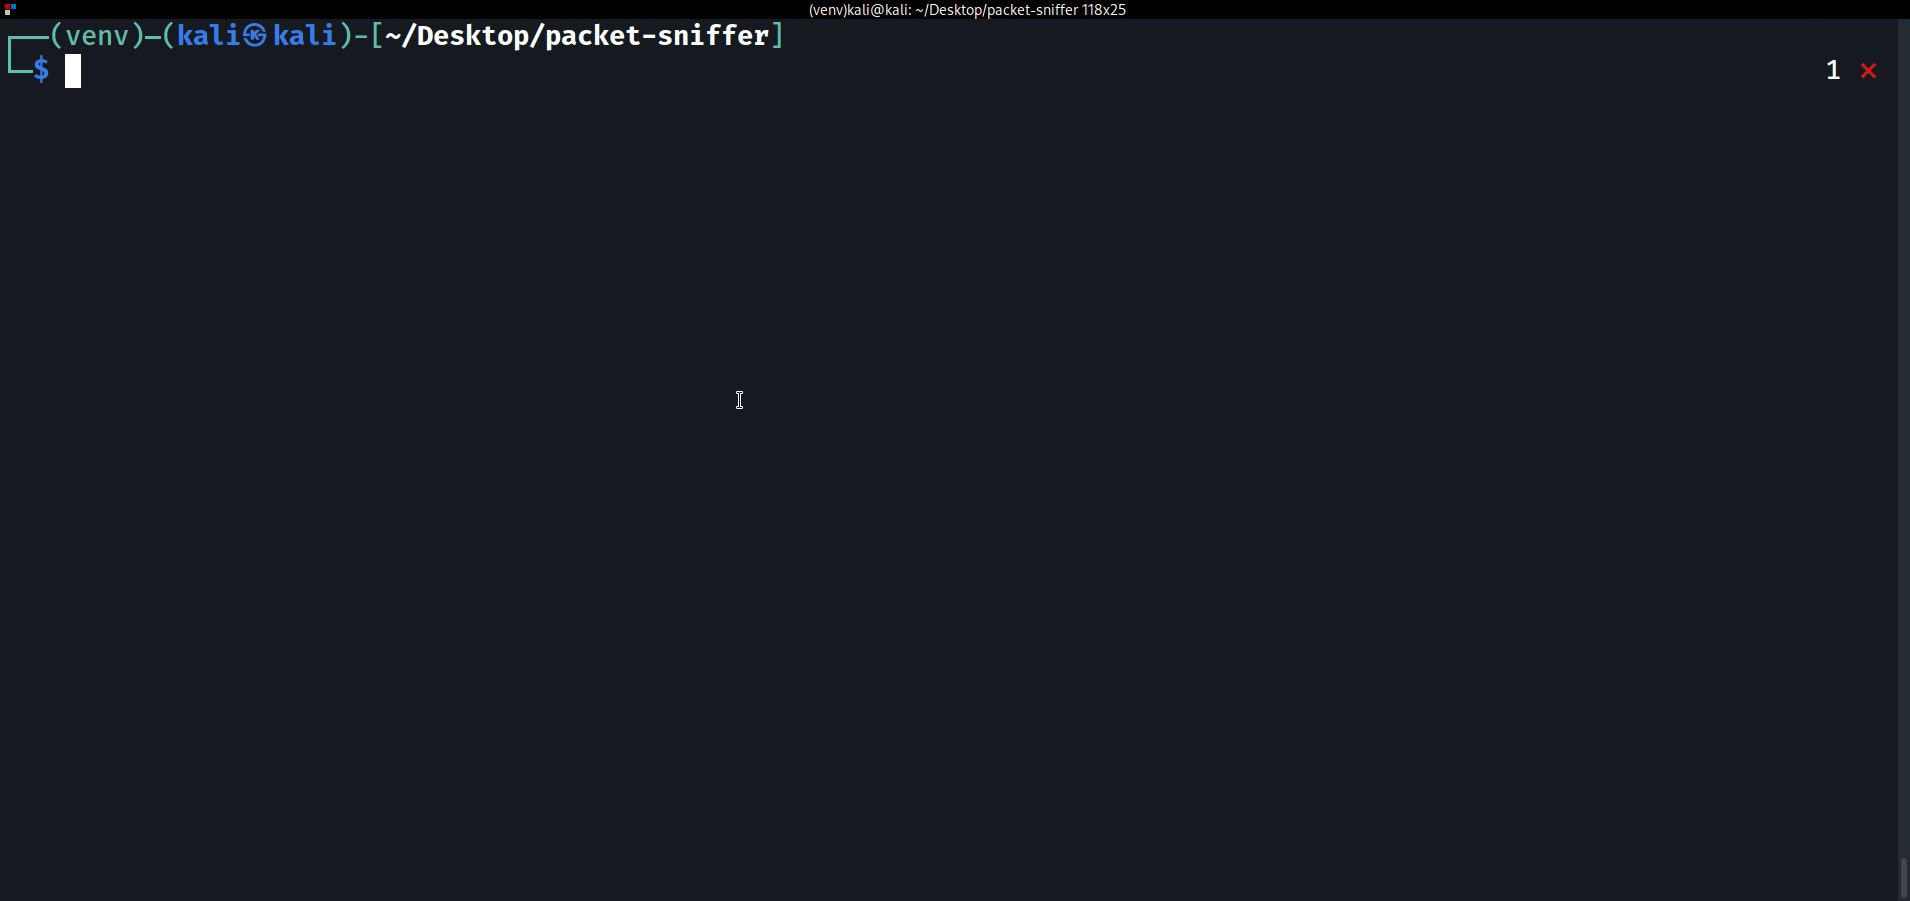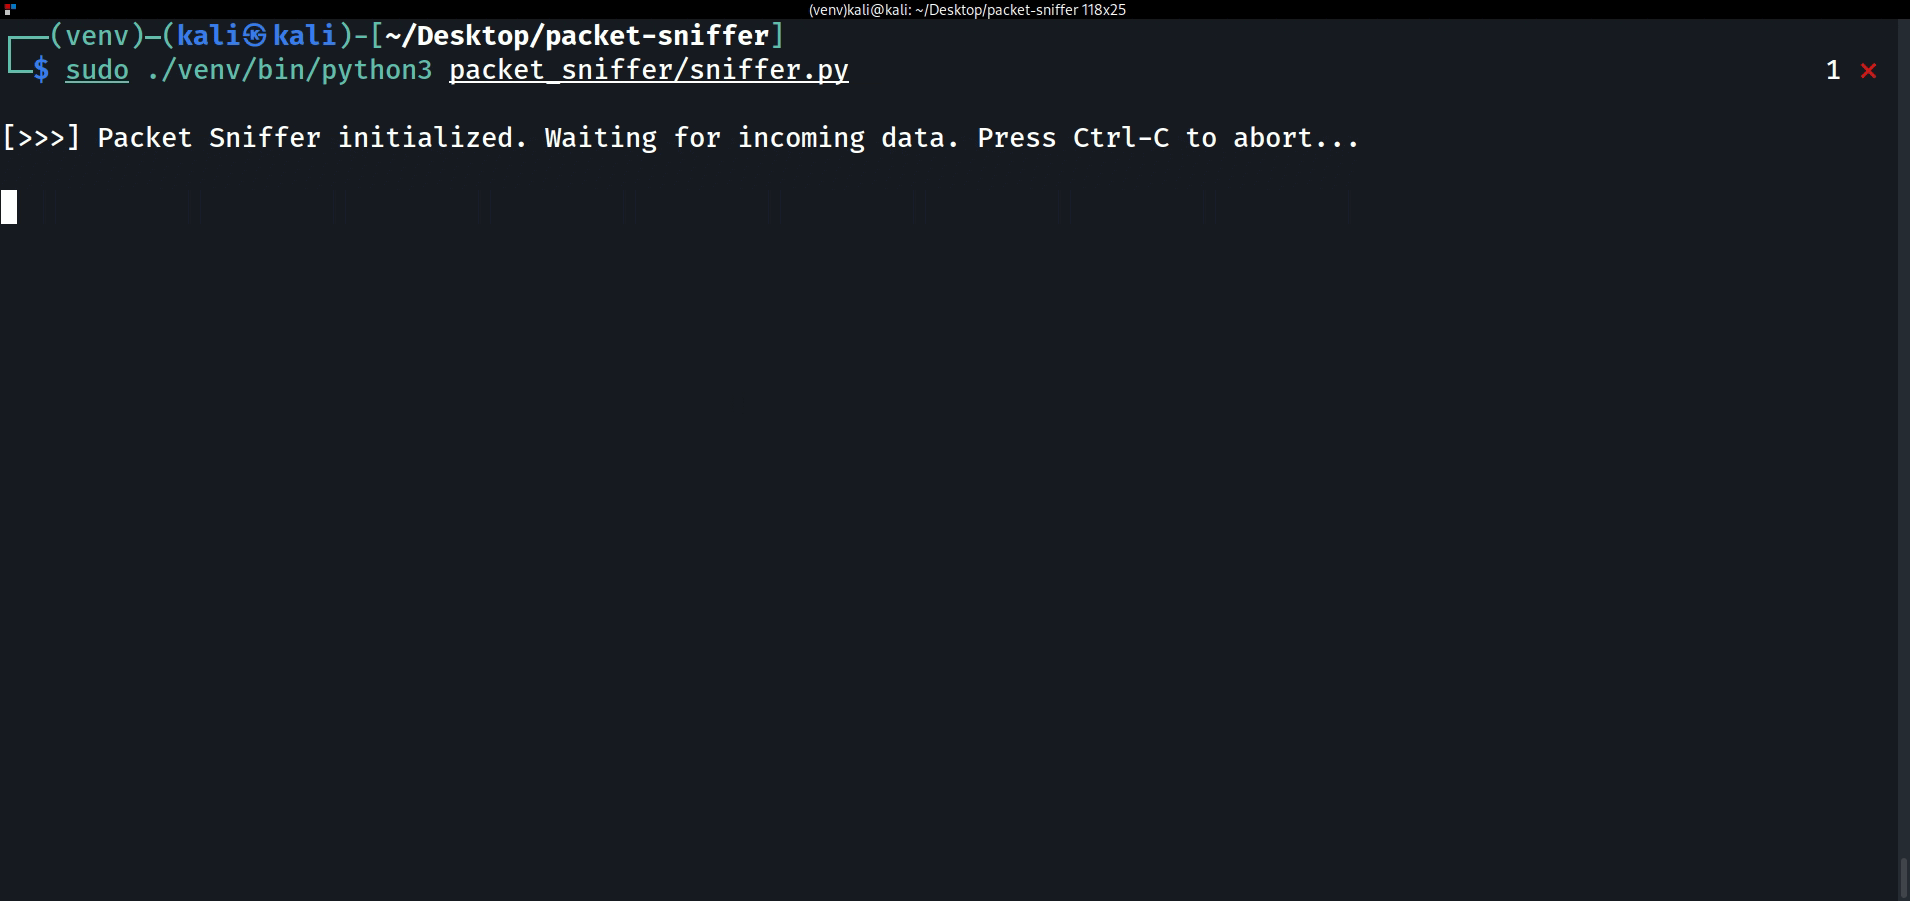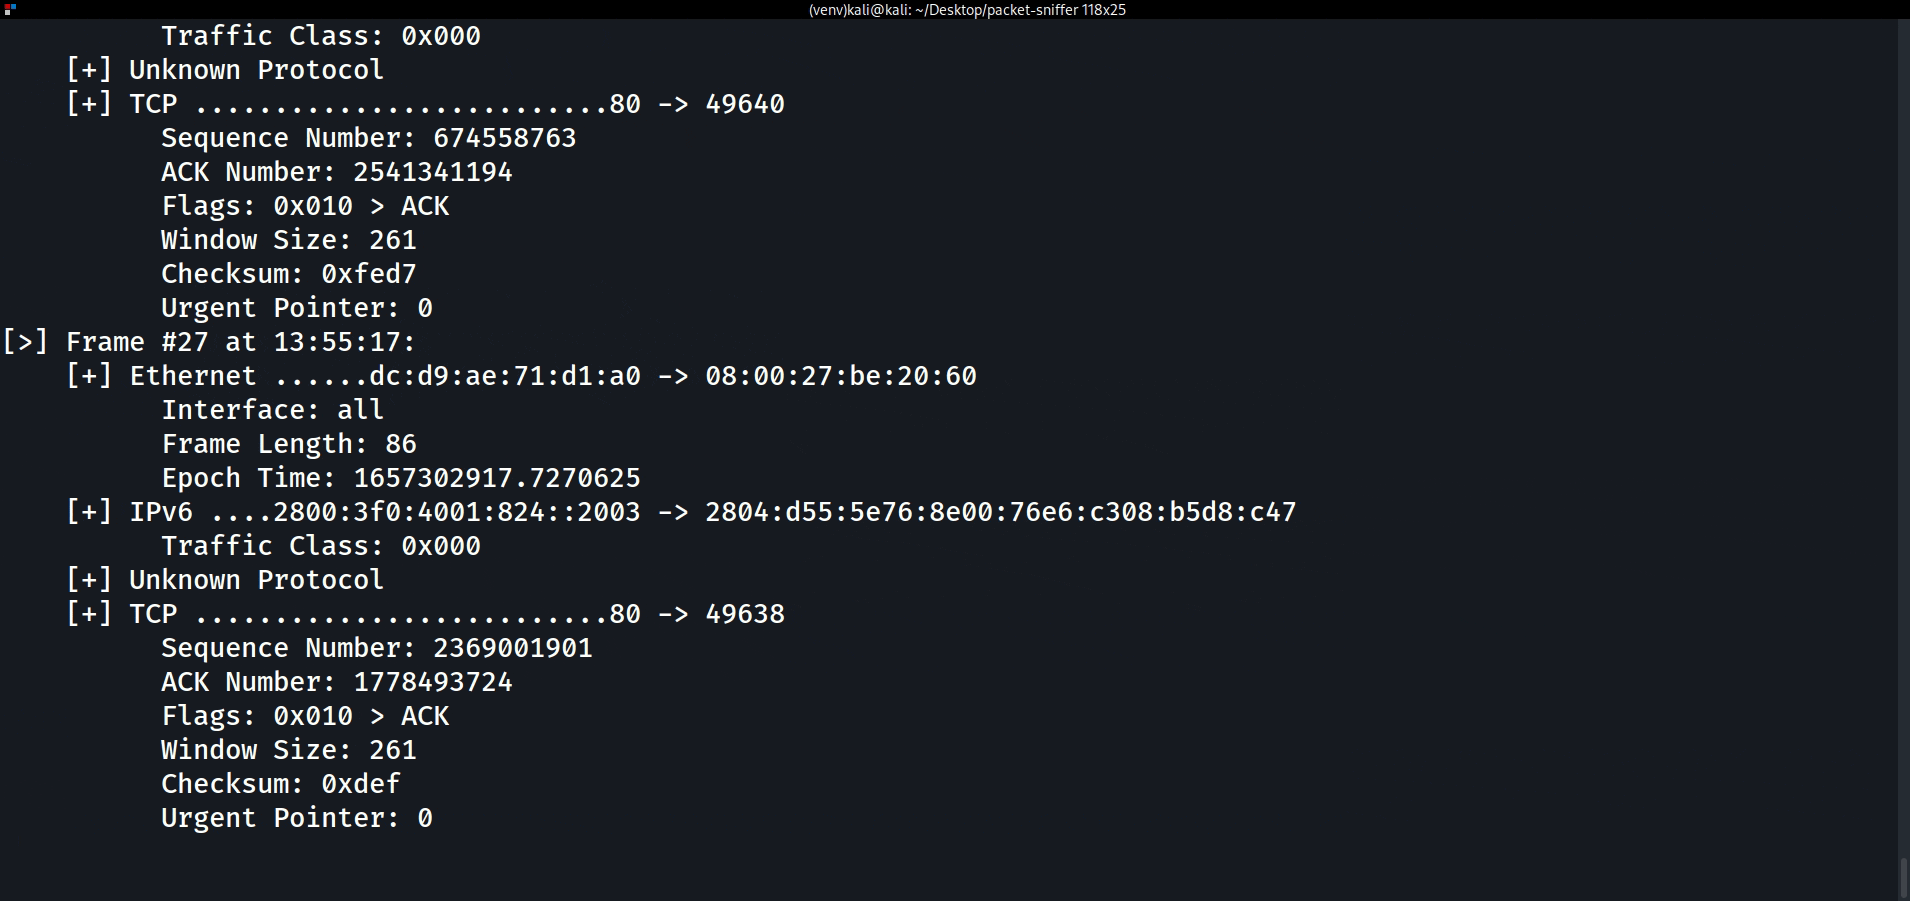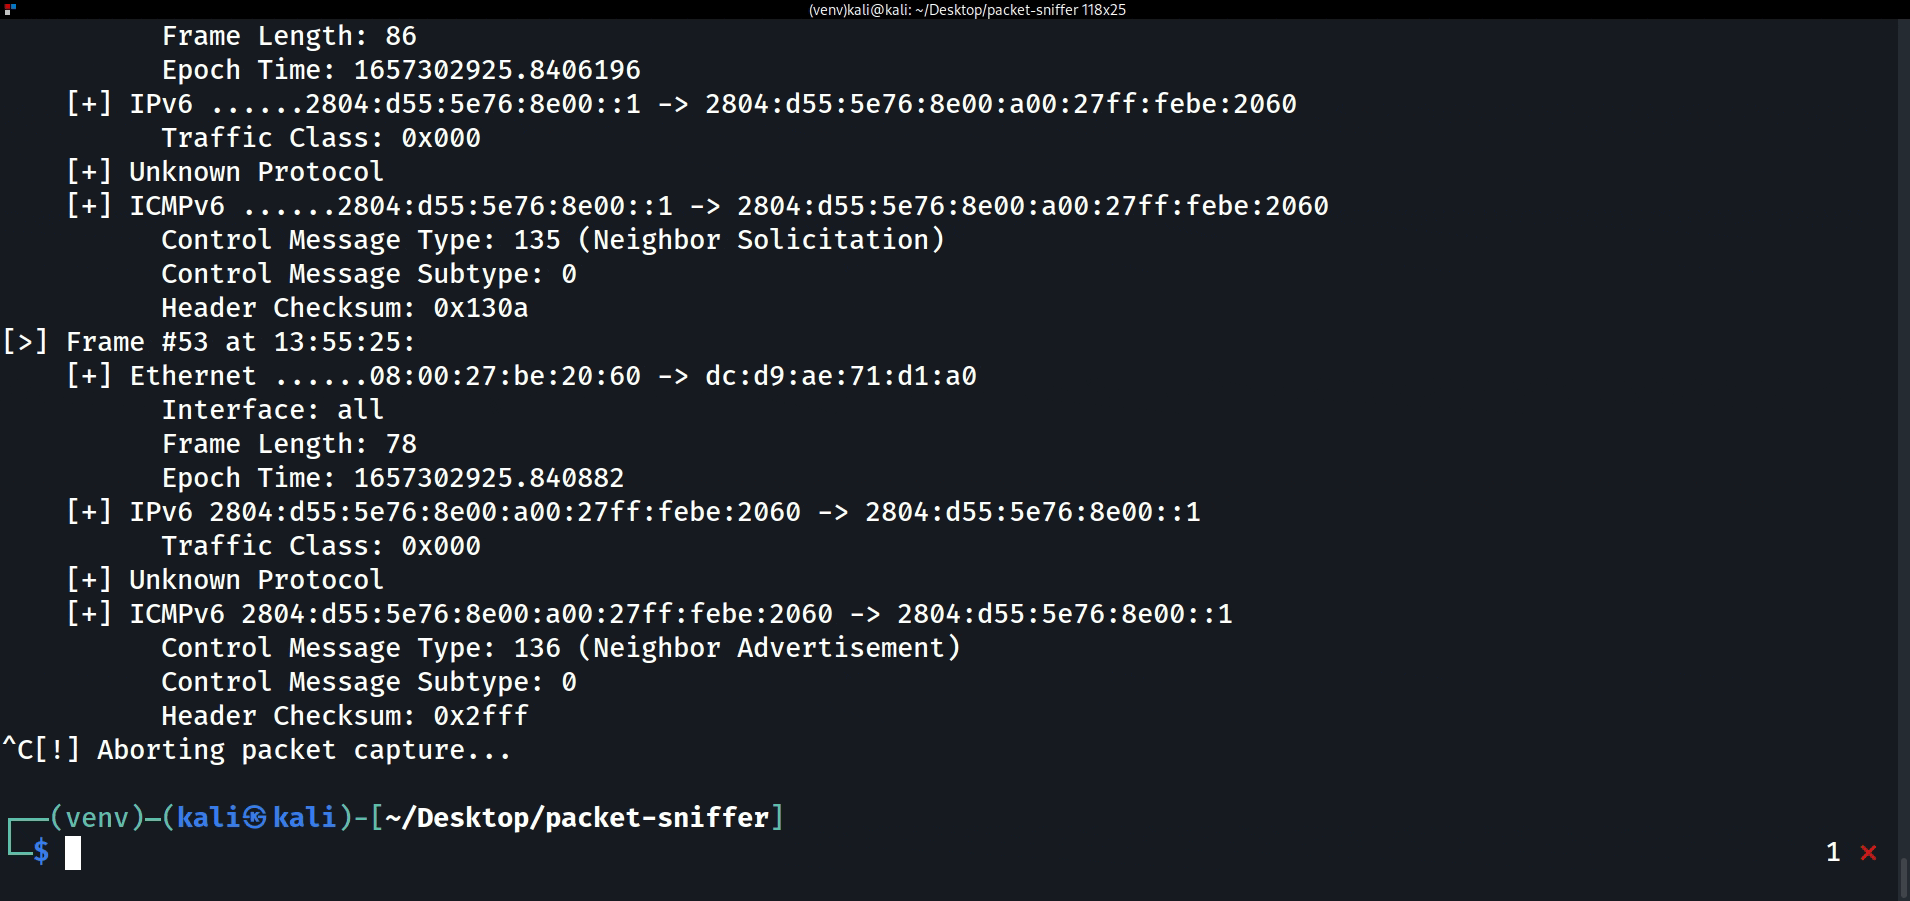 eonraider/packet-sniffer
Raw socket-based network packet sniffer that captures and disassembles TCP/IP packets from network interfaces for security analysis and educational…
 jiaoxianjun/btle
Bluetooth Low Energy (BLE) packet sniffer and transmitter for both standard and non standard (raw bit) based on Software Defined Radio (SDR).
 nccgroup/sniffle
Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…
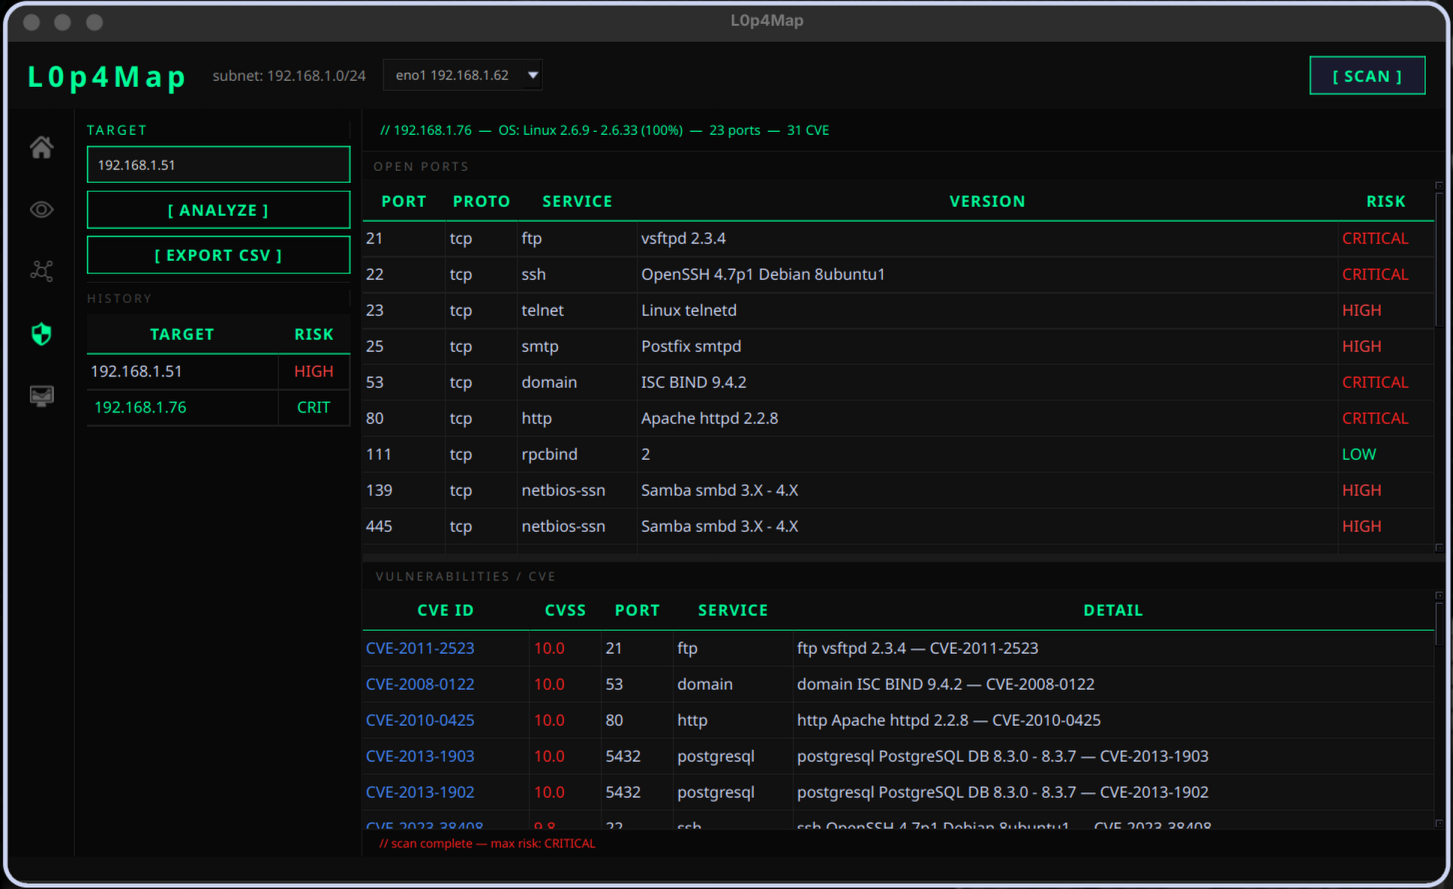 haxl0p4/l0p4map
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…