Detect-CVE-2017-0144-attack
 quynhold/detect-cve-2017-0144-attack
Chương trình theo dõi, giám sát lưu lượng mạng được viết bằng Python, nó sẽ đưa ra cảnh báo khi phát hiện tấn công CVE-2017-0144
educationintrusion-detectionlabs-practice+3
quynhold/detect-cve-2017-0144-attackChương trình theo dõi, giám sát lưu lượng mạng được viết bằng Python, nó sẽ đưa ra cảnh báo khi phát hiện tấn công CVE-2017-0144
 bl4ck5un/cve-2013-4348
DOS (infinite loop) attack via a small value in the IHL field of a packet with IPIP encapsulation
 deepfence/packetstreamer
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐
 digitalsecurity/btlejuice
BtleJuice Bluetooth Smart (LE) Man-in-the-Middle framework
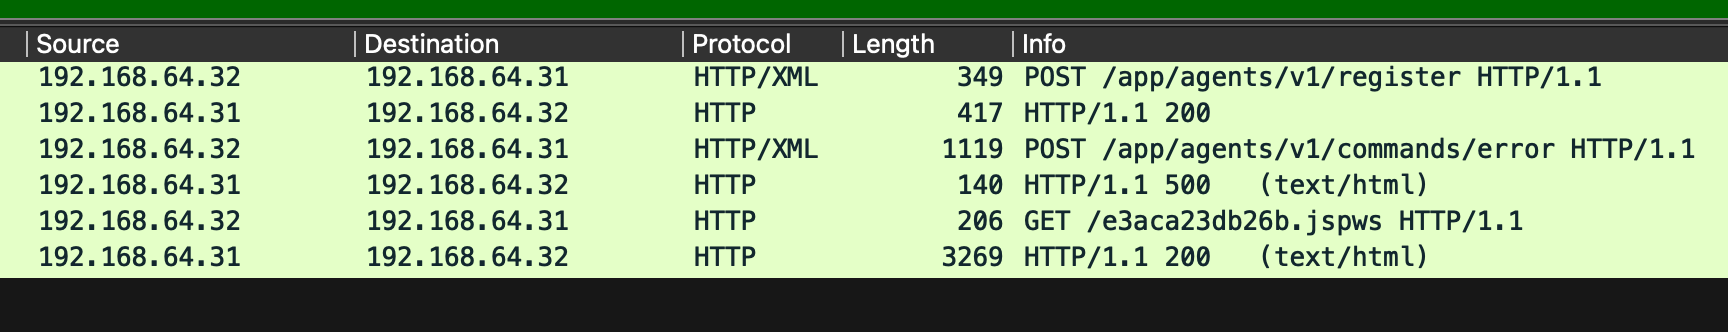 boredhackerblog/teamcity-cve-2026-63077-pcap
teamcity teamcity-CVE-2026-63077 exploitation pcap
 google/stenographer
Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…
 byt3bl33d3r/mitmf
Framework for Man-In-The-Middle attacks