
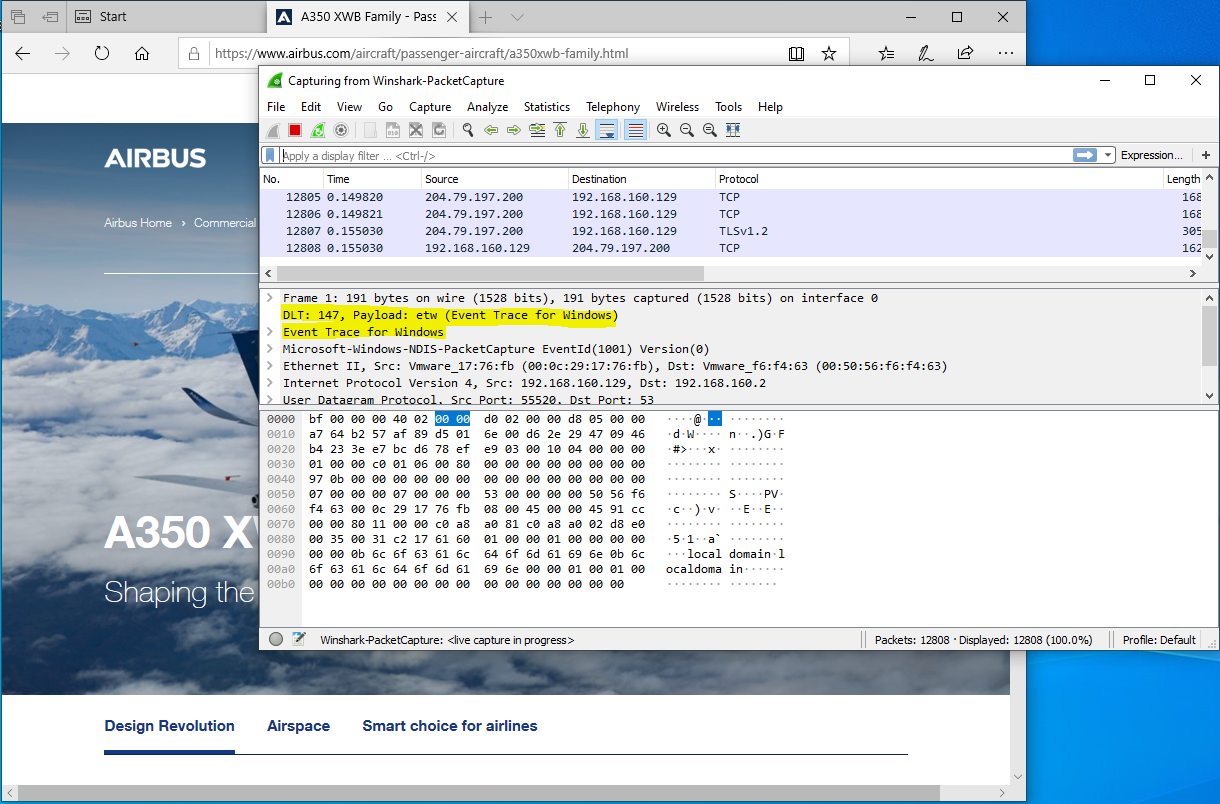
Winshark
 airbus-cert/winshark
A wireshark plugin to instrument ETW
forensicslog-analysisnetwork-security+1
airbus-cert/winsharkA wireshark plugin to instrument ETW
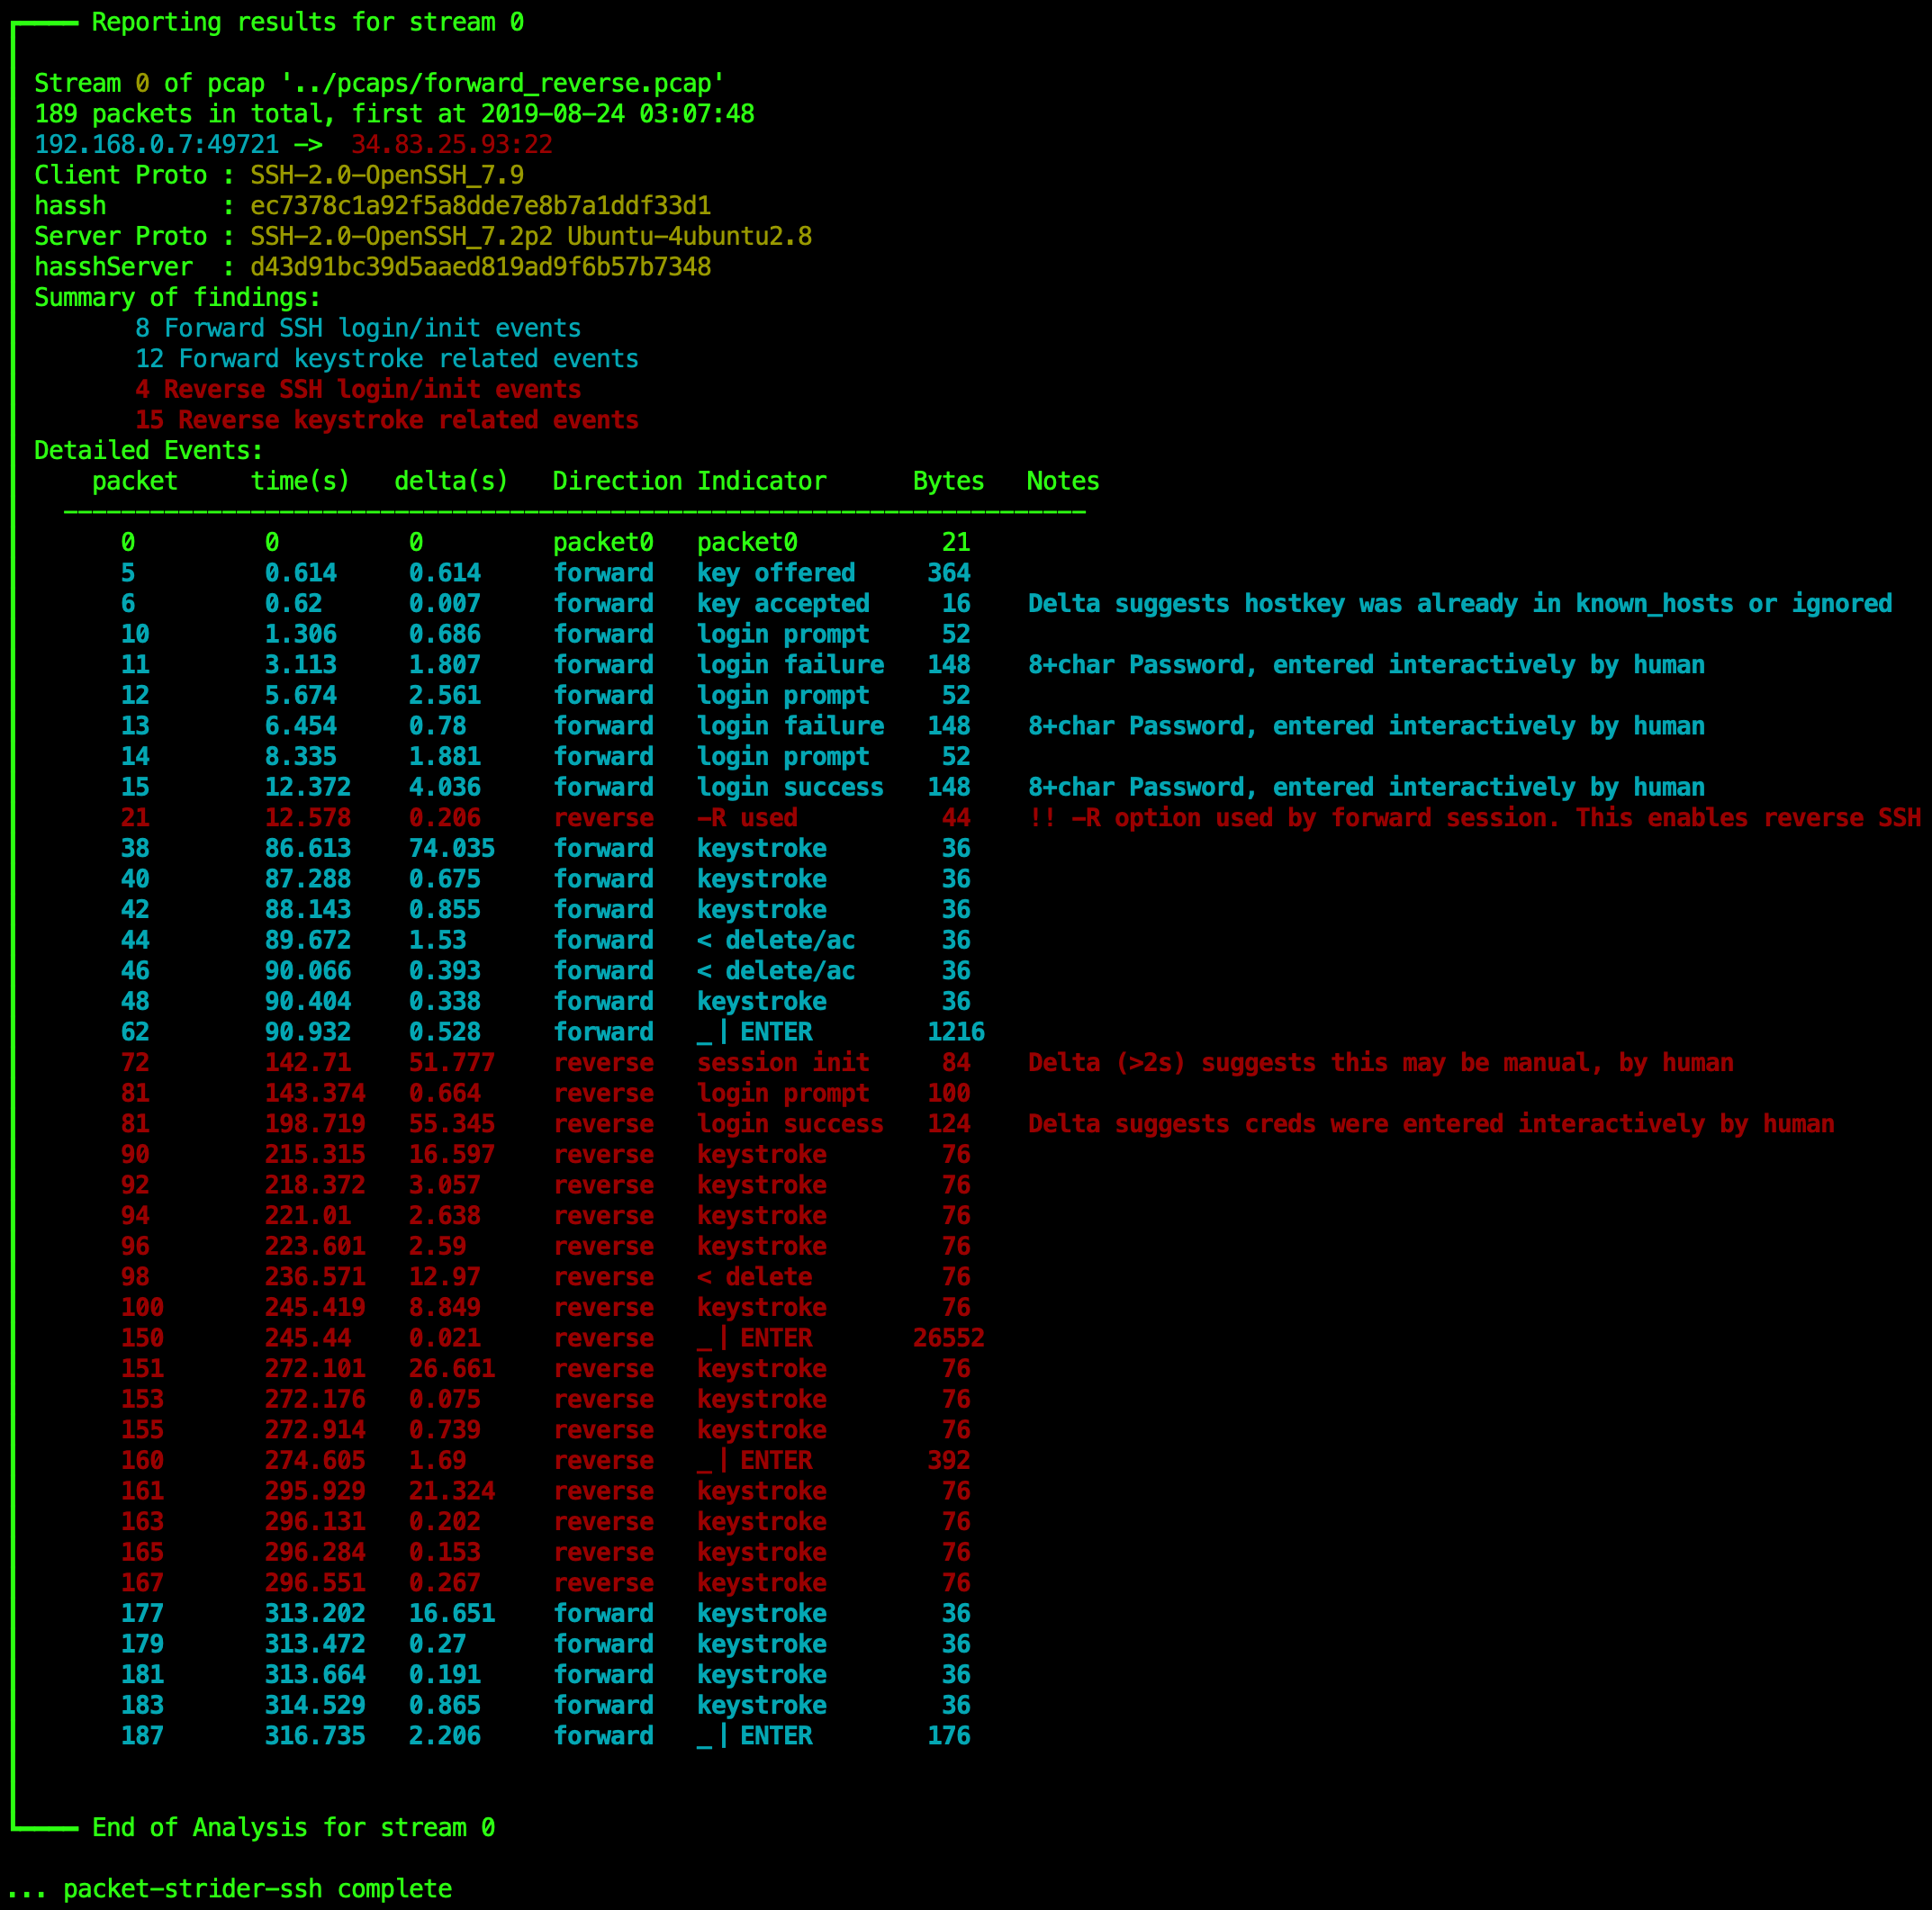 benjeems/packetstrider
A network packet forensics tool for SSH
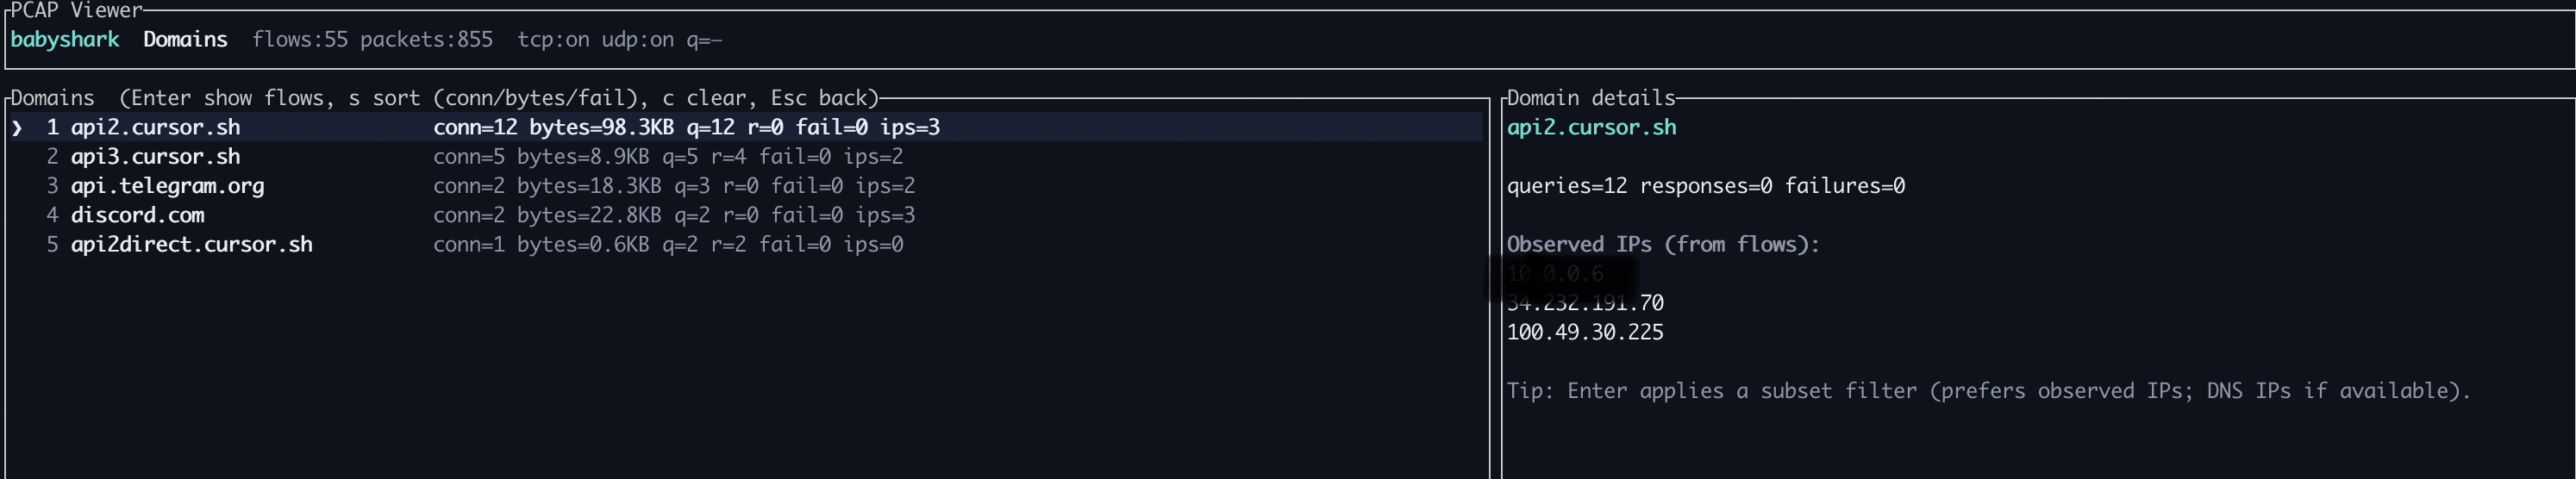 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 mhils/honeyproxy
This project is now part of @mitmproxy.
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)
 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
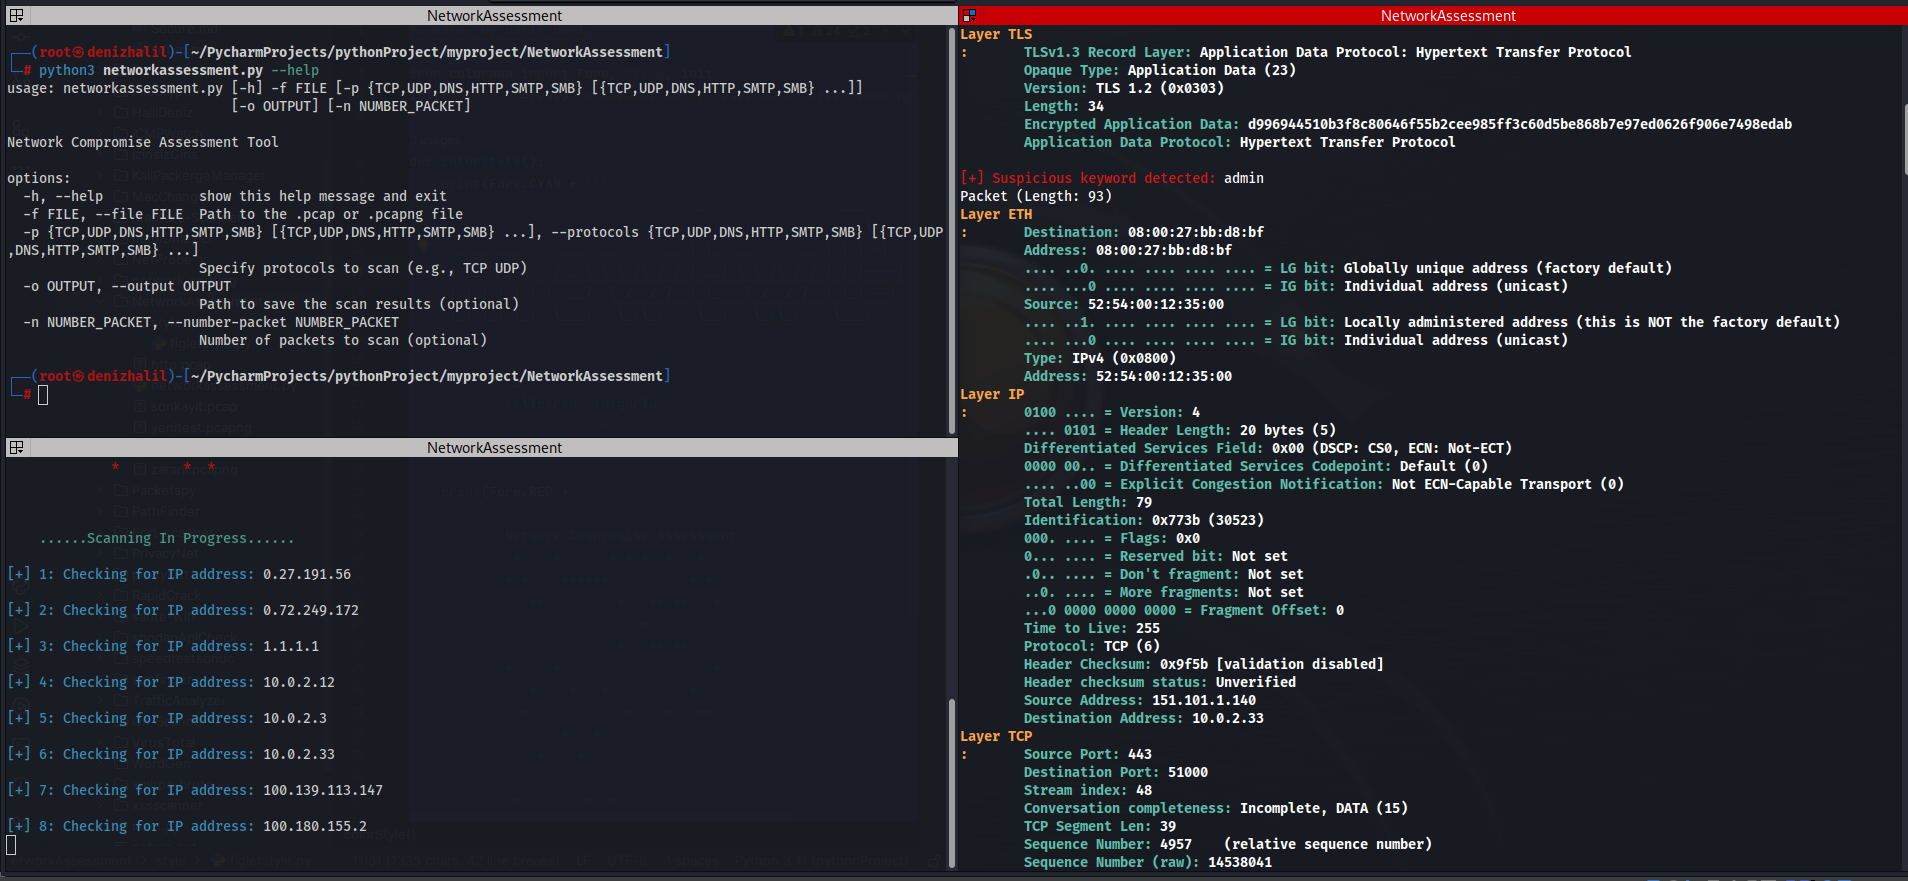 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 leonward/openfpc
OpenFPC, Open Source Full Packet Capture
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
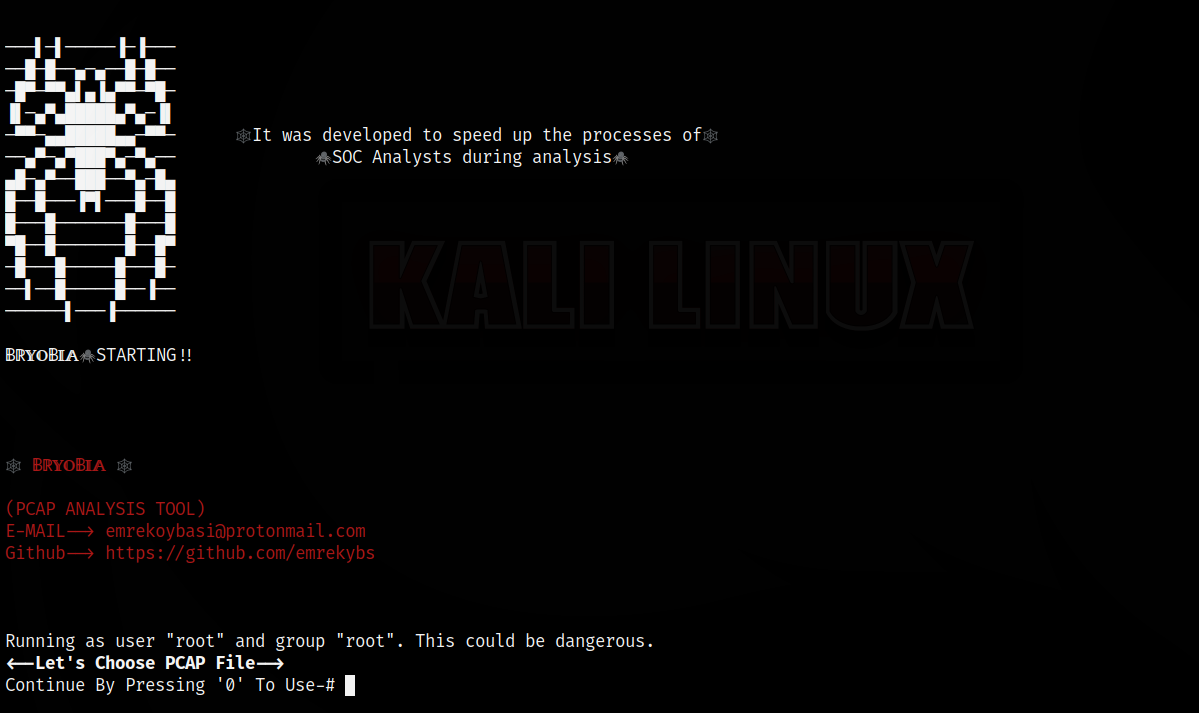 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
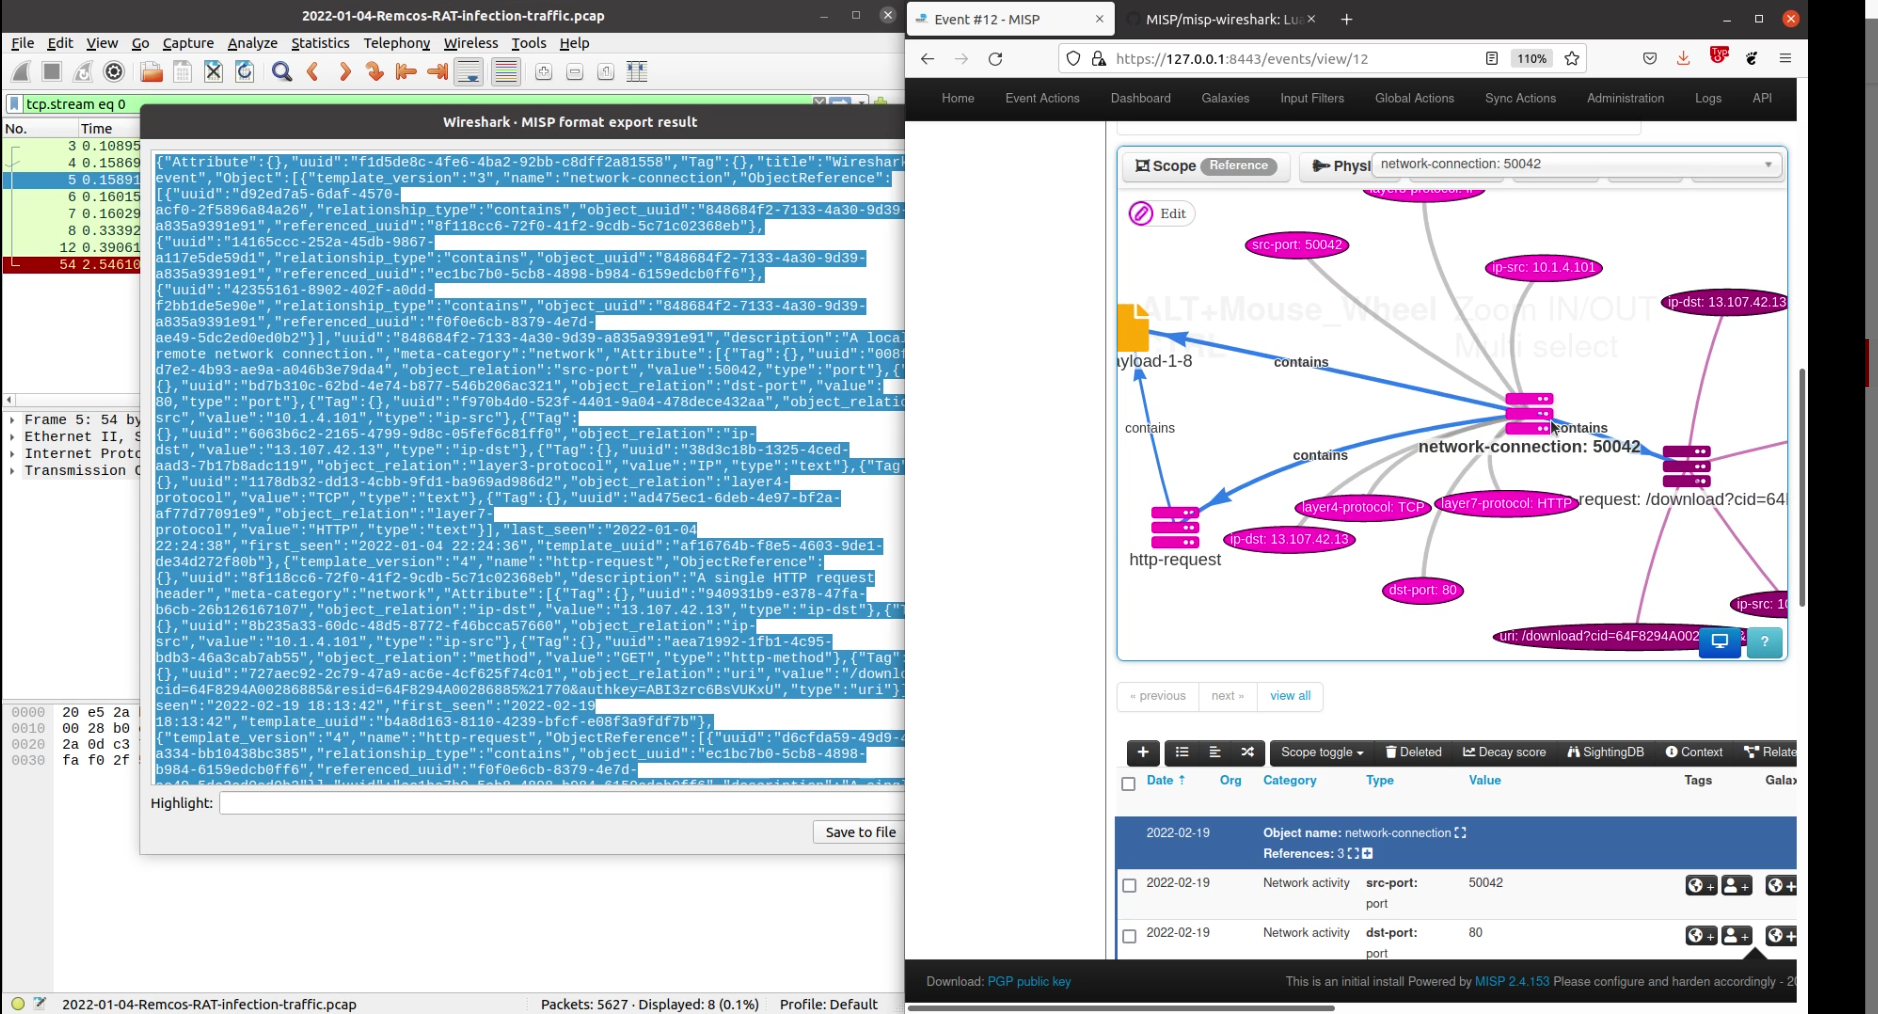 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
 camp0/aiengine
Programmable packet inspection engine with NIDS, DNS classification, frequency analysis, and auto-regex generation. Supports Python/Ruby/Java/Lua…
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
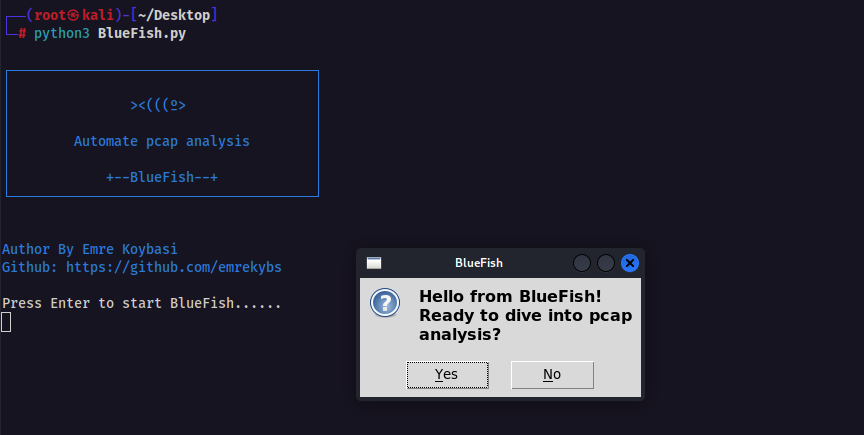 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files