
libbtbb
 greatscottgadgets/libbtbb
C library for decoding Bluetooth baseband packets and extracting piconet information from Ubertooth and USRP hardware for wireless analysis.
bluetooth-securitypacket-sniffing-analysiswireless-security
204
greatscottgadgets/libbtbbC library for decoding Bluetooth baseband packets and extracting piconet information from Ubertooth and USRP hardware for wireless analysis.
 hari-prasaanth/thick-client-pentest-checklist
A OWASP Based Checklist With 80+ Test Cases
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
 nao-sec/ramnit_traffic_parser
Parsing Ramnit's traffic
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
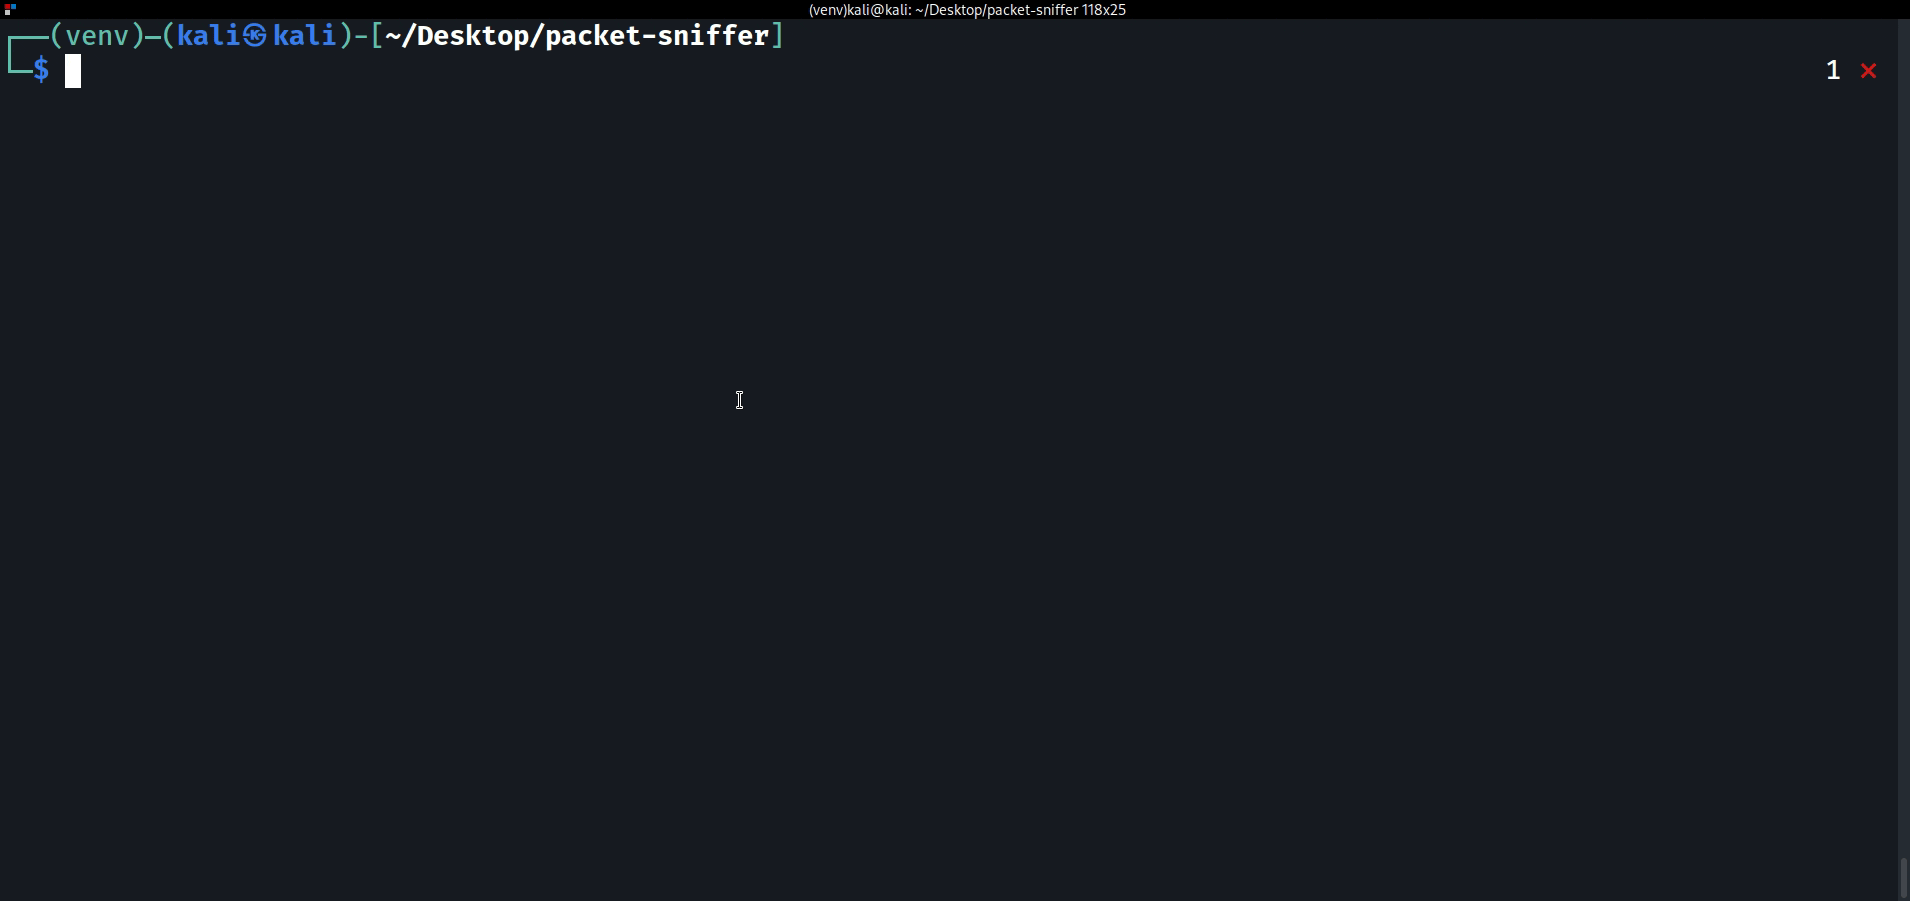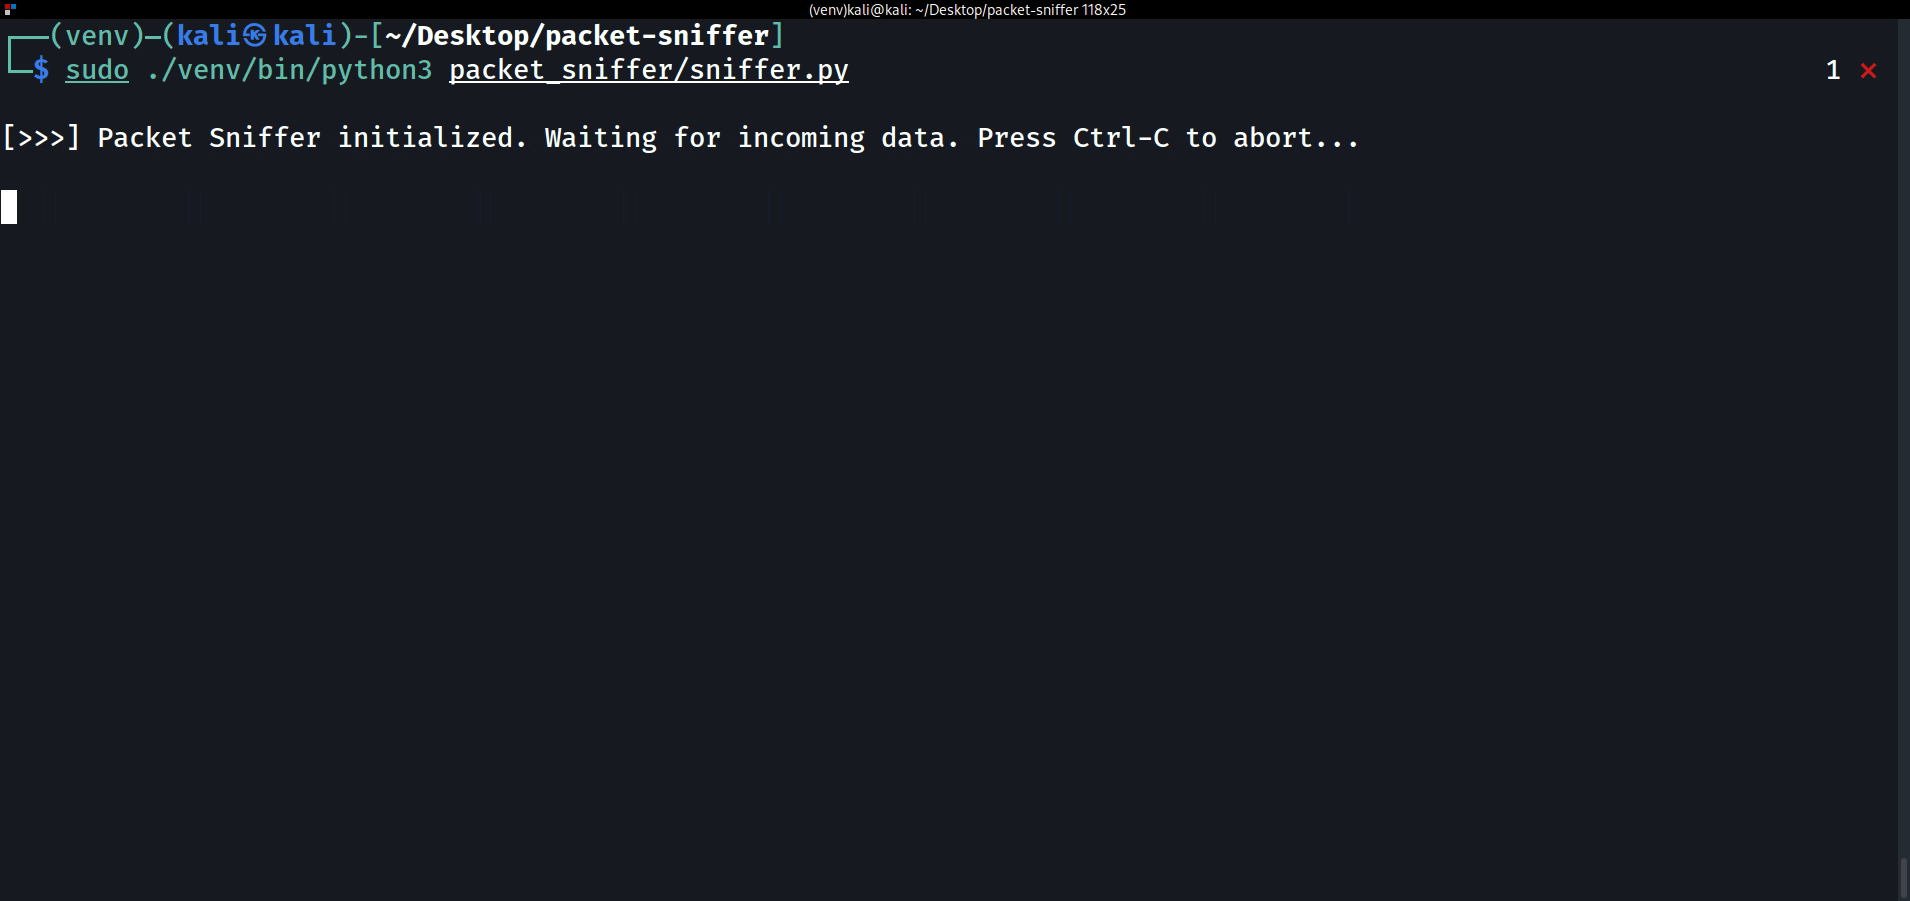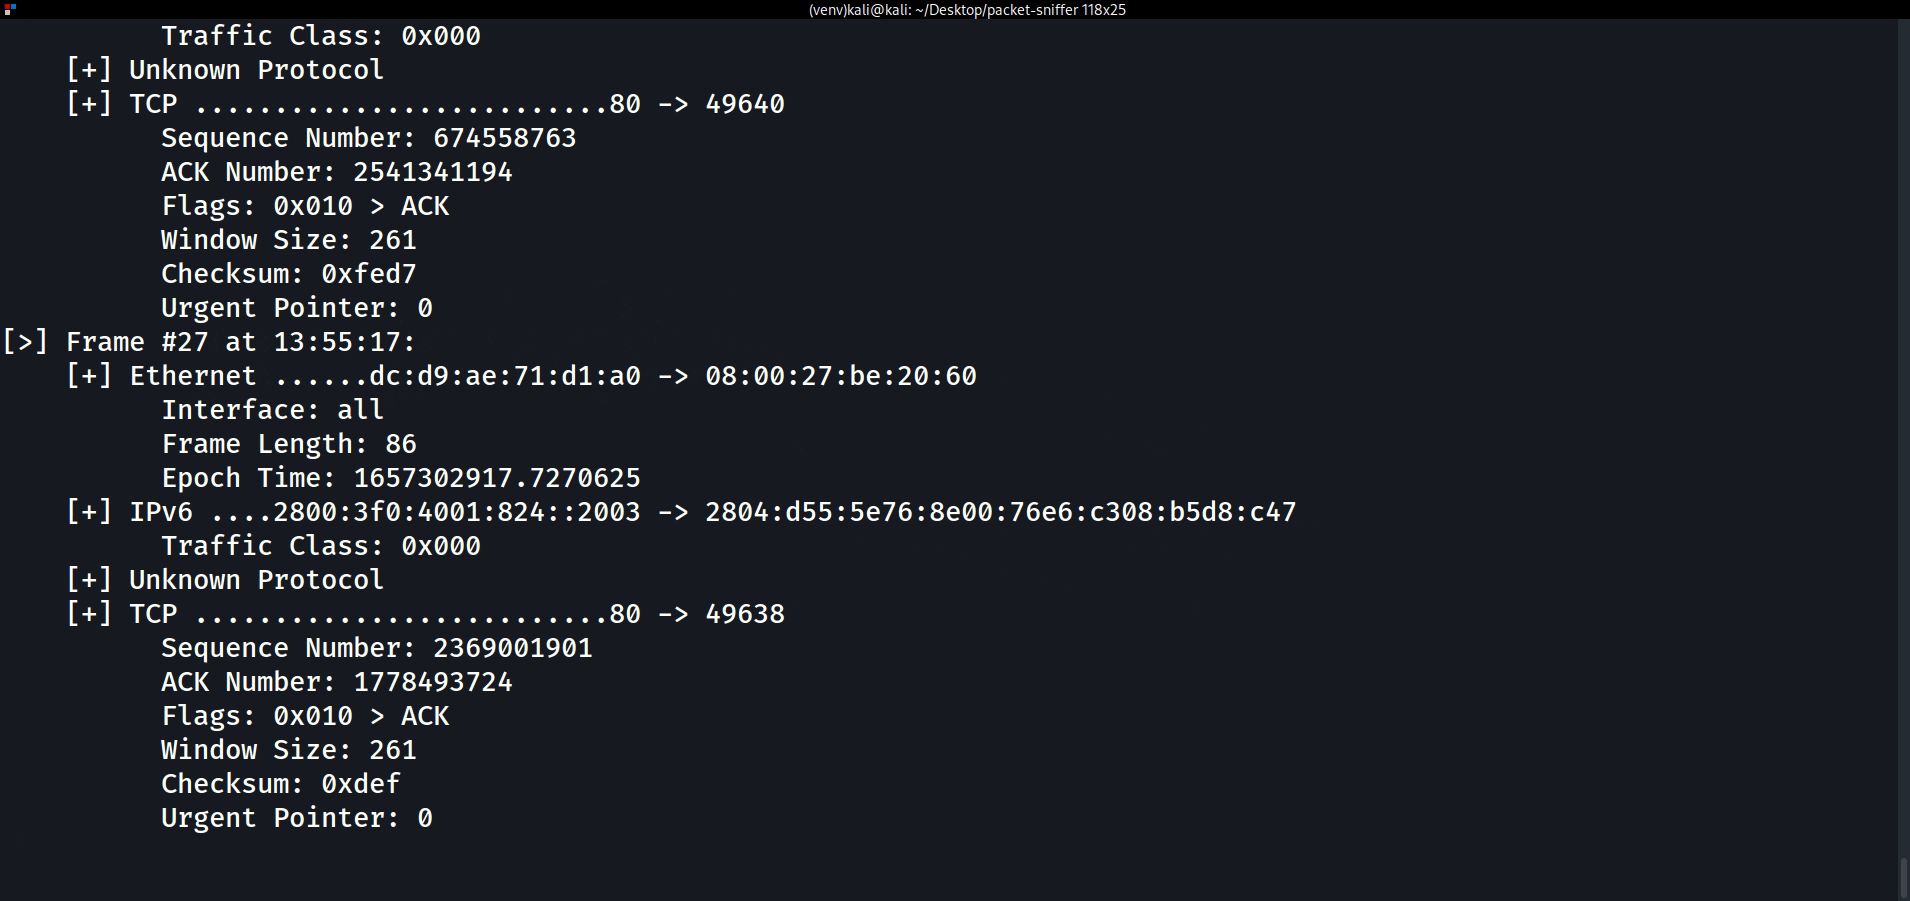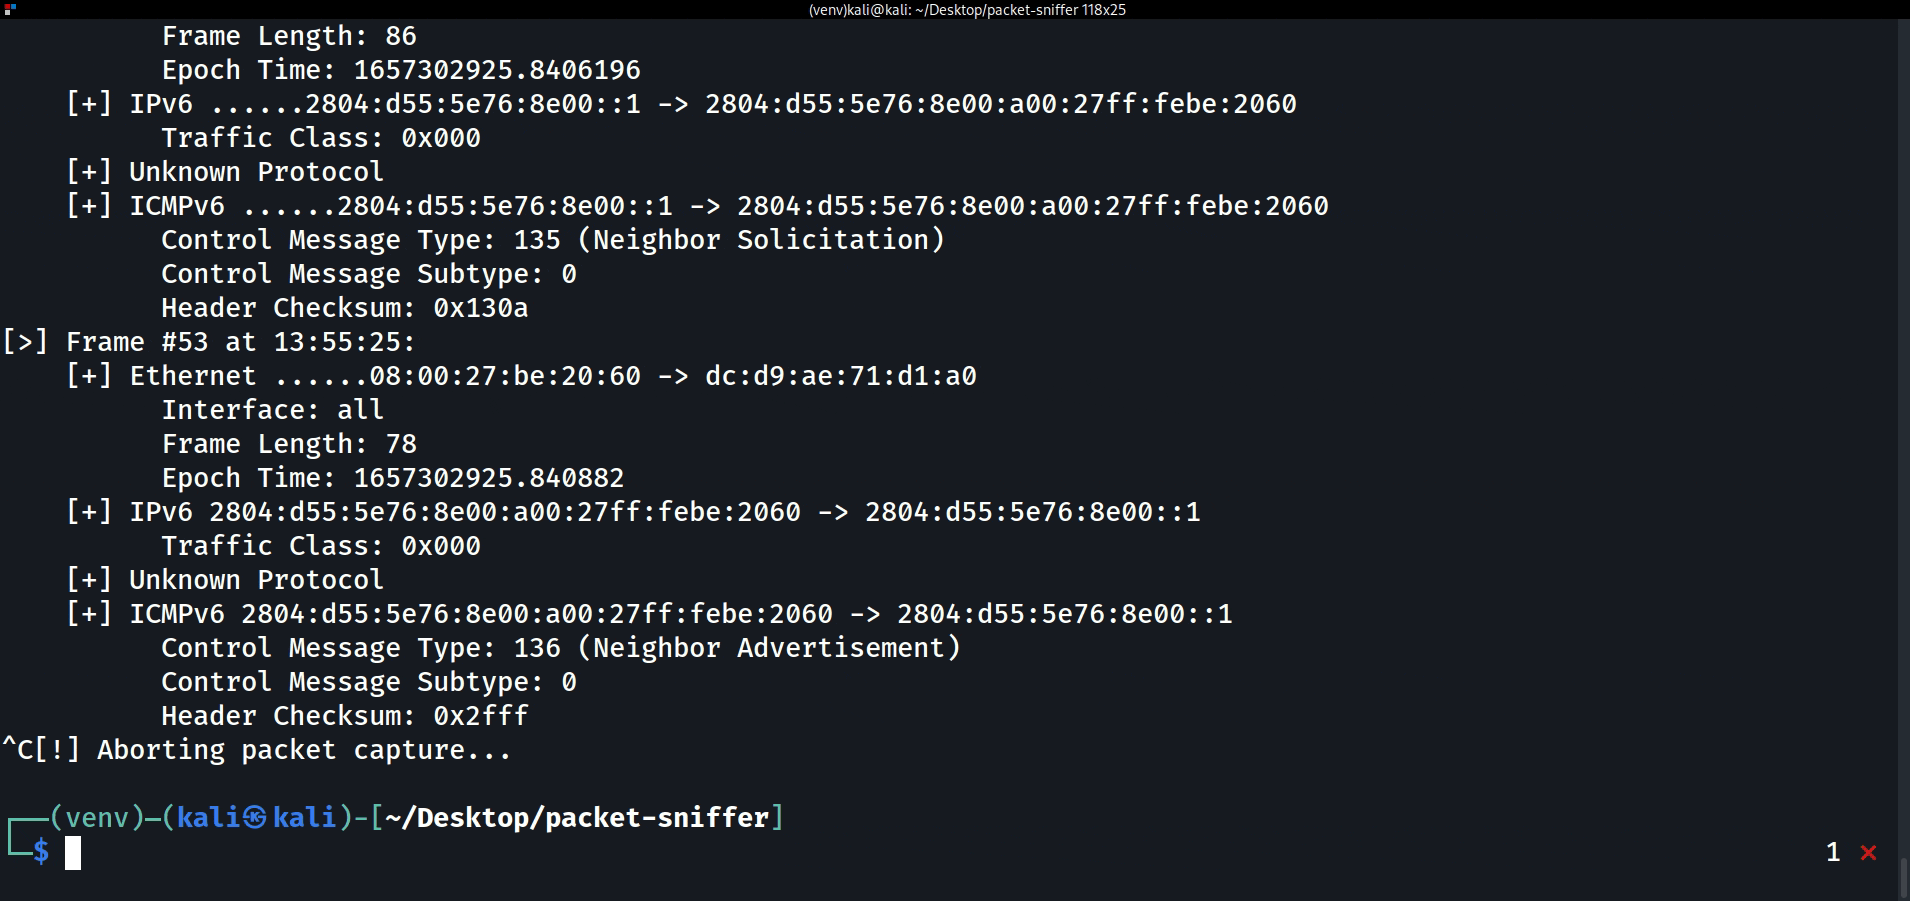 eonraider/packet-sniffer
Raw socket-based network packet sniffer that captures and disassembles TCP/IP packets from network interfaces for security analysis and educational…
 owasp/pysap
pysap is an open source Python library that provides modules for crafting and sending packets using SAP's NI, Diag, Enqueue, Router, MS, SNC, IGS,…

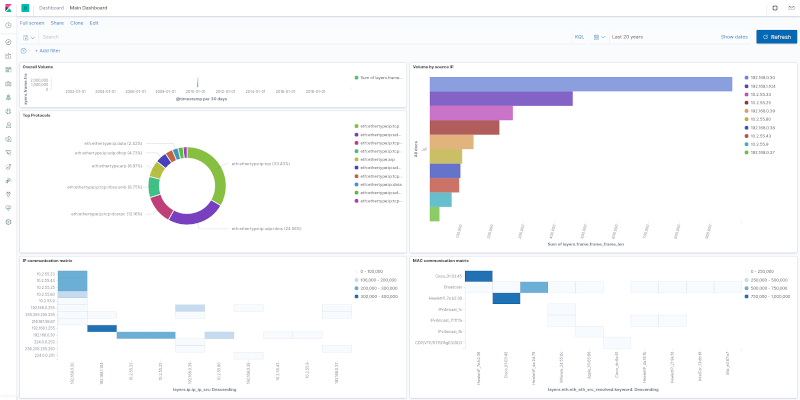 h21lab/tsharkvm
tshark + ELK analytics virtual machine
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
 jean-nestor/evil-twin-ap
Automated evil twin access point toolkit with traffic capture and real-time monitoring for wireless penetration testing and security research.
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
 abiral-timalsina/cyber-defenders-lab-
My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
 trg-1999/detectpacket-cve-2017-8464
Exploit vulnerabilities and vulnerability prevention implementation
 ivoalbacete/kali-metasploitable
Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.
 alexanderortizscript/evillcode
Herramienta de auditoría y análisis de redes para Kali Linux.