
pastokrapacefleciks
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
digital-forensicsforensicslog-analysis+2
nu11secur1ty/pastokrapacefleciksAnalyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 aidilzlkfli/scanning
Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).
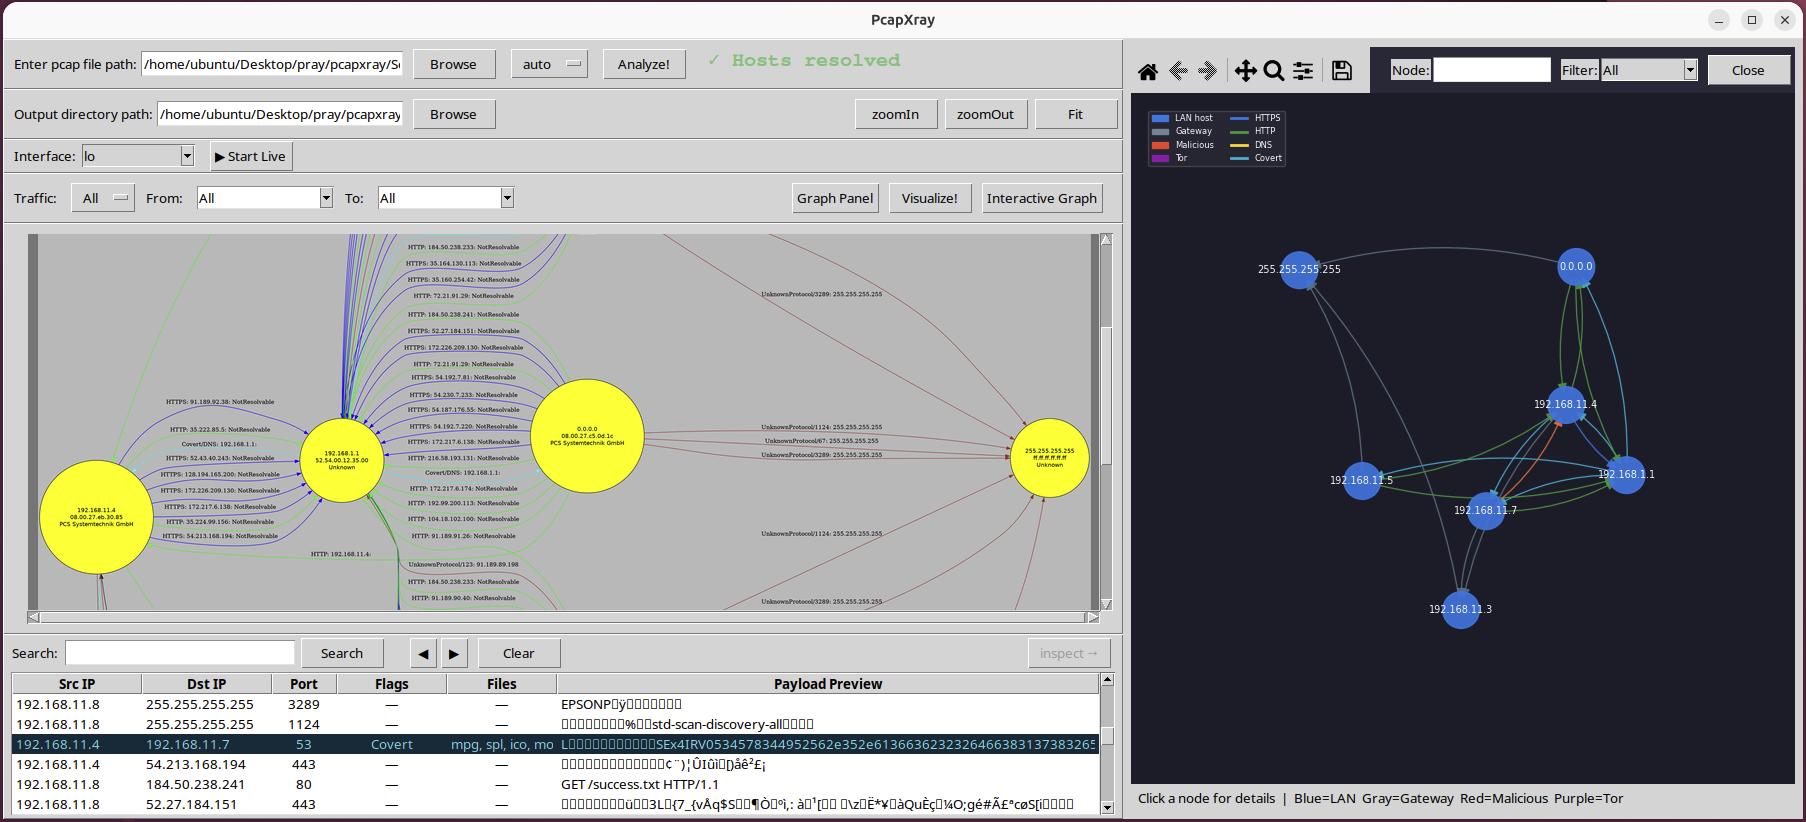 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 lgandx/pcredz
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 kirkdjohnson/wireshark
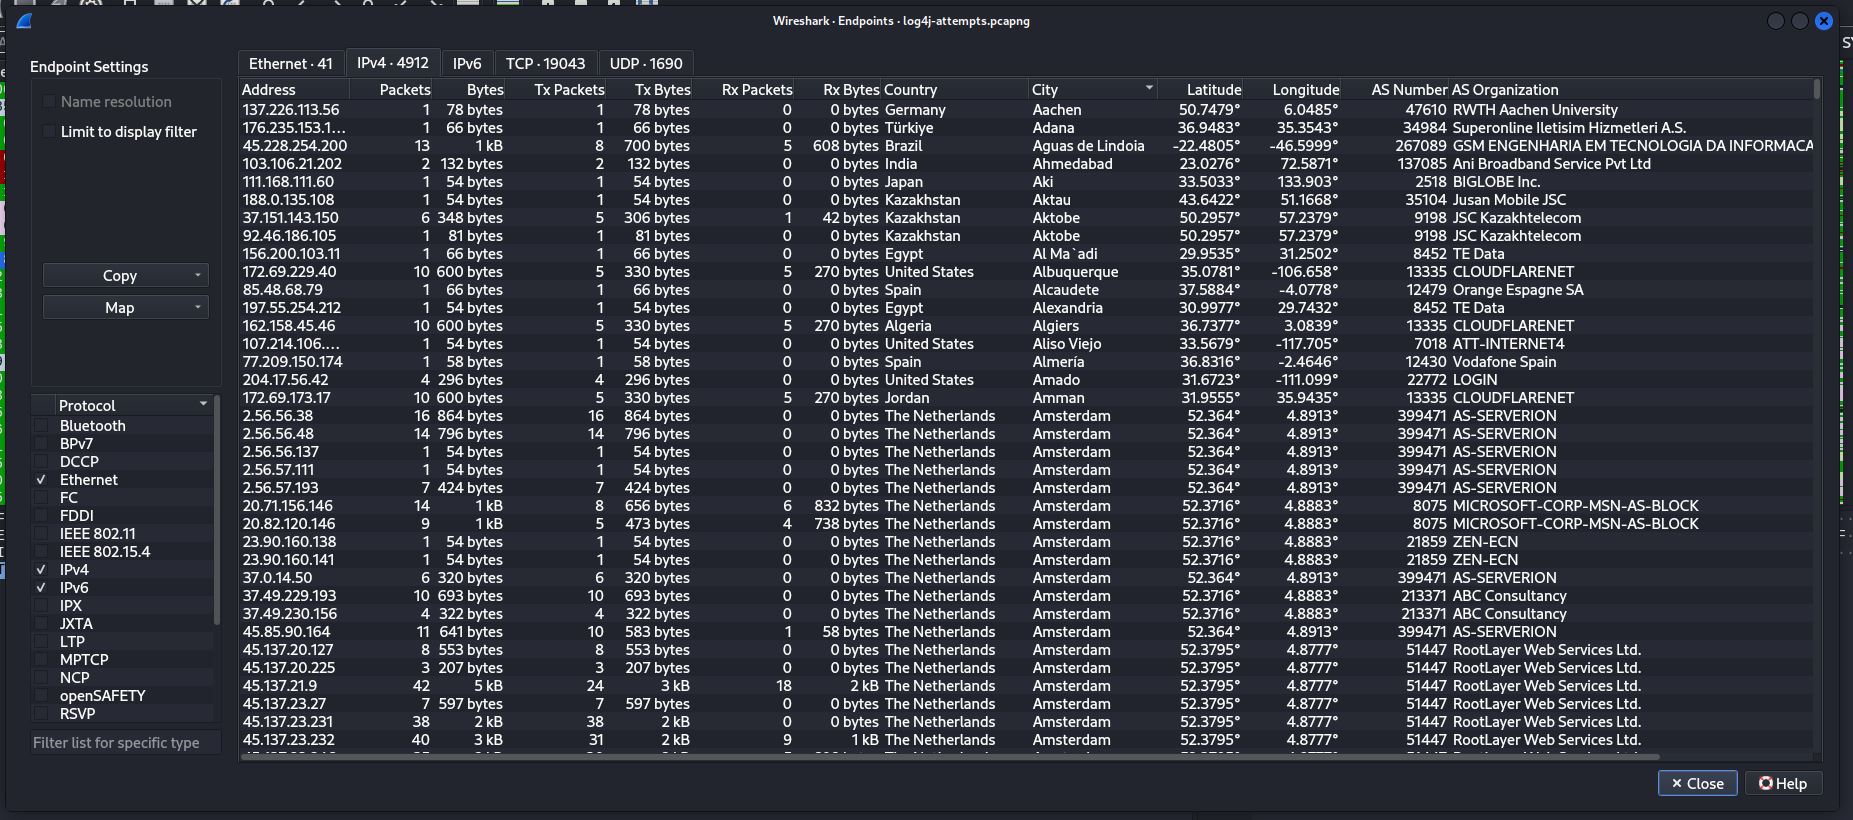
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 corelight/zeek-elf
A Zeek ELF File Analyzer
 alt3kx/airdecloak-ng
My Aircrack-ng contribution with Thomas d'Otreppe
 chrism09/knx-bus-dump
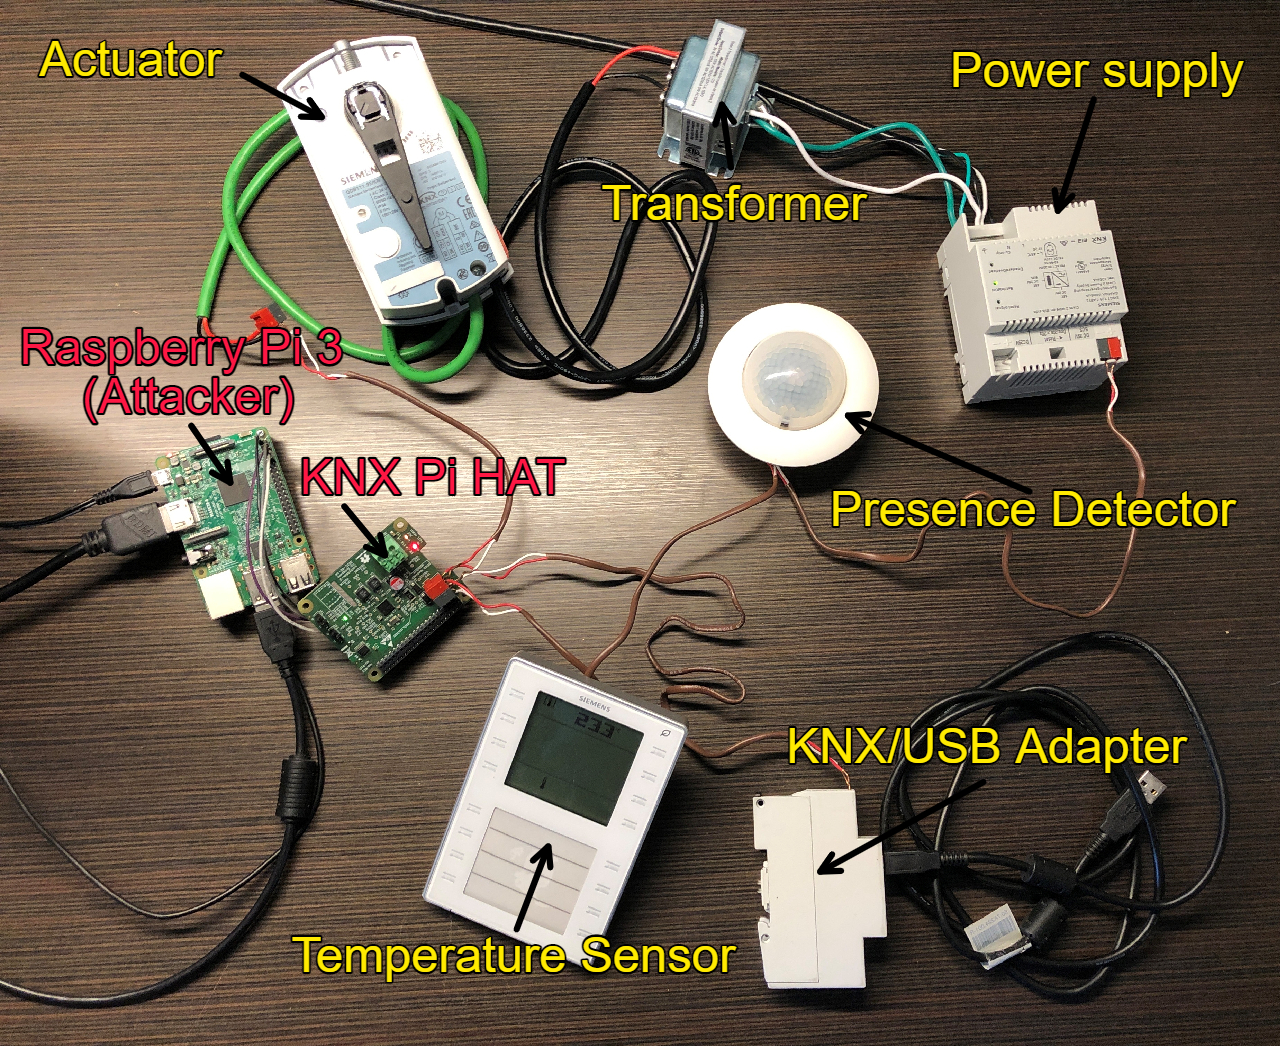
A tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…
 apipia/log4j-pcap-activity
A fun activity using a packet capture file from the log4j exploit (CVE-2021-44228)
 phaethon/kamene
Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…
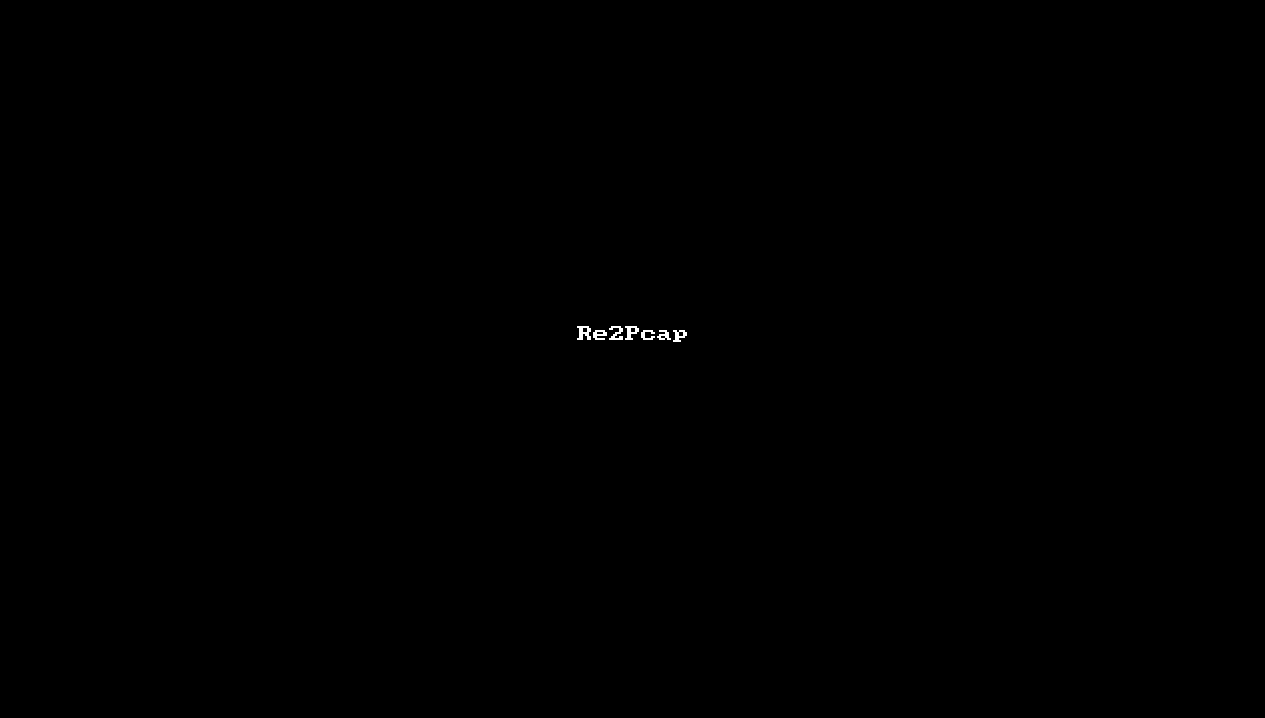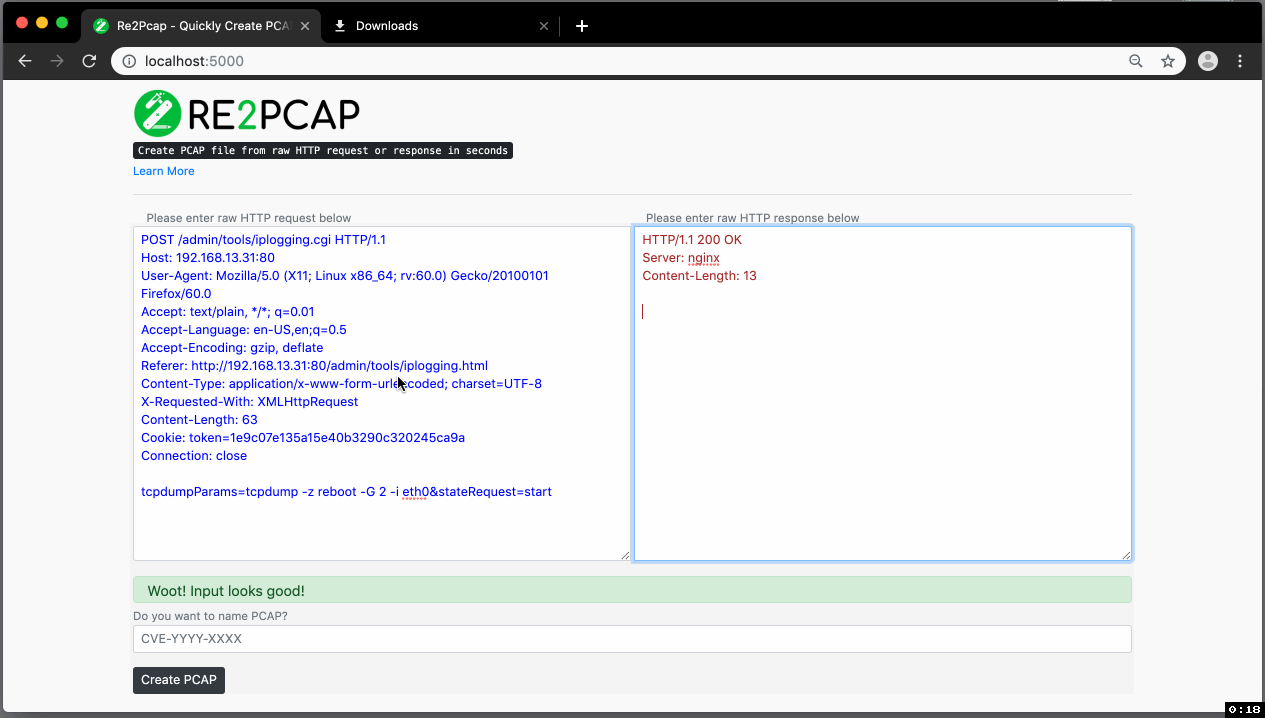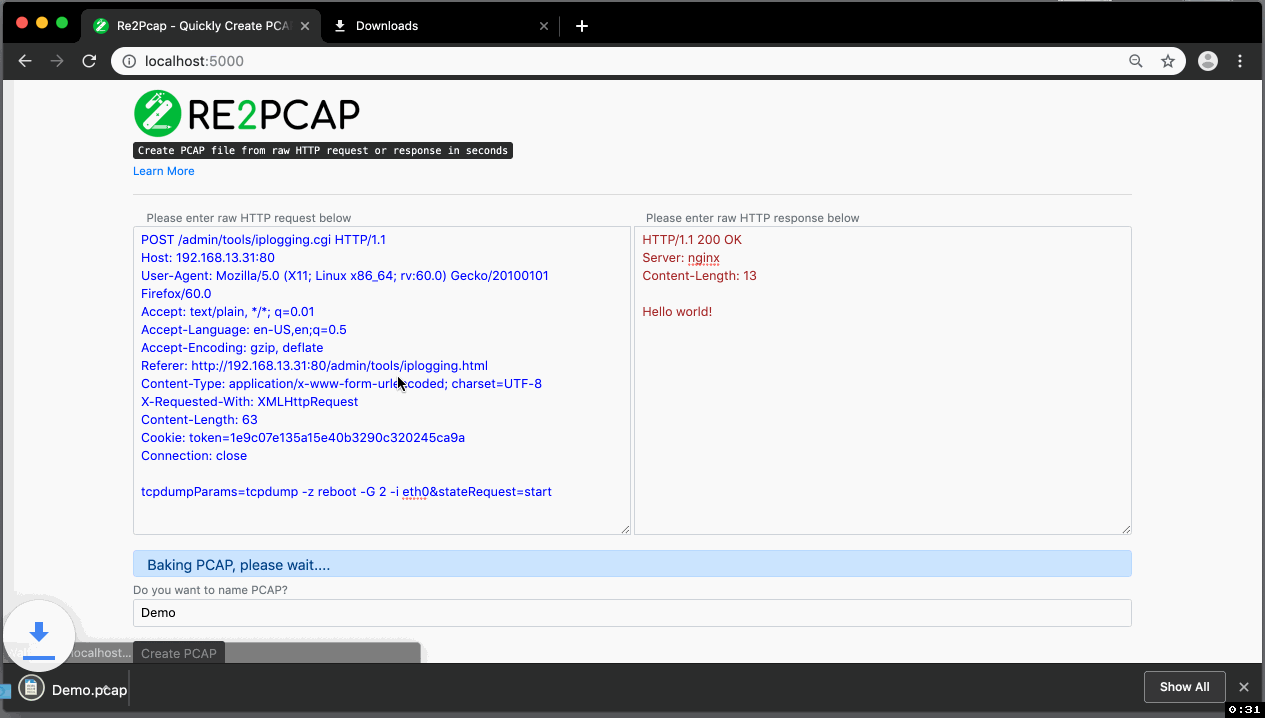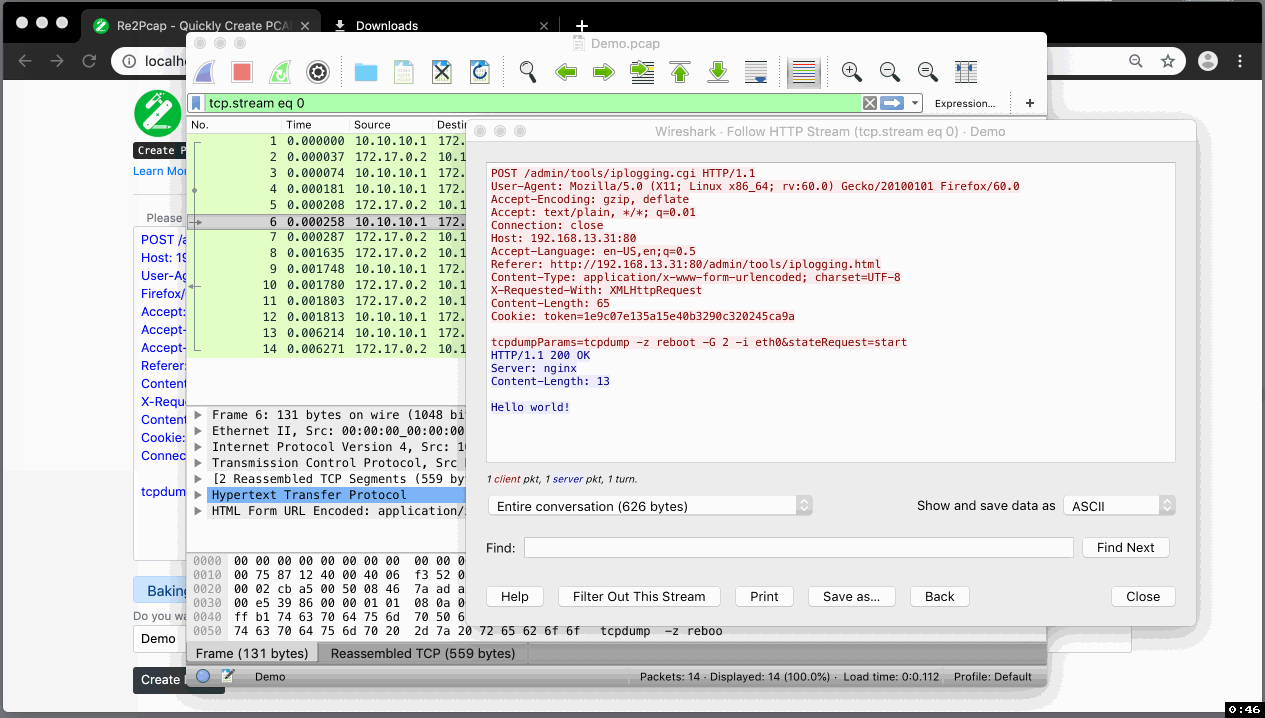 cisco-talos/re2pcap
Convert raw HTTP requests/responses into PCAP files for testing Snort IDS rules and network security analysis. Supports Docker deployment and…
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 danmcinerney/net-creds
Sniffs sensitive data from interface or pcap
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
 withsecurelabs/doublepulsar-c2-traffic-decryptor
A python2 script for processing a PCAP file to decrypt C2 traffic sent to DOUBLEPULSAR implant