reverse-engineering-browser

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

Detects network covert channels using Shannon entropy and Sarle's bimodality coefficient to flag encrypted ICMP/TCP payload exfiltration and…

Longitudinal anycast census system that probes IPv4/IPv6 prefixes via ICMP, TCP, and DNS to detect anycast deployments and geolocate PoPs, publishing…

Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…

Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…

A curated list of resources related to Industrial Control System (ICS) security.

Fast ARP-based network scanner for discovering and fingerprinting IPv4 hosts on local networks, with vendor lookup, adjustable scan rates, and…

Multi-threaded network intrusion detection and prevention system with rule-based detection, protocol-aware inspection, and pcap analysis for…

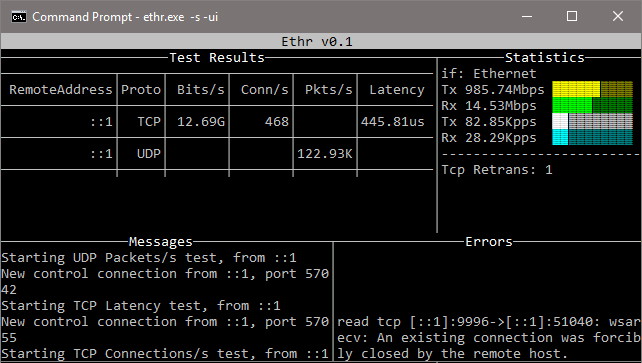
Cross-platform CLI for network performance testing over TCP, UDP, HTTP, HTTPS, and ICMP: bandwidth, connections/s, packets/s, latency, loss, jitter,…

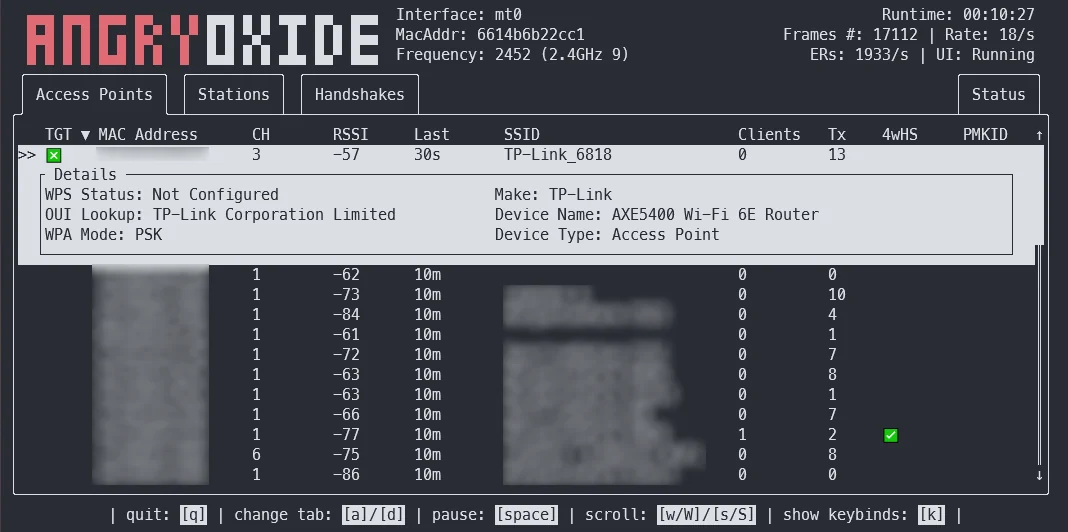
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…

Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…

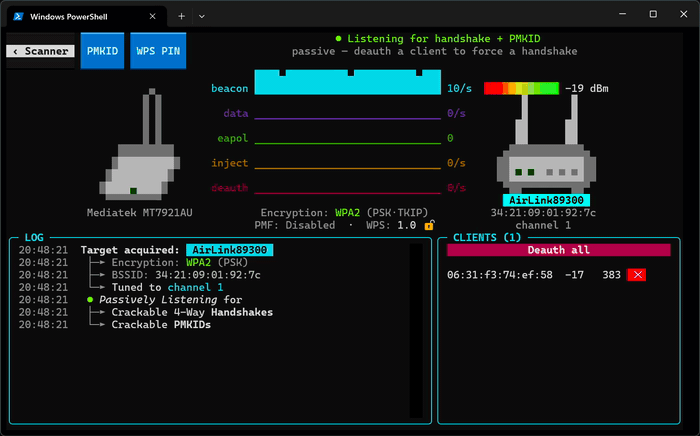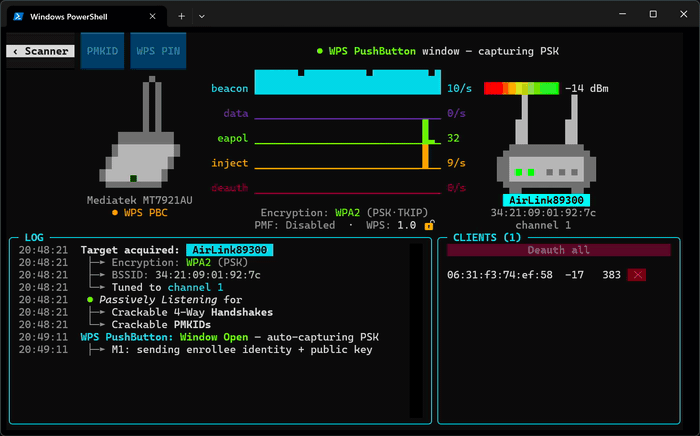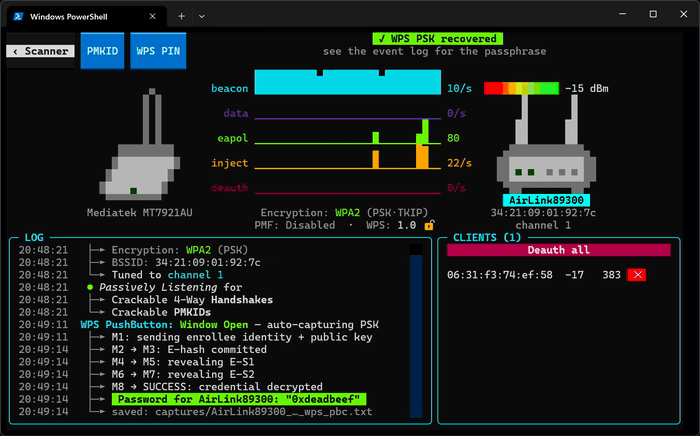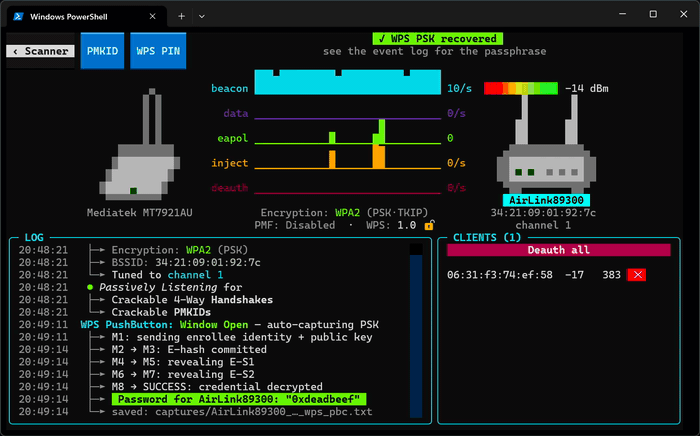
Wifite but USB-only & cross-platform.

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more

This repository contains a list of new remediation scripts.

A mDNS sniffer and interpreter.