Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
27 results
windows-malware-behavioral-analysis preview

windows-malware-behavioral-analysis

GitHub0x0allenace/windows-malware-behavioral-analysis

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…

digital-forensicsdynamic-analysis-sandboxingeducation+8
1 month ago
NetScope preview

NetScope

GitHubspectralzero/netscope

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

anomaly-detectiondigital-forensicsincident-response+5
31 month ago
esp32_bluetooth_classic_sniffer preview

esp32_bluetooth_classic_sniffer

GitHubmatheus-garbelini/esp32_bluetooth_classic_sniffer

Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)

bluetooth-securityembedded-systems-securityexploitation+3
6023 years ago
zeek-quic preview

zeek-quic

GitHubcorelight/zeek-quic

Bro analyzer that detects Google's QUIC protocol

intrusion-detectionlog-analysisnetwork-forensics+2
115 years ago
MITMer preview

MITMer

GitHubhusam212/mitmer

Automated man-in-the-middle attack tool.

dns-analysisnetwork-securitypacket-sniffing-analysis+5
5312 years ago
ipdecap preview

ipdecap

GitHublpefferkorn/ipdecap

Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…

encryption-decryption-toolsforensicsnetwork-forensics+3
357 years ago
ramnit_traffic_parser preview

ramnit_traffic_parser

GitHubnao-sec/ramnit_traffic_parser

Parsing Ramnit's traffic

command-and-controldigital-forensicsforensics+3
48 years ago
loki-parse preview

loki-parse

GitHubr3mrum/loki-parse

A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…

data-exfiltrationdigital-forensicsforensics+5
139 years ago
CVE-2021-33959 preview

CVE-2021-33959

GitHublixiang957/cve-2021-33959

Proof-of-concept exploit for CVE-2021-33959 demonstrating UDP reflection amplification attack against Plex Media Server via crafted M-SEARCH packets…

dns-analysisexploitationnetwork-security+2
13 years ago
LTESniffer preview

LTESniffer

GitHubsyssec-kaist/ltesniffer

An Open-source LTE Downlink/Uplink Eavesdropper

educationinformation-gatheringnetwork-security+5
2.2k1 year ago
arp-dns-attacks preview

arp-dns-attacks

GitHubashishraste/arp-dns-attacks

ARP spoofing, HTTP redirection, DNS spoofing and DNS forging using pcap library

dns-analysiseducationexploitation+3
3113 years ago
kyanos preview

kyanos

GitHubhengyoush/kyanos

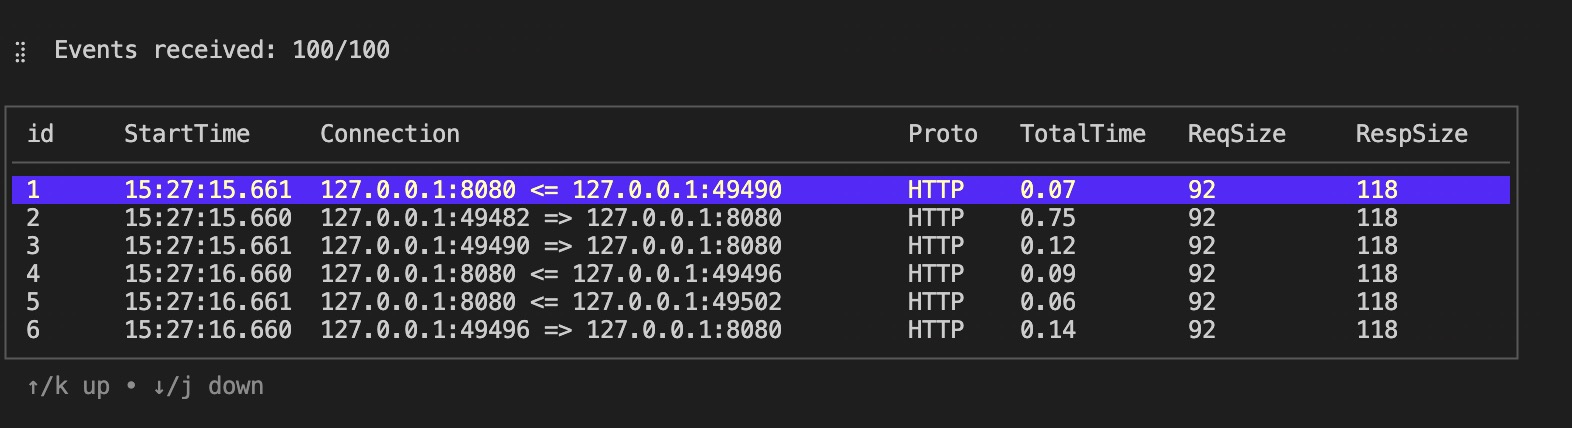
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…

dns-analysisdynamic-analysis-sandboxinglog-analysis+3
5.1k3 months ago
PCAPdroid preview

PCAPdroid

GitHubemanuele-f/pcapdroid

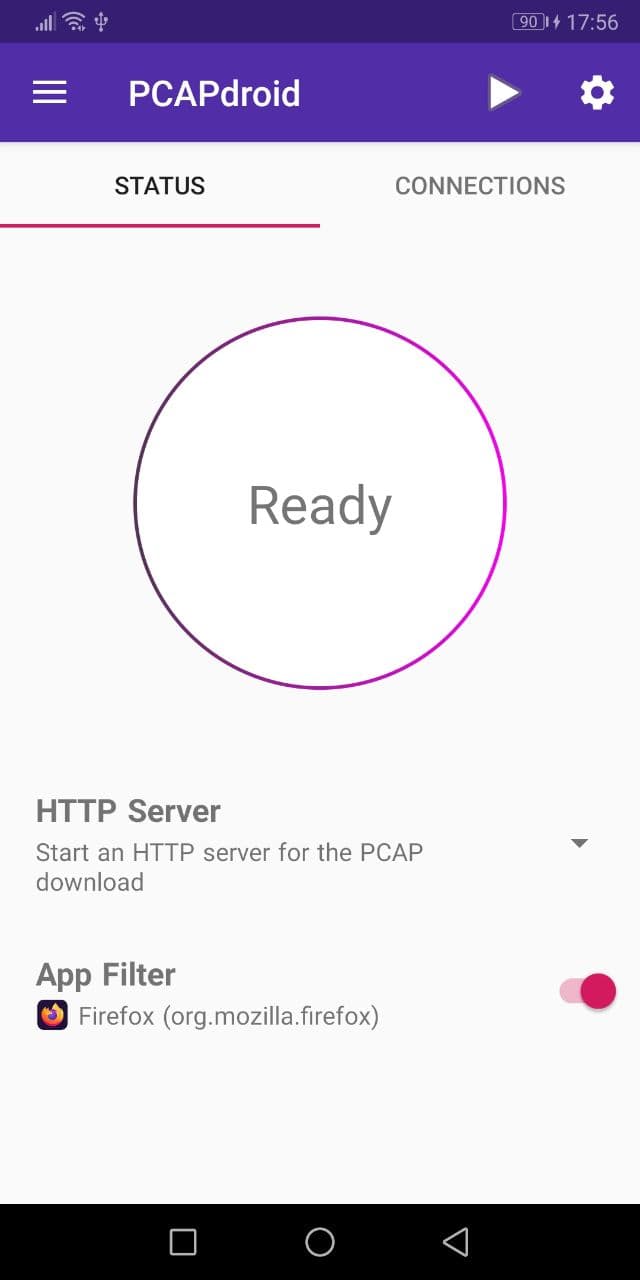
No-root network monitor, firewall and PCAP dumper for Android

android-securitydns-analysiseducation+8
4.7k1 day ago
Malcolm preview

Malcolm

GitHubcisagov/malcolm

Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…

digital-forensicsdns-analysisforensics+9
2.5k21 days ago
Wireshark preview

Wireshark

GitLabwireshark/wireshark

Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

dns-analysisforensicsnetwork-forensics+3
1.6k8h 6m ago
cve-2020-0601-plugin preview

cve-2020-0601-plugin

GitHub0xxon/cve-2020-0601-plugin

Zeek package that uses OpenSSL to detect CVE-2020-0601 exploit attempts

cryptographyexploitationintrusion-detection+3
56 years ago
dhcpoptinj preview

dhcpoptinj

GitHubmisje/dhcpoptinj

DHCP option injector

network-securitypacket-sniffing-analysispenetration-testing+1
436 years ago
BinProxy preview

BinProxy

GitHubnccgroup/binproxy

BinProxy is a proxy for arbitrary TCP connections. You can define custom message formats using the BinData gem.

network-securitypacket-sniffing-analysispenetration-testing+1
1768 years ago
Previous12Next