

mitmproxy
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
android-securityapi-securityapi-security-testing+12
45.1k
mitmproxy/mitmproxyAn interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 ntop/ndpi
Open Source Deep Packet Inspection Software Toolkit
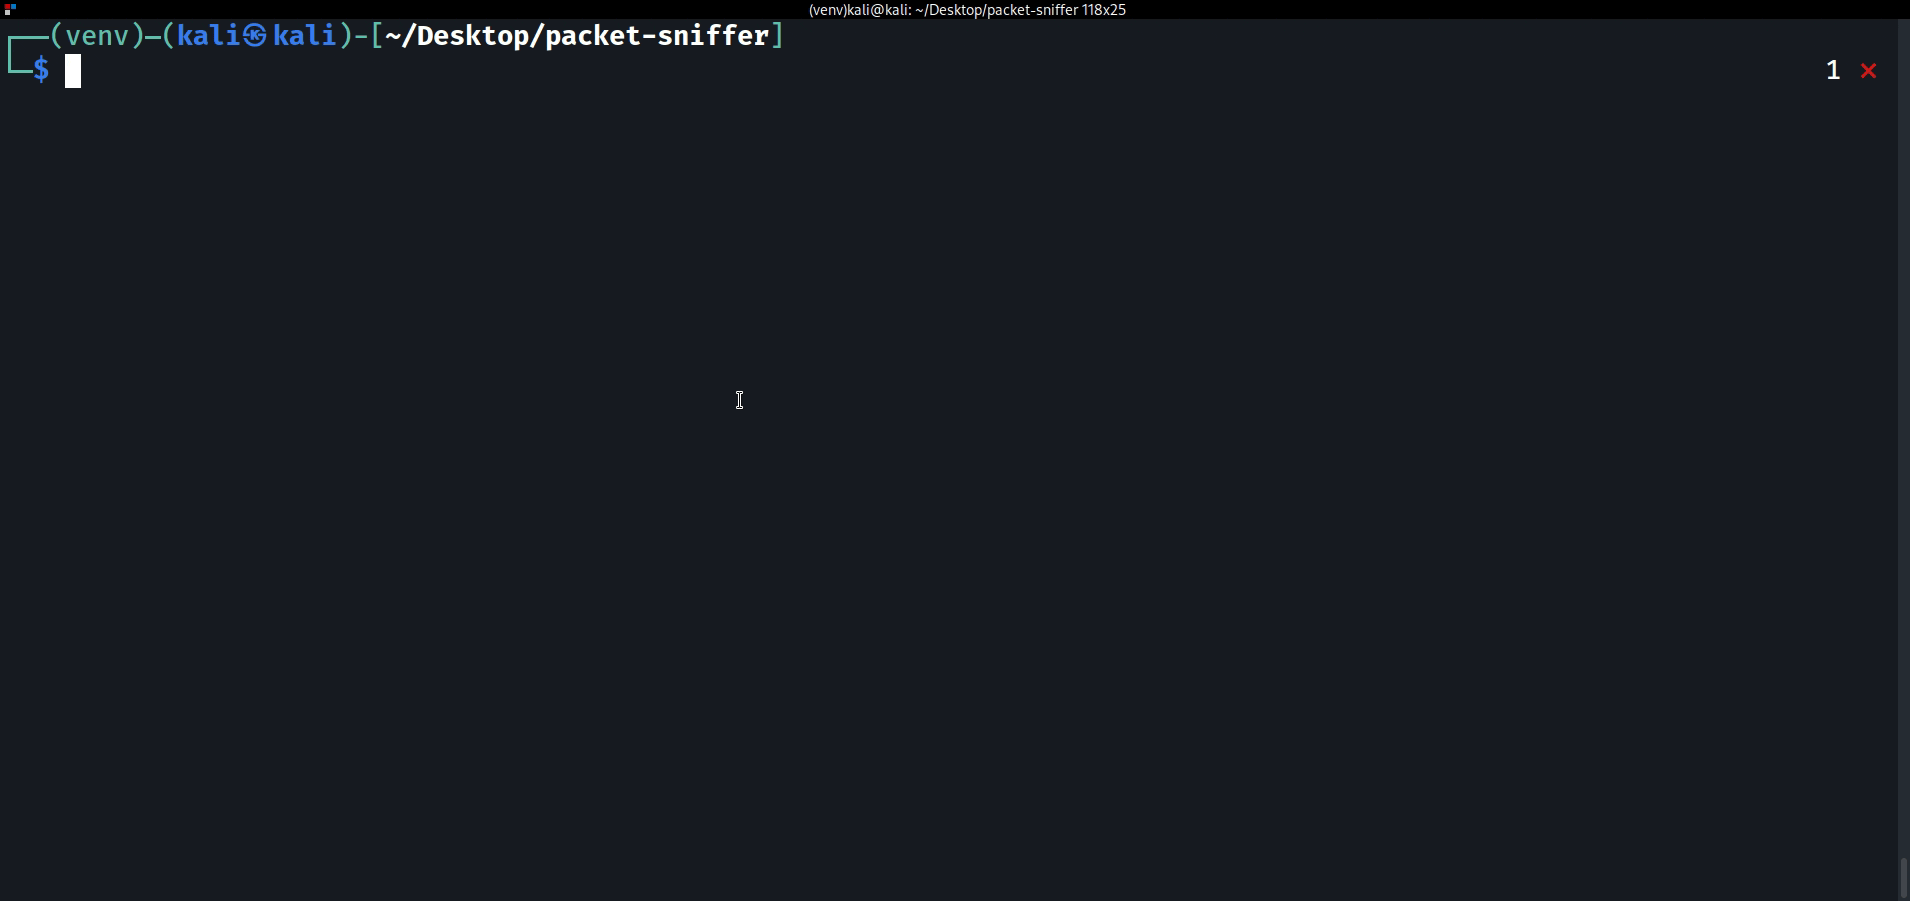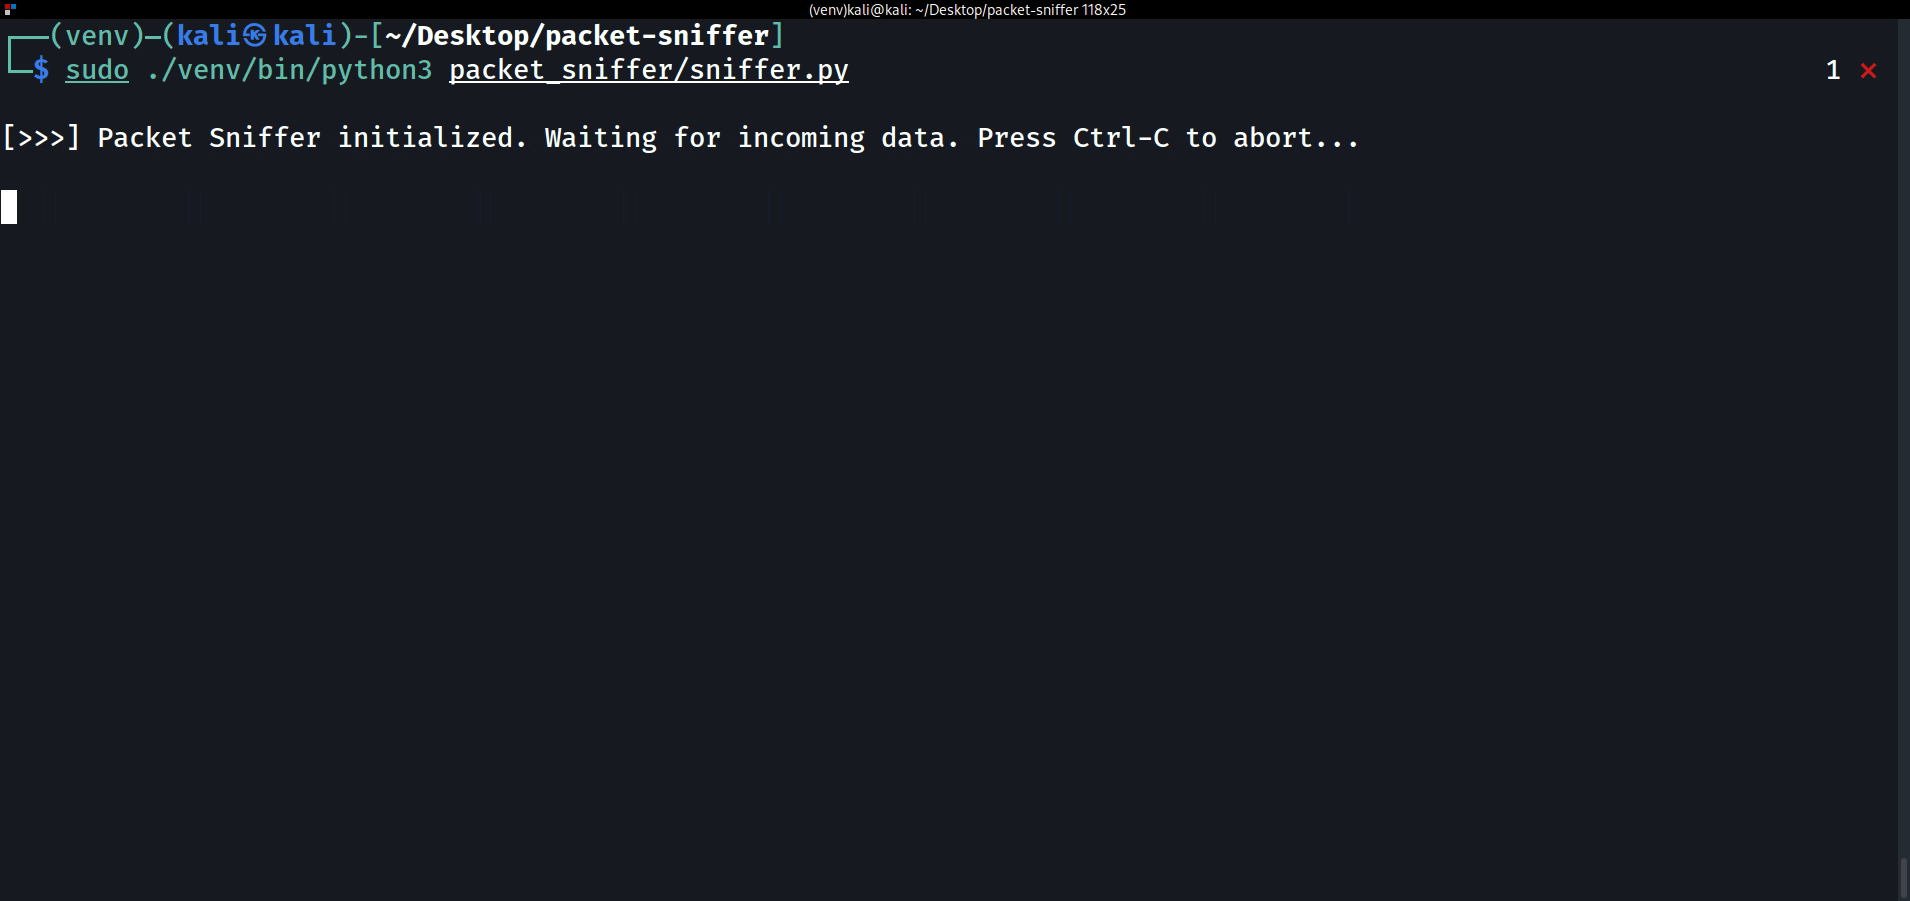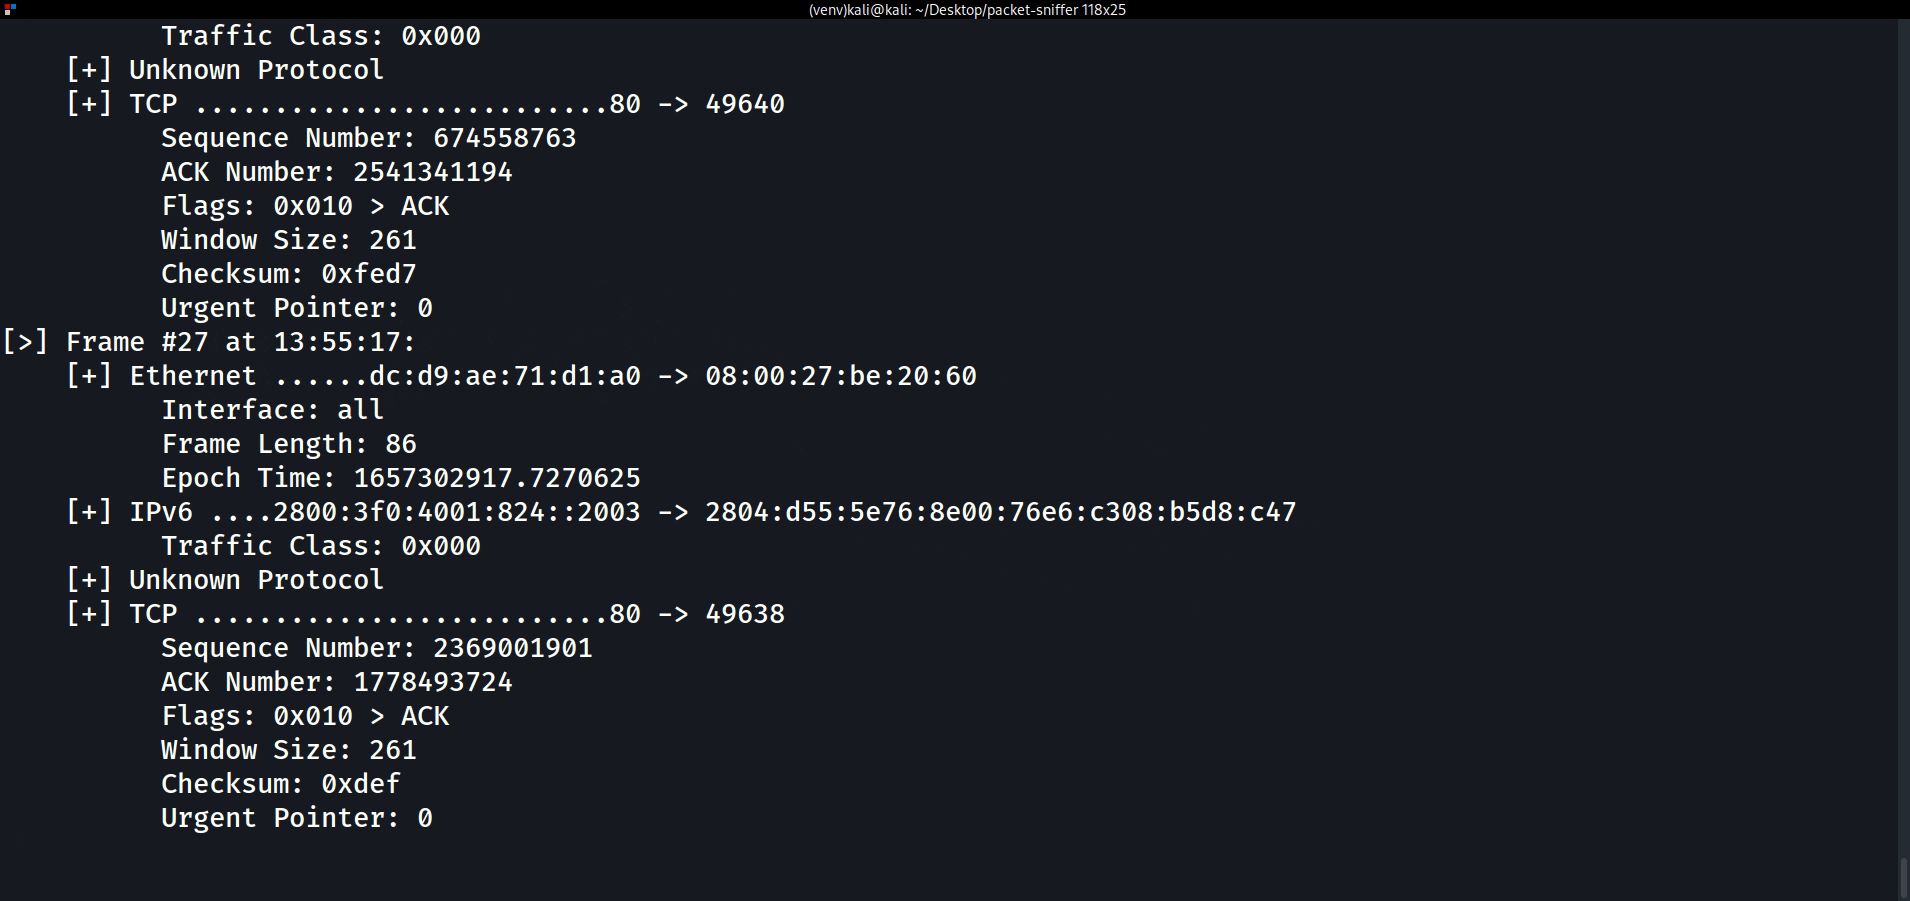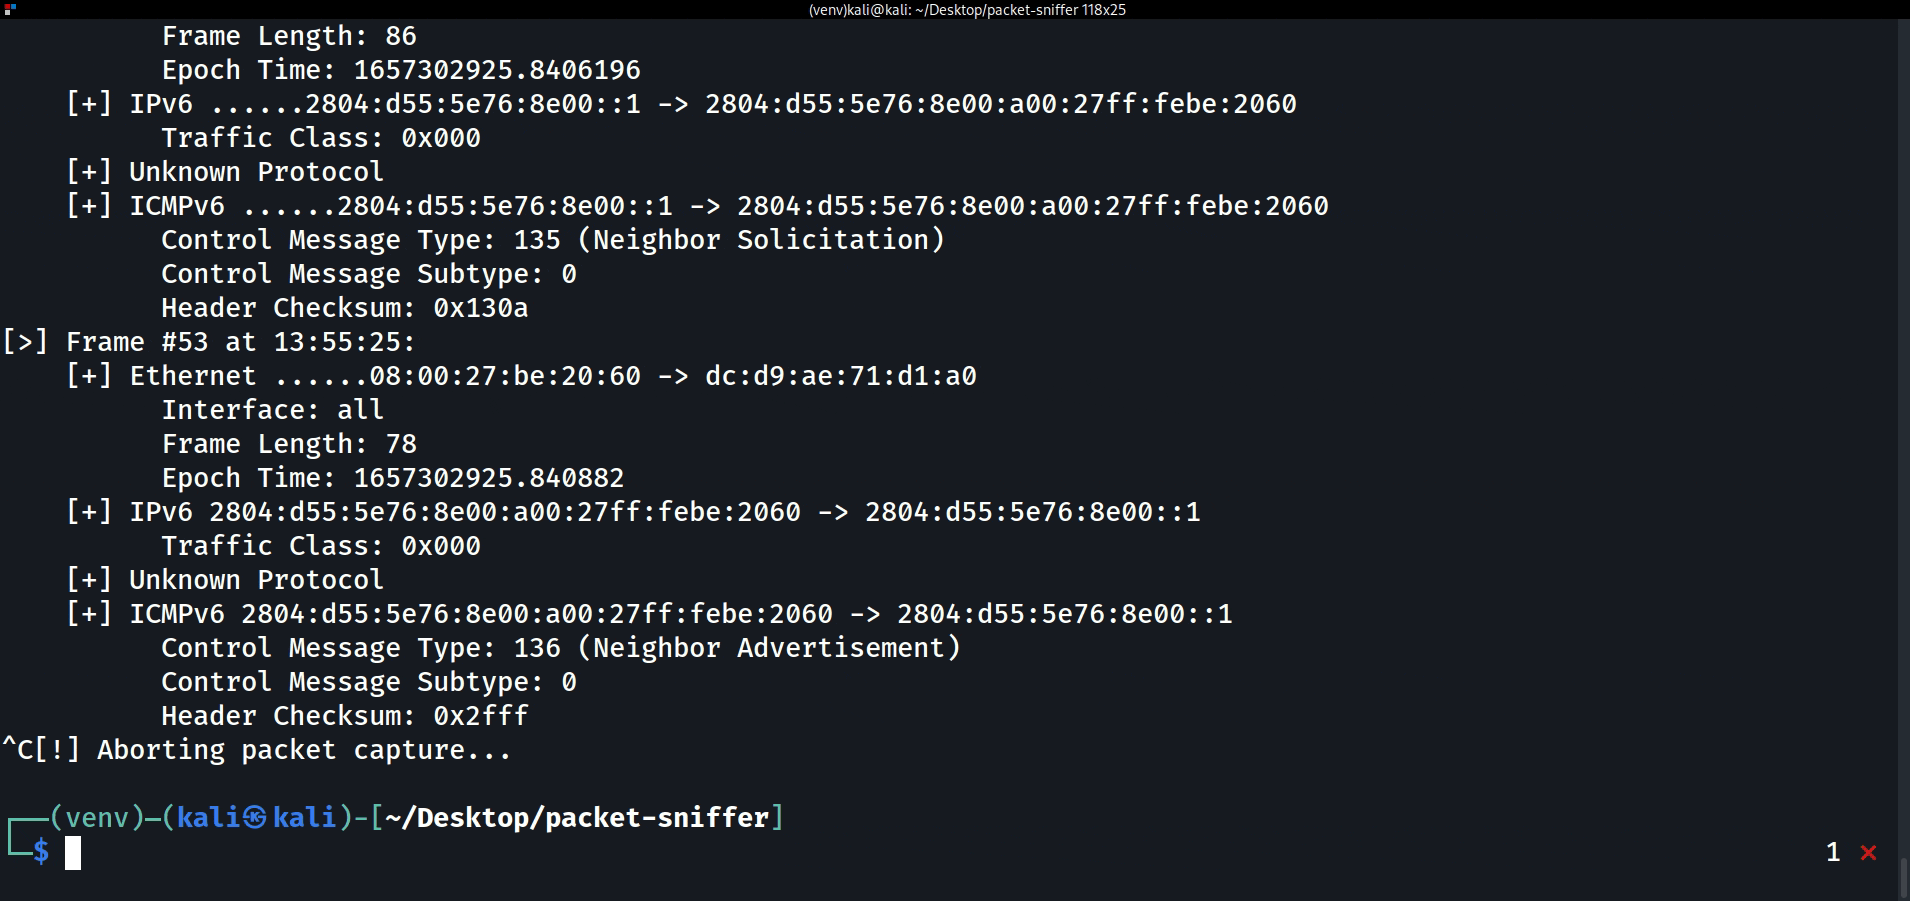 eonraider/packet-sniffer
Raw socket-based network packet sniffer that captures and disassembles TCP/IP packets from network interfaces for security analysis and educational…
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 syssec-kaist/ltesniffer
An Open-source LTE Downlink/Uplink Eavesdropper
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
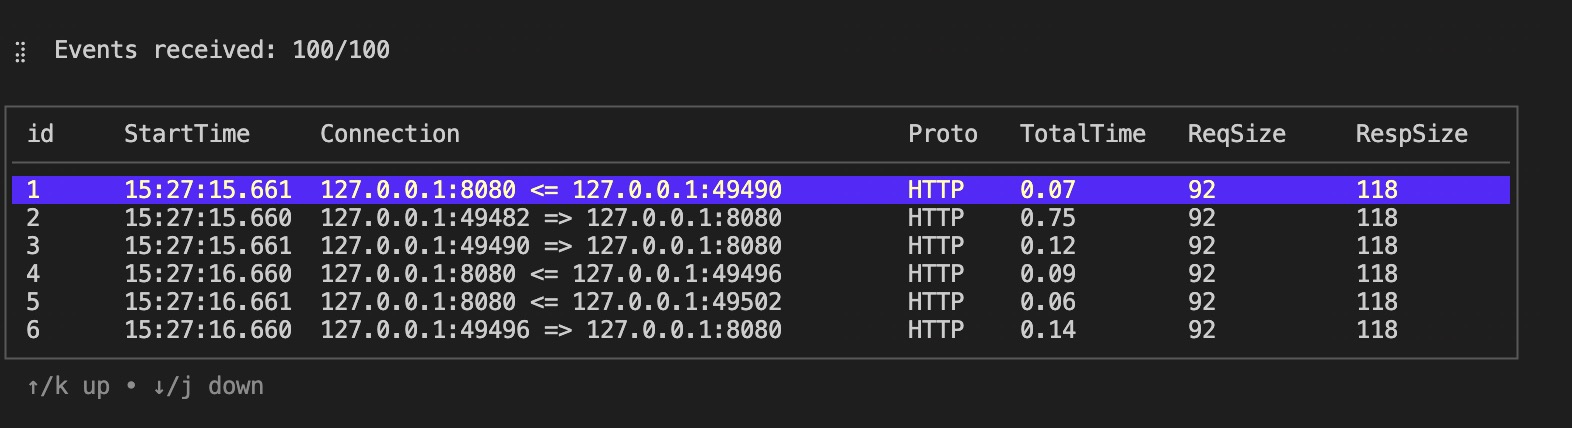 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
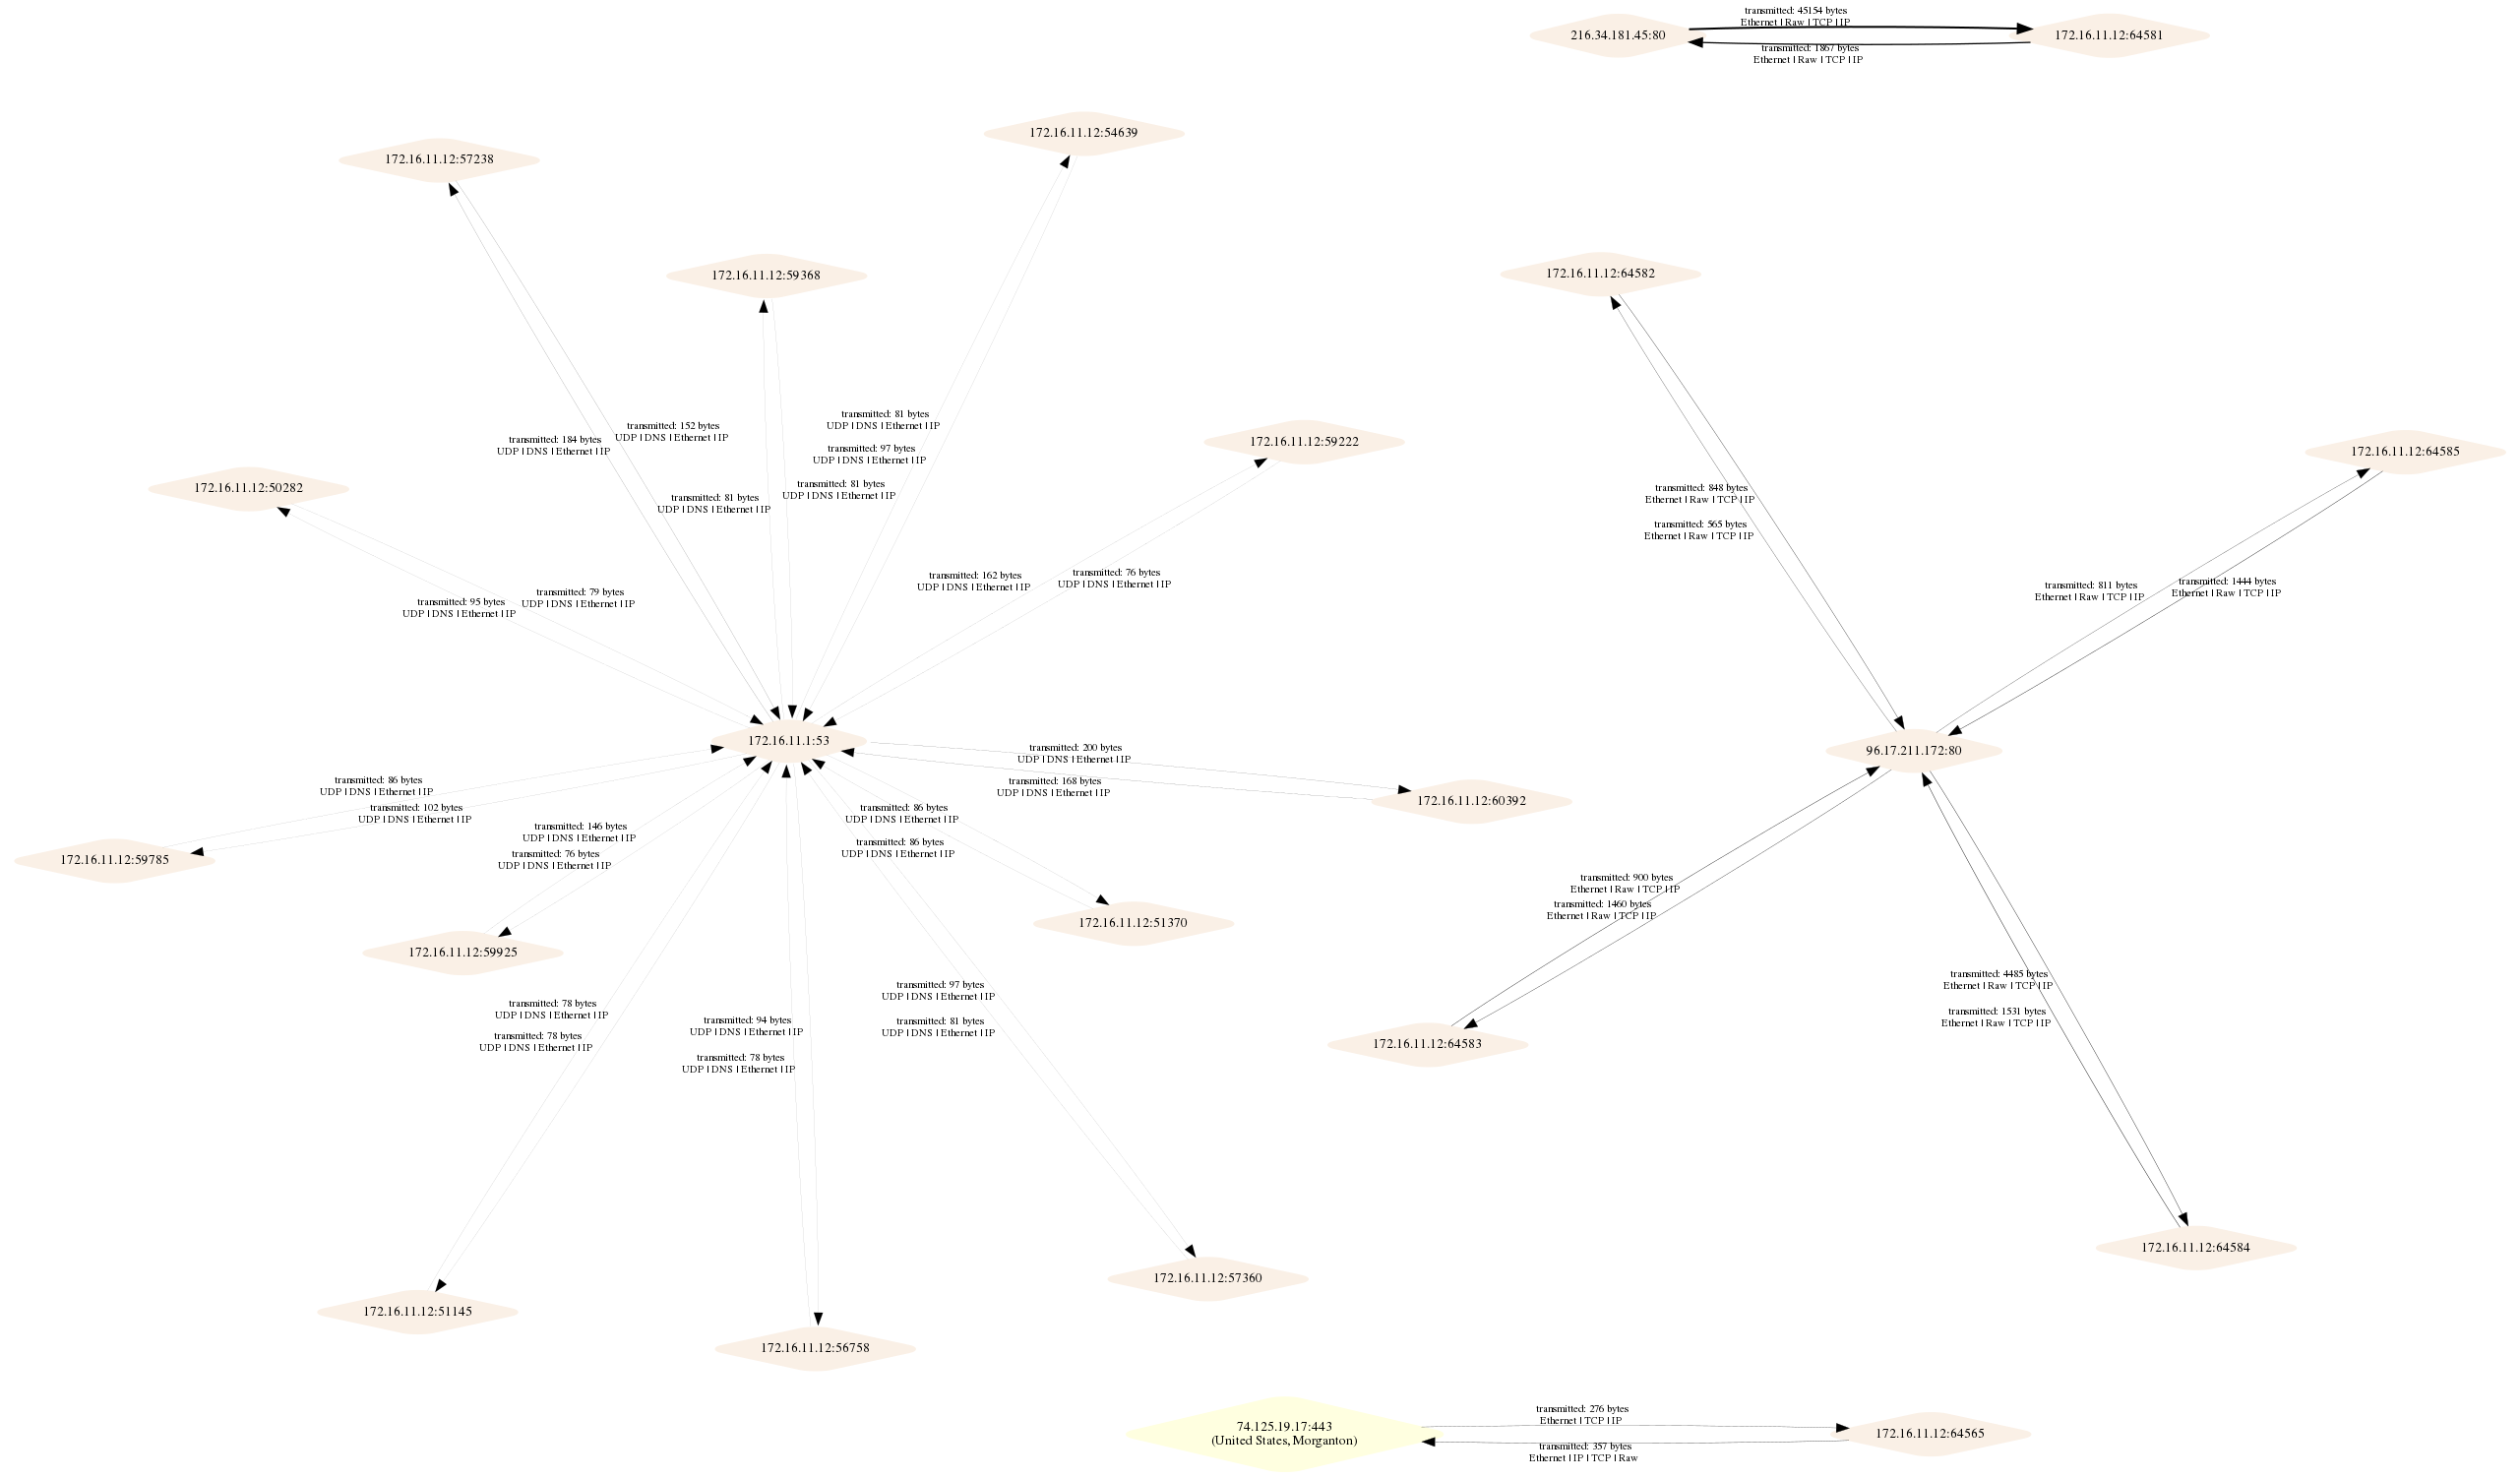 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 sahilmgandhi/iotshark
IotShark - Monitoring and Analyzing IoT Traffic
 cisc0-gif/netcrackpi
RPi3+ Network Cracker Setup Tool